
How to Evaluate an AI SOC
An Evaluation Framework for CISOs and Security Leaders
Wednesday, October 28 |
10am ET / 2pm GMT
Most AI SOC evaluations go wrong before a vendor ever enters the room. You’re buying more than technology: you’re buying an execution layer that will reshape your team, your operating model, and the way your organization defends itself. The criteria from the SIEM, SOAR, and MDR eras don’t measure any of that.
John White spent 20 years in the buyer’s seat, leading security transformations at Virgin Atlantic, ASOS, and Liberty Global. He walks through the framework from The AI SOC Buyer’s Guide: the questions he wishes he’d had when he was the one making the call.
On the table:
- How to define your trajectory before a single vendor gets in the room: Current state, target outcomes, and risk threshold
- What you’re actually buying: The three layers of an AI SOC, and why scoring only the demo-friendly execution layer stalls the relationship
- The differentiators that hold up under scrutiny: Context, memory, and autonomy, plus the list of questions to bring into every vendor meeting
A New Framework for Evaluating AI SOCs
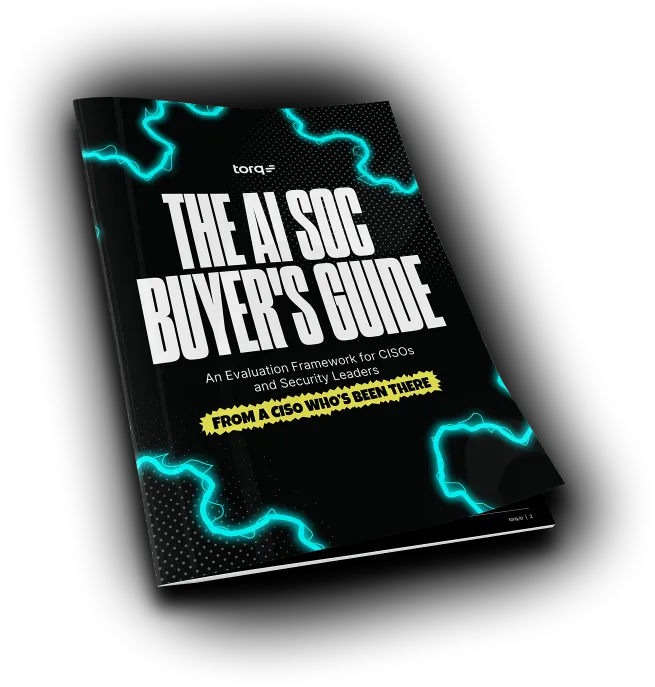
The AI SOC Buyer’s Guide
Define your trajectory before a single vendor gets in the room.
Get the full evaluation framework from John White, Field CISO EMEA at Torq: what you’re actually buying, the differentiators that separate real platforms from marketing, and the questions to bring into every vendor meeting.