The AI SOC Buyer’s Guide
An AI SOC evaluation framework for CISOs and security leaders, written from the buyer’s seat. It covers how to evaluate and buy an AI SOC and how to rethink your approach to SecOps: what you’re actually buying, the differentiators that separate real platforms from marketing, and the questions to ask every vendor.
“This guide is written from the buyer’s seat — the CISO who has to make the call. It’s built from the questions I wish I’d had when I was on the buying side, and the ones I hear CISOs working through now.”
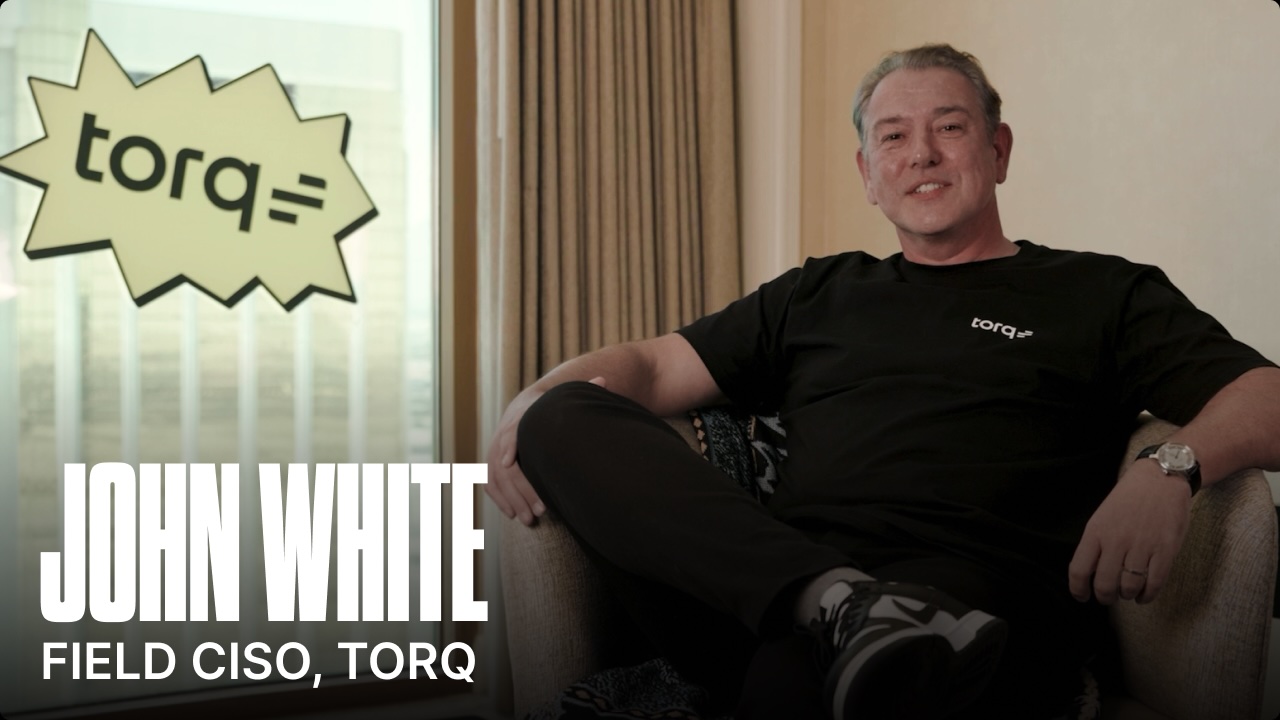
John White, Field CISO EMEA, Torq
With more than 20 years building and running security functions, including SecOps transformations at Virgin Atlantic, ASOS, and Liberty Global, John has been the buyer — and now advises them. This guide distills his approach to an AI SOC evaluation: not just how he judges a platform, but how he thinks about running a SOC once AI changes what’s possible.
AI SOC is a fundamentally different purchase from anything most CISOs have evaluated before. You’re buying more than technology. You’re buying an execution layer that will reshape your team, your operating model, and the way your organization defends itself.
What’s inside
- Know what you’re buying: How to set your direction before vendor conversations, and the three-layer model behind an AI SOC
- Separate real from marketing: The context, memory, and autonomy questions that matter
- Roll it out and prove it: Org design, a 90-day plan, true ROI, and a vendor checklist
A New Framework for Evaluating AI SOCs

How to Buy an 
See John White walk through the framework in this guide, and answer the questions CISOs are actually asking.