Torq REV: The Channel Program Built for the AI SOC Era

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.
Request a Demo

Sheldon Muir is Head of Global Channels & Alliances at Torq, where he leads the REV partner program and the global ecosystem of SIs, VARs, and MSSPs delivering the Torq AI SOC Platform. A three-time CRN Channel Chief, he scaled the program to 175+ partners with a 5-Star CRN rating. Before Torq, he led channel teams at Netskope and Imperva and spent nearly seven years as a Consulting Systems Engineer at Cisco.

Today, we’re announcing Torq REV: Revenue Enablement Velocity, our channel program for resellers, global systems integrators, MSSPs, and MDRs. It’s live worldwide, and partners can go from signed to selling in as little as 10 days.

Deploying the platform is the fast part. Torq was built for agentic decision-making from the ground up, so customers can reach production quickly. Teaching a SOC to actually operate differently is the slower work: new roles, new instincts, a new definition of what good looks like. That takes time, expertise, and someone sitting alongside the customer through it. That work belongs to partners, and the program should be designed to pay for it.

The Question Worth Asking Every AI SOC Vendor

Some AI SOC vendors are quietly building their own managed services businesses and selling directly to the customers their partners introduced them to. It works for a quarter or two. Then the partner stops bringing deals, and the vendor discovers it now owns a services business it never wanted to run.

Our position is the opposite: Torq does not build or sell managed services in competition with our channel. Partners own the customer relationship, partners deliver the services, and partners keep the long-term value that an AI SOC deployment creates.

“Our partners are the force that transforms enterprise security, and Torq REV was purpose-built to help them win more deals, build larger services practices, and lead the AI SOC transition.”
– Ofer Smadari, Torq CEO and Co-founder

Designed Equally for Any Partner Model

Most channel programs make you climb a tier ladder before the economics get good.  We built REV the other way around, starting from the partner’s P&L rather than our quota. There’s no tier ladder to qualify for: REV has three paths, so you pick the one that matches your business, with rebates that grow as your business grows.

  1. If you’re a VAR, distributor, or reseller adding the category to your line card, Resell gives you guaranteed margin, deal registration protection, co-selling support, and joint marketing. You bring the relationships and the sales motion.
  2. If you’re a solution provider or GSI with a delivery practice, Resell + Services adds first right of refusal on professional services and additional margin on services attached. Implementation, migration, and transformation work stays yours.
  3. If you run a managed SOC, MSSP and MDR give you multi-tenant capability, consumption-aligned economics, and dedicated MSSP support, so you can build a next-generation offering instead of retrofitting one.

You can move between paths as your business changes, and nobody has to requalify. Every path also includes joint marketing investment, co-branded campaigns, executive engagement, roadmap collaboration, and dedicated support.

Enablement is the other place programs stall. You sign, then wait a quarter for training cohorts, tenant access, and someone at the vendor who returns your calls. Here’s the REV timeline:

  • Day 1-2: Your named partner manager and partner SE are assigned.
  • Day 1-4: Your team certifies in Partner Academy, self-paced, no cohort wait. 
  • Day 3-7: You get a full Torq tenant for demos and POCs. 
  • Day 8-10: Co-selling support is active on your live deals. 

Ten days from signed to selling is the number we hold ourselves to. 

“What really stood out to me about Torq was how quickly the value resonated with the customer. Torq saw the opportunity to use automation and AI to simplify complex security operations, improve efficiency, and ultimately help teams focus on what matters most.”  

– Daniel Palmer, Client Director, Optiv

That investment in partner technical depth pays off on both sides of the deal.

For you:

  • Higher profitability: Predictable margins, deal protection, and high-margin services attach
  • A practice that lasts: A multi-year AI SOC advisory, implementation, or managed services business
  • No channel conflict: Torq doesn’t build or sell managed services in competition with you

For your customers:

  • Fast time to value: Production in weeks, with a partner guiding the longer work of changing how the SOC operates
  • Proven outcomes: Up to 10x faster response times and far less noise reaching analysts
  • Expert guidance: Certified partners backed by Torq’s channel team and partner SEs

“World Wide Technology has long helped partners translate new technology into durable outcomes for customers, and Torq REV extends that same rigor to the AI SOC market. We’ve felt that value firsthand. Torq’s AI and automation technology have strengthened WWT’s own security operations team, and that’s exactly why we’re excited to see REV bring the same results to more of our customers.”

-Mike McGlynn, Chief Information Security Officer, WWT

What You’re Selling and Where to Start

Partners lead with Torq because the platform holds up under technical evaluation. It runs the complete security operations lifecycle through transparent, agentic AI, with Torq HyperAgents® doing the investigation and response, case management keeping everything in one place, and Torq Socrates™ orchestrating it. Customers have cut response times by up to 10x and automated up to 90% of Tier 1 and Tier 2 work. 

It also survives procurement: Gartner named Torq the Company to Beat in AI SOC Agents for Threat Investigation, KuppingerCole Analysts named Torq the Overall Leader in the 2026 Leadership Compass for the Emerging AI SOC, SACR named Torq a leading Innovator in the 2026 AI SOC Market Report, CRN awarded the partner program a 5-Star designation, and more than 250 enterprises run Torq in production.

The fastest way in is through the ongoing challenge of alert noise, which is why we’ve built a channel-led motion around Torq Auto Triage. It’s a small first ask for the customer and a fast, visible result: what matters, what’s noise, and why — within weeks. 

Once Auto Triage lands, the rest of the lifecycle opens up. Investigation, response, remediation, and managed operations are all follow-on conversations, and every one is a service conversation for you. An AI SOC is a multi-year engagement rather than a one-time deployment, which is what makes it worth building a practice around.

That’s also why REV puts so much into technical enablement. Partners who know the platform deeply deliver implementations that stick, and customers who see measurable value early tend to expand into investigation, response, and threat hunting over time. Strong adoption protects the renewal, and expansion grows the account, which means more recurring revenue for you.

Our channel revenue has grown 150% year over year since 2025, with partners including Carahsoft, Cybersellex, GuidePoint Security, Infinigate, Merlin Cyber, Optiv, Saepio Solutions, RSM, UltraViolet Cyber, and WWT bringing Torq to their customers. REV is the program that growth earned. If your customers are already asking which AI SOC to buy, you don’t need us to tell you the demand is there. You need the economics, the enablement, and the protection to go win it.

FAQs

What is Torq REV?

Torq REV, short for Revenue Enablement Velocity, is Torq’s channel partner program for the AI SOC market. It gives resellers, global systems integrators, MSSPs, and MDRs protected deal registration, predictable margins, self-paced certification through Partner Academy, sandbox access, and co-selling support, with partners able to go from signed to selling in as little as 10 days.

Who can join the Torq REV partner program?

Qualified resellers, VARs, distributors, global systems integrators, MSSPs, MDRs, and technology partners worldwide. There are no tiers to qualify for, and partners join with a simple reseller agreement.

What are the Torq REV partner paths?
  • Resell, for VARs and distributors adding an AI SOC platform to their line card
  • Resell + Services, for solution providers and GSIs delivering implementation and transformation work
  • MSSP/MDR, for managed providers building an AI SOC offering with multi-tenant capability and consumption-aligned economics.
Does Torq compete with its partners on services?

No. Torq does not sell managed services in competition with its channel. Partners own the customer relationship and deliver the implementation, migration, managed, and optimization services that an AI SOC deployment creates.

How quickly can a partner start selling Torq?

As little as 10 days. A named channel manager and partner SE are assigned in the first two days, Partner Academy certification is self-paced and can be finished by day four, sandbox access opens by day seven, and co-selling support is active on live deals by day 10.
SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Buying an AI SOC Isn’t Like Anything You’ve Bought Before

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to Virgin Atlantic, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.

I’ve spent more than 20 years in security, and a good chunk of that time was spent in the buyer’s seat — sitting across from a vendor during a proof of concept, trying to work out whether the technology in front of me would actually solve the problem I had or turn into another integration project that ate more time than it saved. I’ve run those evaluations at Virgin Atlantic, ASOS, and Liberty Global. I know what a good one looks like, and I know how they go wrong.

So I’ll say this plainly: how to evaluate an AI SOC is not a question your old process can answer.  The evaluation criteria we all relied on in the SOAR era, the SIEM era, the MDR era? They don’t fit anymore. And if you run this purchase the way you ran those, you’re going to end up with the wrong platform and a very expensive lesson.

The Category Outran the Frameworks

A year ago, a handful of vendors claimed the AI SOC category. Today, more than a hundred do, and almost every one has bolted “agentic” onto its positioning. Analyst firms are redrawing the category boundaries in real time, and the noise in the market is deafening.

Most of it doesn’t hold up. A lot of what gets sold as an “AI SOC” either stops at triage, wraps a chatbot around a legacy stack, or hides its reasoning in a black box. The plainest test I know still cuts through all of it: if it can’t take action across the threat lifecycle, it isn’t an AI SOC.

And the pressure to decide has only gone up. Attackers are moving at machine speed. The CISOs who were cautiously exploring AI-driven security operations last year are now being asked to commit, with budgets approved, timelines set, and boards expecting results. There’s no longer a long window to plan, adopt, and evaluate. Take the slow and considered path, and the technology will have moved on before you reach a decision.

Why the Old RFP Fails

The first sign that a CISO is still using the old rubric is the questions they ask. They dwell on traditional return on investment: how much does the tool cost? How much in professional services to stand it up? How much will we spend on credits? Those aren’t wrong questions, but they measure the tech in isolation, without weighing the risk or the opportunity.

Most RFPs still measure features and integrations. They don’t measure whether the platform can reason about your environment, learn from your analysts, or act autonomously across the threat lifecycle. Those three capabilities are the whole ballgame in an AI SOC, and the standard scorecard doesn’t even have a column for them.

The real question isn’t “How many features does it have?” It’s whether you can withstand the first wave of a machine-speed attack at all.

Start With a Trajectory, Not a Shortlist

If you take one practical answer from this piece on how to evaluate an AI SOC, make it this one. Most evaluation failures I’ve seen start before any vendor enters the room. They start with the absence of a trajectory.

Every strong evaluation I ran as a CISO began the same way: a clear view of our current state, the outcomes we wanted to deliver, and the actions required to get there, all within our risk threshold. 

Where I see CISOs go wrong today is trying to evaluate everything at once, without a defined path. Establish your trajectory first, and you’ll know quickly whether you’re even talking to the right vendors. (How to actually build that trajectory is one of the first things I walk through in the guide.)

Know What You’re Actually Buying

Here’s the shift that matters most: You’re not just buying a tool. You’re buying an execution layer that will reshape your team, your operating model, and the way your organization defends itself.

That’s a fundamentally different purchase, and it changes what you should be measuring. The guide breaks down the model I use to think about it, as well as the AI SOC org chart and where your analysts go. 

For now, the point is simply this: Evaluate the purchase knowing it changes how your whole function operates, not just which console your analysts log into.

The Questions This Series Will Answer

Once you have your trajectory, you can hold every vendor to the same standard. When every vendor is claiming “agentic,” a handful of questions separate the real platforms from the marketing. Across this series, I’ll go deep on the ones I think matter most — starting with whether a platform can genuinely reason about your environment, whether it actually learns from your analysts, and how much you can trust it to act on its own.

Know these going in, and the marketing falls away fast. If a vendor can’t help you take your first steps or walk you through how to get started, you’re talking to the wrong vendor.

The Budget Cycle Is Coming

These are the things to be thinking about as you put next year’s plan together. The AI SOC is a different purchase, so evaluate it like one: start with your trajectory, understand you’re buying an execution layer and not a tool, and hold every vendor to the questions that actually determine whether the investment succeeds.

I pulled everything I wish I’d had on the buying side into one place. The guide is the long answer on how to evaluate an AI SOC, with the questions to bring into every vendor meeting.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

How Security Orchestration Protects DevOps Environments at Scale

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • Security for DevOps means protecting the entire development lifecycle from code commit to production deployment while maintaining full release velocity.
  • Traditional security approaches create friction in DevOps environments: manual reviews, disconnected tools, and alert fatigue all compound into real operational bottlenecks.
  • SOC teams face core DevOps security challenges: visibility gaps, misconfiguration noise, container vulnerability sprawl, slow incident response, and tool fragmentation.
  • Automated orchestration lets security teams monitor pipelines, detect misconfigurations, and coordinate response across DevOps and security tools. With Torq’s Agentic Builder, engineering teams describe the security outcome they need in natural language and get a production-ready AI Agent deployed in minutes.
  • The Torq AI SOC Platform connects your full DevOps security stack through agentic workflows, giving security and engineering teams the speed and coverage to protect fast-moving environments at scale.

DevOps moves fast by design. Continuous integration, automated deployments, and infrastructure-as-code let development teams ship features in hours rather than weeks. Security teams have a real opportunity here: when they build workflows that integrate directly into the development process, they gain coverage and response speed that manual, disconnected approaches leave on the table.

The answer is orchestration. When security workflows integrate directly into CI/CD pipelines, cloud infrastructure, and development toolchains, SOC teams gain the visibility and response speed they need while development keeps moving. This article covers what security for DevOps requires, the specific challenges SOC teams face in these environments, and how automated orchestration transforms security from a gate into an enabler.

What Is Security for DevOps? Why Traditional Approaches Create Friction

Security for DevOps means protecting every stage of the software development lifecycle, from the moment a developer commits code through build, test, deployment, and production operation. It encompasses code security, pipeline integrity, infrastructure configuration, runtime monitoring, and incident response across an environment that changes continuously.

Organizations built traditional security approaches for a different operating model: periodic reviews, manual assessments, and security gates that pause development until approval is granted. In a DevOps environment running multiple daily deployments across containerized workloads and cloud infrastructure, those approaches create compounding delays that reduce both security coverage and development velocity. Automated orchestration is the opportunity to run both in parallel.

The SecOps, DevOps, and DevSecOps distinction matters here. DevSecOps as a philosophy integrates security responsibility across development and operations teams. Security orchestration is the operational layer that makes that integration real: automated workflows that enforce security controls continuously, with human reviewers focused on judgment calls rather than routine gates.

Understanding DevOps Practices and Security Implications

Three core DevOps practices define the security challenge:

Continuous integration and continuous deployment (CI/CD) means code moves from commit to production in automated pipelines that run dozens or hundreds of times daily. Each pipeline execution is a potential introduction point for vulnerable dependencies, hardcoded secrets, or misconfigured infrastructure. At CI/CD velocity, manual security review cannot scale.

Infrastructure as code (IaC) means teams provision cloud resources through configuration files checked into version control. When those configurations contain errors, including overly permissive IAM roles, unencrypted storage, or open security groups, they deploy at the same speed as application code. Detecting and remediating IaC misconfigurations requires automated scanning integrated into the pipeline itself.

Containerization and microservices multiply the attack surface. A single application may run across dozens of containers, each with its own base image, dependencies, and runtime environment. Vulnerability management across that surface requires automated scanning, prioritization, and remediation workflows that operate at container scale.

Common DevOps Security Challenges SOC Teams Face

Visibility Gaps Across Cloud and Pipeline Environments

DevOps environments span multiple clouds, code repositories, container registries, and deployment targets. Security teams that invest in pipeline-level instrumentation gain visibility into ephemeral containers, serverless functions, and IaC-provisioned resources that conventional perimeter-based tools miss entirely. A misconfigured cloud resource spun up by an IaC template and torn down six hours later shows up in pipeline-integrated security controls, even when it never appears in a conventional security scan.

Comprehensive visibility requires instrumentation at the pipeline level: security controls that embed directly in CI/CD workflows and inspect every build artifact, configuration change, and infrastructure deployment as it happens, in real time.

Alert Fatigue from Misconfiguration Notifications

Cloud misconfiguration scanning tools generate high alert volumes. A mature cloud environment with active development generates configuration drift continuously, and without prioritization logic, every misconfiguration alert arrives at the same urgency level. SOC analysts processing hundreds of misconfiguration alerts per day develop the same response pattern they develop with any high-volume, low-signal alert source: deprioritization and delayed review.

Automated triage and enrichment workflows address this directly. When Torq’s enrichment workflows automatically add exploitability context, asset criticality, and exposure status to misconfiguration alerts, analysts see a prioritized queue with clear action items. Security automation workflows that handle misconfiguration triage at this level consistently reduce the alert volume reaching human analysts.

Vulnerability Management Across Containerized Workloads

Container images inherit vulnerabilities from base images, and applications pull in vulnerable dependencies through package managers. Scanning at build time catches known vulnerabilities before deployment, but newly disclosed vulnerabilities in already-deployed containers require continuous runtime scanning and rapid remediation workflows.

Coordinating vulnerability management across containerized workloads, including scanning, triaging findings by exploitability, generating remediation tickets, and tracking fix deployment, is a multi-step process that manual workflows handle slowly. Automated orchestration runs that process continuously and at scale. See how application security automation accelerates this workflow in practice.

Slow Incident Response Due to Tool Fragmentation

The average enterprise DevOps environment uses a combination of source code management, CI/CD platforms, container registries, cloud providers, infrastructure scanning tools, and security monitoring platforms, often from different vendors with separate APIs, alert formats, and response interfaces. When a security incident occurs in that environment, analysts coordinating response across those tools manually face a slow, error-prone process across multiple consoles and alert formats.

Tool fragmentation also creates coverage gaps. Alerts that originate in a DevOps tool often require context from a security tool to assess accurately. An orchestration layer connecting both makes that correlation automatic and immediate.

Implementing DevOps Security Automation Through Orchestration

Orchestration platforms connect the security and DevOps tool ecosystems through automated workflows that monitor, detect, enrich, and respond across every stage of the development lifecycle, with full coordination handled automatically.

Torq’s Hyperautomation™ engine connects code repositories, CI/CD platforms, cloud security posture management (CSPM) tools, container scanners, SIEM, and incident response systems into unified automated workflows. Security engineers build those workflows using Torq’s Agentic Builder: describe the security outcome in natural language, and Agentic Builder analyzes the environment, selects integrations, writes the orchestration logic, and deploys a production-grade AI Agent in minutes, with the full logic available for engineers to inspect, refine, and own.

Torq HyperAgents® bring autonomous action to DevOps security workflows. HyperAgents is built to monitor pipeline activity continuously, detect security signals across connected tools, and execute response actions the moment a threat is confirmed. When a container image fails a vulnerability scan, HyperAgents can automatically block the deployment, notify the development team, open a remediation ticket, and escalate to the SOC with full context attached. Security engineers can start from a growing library of battle-tested agentic templates for common DevOps security tasks, or build a completely unique agent from scratch. Agentic Builder handles either path.

Torq Socrates™, Torq’s agentic SOC orchestrator, adds intelligent reasoning to DevOps security response and serves as the core orchestrator behind Agentic Builder. Socrates evaluates the context of each finding, including the criticality of the affected service, the exploitability of the vulnerability, and the current deployment status, then determines the appropriate response. A critical vulnerability in a production-facing service triggers an immediate escalation. The same vulnerability in a development environment routes to a remediation ticket with lower urgency. Every step, verdict, and action stays fully auditable, giving engineering teams complete visibility into what an agent did and why.

Integrating Security Into CI/CD Pipelines Without Bottlenecks

The goal of pipeline security integration is continuous protection that adds minimal friction to the deployment process. That requires automated workflows that operate in parallel with the pipeline, running security checks as builds progress.

Torq’s workflow automation pulls security scan results from multiple DevOps security tools as each build completes, enriches findings with threat intelligence and exploitability data, and applies prioritization logic before routing results. Critical findings with active exploits and production exposure trigger immediate response actions. Low-severity findings in non-production environments generate tickets for the development team and deployments proceed on schedule.

This prioritization layer is what separates effective pipeline security from security theater. Automated, risk-based prioritization builds developer trust by demonstrating that security controls are proportionate to actual risk. Explore how cloud-native security automation frameworks support this kind of risk-proportionate pipeline integration.

Choosing DevOps Security Tools That Enable Automated Response

SOC directors building a DevOps security stack face a common architectural tension: point solutions offer deep coverage in specific areas but create integration complexity at scale. A scanning tool for containers, a separate tool for IaC, another for SAST, and a fourth for runtime monitoring each arrive with their own alert format and response interface.

An orchestration layer resolves that tension without a rip-and-replace. It normalizes alert formats across tools, automates cross-tool correlation, and runs response workflows that span the full stack, so existing tool investments keep delivering value.

Four criteria separate platforms that orchestrate from tools that just add another console:

Integration breadth and depth. Coverage has to span code repositories, CI/CD platforms, cloud providers, container platforms, and security tooling, with pre-built connectors rather than custom API work for each one. Torq ships with more than 300.

Multiple extensibility paths. Teams should be able to work in natural language, low-code, or full code depending on the task and the engineer, instead of being locked into one paradigm.

Auditability by default. Every agentic verdict and action should be inspectable after the fact, with the reasoning attached. This is what clears security review and makes autonomy defensible.

Configurable human oversight. Control should be a dial, not a switch: full autonomy for high-volume, low-risk findings, and human approval for actions where a wrong call is expensive.

For teams evaluating their approach, the security automation glossary covers the terminology that distinguishes orchestration platforms from point solutions, and agentic coding for SecOps shows how Torq meets engineers where they already work.

Security That Moves at DevOps Speed

DevOps environments will keep moving fast. The security programs that protect them effectively will move just as fast, with automated orchestration that monitors pipelines continuously, detects threats in real time, and coordinates response across every tool in the stack at machine speed.

Torq’s AI SOC Platform gives security and DevOps teams the orchestration layer to protect DevOps environments at scale: agentic AI that builds and deploys production-grade security agents from natural language intent, deep DevOps integrations, and autonomous response that acts on security signals the moment they appear.

Is your security program keeping pace with your DevOps environment, or is the gap between deployment velocity and security coverage widening?

DevOps environments move at a speed that exposes the limits of manual security operations, and the SOC teams protecting them effectively are the ones that have replaced manual handoffs with autonomous, agentic workflows. Torq is the only true AI SOC platform built to secure fast-moving DevOps environments at the speed they operate.

If your security team is still playing catch-up with every deployment, the AI SOC Apocalypse manifesto is here for you.

FAQs

What is security for DevOps?

Security for DevOps means integrating security controls, monitoring, and response workflows into every stage of the software development lifecycle, from code commit through build, test, deployment, and production operation. DevOps security embeds automated controls directly into CI/CD pipelines, infrastructure provisioning, and runtime environments. The goal is continuous protection that matches the velocity of the development process. Learn how security orchestration enables this kind of continuous, pipeline-integrated security at scale.

How do I secure my DevOps pipeline?

Securing a DevOps pipeline requires automated security controls at each stage: static application security testing (SAST) and dependency scanning during build, IaC misconfiguration detection during infrastructure provisioning, container image scanning before deployment, and runtime monitoring in production. The connecting layer is an orchestration platform that pulls findings from each scanning tool, enriches them with exploitability and asset criticality context, and routes critical findings to the right response workflow. Low-risk deployments proceed on schedule. Torq’s Hyperautomation engine connects these tools through agentic workflows that security engineers build by describing the outcome they need. Agentic Builder handles the orchestration logic and deploys a production-ready AI Agent. Explore application security automation for a deeper look at pipeline security implementation.

Is DevOps part of cybersecurity?

DevOps and cybersecurity are distinct disciplines that overlap significantly in modern enterprise environments. DevOps focuses on accelerating software delivery through continuous integration, deployment automation, and infrastructure as code. Cybersecurity focuses on protecting systems, data, and users from threats. DevSecOps is the practice of integrating security into DevOps workflows, making security a shared responsibility across development, operations, and security teams. SOC teams play a critical role in DevSecOps by providing the security monitoring, threat detection, and incident response capabilities that development and operations teams rely on.

What are examples of DevSecOps in practice?

Common DevSecOps implementations include automated dependency scanning that flags vulnerable libraries before code merges, IaC scanning that detects misconfigured cloud resources before deployment, container image scanning that blocks vulnerable images from reaching production, and automated remediation workflows that generate and assign tickets when vulnerabilities are discovered. At a more advanced level, DevSecOps includes agentic security workflows that monitor production environments continuously and trigger automated response actions when anomalies are detected. Torq’s AI SOC Platform supports all of these workflows through Agentic Builder. Security engineers describe the outcome, Socrates builds and deploys the agent, and the team retains full visibility into the logic and can refine it as their environment evolves.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Cybersecurity ROI Calculator: Measure Your Investment

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • Cybersecurity ROI (return on security investment, or ROSI) quantifies the financial and operational value of security initiatives relative to their cost.
  • Measuring security ROI requires structured approaches because benefits are often intangible, costs shift over time, and the threat landscape evolves continuously.
  • The core ROI formula combines incident cost reduction, prevention rate, and tool investment into a clear business case for security spending.
  • Automation is the most reliable driver of measurable security ROI: faster response, fewer analyst hours on repetitive work, and lower mean time to respond (MTTR).
  • The Torq AI SOC Platform automates Tier 1 triage, alert correlation, and incident response workflows, converting security investment into quantifiable operational and financial gains.

Security teams have always had to justify their budgets, and the bar for that justification keeps rising. Boards and CFOs want proof that security spending delivers measurable business value: reduced risk translated into financial language. That pressure has made cybersecurity ROI calculators a standard part of the security leader’s toolkit, a way to convert threat prevention, automation efficiency, and incident response improvements into the numbers executives understand.

What Is Cybersecurity ROI and Why It Matters

Return on security investment (ROSI) measures the financial and operational return an organization gains from its cybersecurity spending relative to what that spending costs. It answers the question every security budget conversation eventually reaches: are we getting more value from this investment than we are spending on it?

ROSI differs from traditional ROI in one important way. Most investments generate revenue. Security investments reduce risk, prevent downtime, and avoid costs. These benefits are real and require different measurement approaches. A security control that prevents a $2 million breach and costs $300,000 to implement delivers measurable positive return, even though it never appears on a revenue line.

Framing security investment in ROSI terms gives security leaders the language to engage CFOs and boards on their own terms. A well-structured security automation program that reduces analyst hours, cuts MTTR, and prevents incidents delivers financial value that a properly built ROSI model makes visible.

Why Measuring ROI Is Difficult in Cybersecurity

Several factors make it difficult to measure cybersecurity ROI accurately. Understanding them is the first step toward building a framework that holds up in board conversations.

Intangible benefits dominate the value side of the equation. The breach that a control prevented, the data that stayed protected, and the regulatory fine the organization avoided are real financial outcomes. Quantifying them requires probability modeling: estimating the value of a prevented incident means assigning a likelihood to a scenario that the control kept from occurring.

Variable costs compound the complexity. Security tool costs, analyst salaries, incident response retainer fees, and compliance overhead all shift as the organization grows and threats change. ROI models built on current cost data stay more accurate and defensible over time than those built on static annual assumptions.

The threat environment itself introduces measurement uncertainty. A security control that delivers strong ROI against today’s dominant attack techniques may face a different calculus in 18 months as attacker tactics shift. ROI models need regular updating to stay accurate.

A structured approach to ROSI measurement gives security leaders far more defensible budget conversations than gut instinct or competitive benchmarking alone. The frameworks covered below make that measurement practical.

How to Measure Cybersecurity ROI

The foundational ROSI formula looks like this:

ROSI = (Risk Reduction Value – Cost of Security Control) / Cost of Security Control x 100

Breaking that down into inputs:

  • Risk reduction value = Annual Loss Expectancy (ALE) before the control minus ALE after the control. 

ALE is calculated as: Asset Value x Threat Frequency x Impact Factor.

  • Cost of security control = Total cost of ownership for the security investment, including licensing, implementation, maintenance, and analyst time.

A 500% ROI means the security investment returns six times its cost in risk reduction value. For every $1 spent, the organization avoids $6 in potential loss. A 70% ROI means the investment returns $1.70 in risk reduction for every $1 spent. Both represent positive returns; the magnitude reflects the scale of risk reduction relative to investment cost.

In practice, most ROSI calculations work with ranges, since threat probability and incident cost both carry inherent uncertainty. The goal is a defensible estimate that holds up to executive scrutiny.

Sample Cybersecurity ROI Calculator Framework

Here is a worked example showing how automation directly improves security ROI.

Scenario: A 500-person enterprise SOC team handling 1,000 alerts per week

Baseline (before automation):

  • Average analyst time per alert: 15 minutes
  • Analyst fully-loaded hourly cost: $75
  • Weekly analyst cost for alert triage: 1,000 alerts x 0.25 hours x $75 = $18,750
  • Average MTTR: four hours
  • Estimated annual breach probability: 30%
  • Estimated breach cost: $3.5 million
  • Annual Loss Expectancy: $1.05 million

After deploying automated triage and response workflows:

  • Automated alert handling rate: 85% of alerts handled autonomously
  • Remaining alerts requiring analyst time: 150 per week
  • Weekly analyst cost for alert triage: 150 x 0.25 hours x $75 = $2,813
  • Weekly analyst time savings: $15,937
  • Annual analyst time savings: approximately $829,000
  • MTTR reduction: four hours to 45 minutes (estimated 81% improvement)
  • Breach probability reduction with faster response: 30% to 18%
  • New Annual Loss Expectancy: $630,000
  • Annual risk reduction value: $420,000

Total annual value (time savings + risk reduction): approximately $1.25 million 

Annual platform cost (estimated): $300,000 

ROSI: ($1.25M – $300K) / $300K x 100 = approximately 317%

This framework is replicable with your organization’s actual figures. The key inputs are analyst cost per hour, current alert volume, current MTTR, estimated breach probability, and estimated breach cost. Plugging in real numbers from your environment produces a defensible ROSI estimate you can take to the board.

Real-world Torq deployments validate this model: FICO achieved a 99.4% reduction in MTTR after deploying Torq, beating their own automation targets.

How Torq Automation Improves Security ROI

The analyst time savings in the example above reflect what Torq customers experience when they automate Tier 1 triage and alert correlation. Manual alert handling is the highest-volume, lowest-leverage activity in most SOC environments. Analysts reviewing and triaging repetitive alerts add cost without adding the strategic judgment that experienced security professionals bring to complex investigations.

Torq HyperAgents® handle Tier 1 alert triage autonomously. HyperAgents is built to correlate signals across connected systems, enrich findings with threat intelligence and asset context, and execute initial response actions before an alert reaches the human review queue. The analyst workload that remains is the high-value work that benefits from human judgment.

The platform-level numbers speak directly to ROI: Torq customers achieve 10x faster response times, with 95% of Tier 1 cases auto-remediated across more than one billion daily security automations. Valvoline’s security team saves seven analyst hours every day after deploying Torq, hours that now go toward strategic security work. Carvana runs 100% of its Tier 1 alert handling autonomously through Torq AI Agents, at a scale that would require a significantly larger analyst team to match manually.

Torq Socrates™, Torq’s agentic SOC orchestrator, adds intelligent reasoning to the triage layer. Socrates evaluates alert context, prioritizes by severity and business impact, and routes findings to the appropriate response workflow. Response actions start immediately when a threat is confirmed, driving MTTR down consistently.

The ROI impact compounds over time. Every hour of analyst capacity freed from repetitive triage becomes an hour available for threat hunting, strategic risk work, and complex incident investigations — higher-value activities that reduce breach probability and improve overall security posture. Torq’s approach to reducing analyst burnout also drives employee retention, which carries its own significant ROI. Replacing a senior security analyst costs an estimated $150,000-$200,000 in recruiting, onboarding, and productivity loss.

Integration-Driven ROI

Security ROI also flows from integration efficiency. Disconnected tools create duplicate work: analysts manually correlate data between SIEM, EDR, and IAM platforms, copy findings between systems, and manage separate alert queues for overlapping threat categories. Each manual handoff adds time to MTTR and analyst hours to the triage cost line.

Torq Hyperautomation™ connects SIEM, EDR, IAM, ticketing, threat intelligence, and cloud security tools into unified automated workflows. When your SIEM fires an alert, Torq automatically pulls enrichment data from your threat intelligence platform, checks identity context from your IAM system, queries your EDR for endpoint status, and assembles a complete investigation package in seconds. A process that takes analysts 20-40 minutes to complete manually is completed in moments.

Deepwatch, a leading MDR provider, built on Torq’s Hyperautomation to maximize ROI for its customers across global security infrastructure, automating detection and response workflows that would otherwise require significant manual analyst effort. The integration depth Torq provides lets organizations consolidate overlapping tool functions, streamlining their stack and lowering licensing costs in the process.

A real estate enterprise using Torq saved 1,000 analyst hours and $120,000 in a single quarter, a direct return on platform investment that showed up in Q1 financial results. RSM, a leading MSSP, automated 82% of global customer security cases through Torq, a scale of coverage that directly improves the ROI story for every customer they protect.

Building a Business Case for Automated ROI

Security ROI lands with executives when it connects to business outcomes they already track. Framing automation results in operational and financial KPI terms moves budget conversations from defensive to strategic.

Four KPI alignments that resonate with business leaders:

Cost per incident drops as automation handles more of the detection-to-response cycle. When analysts spend fewer hours per incident, direct labor costs decrease and the team handles more incidents at the same headcount.

System uptime and availability improves as MTTR decreases. A four-hour MTTR in a revenue-generating system that processes $100,000 per hour represents $400,000 in potential revenue impact per incident. Cutting MTTR to 45 minutes reduces that exposure to approximately $75,000.

Compliance posture strengthens as automated evidence collection, control monitoring, and audit workflows run continuously. The cost of compliance failures (fines, remediation, and reputational damage) is a legitimate ROI input that many ROSI models underweight.

Analyst retention improves when automation removes the repetitive, low-judgment work that drives burnout. The ROI of security team wellbeing is measurable: lower turnover means lower recruiting and onboarding costs and higher institutional knowledge retention.

When to Use an ROI Calculator vs. Real Performance Data

ROI calculators serve a specific purpose: they help organizations build a business case before deploying a solution, using probability-based estimates to project expected returns. They are valuable for budget justification, vendor selection, and executive alignment.

Real performance data from a deployed automation platform serves an even more powerful purpose: it replaces projections with proof. When Torq dashboards show that the platform handled 12,000 alerts autonomously last quarter, reduced average MTTR from four hours to 38 minutes, and freed 847 analyst hours for higher-value work, those numbers represent the actual financial and operational return on the platform investment.

The strongest business cases for security automation combine both. Use a calculator to project expected returns before deployment. Use platform performance data to validate those projections, demonstrate realized ROI, and build the case for expanding automation coverage. Security automation benefits grow as coverage expands: each new automated workflow adds to the ROI calculation.

Automation Is How Security ROI Becomes Real

Cybersecurity ROI calculators give security leaders a framework for the conversation. Automation is what makes the numbers real. The projected time savings, MTTR reductions, and breach probability improvements in any ROI model depend entirely on whether the security program can execute at speed, correlate signals across systems, and respond autonomously at scale.

Torq’s AI SOC Platform gives security teams the automation layer to turn ROI projections into operational reality: autonomous triage, intelligent orchestration across your full tool stack, and agentic AI that acts on security signals the moment they appear.

Is your security team still estimating ROI based on projections, or do you have the real performance data to prove automation value to your board?

The AI SOC Apocalypse is underway. Security teams that have made the shift to autonomous operations are building ROSI that compounds every quarter, with real platform data that makes the business case undeniable. 

Torq is the only true AI SOC platform built to turn security automation investment into measurable, growing returns.

FAQs

What is a cybersecurity ROI calculator?

A cybersecurity ROI calculator is a tool that estimates the return on security investment by comparing the cost of security controls against the financial value of risk reduction and operational efficiency gains. Calculators use inputs like incident probability, estimated breach cost, tool investment, and analyst time savings to produce a projected ROSI percentage. They help security leaders justify budget requests, prioritize investments, and communicate security value to non-technical stakeholders. Real automation platform data, like response time improvements and analyst hours saved, converts those projections into proven ROI. Learn how Torq’s automation capabilities drive measurable security ROI.

How do you calculate ROI in cybersecurity?

The core ROSI formula is: (Risk Reduction Value minus Cost of Security Control) divided by Cost of Security Control, multiplied by 100. Risk reduction value is the difference between your Annual Loss Expectancy before and after implementing a control. Annual Loss Expectancy equals Asset Value multiplied by Threat Frequency multiplied by Impact Factor. Cost of security control includes licensing, implementation, and ongoing operational costs. For automation specifically, analyst time savings add directly to the return side of the equation: hours freed from manual triage multiplied by fully-loaded analyst cost per hour produce a measurable, recurring financial return.

Is cybersecurity a good investment?

Yes, and the financial case strengthens significantly when automation is part of the program. The average cost of a data breach reached $4.99 million in 2026 according to IBM’s Cost of a Data Breach Report, while effective security automation consistently reduces breach probability and MTTR. Security investments that prevent a fraction of that expected loss at a fraction of the breach cost deliver strong positive returns. The opportunity is in measuring and communicating those returns clearly, which is exactly what a structured ROSI framework and real automation performance data enable. Explore how automated SOC incident response converts security investment into measurable operational outcomes.

What is the ROI of security automation specifically?

Security automation ROI flows from three primary sources: analyst time savings from automating repetitive Tier 1 tasks, MTTR reduction from faster automated response, and breach probability reduction from more consistent and comprehensive coverage. A SOC team handling 1,000 alerts per week that automates 85% of triage can recover hundreds of thousands of dollars in annual analyst hours alone, before factoring in risk reduction. Platform performance data from deployed automation systems provides ongoing, auditable proof of that return. See how Torq HyperAgents autonomously handles alert triage and response to drive measurable ROSI by exploring Torq’s automated SOC incident response capabilities.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

The AI SOC Buyer’s Guide Series

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Rethinking SOC Maturity: Stop Counting Tools, Start Measuring Decisions

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

David Melamed is Head of Emerging Technologies at Torq. He joined through Torq’s acquisition of Jit, which he co-founded and has led as CTO since 2020, building agentic security on a production Context Graph. A cloud security veteran with 20+ years of experience, David previously held senior technical roles at Cisco (via the CloudLock acquisition) and MyHeritage.


In The Odyssey, before Odysseus sails a narrow strait on his way home, the witch Circe gives him a brutal instruction: you cannot pass both Scylla and Charybdis unharmed, so stop trying. Charybdis, the whirlpool, can swallow the entire ship. Scylla, the monster on the cliff, will take up to six men. So Odysseus steers close to Scylla and loses the six men, but keeps the ship, choosing the loss he can survive over the loss that ends the voyage. And he chooses it in advance, with his eyes open.

Sheer volume means that no SOC works every alert, so that judgment call is the most advanced thing a security operations center can do. Almost no maturity model measures it.

Your Maturity Model Is Measuring the Wrong Thing

The common consensus is that SOC maturity is not about tools. But then everyone pulls out a maturity model that is, in practice, a tool and capability checklist: Do you have a SIEM? A SOAR? Threat intel feeds, 24/7 staffing, a detection engineering function, a case management system? Check the boxes, climb the ladder.

The problem is that a SOC can check every capability box and still be bad at the only thing that matters: making accurate, explainable decisions, fast. It can own every category of tool and still decide slowly, decide wrong, and never be able to say why. Tool count is muscle. Maturity is metis, the cunning judgment that got Odysseus home when force could not.

Here is the claim the rest of this post defends: A SOC that claims to investigate every alert is not mature. It is drowning, or it is not telling you the truth. The first blog in this series laid out why: the queue outruns the people every day, false positives dominate, and most teams are overwhelmed by the sheer volume. Full coverage is not on the menu, at least not today, and later posts will show how AI starts to change that math. But right now, the queue wins. 

So the real question was never whether you leave alerts uninvestigated. You do. The question is whether you choose which ones you do investigate on purpose.

Maturity is Choosing Your Losses on Purpose

To continue my analogy, every SOC already steers past Scylla. The immature one just does it blindfolded.

When the queue is too long and the shift ends, something goes uninvestigated. In most SOCs, that choice is made by accident: whatever the tired analyst did not reach by 2am becomes the accepted loss, decided by exhaustion rather than by risk. Nobody signed off on it. Nobody can defend it. And the team finds out what it deprioritized when it shows up in the breach report.

The mature SOC makes the identical choice deliberately. It decides, by risk, what it will not chase this week, and it writes that decision down. Writing down what you chose not to chase sounds like liability, and counsel will flinch at it. It is the opposite. Undocumented risk acceptance is the liability. A dated, risk-based decision is standard GRC practice, and it is defensible precisely because someone owned it. Same loss, opposite posture. Odysseus did not lose six men by accident. He chose them to save the ship, on the best counsel available, before he entered the water.

This is a concrete, testable difference, not a philosophy. Ask a SOC leader what their team deliberately deprioritized last week and why. A mature team has an answer. An immature team has a backlog it is quietly hoping was not important.

Decision Accuracy: Measuring the SOC as a Decision Engine

If maturity is decision quality, then measure decisions. Four questions do more work than any capability checklist and help measure decision accuracy. Three of them you have seen before. The fourth is the one that separates mature from lucky, and almost no maturity model asks it.

  1. What did you choose to chase, and does that match your actual risk? This is coverage, but not the vanity version. Risk ranking is itself a decision, made cheaply and provisionally at intake, so the number that matters is not the percentage of all alerts touched; it is the percentage of the classes you rated high-risk going in that actually got adjudicated. How often that intake ranking was wrong is part of the next metric.
  2. How fast did you decide? Time to decision, the gap between an alert arriving and a verdict someone will stand behind, is the metric post-it almost no one tracks.
  3. How often were you right? Decision accuracy, measured by how often a closed alert was truly benign and how often an escalation was truly warranted. You cannot compute this on alerts you never opened, so mature teams sample: re-investigate a random slice of the deprioritized queue to estimate how often the deferral was wrong. That sample is the honesty check on the entire model, and it tells you whether speed is helping or just producing faster mistakes.
  4. What did you consciously choose not to chase, and can you defend it? This is the Scylla metric, and it is the one nearly every maturity model omits. A team that can name its deliberate losses is operating with judgment. A team that cannot is operating on luck.

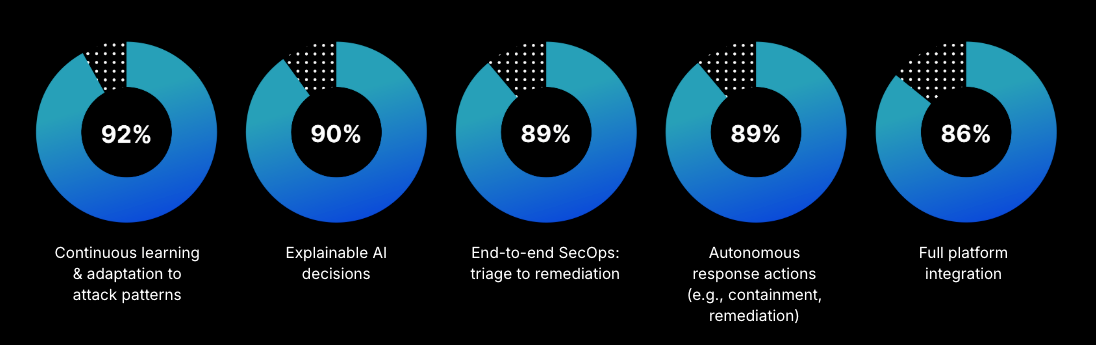
The uncomfortable part is that the industry measures almost none of this. In the SANS 2025 Detection and Response Survey, more than half of teams do not track mean time to detect or respond at all, and many fall back on raw detection and incident counts, which measure activity, not decisions. Torq’s 2026 AI SOC Leadership Report, surveying 450 security leaders, found the same pattern from the other direction: 80% run disconnected point tools, 80% say that fragmentation creates operational complexity, and 85% would rather have one unified platform. Each tool holds a fragment of the picture, which leaves the analyst as the integration layer, stitching partial truths into something close to a single answer. 

Adding tools does not move the number that counts. Counting alerts closed is the security equivalent of counting swings instead of runs. It feels like progress, but it correlates with nothing.

“But choosing not to investigate is how you miss the breach.”

This is the objection a good detection engineer raises immediately, and it is right to raise it. If you bless deprioritization, do you not bless the exact gap an attacker walks through?

No, and the reason is the whole point. You are already deprioritizing, because today’s volume guarantees it.

The risk was never in choosing. It is in choosing blindly. A documented, risk-based decision to defer a class of low-signal alerts is auditable, reviewable, and improvable. You can look back after an incident, ask whether the rule was wrong, and fix it. An accidental gap teaches you nothing, because no one decided it and no one owns it. Deliberate loss is a control. Accidental loss is just exposure with better PR.

And the goal is not to celebrate the losses. It is to shrink them, and this is where the volume math changes. When AI triages every alert automatically, and investigation runs at machine speed, volume stops being the thing that decides what you skip. The analyst is no longer picking which alerts there is time to open. They are setting the bar for what the team is willing to let an automated verdict close, and reviewing what sits above it. The let-go set does not vanish; it becomes a threshold someone chooses. It never reaches zero, and pretending otherwise is how immature SOCs operate. Maturity has never meant having no residue. It means owning the bar that defines it, on purpose. You cannot own a bar you refuse to name.

Where to Start

Do not rebuild your program around a new model this quarter. Do one thing. Pick a single decision metric, time to decision or coverage of what actually matters, and instrument it for one alert type. Then, in your next operational review, ask the fourth question out loud: What did we choose not to chase, and can we defend it? The answer, or the silence, will tell you exactly how mature you really are.

Odysseus reached Ithaca because he was willing to decide which loss to take and to own it. The SOCs that will look mature in three years are the ones learning to do the same now, on purpose, with the receipts to prove it.

Next in this series: What actually changes when reasoning enters the loop, and how agentic investigation shrinks the set of alerts you are forced to let go.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

What We Learned Testing Jev on Security Alert Triage

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Yaniv Zimmer is an AI researcher at Torq, focusing on cybersecurity research at the crossroads of artificial intelligence, deep learning, and defensive operations. Drawing on extensive experience within Unit 8200 alongside industry and academic AI research roles, his work centers on advancing SOC AI architectures and threat detection capabilities

Like a lot of people, we were excited when Jev launched. The premise is genuinely useful in production: an intelligent language model built for classification.

One caveat before the results. Jev is a general-purpose classifier, and security alert triage is a narrow, unusually unforgiving task. We tested it on something it wasn’t specifically built for, and we think the findings say more about the limits of zero-shot classification in this domain than about Jev itself. 

We also ran into the problem the Jev team describes. Consistency is one of the biggest caveats in deployed LLMs, and in security alert triage, consistency is the whole game. When we tested frontier models on triage, the best of them classified consistently only 87% of the time. Run the same alert 10 times, and you will almost certainly get a miss.

Before Jev, we solved that with BERT encoder fine-tuning plus a few additional steps, which we call Torq Reflex. So when Jev was announced, we had an obvious question: Was that work unnecessary? Could we just use Jev instead?

We tested it. The answer is no, and the reason is worth sharing.

Prompt Sensitivity Is the Blocker

We saw that Jev is sensitive to its prompt. An instruction such as “label alerts as malicious only if you see concrete evidence” moved Jev from classifying nearly every sample as malicious to classifying almost none of them that way. For several naive prompts, it collapsed entirely and labeled every alert as a single class, which is a complete failure for a triage task.

That’s the gap between a model that performs well in a general setting and one you can put in front of a production alert queue. When output swings on a sentence of phrasing, the prompt is doing the deciding.

The Numbers

These are preliminary results on a sample of the open-source GUIDE-Microsoft IDS dataset — most specifically, randomly selected tenant n9, and a train:test 2:1 ratio for reflex, sampled with random seed=42.

We see the same trend measured on the full cohort, as well as on high-confidence alerts, where the cohort is determined by the model itself (top 80%).

ModelAccuracyWeighted F1Macro F1Malicious F1
Jev @ 0.821.13%21.92%20.40%3.73%
ModernBERT @ 0.810.33%1.93%6.24%18.72%
Gemini Flash @ 0.846.48%41.18%34.24%26.37%
Torq Reflex @ 0.880.28%76.93%69.95%71.43%
ModelAccuracyWeighted F1Macro F1Malicious F1
Jev 20.30%19.70%19.12%3.12%
ModernBERT 8.65%2.00%5.84%15.49%
Gemini Flash 50.00%46.07%35.18%25.00%
Torq Reflex 69.92%67.17%55.31%36.07%


Jev clearly improves on the earlier ModernBERT approach at the same threshold. But it falls short of the reasoning model (Gemini), and it falls well short of Torq Reflex.

It also scored below what you’d get by simply choosing the majority class. We read that as a consequence of the setup rather than a flaw in the model: without exposure to the data distribution, it has no learned priors for a domain where the priors carry most of the signal.

How We Queried Jev

The Jev query has two parts. The instructions and criteria contain the prompt and the classification options. The state holds the specific alert we’re asking the model to classify.

{
 "state": "GUIDE CLOSED-INCIDENT EVIDENCE ... (truncated)",
  "model": "Jev-latest",
  "questions": {
    "incident_grade": {
      "type": "choice",
      "instructions": "Act as a Tier-3 security analyst performing final incident triage. Classify the described behavior, not the mere existence of an alert...",
      "criteria": {
        "False Positive": "No concrete security-relevant behavior is described...",
        "True Positive - Benign": "A real activity is described and its behavior is best explained as authorized administration, expected software or user activity, testing, simulation, or policy-only activity...",
        "True Positive - Malicious": "Concrete supplied behavior or observables support attack activity, unauthorized access, compromise, harm, hostile infrastructure, or another adversarial explanation."
      }
    }
}

[Full prompt variants and the complete state payload are in the appendix, so results can be reproduced.]

Where Domain Priors Matter

Prompt sensitivity is one limitation. The other shows up when the evidence and the framing disagree.

Here’s an alert Jev correctly classified as malicious:

Alert: Suspicious PowerShell execution
Severity: High
Category: Execution
Description: Encoded PowerShell launched by a user process
Techniques: T1059.001 PowerShell
Obs: command=powershell.exe -enc <redacted> | parent=winword.exe

And here’s a near-identical alert, where only the title changed, which it also classified as malicious:

Alert: Legitimate PowerShell execution
Severity: Low
Category: Execution
Description: Encoded PowerShell launched by a user process
Techniques: T1059.001 PowerShell
Obs: command=powershell.exe -enc <redacted> | parent=winword.exe

The observables are the same in both cases. What changed was the framing, and the classification followed the framing rather than the evidence. A trained analyst weighs winword.exe spawning encoded PowerShell against what’s normal in that environment. A zero-shot model with no exposure to that environment has nothing to weigh it against, which is a property of the approach rather than a bug in any one model.

The Honest Pros and Cons

Jev has real advantages. The context window is larger than the 8K we’re working with in the encoder approach, and you don’t have to retrain when you introduce new labels, which matters if your taxonomy changes often.

The tradeoff is the one that decides it for security: you can’t fine-tune it to your environment or your analysts’ judgment. In triage, that judgment is the product. The knowledge that makes a verdict correct lives in your history and your team’s past decisions, and no prompt can substitute for it.

Why We Still Train

The era of decision-making models is here, and the idea behind Jev is a good one. We’ve been running a version of the same thesis with Torq Reflex, and these results match what that experience taught us: in a domain this specialized, the priors have to come from training rather than from instructions.

If you’re evaluating a platform that claims its AI learns, the question worth asking is whether it trains on your data or rewrites its prompt. Those produce very different results on day 100.

We’d genuinely like to compare notes with the Jev team and others working on this problem, and we’d be glad to see what a domain-adapted version looks like. These results are preliminary, the dataset is open, and we’re happy to share our full prompt set so anyone can reproduce or challenge them.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

From Agreement to Action: What’s Actually Stopping Us?

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Over the course of this series, I’ve laid out the case for a fundamentally different security operating model — one built around Outcome, Judgment, and Execution layers, where AI handles the execution at machine speed, and humans focus on the decisions that actually need them. I’ve argued that the CISO’s role is changing, that human-centric security no longer scales, and that the org chart needs to reflect where AI fits on the team.

Most of the CISOs I talk to agree with all of it. And yet many of them haven’t moved.

This is the piece I wanted to write most, because it’s the one I’ve lived. The gap between agreement and action is not a new phenomenon in security. But with agentic AI, the cost of that gap is compounding faster than it ever has before.

The Gap Is Not What You Think

When I ask CISOs what’s holding them back, I rarely hear “budget.” I rarely hear “we don’t believe in the technology.” I almost never hear “our board said no.”

What I hear is hesitation. And hesitation, in my experience, is not one thing. It’s a collection of smaller, quieter blockers that don’t show up in a slide deck but absolutely show up in the pace of decision-making.

It sounds like this:

“We’re waiting to see how the market shakes out.”

“We need to finish our current platform migration first.”

“We haven’t figured out who owns this internally.”

“I want to do a proper evaluation, and we just haven’t had the bandwidth.”

None of these are unreasonable on their own. But stacked together, they produce the same outcome as saying no without anyone ever having to say it.

Ownership Is the First Problem

In most organizations I’ve worked with, AI adoption sits in an awkward governance gap. Security wants it, IT has opinions about it, data teams think they should lead it, and the CISO knows they need it but isn’t sure whether it is a security or an enterprise technology initiative, or something else entirely.

When nobody steps forward to own the decision, the decision doesn’t get made. It gets deferred into a working group, studied for another quarter, and revisited at the next offsite.” And six months later, the CISO is still in the same position — agreeing that AI is necessary, attending the same vendor demos, and waiting for something to change.

Here’s what I’ve learned: whichever function grasps the nettle first will benefit most. Security is uniquely positioned to lead AI adoption because we already operate under the conditions that make it essential — relentless alert volume, machine-speed threats, and a structural inability to hire our way out. We don’t need permission from another function to solve our own operational challenges. We need to lead.

If security doesn’t step into that role, someone else will make the decisions for us. And they will optimize for their priorities.

Fear of Getting It Wrong

There’s a second blocker that’s harder to talk about: the fear of making a wrong bet.

CISOs are trained to be risk-averse. It’s in the job description. When the AI SOC vendor market is noisy, fragmented, and moving fast — when every vendor is claiming “agentic” and the analyst landscape is still forming — the safest-feeling move is to wait for the market to mature and let someone else go first.

I understand the instinct. I’ve had it. When I was on the practitioner side, the biggest thing that slowed me down was the lack of a clear framework for distinguishing between what was real and what was marketing. Every vendor had a slide that looked like the future. Very few of them could explain what happened when you actually turned it on.

But here’s the problem with waiting: the threat environment is not waiting with you. AI-augmented attacks are accelerating. The gap between your attack surface and your defense capability is widening every quarter you don’t act. And the accountability question — did you fail to adopt capabilities that would have materially reduced your exposure — is already being asked by boards and insurers. Regulators will follow.

Waiting feels safe. It is not.

The Market Has Shifted

Something has changed in the last 6-9 months: the hesitation is starting to break.

A year ago, at InfoSecurity Europe, the conversations I was having were exploratory. CISOs were curious but cautious. They wanted to understand what “AI SOC” really meant. They were doing research, comparing vendors, and trying to determine whether the category was mature enough to warrant a serious evaluation.

This year, the conversations are different. CISOs are coming in with approved budgets and set timelines. Some are skipping the proof of concept entirely and going straight to purchase — a signal that they understand the problem, they’ve done their homework, and they have organizational momentum behind them. The early majority is moving.

The organizations that acted 12 months ago are now operating at a fundamentally different speed. They have AI handling Tier 1 and Tier 2 triage around the clock. They’ve moved analysts out of repetitive ops and into roles where they apply judgment, not just process volume. They’re measuring outcomes, not activity. And they’re doing it with the same headcount — or less.

The question is no longer whether AI belongs in the SOC. The question is whether you’re going to design this intentionally or scramble to catch up.

What the Smallest Step Looks Like

If you’re a CISO who agrees AI is necessary but hasn’t moved yet, here is the most practical advice I can give: stop trying to solve the whole problem at once.

Pick one category of alerts. Something repeatable, consistent, and high-volume — phishing, maybe, or endpoint detections that follow a predictable pattern. Something where the decision criteria are clear and the risk of an autonomous action is low.

This is exactly where the Torq AI SOC Platform starts. Auto Triage ingests your alerts, filters the noise, and surfaces the cases that actually matter. From there, specialized AI Agents handle the investigation and response (within the guardrails you define), while your analysts focus on the judgment calls that need them. You don’t bolt AI onto your existing workflow. You start with an execution layer and build around it.

Set the guardrails, watch the output, and build confidence in the results. Measure what changes: time saved, accuracy, analyst capacity freed up, and then expand. Carvana is auto-resolving 100% of Tier 1 and Tier 2 cases. That’s what the trajectory looks like when you start with the right platform.

You don’t need a 12-month roadmap, a team reorganization, or buy-in from every stakeholder. You need one use case, one quarter, and the willingness to start.

Everything I’ve written in this series — the Outcome, Judgment, Execution model, the org design shift, the accountability conversation, the case that human-centric security no longer scales — it all becomes real when you take that first step.

The Window Is Closing

I want to end this series where I started: with a direct challenge to every CISO reading this.

You agree. I know you do. The data is clear, the technology is deployable, the market has validated it, and the threat environment demands it. The only thing between agreement and action is a decision.

The organizations that design around this model now will have the agility to operate at machine speed when it matters most. The ones that wait will try to bolt it on mid-crisis and wonder why nothing holds together.

The future of the SOC is humans at the edges and AI in the middle. The only question is whether you design that intentionally or let it happen to you.

Don’t let this be the year you watched from the sidelines.

Keep Reading John White’s CISO to CISO Series

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

How CISOs Should Brief the Board on AI in the SOC

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to that, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.

I’ve briefed a lot of boards, and I’ve watched plenty of sharp security leaders lose one. The strategy was sound and the spend was justified, but the room still went quiet in the wrong way because the briefing was built for a SOC standup rather than a boardroom.

Every serious conversation about AI in the SOC eventually reaches the board. Whether it lands depends on two things: a platform that can back the claims, and the language you use to make them. After 20+ years on the practitioner side, here are the four frames I’ve watched directors actually respond to, and the words I’d leave outside the door.

If you’ve followed this series, you know the scenario: More than 100 vendors now claim the “AI SOC,” most stop at triage or bolt chatbots onto legacy systems, and the AI SOC Apocalypse Manifesto laid out how to tell the real platforms from the pretenders. The boardroom is where all of that noise turns into a budget decision. Brief it well, and the platform you chose becomes an obvious yes. Brief it badly, and you hand the room a reason to wait another year, while attackers keep moving at machine speed.

Frame 1: Value and ROI

Boards don’t fund security. They fund business outcomes, and your AI SOC story has to connect to value creation as tightly as it connects to risk. The question in the room is simple: what do we get, and what does it cost?

So give them the all-in numbers, framed as risk-adjusted ROI. In plain terms, that’s three things: 

  1. What the AI SOC delivers (faster containment, more threats handled, capacity recovered without new hires)
  2. What a breach would cost the business if our controls fail
  3. What we spend to close that gap while keeping the business fast

Don’t frame it as money saved. Adding AI agents rarely means cutting analysts, so the honest story is one of incremental returns. For the extra you invest, how much more do you get back in threats handled, time to contain, and work closed within SLA? The capacity you free up gets redeployed into higher-value work, and that redeployment is its own line of value. Measured that way, security spend reads as protection for the bottom line, not a tax on innovation.

The line I’d use: “Here’s the value our AI SOC creates, here’s what a failure would cost us, and here’s what we spend to keep moving fast safely.”

Frame 2: Strategic Focus

Most boards have sat through a dozen AI demos and watched none of them reach production. They know pilot purgatory when they see it, and their patience is thin. Don’t walk in with a menu of experiments. Walk in with a short, ranked list of high-impact commitments tied to what the business already cares about.

In the SOC, that means being honest about where AI earns its keep — autonomous triage and response on the high-volume, time-sensitive work — and where it’s merely table stakes. Governance effort should scale with impact: an agent that can contain a host or disable an account deserves board-level attention; one that drafts a summary doesn’t. Showing the board you’ve drawn that line demonstrates focus rather than FOMO.

The line I’d use: “We’ve pointed AI at the few SOC outcomes that move the needle, and we govern each one in proportion to what it can touch.”

Frame 3: Risk Appetite and Governance

This is the frame that may be the most consequential. AI has crossed a line our governance habits haven’t caught up to: it moved from suggesting to executing. It triggers live workflows, queries production systems, and takes actions that affect the business, sometimes before a human reviews the output. Once a system acts, governance has to graduate from a static PDF policy to active permissioning — who can touch what, under which approvals, with what rollback.

The framing that works in the room is autonomy as a dial, not a switch. You widen it as trust builds: start with low-risk, high-volume processes, verify the outcomes against what a good analyst would have done, and expand layer by layer. That measured, risk-based approach is exactly what boards and auditors want to see.

Give the board the risks in plain language: data leakage, model abuse, integrity failures, model supply-chain exposure, and compliance pressure as rules, such as the EU AI Act’s high-risk requirements, take effect in August 2026. Then show the guardrails are formal: documented as policy, operationalized in the platform so they’re enforced automatically, and reviewed on a set cadence — not a set of good intentions in a Slack channel. 

Expect the board, and later the auditors, to get specific, so have the answers ready: What due diligence did we apply? Have we risk-assessed each process we’ve automated? Do we understand the data involved and the regulatory requirements around it? How do we evidence that what’s in place is working? The point that lands: as autonomy goes up, blast radius goes up, so governance has to scale with it instead of lagging behind.

The line I’d use: “As our AI started taking action, we tightened the guardrails to match: scoped permissions, human approval on high-impact moves, and a rollback for everything it does.”

Frame 4: Accountability and Ownership

The last question is the shortest: Who owns this? Boards want a single accountable owner and unmistakable role clarity across leadership. In nearly every AI incident I’ve tracked, the root cause wasn’t a purely technical failure. It was three executives in a room, each assuming the problem belonged to someone else. When it goes public, that confusion becomes the headline. The story isn’t “the model got it wrong.” It’s “no one was in charge.”

So bring a clean RACI. The business owns outcome and use-case risk acceptance; security owns the controls and monitoring; legal owns regulatory alignment; the AI solution owner sets standards and lifecycle governance; and the board owns oversight and risk appetite. For the SOC specifically, be explicit about who owns an autonomous agent’s actions, who reviews them, and how an escalation reaches this board.

The line I’d use: “Here’s exactly who owns the AI’s decisions, who reviews them, and how an escalation reaches this board.”

The Language to Leave Out

The fastest way to lose the room is to brief the board the way you’d brief your team.

Drop the jargon. “Agentic,” “LLM,” “SOAR,” product names, model names — none of it survives contact with a board, because directors don’t buy architecture; they buy outcomes. Drop the vanity metrics, too. Raw alert volume and integration counts measure how busy you are, not how protected the business is. And go easy on the superlatives. “Fully autonomous” and “revolutionary” invite skepticism faster than they build confidence.

Before any capability comes out of your mouth, translate it into risk, dollars, or defensibility. If it doesn’t map to one of these, it doesn’t belong in the room.

A Briefing That Lands in Three Slides

If you want a board briefing structure you can reuse, this is the one I keep coming back to:

  1. The risk. Machine-speed threats against human-speed response, in business terms.
  2. The move. An AI SOC that reduces exposure, expands capacity, and stays defensible.
  3. The proof. Your own before-and-after numbers — time-to-contain, capacity recovered — and the governance that backs them.

The AI SOC Decision Underneath the Briefing

The board conversation isn’t really about whether to adopt AI in the SOC. Machine-speed threats made that call for most of us already. It’s about which platform earns the risk, capacity, and defensibility story you’ll tell in that room.

This is where the AI SOC Apocalypse Manifesto‘s test follows you into the boardroom: If it can’t take action, it’s not an AI SOC. A triage-only tool can’t honestly promise a board faster containment, because it stops at the verdict and hands the real work back to your team. The same pretenders that look fine in a demo fall apart the moment a director asks, “So what happens after the alert fires?”

A true AI SOC gives you all of these frames at once. It reduces exposure by taking action across the full threat lifecycle. It expands capacity by handling the repetitive work, so your people can focus on judgment. And it stays defensible because every decision is grounded, logged, and reversible. That’s the platform that lets you walk into the boardroom with a story directors say yes to, and it’s the bar this series has held every “AI SOC” up against from the start.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Fal.Con 2026 Recap: CrowdStrike Finds Threats, Torq Finishes Them

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

The Torq team headed back to Vegas for CrowdStrike’s Fal.Con conference this week, and it quickly became clear that the conversation has moved past whether AI belongs in the SOC. This year, everyone wanted to know what happens after a detection fires and who actually closes the case.

That question is the reason Torq and CrowdStrike fit together so well: CrowdStrike finds threats, and the Torq AI SOC Platform finishes them. Here’s what stood out from the week.

The Gap in the Current SOC Model

We said it last year, and it was even more true this year. There are too many alerts, too few analysts, and too many threats slipping through the gap between the two. Detection has never been better. Closure is where teams still drown.

What changed in 2026 is the noise around the fix. The market is now crowded with “AI SOCs” that stop at triage — they summarize an alert, maybe suggest a next step, and hand it back to a human. That is not finishing the job. A CrowdStrike Falcon detection deserves a platform that carries it all the way from alert to closed case, automatically, and that was the bar everyone at Fal.con was measuring against.

What Everyone Was Talking About at Fal.Con 2026

Four themes came up at Torq’s Fal.Con booth.

  1. Finishing the job, not just flagging it: A CrowdStrike Falcon detection flows straight into Torq Auto Triage, then investigation, then response, then a closed case, with prebuilt CrowdStrike steps and no manual handoff in between. Watching an alert close itself is a different demo than watching one get summarized.
  2. Grounding agentic decisions in your SOC’s reality: Beneath Torq’s AI Agents sits the Torq SOC Brain™, the layer that makes autonomy trustworthy: the Context Graph models your environment, Torq Recall draws on your case history from day one, and Torq Reflex learns your team’s judgment over time. It is the difference between a platform that starts every shift from zero and one that remembers.
  3. Turning autonomy into a dial: Socrates orchestrates Torq HyperAgents® with transparent, auditable reasoning and analysts on the loop. The point that landed: autonomy is a dial you widen as trust builds, not an all-or-nothing switch.
  4. Bridging the SOC and the rest of the stack: Torq sits across CrowdStrike Falcon and other data sources to correlate, act, and manage data across the whole environment, not just one console. For teams running more than one data lake, that was the unlock.

Torq + CrowdStrike: Better Together

The Torq and CrowdStrike partnership runs deep. Torq’s AI SOC platform natively integrates across CrowdStrike Falcon detections, incident response, and vulnerability management with nearly 100 pre-built CrowdStrike steps ready to embed in Torq HyperAgents. There is no manual handoff between CrowdStrike finding a threat and Torq closing the case.  

While Falcon Fusion automates inside the CrowdStrike ecosystem, Torq orchestrates those signals across the entire security stack — spanning identity, cloud, email, and ticketing. A Falcon detection triggers endpoint containment and then coordinates action wherever else it needs to go across the entire SOC.

Above the integration sits Socrates, Torq’s agentic AI SOC orchestrator that reasons through an investigation, plans next steps, and closes nearly 95% of cases automatically. But the entire action plan still runs on Falcon-native data from detection to remediation: 

  • Detection: Falcon Next-Gen SIEM telemetry via CrowdStrike trigger
  • Investigation: Natural language hunting over Falcon telemetry through a Torq NGSIEM query agent
  • Response: Falcon Real Time Response commands executed from inside Torq
  • Vulnerability prioritization: CVEs from Falcon Exposure Management scores against CISA and NIST

Every alert triggered by CrowdStrike is fed into Torq Auto Triage for filtration and prioritization, and every security case gets AI case summaries, agentic investigation, and a full audit trail with explainable reasoning. The agentic decisions are based on the Torq Context Graph, building on Falcon telemetry with a real grounding in what’s true about the entire environment in that moment, and each alert allows the Torq AI SOC Platform to learn over time and produce more accurate responses. 

The Torq and CrowdStrike partnership is the difference between a detection and a defensible outcome, with:

  • 60-second average triage time
  • 60x increased triage velocity
  • 10x faster response
  • 95%+ of Tier 1 work auto-remediated
  • Near-real-time case management on CrowdStrike data

Onstage: What a Unified AI SOC Actually Looks Like

I had 20 minutes on the Fal.Con theater stage this year, and I used them to unpack a finding from Torq’s 2026 AI SOC Leadership Report: 94% of security teams now use AI somewhere in the SOC, the average team runs seven different AI tools, and 85% still say they want something different. 

During the discussion, we talked about the tension in those data points. AI adoption is high, and so is the confidence, but most teams still aren’t satisfied. The reason is that most “AI SOC” tools stop at triage, so teams keep adding another one to cover the next gap until they end up with disconnected solutions that aren’t seeing the full picture, or worse, shelfware. 

The data shows that it all comes down to trust and transparency in AI decisions. CISOs and security leaders need to see why AI reached a decision and how it got to that point before trusting it to actually act on the next one. When we asked those same CISOs what specifically they were looking for, the results were clear:

  • 92%: Continuous learning & adaptation to attack patterns
  • 90%: Explainable AI decisions
  • 89%: End-to-end SecOps: triage to remediation 
  • 89%: Autonomous response actions (e.g., containment, remediation)
  • 86%: Full platform integration

The answer: a unified AI SOC platform.

I walked through what transparent, end-to-end agentic SecOps actually requires — carrying an alert from detection through remediation on one platform — and how enterprises like Carvana, Valvoline, and Kenvue are operationalizing it in production today, using the Torq AI SOC Platform. 

See Torq + CrowdStrike in Action

Detection isn’t the hard part anymore. The advantage is in closing the case at machine speed, with a full audit trail behind every decision. CrowdStrike finds it. Torq finishes it. If we missed you at the booth, we’ll show you what that looks like on your own stack, running on your Falcon data.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO