How to Measure AI SOC ROI: Beyond Hours Saved

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.
Request a Demo

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to Virgin Atlantic, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.

Every CISO I speak to eventually arrives at the same meeting: the one where you have to show what the investment bought you. And almost everyone walks in to defend their AI SOC ROI with the same number: hours saved.

It’s the weakest number you can bring. It invites the obvious follow-up question about headcount, which you don’t want to answer because the answer is that you aren’t cutting anyone. Worse, it describes a fraction of what actually changed. AI SOC ROI means different things depending on who’s asking, and “how many hours did we save?” is only one form of return.

Here’s how I’d measure it instead.
Measure AI SOC ROI as an Incremental Return

Adding AI agents doesn’t mean firing analysts, so don’t frame it as money saved. Frame it as an incremental return: for the extra you spend on agents, how much more do you get back?

Take an illustrative team of 10 analysts, still overwhelmed by volume and short on coverage across controls and projects. Add an agentic layer at roughly the cost of two or three good analysts, and you can automate the vast majority of your team’s Tier 1 work. Those analysts are released from the mundane and repeatable work and reallocated to higher-value activities. Compliance improves because the team now covers more controls. Risk from machine-speed attacks drops because triage and response happen at machine speed. Re-motivated analysts start engineering and delivering new capability on timeframes you couldn’t have committed to before.

That’s a significant uplift across the board, and it would have taken a team twice the size under a traditional, human-scaled model. That’s the number to bring.

Run Two Dashboards, Not One

One transformation, two audiences. I’d split measurement into a strategic dashboard and an operational one.

The strategic dashboard tracks what the board cares about: what you spent, how headcount was reallocated, how far risk came down, whether control metrics are improving, and whether the auditors are satisfied. If you’re reporting upward, ROI might mean that risk thresholds are met, the likelihood of breach is reduced, the cost of exposure is reduced, and legal and regulatory obligations are satisfied. It might mean showing no increase in committed headcount while efficiency and control coverage both go up. It might mean proving you delivered this transformation alongside a tech debt program or an ERP onboarding without derailing either.

The operational dashboard tracks how the work itself has changed: how many people moved from operations onto projects, which roles were refactored into the new structure, and how far case resolution time has dropped. In one enterprise I know, that went from 30 minutes to two. Quality improves as well, because every case arrives enriched with more context before anyone makes a decision.

The link between the two is capacity. Freed capacity isn’t a saving sitting in a spreadsheet: it’s value you redeploy, and the strategic dashboard is where that shows up.

The Benefits Most CISOs Aren’t Measuring

The secondary effects are where a lot of the real value hides, and most teams never put a number on them.

Reallocated hours change your risk posture. Reduced exposure changes what the business sets aside for cyber insurance. There’s the story you tell a regulator, for example, about running strong, agentic security inside critical national infrastructure, and there’s the evidence you can produce for the EU AI Act and the Cyber Resilience Act. 

None of that is technical, and all of it counts. The business benefits matter as much as the operational ones.

Get the Right People in the Room

The measurement conversation can’t stay inside the SOC, and this is where I see good programs undersell themselves.

You need the GRC team, enterprise risk, and procurement involved. Often, you want your other vendors too, because they’re seeing reduced volumes and faster response on their side, and that’s evidence you can use. Bring in any IT outsourcing team that owns part of the process. Don’t forget the regulators. Each of them measures your success differently, and if you’re the only one defining the measure, you’ll define it too narrowly.

Score AI SOC ROI Across All Three Layers

I’ve written before about the three layers you’re buying with an AI SOC: outcome, judgment, and execution. Measurement works the same way, and each layer has a tangible, measurable benefit.

  1. At the outcome layer, you set risk reduction targets, machine-speed defense requirements, compliance obligations, and the confidence you need to demonstrate to your board, your regulators, and your insurers. These get defined up front and measured within the judgment function.
  2. At the execution layer, you measure the incremental return described above. That’s where the leverage lives, as long as you measure it the right way.
  3. At the judgment layer, you measure continuous improvement, decision quality, and audit transparency. Can the system show you its reasoning? Can you tune it? Does it get better? That’s the layer that tells you whether you bought a capability or just a tool.

If a vendor can only show you the execution layer and can’t speak to judgment or outcomes, the relationship will stall. That’s worth knowing before you sign rather than after.

The Org Change That Makes the Metrics Move

There’s a hard truth underneath all of this. Without organizational change, the metrics plateau no matter how good the technology is.

Adopt the three-layer model as a product approach. Lay out your services, define the capabilities that deliver them, and measure how every capability performs. Move people into roles that understand this approach — something service- and capability-oriented — and split them into connected teams that deliver on outcomes, execution, and judgment. 

The technology gives you the capacity. The organization decides whether that capacity turns into results.

Inaction Is Its Own Risk

At the very least, after all of this, have a plan. If your plan is not to adopt an AI SOC yet, you need a justification that stands up to scrutiny, and I’d challenge you to find one. Are you saying machine-speed threats aren’t a risk to your organization? Do you have the resources to cope with current alert volumes, let alone next year’s?

Look at how fast a machine-speed attack actually moves. If your first line of defense runs at human speed, you’re handing attackers the dwell time they need before you’ve begun to respond. The exposure that comes from standing still outweighs the risk of taking a first step in the right direction. A tentative, risk-based, well-planned move forward beats waiting for a certainty that isn’t coming.

Whatever you choose, run it like a program rather than a purchase. Start with the repeatable Tier 1 work that eats the most time, prove it, measure it in terms your board and your auditors care about, and expand as trust builds.

You need a plan. Start building it now.

The full AI SOC Buyer’s Guide has the measurement dashboards, the incremental AI SOC ROI model, and the questions to bring into the room with every vendor on your shortlist.
SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Torq For Good: Bringing GO Kart Gaming Stations to Niswonger Children’s Hospital 

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Maycie Belmore is Senior Content Marketing Manager at Torq, where she helps lead content strategy across the blog, social, and website. Maycie focuses on SEO and AEO content and turning complex topics like agentic AI and security automation into clear, practical content for security teams. Maycie is also a voice for the Torq brand through video, live webinars, and events.

Some days remind you why you do what you do, and sometimes that has nothing to do with your actual job.

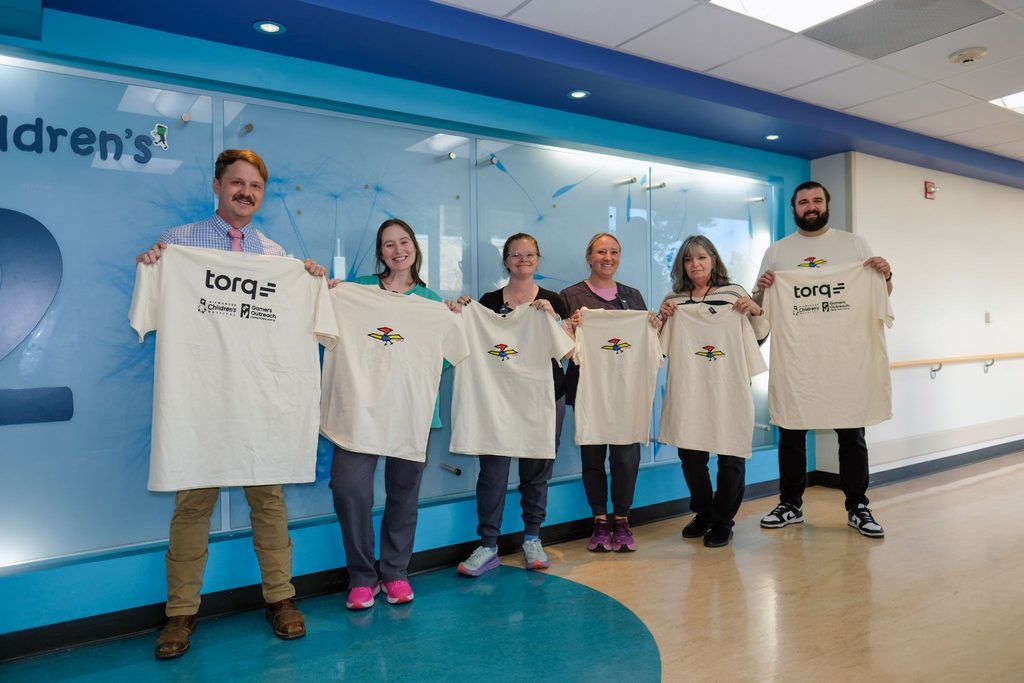
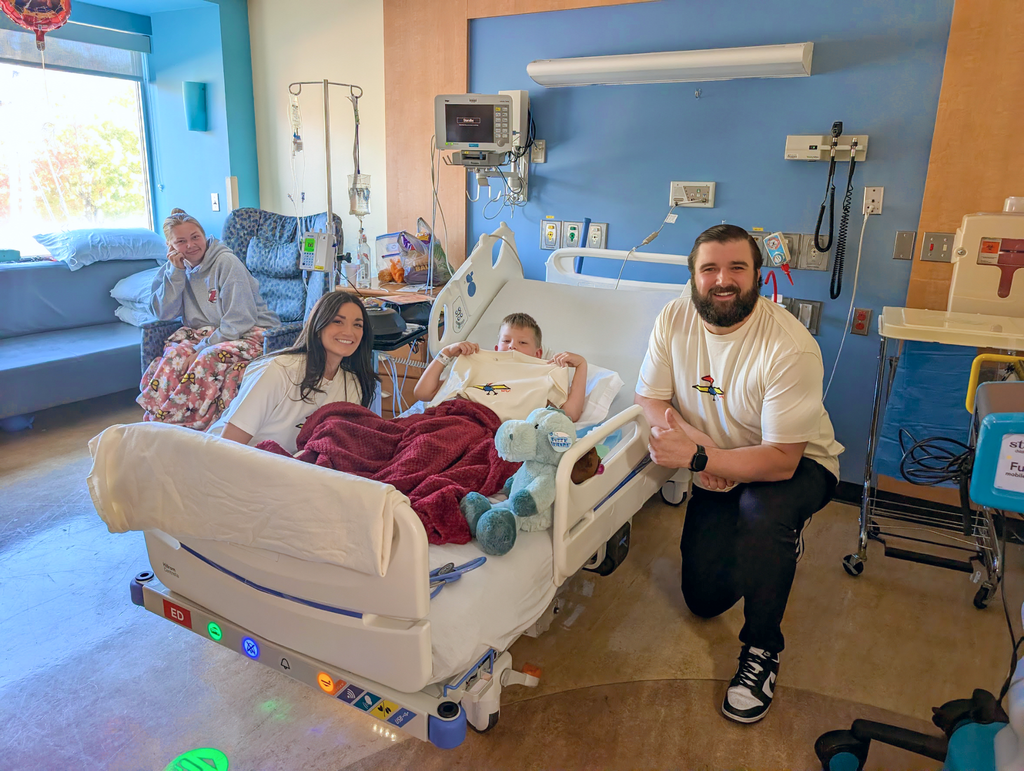
Torq For Good is our internal initiative to give back to local communities around the world. It builds on Torq’s previous investments in supporting young people and the next generation. This October, it sent my colleague Bob Boyle and me to Johnson City, Tennessee, to join something really special at Niswonger Children’s Hospital. It’s rare to have such an incredible opportunity to do something we don’t get to do every day. And I’m so thankful to work for a company that makes an effort to make a difference. 

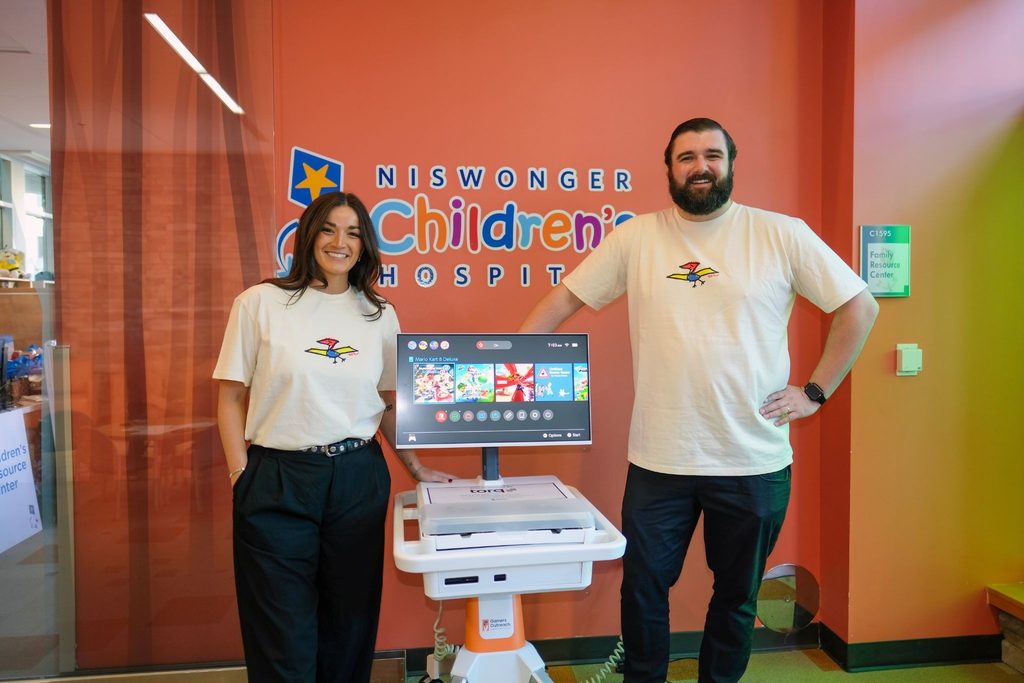
Torq teamed up with Gamers Outreach, a charity that empowers hospitalized families through play, to donate GO Kart multi-platform video gaming stations that roll right up to a patient’s bedside. Both GO Karts are permanent for the hospital, so patients can keep playing long after our visit. Gamers Outreach’s programs, including the GO Karts, support more than 350 hospitals and deliver over 8.4 million gaming experiences each year. 

Playing a video game might seem like the most ordinary thing in the world. But when a hospital stay keeps a child from school, birthday parties, and everything else that makes childhood feel like childhood, a game becomes something bigger. It gives them a chance to feel like a kid again. 

Our co-founder and CEO, Ofer Smadari, said it best: 

“Our team knows what great technology can do, but the best of it brings people together. For a child in the hospital, a video game is more than a game. It’s a way to connect with others, and forget for a little while where you are. Partnering with Gamers Outreach to put GO Karts in Niswonger Children’s Hospital is our way of giving back to a community that matters to us. We hope these patients and their families get a morning full of fun, and that the GO Karts keep that fun going long after we leave.”

– Ofer Smadari, Co-founder and CEO, Torq

Meeting The Team

Bob and I kicked off the morning at Niswonger Children’s Hospital, part of Ballad Health and the only children’s hospital in the region. It serves children and teens across East Tennessee and Southwest Virginia with state-of-the-art medical care in a family-centered environment, and it has been the region’s Children’s Miracle Network Hospitals affiliate for more than 30 years. There, we met Rodney Rhodes, the hospital’s Child Life Manager, and Jessica Fuller, the Media Relations Manager.

Next, Shanna Talaban from Gamers Outreach showed us around the GO Karts. These medical-grade video game kiosks are built for hospitals. Each one comes with Xbox and Nintendo Switch consoles, a monitor, controllers, and games, so patients can enjoy play as therapy during their hospital stay. Best of all, both GO Karts now live at Niswonger Children’s Hospital, so the kids there can keep playing every day, not only on event day.

The event also drew local media. Reporters from ABC TV affiliate WJHL News Channel 11 and Johnson City Press stopped by to hear about the joint initiative between Torq, Niswonger, and Gamer’s Outreach. I’d like to thank our fantastic PR agency Highwire for their help in creating community awareness for all the great work Niswonger and Gamers Outreach do.

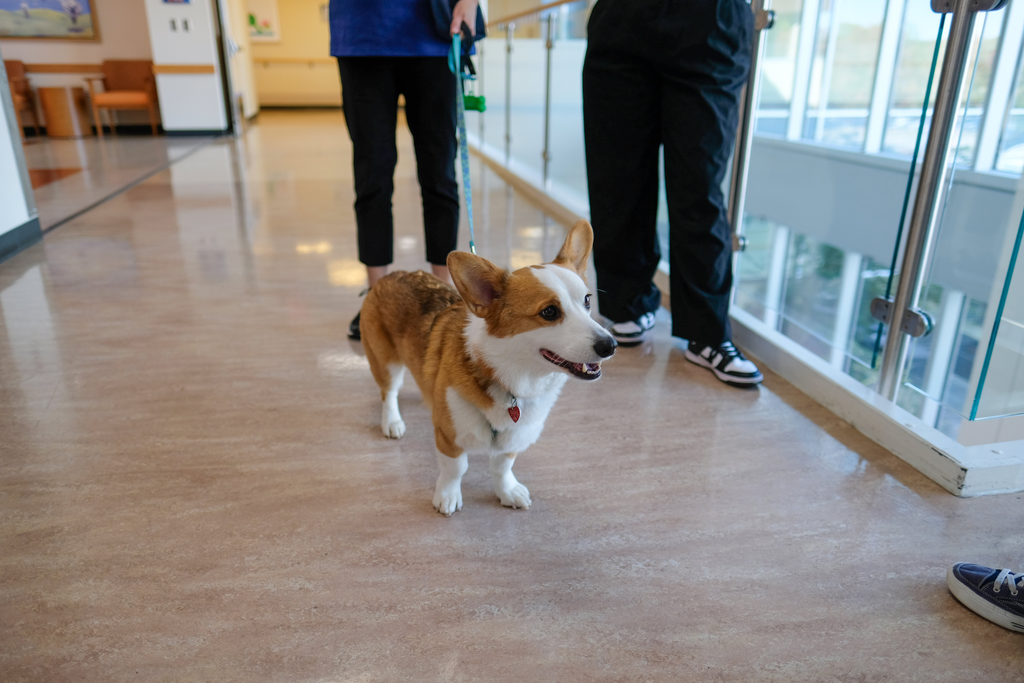
Everyone welcomed us so warmly, and their excitement to have us there was obvious. We even got to meet Rigby, the hospital’s therapy dog. He roams the hallways and bedsides and arguably has one of the most important jobs in the hospital.

Bedside with the Bravest Kids I’ve Ever Met

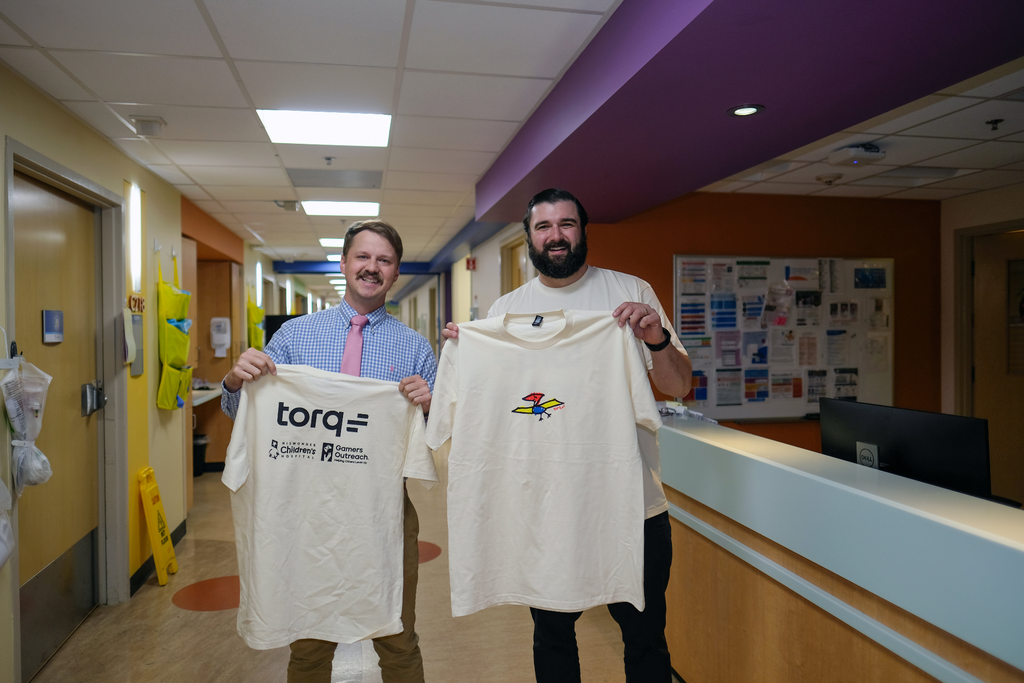
Then came the part I’ll carry with me the longest. We spent the day having bedside conversations with kids between the ages of 4 and 15. We built rapport, laughed, and passed out custom-made Niswonger Children’s Hospital + Torq t-shirts. 

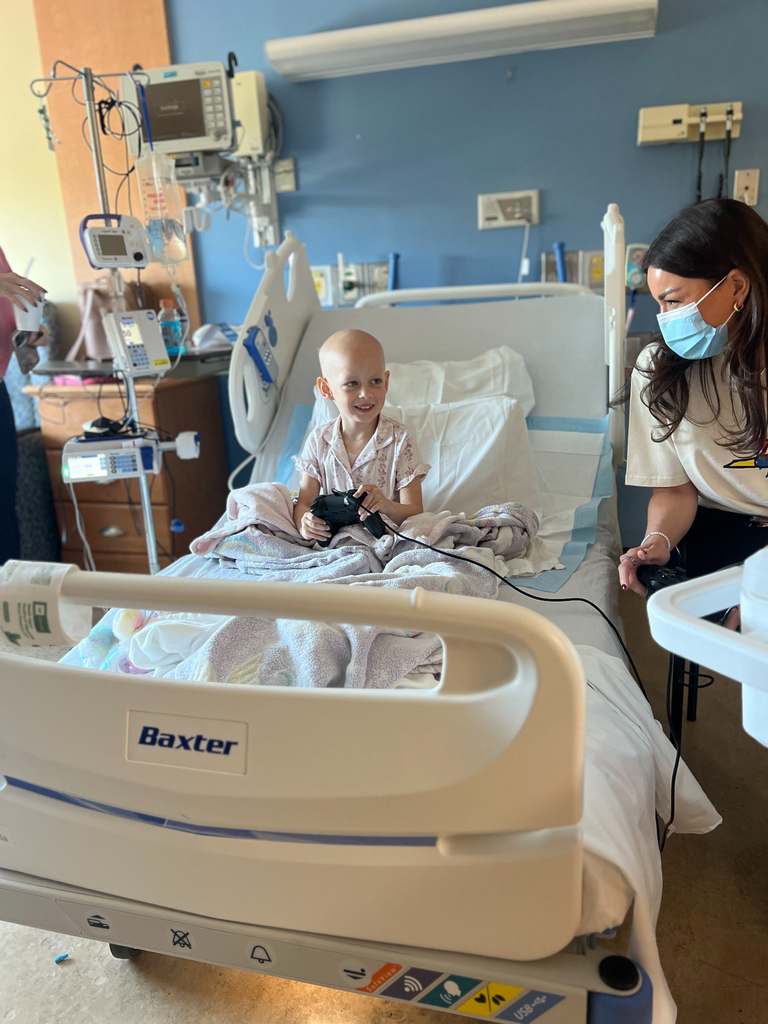
Seeing these children show so much bravery and strength through illnesses they shouldn’t have to face at such a young age was tough. But when we wheeled in the GO Kart and their faces lit up like Christmas Day, our hope came true: these kids got a moment to feel like kids again. 

That feeling stayed with me all day, especially when I met Isla, one of the younger patients I spent time with. She was new to Mario Kart Racing but after a quick lesson and a few giggles, she picked it up, and by the end, she was beating me! 

Rodney Rhodes, the hospital’s Child Life Manager, told WJHL that a gaming system can turn a day full of missed school and missed birthday parties into the highlight of a child’s week. 

And Bob and I watched that happen in real time. 

Giving Back Matters

Stepping out of our cybersecurity world and into a completely different one to give back showed me exactly why Torq For Good exists. Torq’s funding made this day possible, and it shows how businesses, nonprofits, and healthcare providers can work together to support hospitalized children, their families, and a wider community.

“True community support means showing up where it matters most. Thanks to our partnership with Torq and Gamers Outreach, our patients get an incredible experience filled with gaming, excitement, and shared fun. Bringing gaming right to the bedside brings so much joy to our children and reminds them how many people across Tennessee are working to help support their healing.”

– Rodney Rhodes, MHA, CCLS, Manager of Child Life Program at Ballad Health Niswonger Children’s Hospital

I’m grateful to work for a company that wants to make a difference. Torq spends its days protecting enterprises from security threats, but it also invests in the communities around us. Being part of Torq’s initiative of giving back, and traveling to Johnson City, Tennessee to see it firsthand, was a once-in-a-lifetime experience that Bob and I will carry with us forever. 

Thank you to Gamers Outreach, to Rodney and the team at Niswonger Children’s Hospital, and to every patient and family who welcomed us in. We hope the GO Karts keep the fun going long after we leave. They’ll stay right there at the bedside, ready for the next kid who needs it.

Want to read more? Check out the coverage from the Johnson City Press and WJHL (also on MSN).

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Torq Retrospect: Your SOC’s Past Shouldn’t Be the Price of Switching

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Noam Cohen is Head of Artificial Intelligence at Torq, where he leads the AI research and engineering work that powers the platform’s agentic SOC capabilities. Noam’s work at Torq spans the core AI systems behind autonomous threat investigation, SOC memory, confidence-based decision thresholds, and the guardrails that make agentic AI trustworthy enough to act in production security environments.

Key Takeaways

  • Moving to an AI SOC shouldn’t wipe out the case history your analysts spent years building.
  • Torq Retrospect uses an LLM once to learn the schema mapping, then copies records deterministically. It never rewrites them.
  • Unmapped fields are measured, and a human checks a sample before anything is called done.
  • One customer’s 2,000+ cases went from export to triage-ready in under an hour.

The new platform is approved. The pilot went well, the budget is signed, and the team is ready to move. Then someone in the kickoff asks the question nobody planned for: what happens to our history?

Three years of closed cases. Every alert someone already proved benign. Every host that turned out to be the red team’s box. Every incident write-up that explains why a particular 2am login pattern is fine for that one service account. That history is where most of a SOC’s hard-won knowledge lives, and it sits in a schema the new platform has never seen.

The usual approaches are both bad. Spend a month building a migration pipeline, or go live with an AI that knows nothing about you and let your analysts re-teach it from scratch. Plenty of teams pick a third option: they don’t switch.

We built Torq Retrospect so that the question has a short answer. Retrospect takes your case history from whatever system holds it today and rapidly makes it usable in Torq, already validated, indexed, and recency-weighted.

Every SOC Switch Starts With Amnesia

Think about the last time you set up a new phone. Ten years ago, that meant losing half your contacts and emailing yourself photos. Now you put the two phones next to each other, and twenty minutes later, your apps, messages, and photos are just there. Nobody would buy a phone that made them start over.

SOC platforms are still in the ten-years-ago era. Switching tools, whether from a legacy SOAR, a ticketing system, another AI SOC, or an MDR’s case portal, usually means your new system starts with an empty case history.

That matters more for an AI SOC than it did for older tools. A playbook engine doesn’t care what happened last year. An AI that triages alerts does. When it sees a suspicious PowerShell execution on a finance workstation, the most useful thing it can know is that your team saw the same pattern forty times last quarter, and every one of them was a patching script. Without that precedent, the AI reasons from first principles every time (and first principles are exactly what produces the false positives your analysts are tired of closing).

Traditional Migrations Move Data and Lose the Meaning

So teams migrate. Someone exports the old cases. Then the bespoke pipeline work starts: cleaning malformed records, matching the old fields to the new ones, deduplicating cases that were merged or reopened, and converting formats that never quite line up. Teams we’ve talked to say this takes anywhere from weeks to a month, and that’s when it goes well.

Time isn’t the only problem. A traditional migration has three ways to fail quietly:

  1. Loss in conversion. A field that doesn’t map cleanly gets dropped, flattened into a free-text blob, or truncated. Nobody notices until an investigation needs it.
  2. No proof it worked. Ensuring nothing is lost means building a validation process alongside the pipeline. Most teams spot-check a few cases and hope for the best.
  3. Imported isn’t usable. Even if every record arrives intact, the new system still has to find the right one at the right moment. Dump three years of cases into an index with equal weight, and the 2023 incident tied to a decommissioned server competes with last week’s case on the same alert type. The history is all there, and it’s mostly noise.

In 2026, there’s an obvious shortcut: Point an LLM at the old cases and have it rewrite each one in the new format. It sounds efficient. It also means a probabilistic model is regenerating thousands of records you may one day need in an audit or a post-incident review. One invented hostname or one “summarized” timeline, and your history is no longer your history.

We wanted neither.

Torq Doesn’t Recreate Your Data. We Learn How to Copy-Paste It.

The hard part of a migration was never moving bytes. It’s translation: working out that a field called src in one system, Attacker Address in another, and Origin IP in a third all mean the same thing in Torq’s data model. Field names across security tools agree only loosely. Some are obvious synonyms. Some mean the same thing only in context. Some look alike and mean different things.

That kind of loose-similarity matching is exactly what LLMs have become good at. So Retrospect uses the model where it’s strong, on the schema, and keeps it away from the records.

Retrospect works in four steps:

  1. The LLM reads both schemas. It sees your source system’s fields and Torq’s case data model.
  2. It proposes a mapping. Each source field has a destination in Torq’s model, including cases where the names are only mildly similar.
  3. The mapping becomes deterministic. Once validated (more on that below), it’s a fixed translation. Every record goes through the same rules.
  4. The records are copied, not regenerated. The value in your old system is the same as the value in Torq. The model wrote the instructions for the move. It didn’t touch the cargo.

The LLM’s work happens once per source schema, not once per case. That’s why the job takes minutes instead of weeks. It also means the thing you have to get right is the mapping, and you check it once instead of auditing every record.

Nothing Falls Through Without Someone Seeing It

A deterministic copy still raises the obvious question: what about the fields that don’t map?

Retrospect measures them. Every field the mapping doesn’t cover is counted as unmapped data, so coverage is a number you can read, not something you find out about three months later. If a source field has no home in Torq’s model, it shows up on that list. It doesn’t vanish quietly.
Then a human looks. Before the migration is called done, someone checks a representative sample of migrated cases against the source. The person checking reviews the translation on cases they recognize. They aren’t auditing a black box.

Silent drops and flattened fields, the things that make traditional migrations risky, show up before go-live instead of in the middle of an investigation.

Imported Isn’t Ready Until It’s Indexed

Getting the records across solves the first problem. Retrospect’s definition of done is stricter: the history has to be usable in triage and investigations the moment the migration finishes.

Migrated cases land in Torq’s case management already indexed, and the index knows when each case was created. Recent cases are more relevant than older ones. When Torq Recall looks for precedent on a new alert, last month’s resolution of the same pattern outweighs a two-year-old case from before your environment changed.

That keeps old data from turning into noise. You don’t need to curate your history before migrating it or decide which years are still trustworthy. Bring all of it. Recency weighting means the old cases are there when nothing newer matches, and stay out of the way when something newer does.

Two Thousand Cases, Under an Hour

One customer brought over 2,000 cases from the past year. With Retrospect, those cases went from export to imported, indexed, and ready for alert triage and investigations in under an hour. Compare that to the traditional, legacy path we described above — bespoke pipelines, cleaning, matching, and dedupe — which takes weeks to a month.

That’s just one customer’s migration. A messier source schema or many more years of history will take longer. The expensive part — translating the schema — still happens once, so more cases don’t mean more translation work.

Next, Your History Becomes Judgment

Torq Recall uses your history as memory: when a new alert comes in, it finds the precedent. That’s the first payoff, and it’s live from the hour the migration finishes.

The second payoff is Torq Reflex, which trains a model on your analysts’ past decisions, so that the AI actually learns your team’s judgment, instead of matching cases one at a time. It picks up the “we always escalate this one” instinct that no prompt captures.

A model like that needs decisions to learn from. Retrospect brings them across, each case with its analyst’s verdict attached. Your migrated history is the material Reflex learns your team’s judgment from, so it doesn’t have to start from zero after a switch.

What Torq Retrospect Means for Your Team

  • Switch without starting over. Your closed cases and their verdicts come with you, in Torq’s data model, from day one.
  • Minutes, not a migration project. No bespoke pipeline, no month of cleaning and matching. In the customer case above, it took under an hour.
  • Your records stay your records. The LLM translates the schema once. Your data is copied, never regenerated.
  • Coverage you can see. Unmapped fields are counted, and a human checks a sample, so gaps surface before go-live.
  • History without noise. Recency-weighted indexing puts recent precedent first, so you can bring everything without curating it.
  • The foundation for learning. The same history powers Recall today and gives Reflex the decisions it learns from.

Bring Your SOC’s Past With You

The reason teams stay on tools they’ve outgrown is rarely the tool itself. It’s everything they’ve built inside it. Every SOC that has switched platforms knows the cost: weeks of migration work, or a new system that has to be taught everything again.

The cost of adopting better technology is a thing of the past. With Retrospect, it doesn’t have to be.
Torq Retrospect is part of our series on Context, Memory, and Learning in the AI SOC, alongside Recall, Reflex, and the Torq Context Graph.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Everyone Says Context Matters. I Wanted Proof.

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Amir Kessler is Director of Product Management at Torq, where he leads the Context Engine and Data Fabric, the layer that gives the AI SOC Platform the organizational context it needs to investigate and act. He joined Torq with its acquisition of Jit, where he was VP of Product. Amir has spent more than 15 years in cyber, starting in IDF intelligence and going on to lead product teams at several security companies.
Before Jit became part of Torq, we built our product on one bet: an AI agent investigating a security issue is only as good as what it knows about your organization, including who an account really belongs to, what a server connects to, and what breaks if it’s compromised.

When Torq acquired Jit in May, I brought that bet into the SOC as the foundation of the Torq Context Graph and promptly hit a wall. “Context” is one of the most overused words in AI SOC marketing. Vendor after vendor claims it, with no details on what their ‘context’ contains and no proof of what it changes. To a SOC leader, my vision sounded like everyone else’s pitch.

So here’s what ours actually is. The Torq Context Graph is a live model of your organization that sits underneath every autonomous triage verdict in the Torq AI SOC platform, and it does three jobs: 

  1. Resolves the same person, device, or service across every tool in your stack into a single entity
  2. Maps the relationships between them (which service account can reach which privileged group)
  3. Computes the conclusions an analyst would otherwise work out by hand, like whether an account is dormant, a host is critical, or a user is a VIP 

All of it is kept current as the organization changes, and agents query it during triage instead of reconstructing it from raw logs on every alert.

That’s what separates the Torq Context Graph from most of what gets sold as context. An inventory tells you what you have, and enrichment adds a few fields to an alert. The graph tells the agent what those things mean together, before it makes the call.

Building context that holds up at enterprise scale is hard: every identity, device, and relationship must be resolved across the whole security stack and kept current as the organization changes. That’s the know-how Jit pioneered. But even a well-built graph doesn’t prove itself. I had to show where it moves the needle for an enterprise SOC. So I stopped making the argument and went looking for proof.

At one customer, the same alert kept firing: a Python script churning through batches of GIS map files. Without context, the Torq Auto Triage agent flagged it as suspicious scripting every time. With context, it came out three different ways, depending on what the graph knew about the user and host behind it. One of the three should have been escalated immediately. I’ll come back to it below.

Proof Starts With Real Alerts

ABOUT THE DATA
Every alert in this research came from a customer organization that opted in to share it with us, and every environment was anonymized. These are the alerts real enterprise SOCs face, with all their noise and edge cases — not a dataset built to make a slide look good. To every team that said yes: Thank you. You turned a claim into evidence.

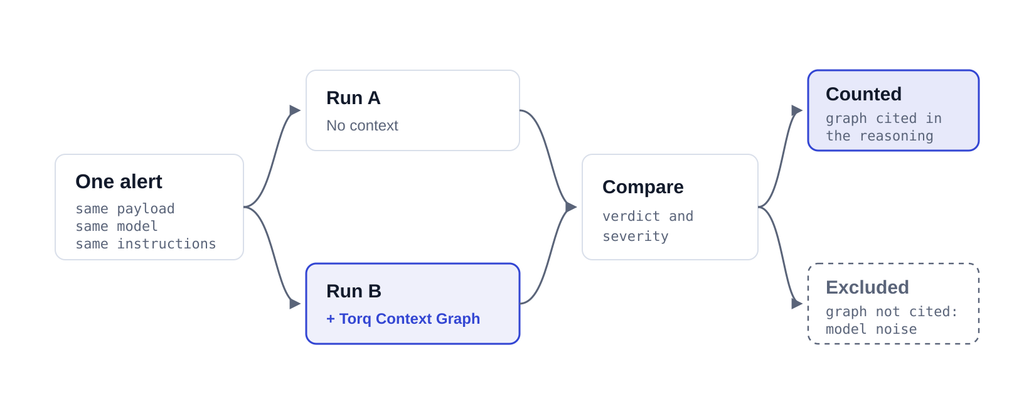
We sampled 400 alerts across customer environments of different sizes and verticals and ran the Torq Auto Triage agent on each one twice: same payload, same model, same instructions. One variable: access to the Context Graph.

The rule was strict. A change in verdict or severity only counted if the graph context appeared in the agent’s reasoning. Anything else was model noise, and we threw it out. Because the Auto Triage agent queries the graph during its analysis to test specific hypotheses, every change leaves a chain-of-reasoning trail: what the agent asked and what it learned.

FIG. 1   Each alert ran twice. Only changes the agent attributed to graph context were counted.

Nearly One in Four Verdicts Changed

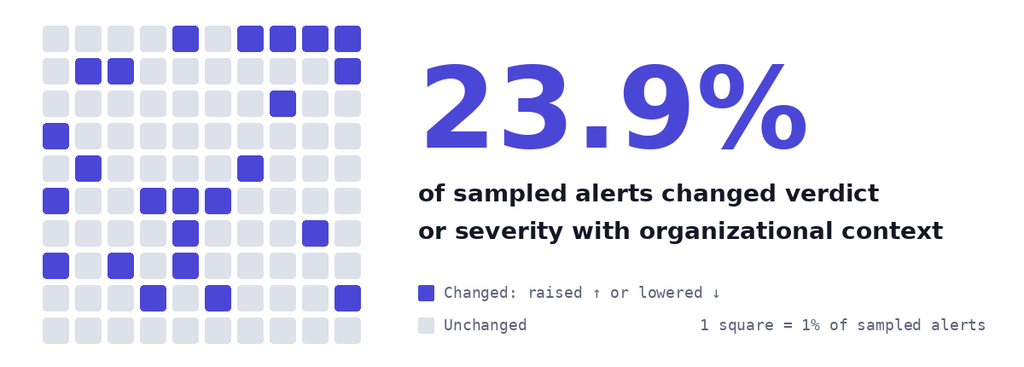
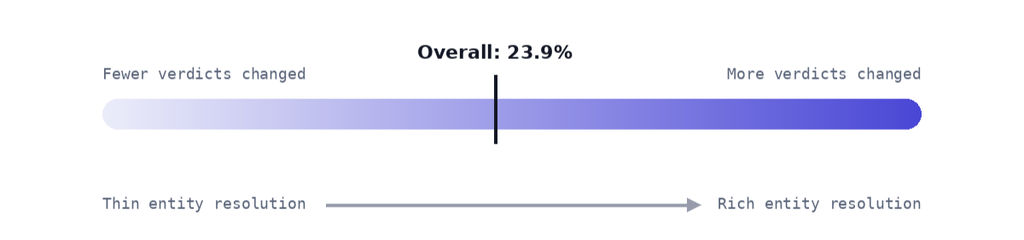
23.9% of verdicts changed. That’s where the risk lives. 23.9% of alerts changed verdict or severity once the agent had organizational context. Roughly one in every four.

FIG. 2   Share of sampled alerts whose verdict or severity changed with context. Square placement is illustrative.

That 23.9% is far greater than a rounding error. It’s the slice of the alert queue where the verdict was actually in play, and it’s where a SOC gets hurt. For every alert in it, the verdict, without context, was at risk of being misclassified, requiring human oversight. When that error runs in the dangerous direction, a real threat gets closed as benign or left at the bottom of the queue. That’s how attacks get missed.

The rate varied by environment. The spread tracked one thing: how many of the alert’s users and devices the graph could resolve to known entities. Environments where the graph could identify most of them saw the most changes in verdicts.

FIG. 3   The more of an alert’s users and devices the graph could resolve, the more verdicts moved.

Not Every Change Weighs the Same

Context pushed verdicts in both directions. Of the alerts whose verdict flipped between close and escalate, 53% went up to escalate, and 47% went down to close. Those two moves carry very different costs.

↓ Context lowers a verdict
Closed, deduplicated, or deprioritized. The SOC stops spending analyst hours on alerts that don’t need them, and at enterprise volume, that adds up fast.

Cost of the old verdict: Wasted time
↑ Context raises a verdict
An alert that looked routine gets pulled out of the noise and put in front of a defender, fast.


Cost of the old verdict: A missed attack

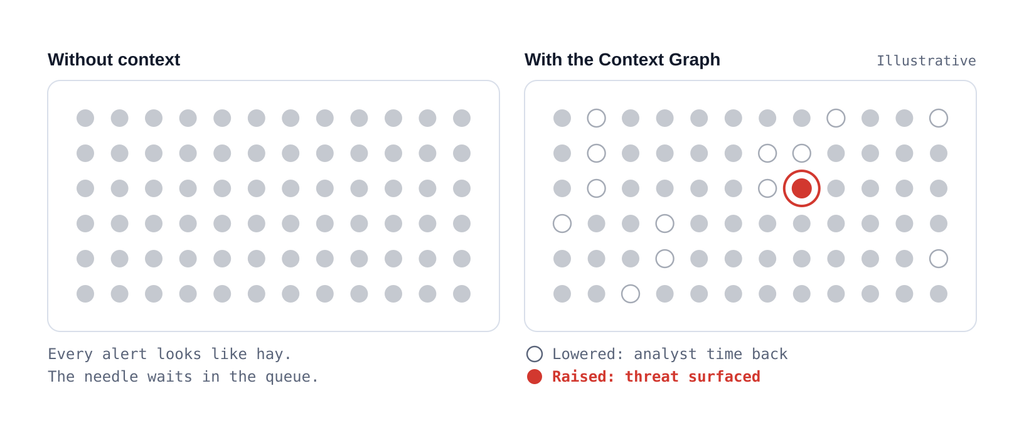
Lowering a verdict (e.g., to benign) shrinks the alert haystack. Raising a verdict finds the needle. Both matter, but the second is the reason a SOC exists. Every escalation that context drives is a defender one step closer to a threat that could otherwise have slipped through.

FIG. 4 Illustrative. Lowered verdicts take hay off the pile. A raised verdict moves the needle to the top of the queue.

What Moved the Verdicts

Almost none of the deciding signals were a field in a single tool. Each was a join, a path, or a computed conclusion.

SIGNALVERDICTGRAPH LAYER
Activity fits the user’s role↓ LowerResolution
“Suspicious” IP is the user’s own managed workstation↓ LowerResolution
Entities already part of an open incident↓ DedupeRelationship
Dormant service account suddenly active↑ RaiseInsight
Server on a privileged admin path, MFA missing↑ RaiseRelationship + Insight
User or device the graph can’t attribute↑ RaiseResolution gap

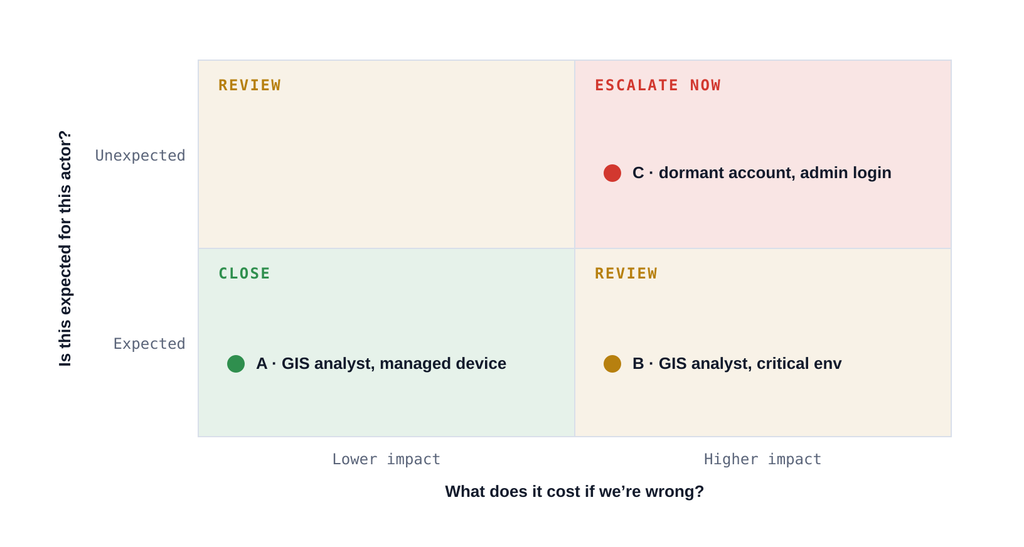
Each context layer answers a question analysts already ask:

  • Is this expected for this actor? Resolution.
  • What does it cost if we’re wrong? Insights: privilege, VIP status, criticality, posture.
  • Is this already known? Relationships. Closing here means “don’t escalate twice,” not “harmless.”

The first two did most of the work together. Expected activity, low impact: Close. Unexpected activity, high impact: Escalate now. Everything in between: Review.

FIG. 5   How the two main questions combine. The dots are the three alerts in the next section.

One Alert, Three Verdicts

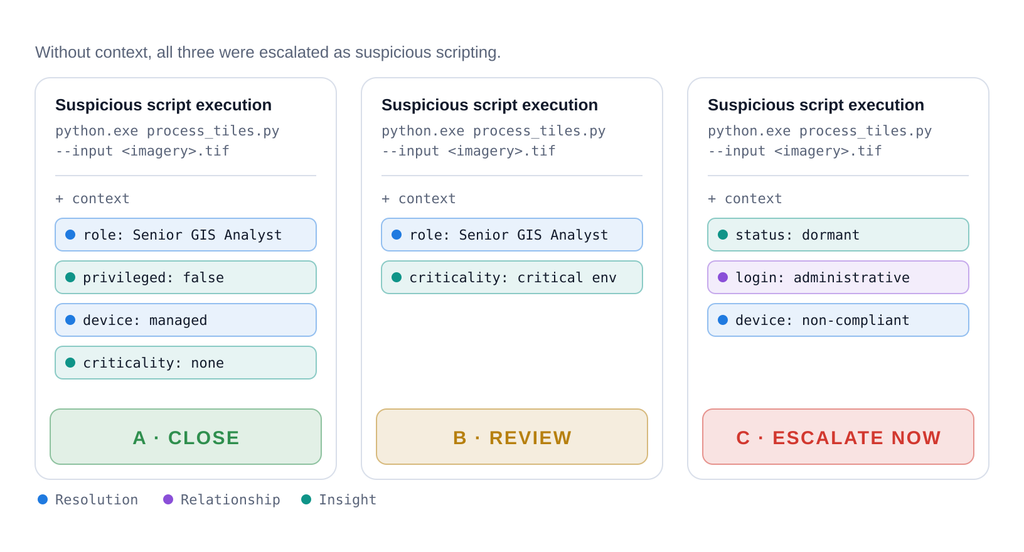
The clearest case was a recurring alert on Python scripts processing map imagery. Without context, these were escalated as suspicious scripting. With context, they split three ways.

FIG. 6   Identical process, arguments, and file types. Every fact that separates them comes from the graph.

A suppression rule or an allowlist would have closed all three, including the one that should ring the Batphone. Nothing in the alert distinguishes them. Everything that does is in the Context Graph.

“Can’t I Just Point an Agent at My Data Lake?”

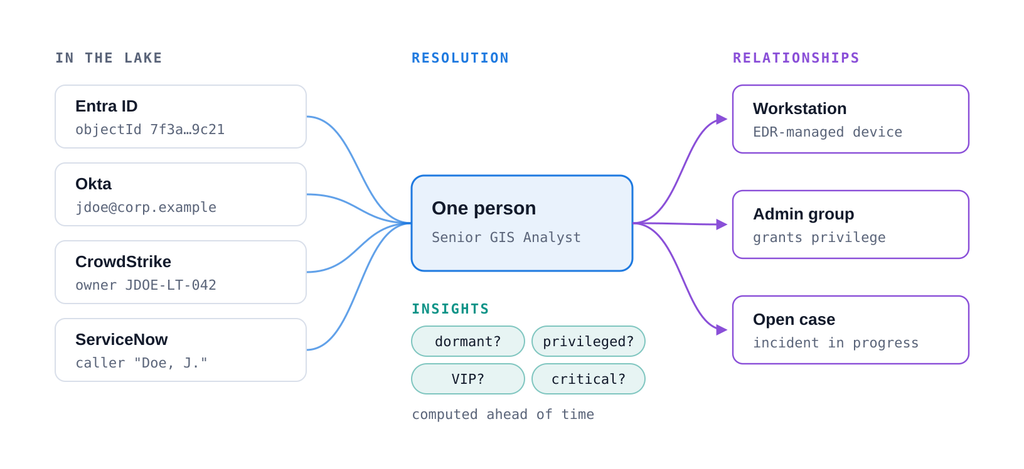
Your lake probably holds every source behind that table, but lacks what changes the verdict.

FIG. 7   Illustrative identifiers. The lake stores the records. The Context Graph knows who they belong to, what they connect to, and what that means.
  • Resolution. In a lake, one person is an Entra object ID, an Okta login, a CrowdStrike owner string, and a ServiceNow caller, with no reliable key between them. The agent would rebuild that match for every alert.
  • Relationships. “Tied to a privileged admin group” isn’t a row. It’s a path: host → service account → group → privilege. A lake stores the hops, not the path.
  • Insights. Dormant, privileged, VIP, and critical are conclusions, not fields. They must be computed in advance and kept current, not improvised within a triage prompt.
  • Rebuilding all of that per alert is also expensive and unstable. The agent spends tokens and time redoing the same joins on every alert, and two runs on the same alert can land on different answers. Whether two records belong to the same person, or whether a host sits on an admin path, should be a stored yes or no that the agent looks up.

Three Questions For Any Vendor, Including Torq

These are sampled, preliminary results. We measured whether and why verdicts changed, not yet whether every new verdict was right. Scoring both runs against analyst-confirmed outcomes is next, and we’ll publish it. I’m holding us to the same standard I’d ask of any vendor.

If a vendor tells you context matters, ask them:

  1. Which entities and relationships moved the verdict, and can I see them?
  2. Is the context resolved and computed ahead of time, or assembled from raw data per alert?
  3. What does the agent do when the data is missing?

If the answer is a claim without proof, keep asking.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

REV’d Up: Partner Stories

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

AI SOC Adoption: Where to Start in the First 90 Days

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to Virgin Atlantic, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.

You’ve signed the AI SOC contract. The question I get next is always the same: where do I start? What can I turn on without worrying about it, and what do I need to watch closely?

The instinct at the start of any AI SOC adoption is to boil the ocean, to point AI at everything at once and prove the whole thesis in a quarter. That’s how good rollouts stall. The faster path is narrower. Lead with agentic triage on the work that’s drowning your team, prove it, then expand as trust builds. Here’s how the first 90 days should go.

The First 90 Days of AI SOC Adoption

Start with why you bought the platform. What are you trying to deliver, and how will you know it’s working? Get your objectives on paper, look at the processes and the team you have, and start designing the plans, automations, and agent roles that will deliver them.

Deploy agentic triage on your highest-volume Tier 1 alerts. You’re putting the plan into practice, pulling people together on a project basis, and working out whether it’s performing. Some of them will start moving into roles that aren’t in their current job description yet, designing the new structure as they go.

The basics are working, and you see real movement from human process to machine speed. Lead with agentic triage to shut the door on machine-speed threats before the noise ever crosses into your SOC, because that noise is what overruns the team first. In parallel, pick a handful of your most time-consuming use cases and automate them. That combination gives you the fastest return. This is also your first review period. You’ll have a board meeting inside these 90 days, and the C-suite, board, and audit committee will want to know what you spent, what you’re getting out of it, what the risks are, and whether there have been mistakes. Positive answers get you the green light to expand.

Start AI SOC Adoption With Triage

The best starting point for an AI SOC deployment is your highest-volume Tier 1 work: triage. It has clear processes, a clear track record of how alerts have been handled, and it’s the single biggest time sink in the SOC. Manually clearing noise is exactly the kind of high-volume, repeatable work agentic AI is built for, so agentic triage is the right first move rather than something you save for later.

There’s a compounding effect here that’s easy to miss. Automating your biggest time sink frees up hours your team can put into the next layer. You spend time now to get far more of it back later.

While triage is coming online, pick a few use cases that eat the most analyst time and automate them too. Whether each one is agentic or deterministic depends on the process. This is the quickest path to visible ROI, and it gives you something concrete to show the board alongside the triage numbers. From there, you pick off the next candidates one at a time.

When you measure it for that board conversation, be careful how you frame it. Adding agents rarely means cutting analysts, so this isn’t a story about money saved. It’s an incremental return: for the extra you invest, how much more do you get back in threats handled, time to contain, and work closed within SLA? The capacity you free up gets redeployed into higher-value work, and that redeployment is its own line of value.

Build Trust Process by Process

You don’t earn autonomy in one move. You earn it one process at a time. When outcomes match expectations and nothing goes sideways, trust builds. You’ve shown your C-suite it works, so you can sell the next phase with evidence instead of enthusiasm. Continual results earn continual buy-in.

This is also where the org starts to change, and it’s worth planning for deliberately. The analysts who set up autonomous triage are the ones who understand it best, and they move into Tier 2, engineering, and assurance roles as the layer matures. I wrote about that shift in detail in the AI SOC org chart, so I won’t repeat it here, but keep it in view: the platform handles the work, and you redesign the team around what that frees up.

The Mistake That Stalls AI SOC Adoption

The common failure I see with AI SOC adoption is handing everything to AI agents at once, without a risk-based approach. Shore up the front door first, then expand deliberately. Try to do it all in one go, and you run out of resources, and you start confusing what’s running agentically versus manually, doing part of a process one way and part another.

Shore up the front door means exactly what it says. Machine-speed attacks are already here, and human-speed response is the lag attackers exploit. Get your highest-volume triage running at machine speed, prove it, measure it in terms your board and your auditors care about, and grow from there. That’s how you turn a tool into an operating model and bring the organization with you.

The full guide lays out the 90-day plan, the measurement dashboards, and the questions to ask a vendor about how they’ve done this with other teams.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

REV’d Up: GuidePoint Security on the Modern SOC

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

REV’d Up is our series on the partners we team up with to help customers modernize their security operations — the resellers, distributors, GSIs, and MSSPs in Torq REV (Revenue Enablement Velocity), our channel partner program. Each post shares a partner’s perspective: who they are, the customer problems they focus on, and how we work together to solve them.

First up: GuidePoint Security.

It’s a fitting place to start. Security teams are stretched thin, facing rising alert volumes and threats that move faster than manual processes can handle. Helping customers navigate that and reach the outcomes they need is exactly the kind of work GuidePoint focuses on.

Meet GuidePoint Security

GuidePoint Security works with organizations of every size, from a few hundred employees up through Fortune 100 companies. Its approach is deliberately vendor-objective: the firm evaluates a wide range of security technologies so it can recommend what best fits a customer’s environment and goals. That work is backed by a team of certified engineers, architects, and consultants.

GuidePoint and Torq bring complementary strengths to the table. GuidePoint provides advisory and services expertise to help customers assess, deploy, and operationalize security technology, and the Torq AI SOC Platform gives them agentic AI and automation across the threat lifecycle, from triage through investigation and response, with analysts in the loop for decisions that require human judgment. Working together, the focus is the same: helping customers reach the security outcomes they’re after.

That partnership mindset is what Mateo Gutierrez, Senior Account Executive at Guidepoint, keeps coming back to. “It’s not just here you go, see you later,” Gutierrez said. “It’s much more of a true partnership with our customers: step by step, how is this going to impact your roadmap over the next three to five years, and how do we help you get there?”

Gutierrez is candid that customers face a lot of complexity, and they lean on GuidePoint for the expertise to work through it.

Focused on Customer Outcomes

Many security teams are fielding more alerts than they can clear and running more tools than they have the headcount to operate. Working together, GuidePoint and Torq help customers operationalize their existing resources so their teams can respond faster and focus on the work that matters most.

“Security teams have been underwater for a long time,” Gutierrez said. “When you can accelerate and automate the threat detection, investigation, and response lifecycle, organizations reach the outcomes they’re after without exhausting their resources.”

For GuidePoint, much of the value is in helping customers get more out of what they’ve already invested in. “So much of our job is helping customers operationalize what they’ve already bought,” Gutierrez said, “and get mean time to respond and mean time to resolve down from days to, hopefully, minutes.”

That time-to-outcome is what customers care about most. “What customers really care about is the ROI from a time perspective,” Gutierrez said. “How much investigation and containment can happen before a human even has to step in?”

As an example of what that can look like, a Torq live demo resolved an incident that would normally take two to three days start to finish in 15 minutes or less, with several integrations handling containment automatically.

Support That Continues After Go-Live

GuidePoint doesn’t hand customers a platform and walk away. They back the partnership with a technical bench that keeps tuning the deployment after go-live. “We have people who can support it from a services standpoint and continuously fine-tune it to reach those outcomes,” Gutierrez said. Because GuidePoint often helped the customer select the tools involved, it’s well positioned to bring everything together for them. “It’s lockstep,” he said.

Customers are modernizing their security operations, whether their partner leads that conversation or not, and GuidePoint is choosing to lead it. “I only see this partnership [with Torq] growing,” Gutierrez added. “It comes up in more and more of our customer conversations.”

Interested in partnering with Torq to solve customer challenges?

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

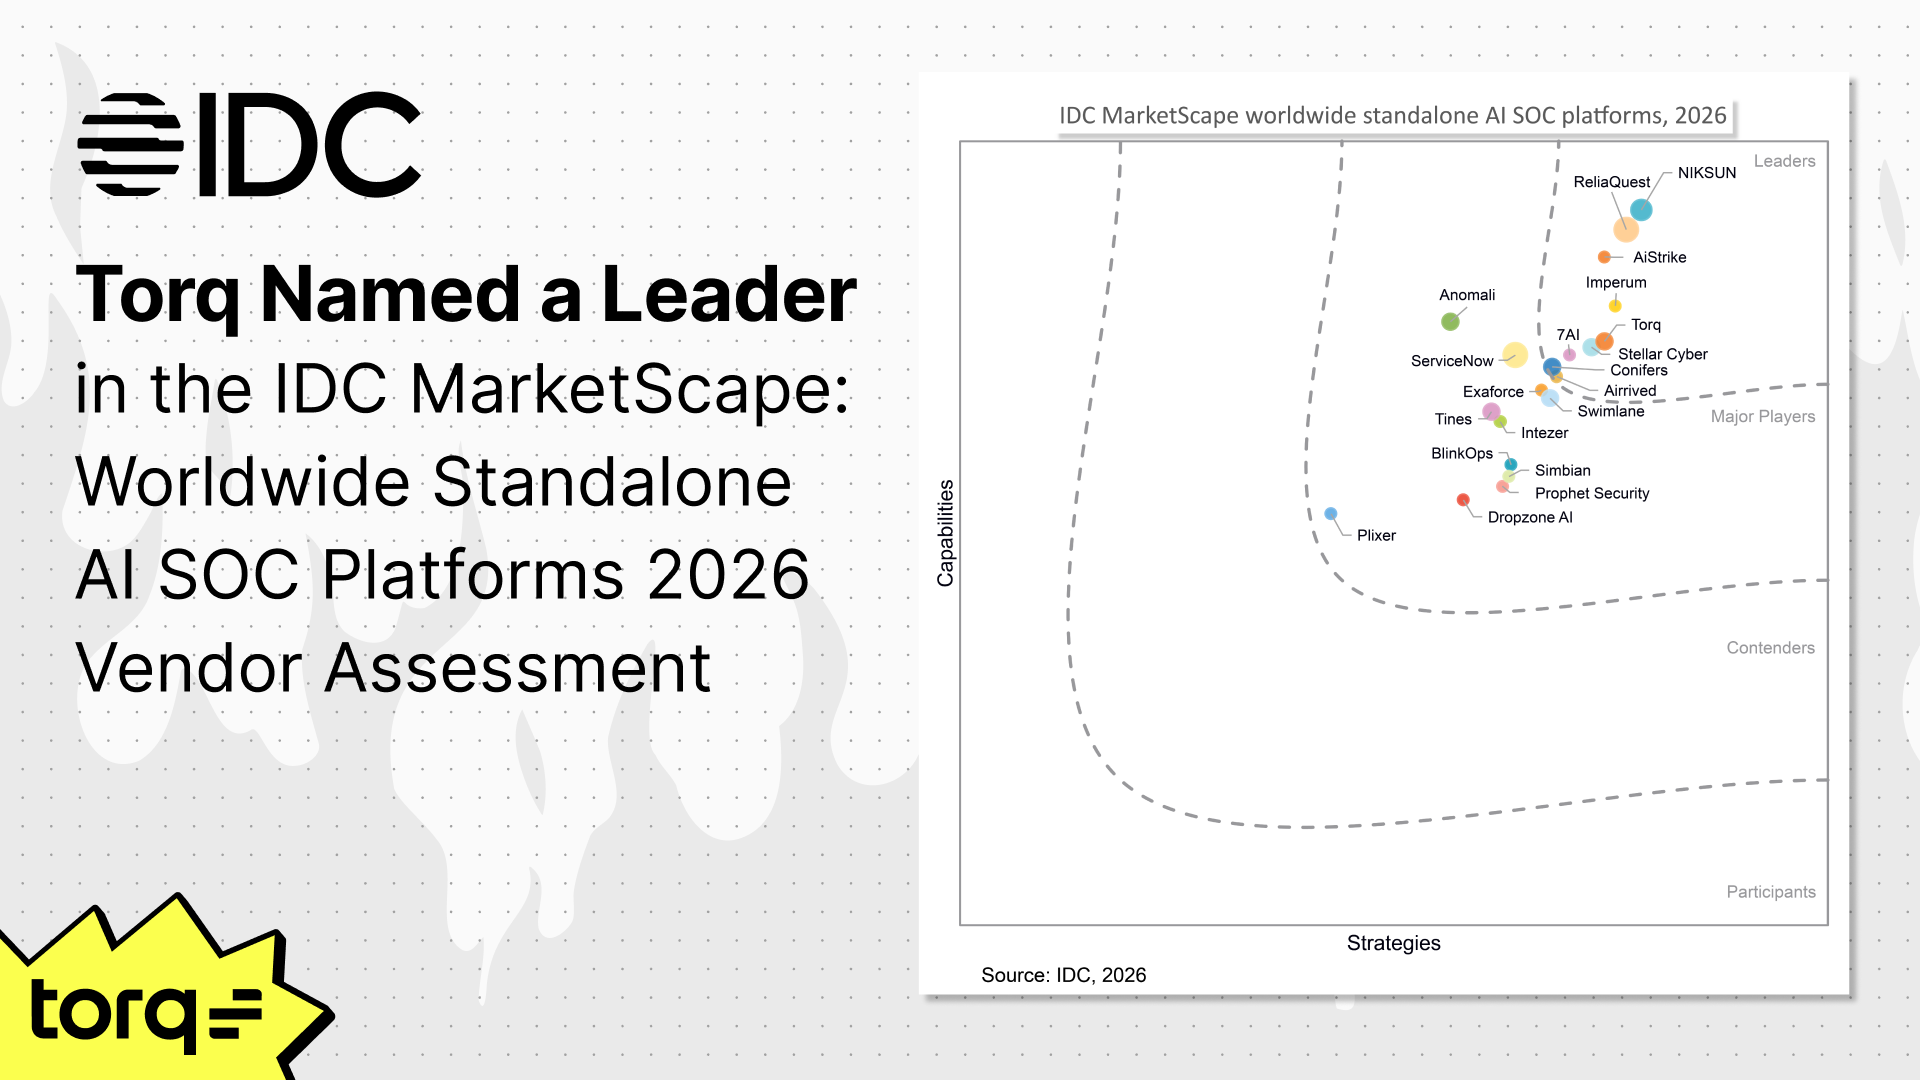
Torq Named a Leader in IDC MarketScape: Worldwide Standalone AI SOC Platforms 2026 Vendor Assessment

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Chris Kissel, Vice President of IDC Security & Trust, just drew a line in the sand for the AI SOC category with one simple sentence: 

“Vendors that can show their agents reason transparently, act within defined guardrails, and improve with each investigation will define this category. The rest will be measured against them.” 

We couldn’t agree more. That is the new bar for any AI SOC vendor to meet, and it is the bar that Torq has been building on top of since before anyone called the AI SOC a category: 

Transparent reasoning. Agentic action. Defined guardrails. Continuous learning. 

Building a platform based on these four essential pillars has already earned Torq leadership recognition in the AI SOC market. In April 2026, Torq was named a leader in all four categories in the KuppingerCole Analysts Leadership Compass for the Emerging AI SOC. In the May 2026 Gartner® report, AI Vendor Race: Torq Is the Company to Beat in AI SOC Agents for Threat Investigation, Gartner named Torq the Company to Beat, then doubled down with a report update in August 2026. And in July 2026, Software Analyst Cyber Research (SACR) named Torq a Leading Innovator in its 2026 AI SOC Market Report.

Most recently, in the IDC MarketScape: Worldwide Standalone AI SOC Platforms 2026 Vendor Assessment (Doc #US54127026), Torq was named a Leader.

This IDC MarketScape study assesses vendors offering standalone AI security operations center (SOC) platforms that meet the inclusion criteria of this study, scored against strategy and capability criteria built from vendor RFI responses, product demonstrations, and customer reference interviews. Let’s break down what the IDC MarketScape team evaluated regarding Torq AI SOC Platform in the report. 

Transparent Reasoning an Analyst Can Follow 

The IDC MarketScape notes, “Torq delivers its AI SOC Platform as SaaS, built around named modules, Torq Auto Triage, Torq HyperAgents, Torq Socrates, and Torq Case Management, that together handle ingestion, normalization, triage, enrichment, verdict, and response rather than centering on a dedicated detection data lake.” 

Alerts come in and are normalized to the Open Cybersecurity Schema Framework (OCSF). An alert-family classifier routes each alert to either a specialist pipeline for known types, such as EDR, phishing, identity, cloud, network, etc., or a generalist semantic chain-of-thought pipeline for anything that doesn’t fit a known category for the organization. Then, entity, IOC, and business-context enrichment run in parallel before a dual-verdict mechanism, Torq Reflex and Torq Recall, helps inform a final verdict. 

Policy-based routing dismisses false positives and creates comprehensive security cases, mapped to the MITRE ATT&CK® framework, for true positives. Every agentic decision is recorded and logged, viewable in real time, and audit-ready for analyst confirmation or correction. 

Each stage of this verdict pipeline is inspectable, giving analysts a traceable path from raw alert to conclusion, rather than an opaque black-box scoring system, on any given alert. According to the report, “Rather than a single black-box model, verdicts move through a structured, multistage pipeline: ingestion and OCSF normalization, alert-family classification into either a specialist pipeline for known types, EDR, phishing, identity, cloud, network, or a generalist semantic chain-of-thought pipeline for anything else, parallel entity, IOC, and business-context enrichment, and a dual ML-and-RAG verdict mechanism, Reflex plus Recall, before MITRE ATT&CK mapping and policy-based routing produce a final call. Each stage is inspectable, giving analysts a traceable path from raw alert to conclusion rather than an opaque score, and the same pipeline underlies the storyboard view an analyst sees on any given alert.” 

End-to-end Threat Lifecycle Coverage

An AI SOC is a platform that applies agentic reasoning to triage, investigation, and response, compressing multi-console work into a largely automated workflow. Not triage and prioritization alone, but end-to-end SecOps. 

“Agentic technologies are compressing detection and response from hours to minutes, and speed is no longer optional.”

– Chris Kissel, Vice President, IDC Security & Trust

Torq’s AI SOC platform handles ingestion, normalization, triage, enrichment, verdict, and response rather than centering on a dedicated detection data lake. Instead of being locked into a single provider, security teams can consolidate autonomous triage, agentic investigation, case management, and response action (both deterministic and agentic)  into one system with Torq. 

The platform’s central agentic capabilities, Torq SocratesTM and Torq HyperAgents®, handle both autonomous and semi-autonomous response actions in the platform, including incident containment and case closure end-to-end.

Enterprise-Ready, With the Receipts to Prove It 

While agentic action is of the utmost importance in battling adversaries that have already begun using AI to discover vulnerabilities and chain exploits, the report makes it clear that agents that act within defined guardrails are equally crucial for enterprise security operations centers.

Most Torq customers build agents and automations through natural-language prompts via the Socrates Agentic Builder, which can generate a new integration in minutes. The Torq Socrates Agentic Builder builds production-grade AI agents, turning human intent into agentic outcomes in minutes. 

According to the report, “Customers build automation through visual no-code workflows, natural-language prompts via the Socrates Agentic Builder, full “as code” API and SDK access, or by bringing their own coding or reasoning agent through MCP and A2A protocols, a wider range of extensibility paths than a single-paradigm approach offers. The Agentic Builder can reportedly generate a new integration from vendor documentation in minutes, and the vendor cites hundreds of customer-built long-tail integrations created this way. Custom agent creation, Torq HyperAgents, extends this further with configurable tools, guardrails, and skills.” 

Transparent reasoning and this custom configuration are what give security teams the confidence to allow Torq HyperAgents to take action on behalf of their SOC, but for the largest enterprise buyers, it matters even more how the platform runs and who has certified it. Torq’s AI SOC platform runs on a multi-region, multi-availability-zone architecture spanning the U.S., EU, and APAC. 

According to the report, “Torq delivers its AI SOC Platform as SaaS, built around named modules, Torq Auto Triage, Torq HyperAgents, Torq Socrates, and Torq Case Management, that together handle ingestion, normalization, triage, enrichment, verdict, and response rather than centering on a dedicated detection data lake. The platform reached general availability March 1, 2026, and runs on a multiregion, multi-availability-zone architecture spanning the U.S., the EU, and APAC, with a track record of 99.99% availability over five-plus years and contractual recovery-time and recovery-point commitments.”

Torq applies safety guardrails not only to individual AI Agents but at the platform level to meet the demands of the individual complexities presented by each Torq customer, spanning some of the largest global enterprises such as Chipotle, Lego, Lowe’s, Macy’s, Marriott, Prudential, Siemens, Uber, Valvoline, and Virgin Atlantic. 

The report states the following as a strength for Torq: “Broad, AI-specific compliance posture. Beyond SOC 2 Type II, Torq holds ISO 27001, BSI C5 Type II, CSA STAR, HIPAA, and GDPR coverage, and was an early adopter of ISO/IEC 42001 which is the standard specifically for AI management systems. A named federal partner network, Merlin Cyber, Carahsoft, and BAE Systems, targets FedRAMP Moderate and High, GovRAMP, and DoD IL5 requirements, positioning the platform for regulated and public-sector procurement even while FedRAMP authorization itself remains in process.”

A Platform That Gets Smarter With Every Case

The report noted, “Torq names distinct techniques behind its verdict pipeline rather than describing machine learning generically: per-customer BERT encoder models on dedicated GPUs, a Contrastive-Loss and Weighted-Cross-Entropy-trained classifier, GEPA prompt optimization, and a reinforcement-learning model gym for ongoing calibration.”

This system is powered by the self-learning Torq SOC BrainTM, made up of Retrospect, Recall, and most notably, Reflex. Torq Reflex is the underlying technology responsible for learning a specific team’s judgment from every analyst correction rather than only updating prompts or looking up past cases. This means that when an analyst confirms or corrects a verdict, that judgment becomes part of how the agentic reasoning occurs for that customer, based on that customer’s own encoder model. 

As a result, Torq Auto Triage — the agentic engine that applies business context, threat intelligence, and known organizational history to deliver verdicts and suppress noise — matches an analyst’s corrected verdict at least 20% more often than the semantic-search approach more commonly leveraged by vendors in this category. 

Your SOC does not think, act, or respond like any other organization’s SOC, and the models making calls in it should not be trained as though they do. The Torq AI SOC Platform is the only AI SOC that is shaped by your analysts’ judgment, informed by your incident history, calibrated to your risk posture, and gets more accurate with every case your team works. 

Future-Proofing Your SOC by Design

The IDC MarketScape also includes a challenges section for each vendor profile. Here, the report notes, “Ransomware detection they noted as fully supported, yet the narrative states detection itself is “the primary domain of EDR,” with Torq enriching EDR telemetry with threat intelligence and business context rather than detecting ransomware natively; native DLP and data-anomaly detection is similarly noted as fully supported while the accompanying narrative describes it as dependent on third-party frontier model partnerships (Bedrock, Vertex, Azure AI Foundry, OpenAI, Anthropic) rather than a native engine. Both patterns leave it unclear what native detection signal, if any, the platform contributes absent those integrations.” This is both true and intentional. 

Enterprise SOC teams have spent years and a ton of money building out detection systems and a complete security stack. They have gone through cycles of deploying, ripping, and replacing security technologies that target endpoints, email, networks, and the cloud as new best-of-breed solutions emerge from the hundreds of vendors cycling in and out to fill the halls of conferences like Black Hat and RSAC. And most importantly, every enterprise organization has felt the pain of losing a senior analyst to the next chapter of their career, with years of priceless institutional knowledge walking out the door with them.

Torq’s job is not to replace those systems or those humans. Detection does not equal priority or action. Moreover, each detection tool has its own limited worldview of risk: EDR, CNAPP, IAM, etc. Instead, Torq’s value is in taking those signals and finishing the work — across triage, investigation, case management, and response — with agentic velocity to keep up with machine-speed attacks.

At a time when offensive AI is scaling as fast as defensive AI, organizations do not need another solution that generates noise. Instead, they need a platform that is going to ingest, prioritize, and reduce alert overload, false positives, and process limitations. Torq closes that gap and gives analysts the time back they need to focus on critical risk.

Squash the noise. Investigate agentically. Respond quickly. All in a fully controlled fashion, with AI that works with and alongside your team, learns your organization’s standard operating procedures, and future-proofs your security operations.

The Rest Will Be Measured Against Us

In the report, “A consumer products manufacturer’s cybersecurity architect described replacing a costly third-party MSSP and an existing SOAR with Torq, citing roughly $500,000 a year in combined savings, a “council” of models cross-checking severity verdicts, and close to 1,000 AI-generated SIEM tuning recommendations over the past year.” This is what Torq looks like in production.

Kissel is right to say that the urgency around the AI SOC category is no longer theoretical, and the gap between disclosure and exploitation continues to narrow. For organizations evaluating AI SOC platforms, this simply means the buying decision is being narrowed to those vendors whose reasoning you can inspect, with agentic response actions, guardrails you can control, and, most importantly, learning that compounds with every alert. 

These are no longer differentiators; they are the entry fee. Torq has been building a platform to meet that standard for years, and we believe being named a Leader in the IDC MarketScape for this category is the confirmation.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

The Autonomous SOC Was a Promise SOAR Never Kept

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

David Melamed is Head of Emerging Technologies at Torq. He joined through Torq’s acquisition of Jit, which he co-founded and has led as CTO since 2020, building agentic security on a production Context Graph. A cloud security veteran with 20+ years of experience, David previously held senior technical roles at Cisco (via the CloudLock acquisition) and MyHeritage.


For all the gods and monsters in The Odyssey, the ship mostly moves for one reason: men row it. Divine wind is promised often and arrives sometimes, but it never lasts. Sooner or later, the sail goes slack, and the crew bends back over the oars and moves the ship the only way that reliably works, by hand.

Security operations were promised a wind, too. We called it SOAR (which stands for Security Orchestration, Automation, and Response), and the pitch was that you would set it up once and the SOC would start to run itself. How convenient, right?

But… it never did. And understanding exactly why it did not is the difference between falling for the same promise a second time and knowing what to demand instead.

Here is the claim up front. SOAR’s automation worked. What failed was the idea behind it: that enough flowcharts, stacked together, would add up to a SOC that runs itself. The industry is about to repeat that mistake with AI, and the only protection is to demand proof before you buy the promise.

We Have Heard This Promise Before

SOAR arrived as the answer to the problem described in the first and second posts in this series: too many alerts, too few people, and decisions that would not scale. The pitch was clean: encode your analysts’ playbooks once, wire the tools together, and the machine runs the repetitive work while humans supervise. In a nutshell: the self-driving SOC.

Teams bought it, built it, and then found out what they had actually bought.

What You Actually Bought Was Maintenance

A playbook automates the steps a human mapped in advance. That works for the narrow, stable path: this specific alert type, this enrichment, this ticket, this case. But unfortunately, security does not stay on the narrow path. A new detection, a renamed field, an unexpected response from a tool, an edge case nobody foresaw, and the playbook breaks, usually quietly, and usually at the worst moment.

So someone has to keep it alive. Every integration change, every new alert source, every tuning cycle adds to a backlog of playbook upkeep. The automation that was supposed to free the analyst turned the analyst into its mechanic. Ask anyone who has lost a Friday afternoon to a playbook that broke because a third-party vendor quietly renamed a field. The work did not disappear. It just moved from investigating alerts to maintaining the thing that was supposed to investigate alerts.

And it shows up in the data, not just in the war stories: 80% of security leaders say they rely on disconnected point tools, 80% say that fragmentation creates operational complexity, and 85% would prefer a single unified platform. The wiring was never finished because in a stack that keeps changing, it never can be.

The Mistake Was Deeper Than Brittleness

Brittleness was the symptom. But the real reason SOAR could never deliver autonomy lies in the premise beneath it.

SOAR asks you to encode judgment as part of the flowchart. But the hard part of a Tier 1 analyst’s job is not executing known steps. It is deciding what to do when the situation matches no known step. That is judgment, and judgment is not a decision tree with more branches bolted on. You cannot pre-write the response to a case you have never seen. So the exact work that would define an autonomous SOC, handling the alert nobody scripted, was the one thing a playbook, by its nature, could not do. SOAR automated everything except the part that actually required an analyst.

To be fair to the category, orchestration and automation were never the problem, and they are not going away. Wiring tools together and executing a known response at machine speed is real value. The error was believing that enough of those wired-together steps would add up to judgment. They never do.

The Same Promise Is Back on the Table

Now a new generation of vendors promises autonomy again, and most of the demos look exactly like the self-steering ship: clean data, a confident verdict, a slide that says “autonomous.” The lesson from SOAR is not to stop believing in automation. It is that the promise and the proof are different things, and the gap between them only shows up after you have signed, when the platform meets your real stack, your real volume, and your real compliance rules.

So treat the new promise the way a burned crew treats a fresh guarantee of fair winds. Make it prove it holds in your environment before you trust it to carry the ship. Ask the questions a polished demo is built to avoid:

  • Can it reason across your whole stack, or only the clean slice on the slide?
  • Can it show its work, or only hand you a verdict?
  • Can you govern what it is allowed to do?
  • Can it prove impact with named customers and real numbers, not logos on a wall?

Torq published a list of 20 such questions for exactly this reason: the honest answers are what separate a real AI SOC from a repackaged one, and we would rather you ask them of everyone, us included.

What SOAR Could Never Do

There is one thing that genuinely separates this wave from the last, and it is not more automation. It is reasoning: the ability to make sense of context and work an investigation that no one pre-scripted, choosing the next step based on what the last step turned up, the way a human analyst does. That is the single capability a flowchart could never capture, and it is why the autonomous SOC is finally a real conversation rather than a rerun of 2016.

Odysseus got home the moment he stopped waiting for a wind to do the work for him and started navigating by judgment. Security operations are at the same point. SOAR was the last promised wind. What comes next is not a better flowchart. It is a different kind of propulsion.

Next in this series: From playbooks to reasoning, what agentic AI actually changes, and why it can finally do the one thing SOAR never could.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Three AI SOC Differentiators That Separate Real From Marketing

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to Virgin Atlantic, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.

Every vendor in this category now says the same word: agentic. I understand why. It’s what the market wants to hear. But when you’re the one signing the contract, “agentic” tells you almost nothing. I’ve sat on the buying side of enough of these conversations to know that the label and the capability are often two very different things.

The SecOps industry spent the last two years proving that a large language model can read an alert and produce a credible analysis on day one. That was a real breakthrough, and it was the relatively easy part. Every vendor now builds on the same handful of frontier models, so reasoning on its own no longer sets anyone apart. 

What’s harder, and what actually separates one platform from another, is the layer beneath the agents: the context that grounds a decision, the memory that gives it precedent, and the learning that teaches it your team’s judgment. A model that reasons well but forgets every decision it makes, misses the context of your environment, and never learns your analysts’ judgment will hand you confident wrong answers at scale.

You don’t need a data science degree to tell the difference. Three questions do most of the work, and they map to the three AI SOC differentiators that actually matter. Can the platform reason about your environment, learn from your analysts, and act with control? Context, memory, autonomy. 

Differentiator 1: Context: Can It Reason About Your Environment?

Not all AI reasoning is equal. The real differentiator is whether an AI SOC tool understands your environment or just processes your alerts.

The clearest way I’ve found to frame it is as a knowledge graph versus a context graph. A knowledge graph tells you what you have: assets, identities, network topology. That’s an inventory. A context graph determines what all of that means: the relationships, the interaction patterns, what’s normal and what’s abnormal in your specific environment.

Context in isolation leads to poor decisions. A phishing alert judged through your email gateway alone looks very different once identity data, endpoint telemetry, and network behavior feed into the same determination. That’s an architectural requirement, not a marketing claim: multiple data points reasoning together on one platform.

In an AI SOC demo, I’d ask the vendor to show me how the platform uses its integrations, where the data goes, and whether a single determination draws on more than one source or each integration sits in its own silo. The risk of not asking is ending up with something that carries an AI label but behaves like a collection of disconnected tools. A platform that can’t reason across your whole environment will make ‘confident’ decisions on partial information, and that’s worse than no decision at all.

Differentiator 2: Memory: Does It Learn, or Just Respond?

This is the question most vendors gloss over, and the one that separates a platform that scales from one that stays stuck at triage.

There are two kinds of memory that matter, and they do different jobs. 

  1. The first is precedent: Has your SOC seen this exact thing before, and what did your team decide? Torq Recall does this with exact matching on real observables like IPs, file hashes, and hostnames, so an old verdict only counts when it’s genuinely relevant. 
  2. The second is judgment: How does your team actually rule, and what evidence do they demand before they escalate? Torq Reflex learns over time and applies that learning to alerts it has never seen before.

The tell is what happens on day 100. An AI SOC platform that learns runs a continual improvement loop: it makes a determination, stores what it learned, and applies it the next time the same question comes up. What I call “the next better decision”. An agent without memory reasons from scratch every time. It may land on a good answer, but it doesn’t carry forward what it found or what your analysts corrected, so it re-investigates the same benign pattern next week and can call the same alert differently on Monday and Tuesday.

Here’s my favorite way to cut through it: product, not promises. Every vendor says their platform “learns.” Ask them to prove it. How are the models trained and maintained? Can you show me a case where past precedent changed a verdict? Can you show me the accuracy curve over time, not just a day-one benchmark? If a vendor can’t describe that ongoing work, the learning claim is hollow.

Differentiator 3: Autonomy: Can It Act With Control?

Every vendor claims to be autonomous. Two things decide it: whether the platform exercises sound judgment and whether it can show you the receipts.

Start with how the agents are built: their roles, permissions, purpose, and the environments and timings in which they can operate. Then ask how granular they are. Like a human analyst who accrues permissions across role changes and never gets them decommissioned, an agent with too much responsibility ends up with keys to too many kingdoms. What you want is precise control over exactly what data each agent can touch, which actions it can take, and under what conditions, with anything outside that carved into a separate agent.

Assurance lives in the audit trail. You need to inspect any point of a decision, see why it was made, and keep the ability to change it. When an analyst disagrees with an outcome, the system should accept the correction and fold it into the next determination. If you can’t get into the reasoning and change it, you’re looking at a black box, and a black box has no place acting autonomously in your environment.

The framing that matters most: autonomy is a dial you set, not an all-or-nothing switch. You start eyes-on and skeptical, verify the outcomes against what a good analyst would have done, and widen the dial process by process as trust builds. Where to draw the line between autonomous action and escalation isn’t the vendor’s decision. It’s yours.

The AI SOC Differentiators That Hold Up on Day 100

A real platform answers these questions with specifics. When you ask how it reasons, how it learns, and how it’s governed, you should hear about a bitemporal graph that stays isolated to you, deterministic retrieval that weighs signal strength, and a per-tenant model with a calibrated confidence score and an audit trail you can open. A vendor that can only give you “fully autonomous” and “self-learning” is deflecting.

The next model release won’t fix any of this. It’s in your environment, your history, and your analysts. That’s exactly why the AI SOC differentiators worth paying for sit beneath the agents rather than in them. A day-one demo can be dressed up by anyone. What tells you the truth is the foundation on day 100, after months of your alerts and your corrections have run through it. Ask who is still learning by then. And it all comes down to a simple test: If it can’t take action across the threat lifecycle, it isn’t an AI SOC.

Context, memory, and autonomy are the short-form AI SOC differentiators that matter. The AI SOC Buyer’s Guide turns them into questions to bring into the room, with the specific things to ask under each one.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO