SEE TORQ IN ACTION
SEE TORQ IN ACTION
See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

David Melamed is Head of Emerging Technologies at Torq. He joined through Torq’s acquisition of Jit, which he co-founded and has led as CTO since 2020, building agentic security on a production Context Graph. A cloud security veteran with 20+ years of experience, David previously held senior technical roles at Cisco (via the CloudLock acquisition) and MyHeritage.
Odysseus left Troy with a fleet and reached Ithaca with nothing, having lost every ship to the sea. While the war was won by force, the journey home was won by wits, and ultimately the fleet barely mattered.
Most security operations centers are still running their SecOps voyage the way Odysseus ran the war: more tools, more force, more signal. It is the wrong instinct, because the SOC bottleneck was never how much you can see. It is how fast you can decide.
You already agree with this. That is the problem.
Of course more tools won’t fix the SOC. Everyone knows that. “Tool sprawl” and “alert fatigue” have been on conference slides for a decade, and no security leader would defend buying their way to maturity out loud.
And yet the same people who nod along will buy another tool the next time a new threat class appears, stand up another console, and still report their program by how many detections fired rather than how many good decisions got made. A claim everyone repeats, but no one acts on, is not a consensus. It is a collective blind spot.
Tools are not the enemy, and a real coverage gap deserves a dedicated tool. The failure is reaching for a purchase when the real constraint is decisions, a move leaders may still knowingly make because a purchase is a single defensible act, and the system rewards visible action over structural change.
The first symptom is noise. Enterprise SOCs field thousands of alerts a day, and because the average SOC now runs seven AI-powered tools, with 80% of teams relying on disconnected point solutions, the same event often fires as duplicate alerts across several platforms with no shared context.
Most teams named false positives their single biggest detection challenge, and the rate is rising every year. That is the point, not a footnote. The flood is not raw blindness; teams can see plenty. But they lack the capacity to handle incoming alerts and make decisions fast enough to matter and with enough confidence to close the related case: is the suspicious PowerShell on a finance laptop an intruder or the IT team? Nearly two-thirds (62.5%) say they are simply overwhelmed by the volume of data.
The attacker is not waiting. Verizon’s 2026 Data Breach Investigations Report found that for the first time in 19 years, exploitation of vulnerabilities overtook stolen credentials as the top initial access vector, rising to 31% from 18% the year before, while breaches involving a third party climbed to nearly half of all cases. Verizon’s own read is blunt: the speed at which known vulnerabilities are now weaponized, accelerated by AI, risks a capacity crisis for security teams. The inflow is accelerating faster than any hiring plan can keep up with.
The consequence is not just wasted effort; it is lost coverage. Most analysts spend time manually sorting low-value alerts that should have been filtered upstream, ultimately leading to slow responses: about a third of teams (32.8%) take hours rather than minutes to respond to a threat. Hours are a losing trade against the velocity Verizon just described.
There is an easy answer on the market, and it is the wrong half. Speeding up triage is the win every tool sells, but automation that acts faster without proving when it is right does not remove risk. It simply relocates risk from a slow human to a fast machine no one has taught you to trust. Speed is not the hard problem. Earned trust is.
The other half of the equation is the people, and it is not fixable by hiring, because you cannot hire fast or cheaply enough.
The ISC2 2025 Cybersecurity Workforce Study, drawn from more than 16,000 practitioners, found that a third of organizations lack the resources to adequately staff their security teams, that skills gaps are now nearly universal, and that 72% of professionals believe cutting security staff materially raises the likelihood of a breach. The talent you do have does not stay: SANS found that 70% of analysts with five years or less of experience leave their roles within three years.
So the loop closes on itself. Volume overwhelms the team, the team burns out and turns over, institutional knowledge walks out the door, and the next analyst inherits an even larger backlog. You cannot hire your way out at the speed or price the math requires. The point is not fewer analysts; it is more decisions per analyst: people spending their hours on judgment calls only a human should make, instead of clearing queues a machine could clear.
It is tempting to call all of this a visibility problem. It is not, and the distinction is the whole point of this series.
Most SOCs are not blind. A great deal of telemetry exists, spread across dozens of consoles. But two things make “we can see it” a false comfort. First, raw data is not always easy to query in the moment, and the context that actually settles a decision often lives entirely outside the security stack. Confirming whether a flagged user is on approved leave means reaching into an HR system. Confirming whether that odd remote login was really an employee can mean pinging them directly. None of that is a detection feed, and none of it is one query away.
Second, even when the evidence is all technically available, someone has to assemble it. An analyst working on one alert pulls evidence from several tools, enriches the indicators, and checks by hand whether this signal connects to something the team has already seen, one pane of glass at a time.
Torq’s 2026 AI SOC Leadership Report, featuring 450 security leaders, puts a number on that bridging work: Analysts spend 8.6 hours a week validating and reconciling AI outputs across disconnected tools. That isn’t lost time. AI took over the old execution work, and 9 in 10 leaders say it has improved SOC workload. Those 8.6 hours are the new judgment layer.
The catch is where the hours go. Reviewing clear, explainable reasoning is time well spent. Stitching partial answers together across disconnected tools is not. Same 8.6 hours, and the difference is platform design. So a phishing verdict that should take minutes can sit for hours, not because the evidence is missing, but because assembling it is slow.
That is not a gap in what the SOC can see. It is a gap in how fast a human can gather scattered context, some of it outside the security tools, into a single judgment, and how little of that judgment survives the next shift change. Which puts manual correlation squarely on the decision side of the ledger, not the visibility side, and makes it one of the most expensive line items on that side.
Let’s return to the Odyssey for a moment. A day from home, Aeolus gives Odysseus a bag holding every storm wind, so only a fair breeze carries him towards his home in Ithaca. In sight of the shore, his crew opens it, certain it hides treasure. The freed winds blow the ship all the way back out to sea. The gift was real, but it worked only while one condition held; the moment reality stepped outside it, the tool did not just stop helping — it undid the progress already made.
That is the signature of static playbook automation. It executes the steps a human mapped in advance, so it runs beautifully while an incident matches the script and fails the moment one does not — quietly, at the worst time. Automation itself is not the issue here. The problem is that deterministic-only automation, where every branch is pre-mapped by a human, has no answer for anything unmapped. The fix is not less automation; it is automation that can reason rather than replay a fixed script.
But adaptive automation brings its own failure mode: a confident wrong answer. So the hard part is not the reasoning; it is proving when to trust it. (But that is the focus of a later post; I will get back to it).
Zoom out, and the pattern repeats. SIEM promised that centralizing the logs would surface the answers, and delivered more signal with a search problem. SOAR promised that automating response would let humans step back, and delivered brittle playbooks to maintain. XDR promised cross-domain correlation and delivered real value, but still left a human to decide what each correlated case means. Each added capability downstream of the real SOC bottleneck, so each moved the constraint rather than removing it. Automate the response, and the bottleneck moves to triage. Centralize the logs, and it moves to investigation. The decision was always the part that did not scale.
The honest test of any security investment is simple, and you can try it at home: Does it increase the number of correct decisions your team can make in a day, or does it just increase the number of things your team has to decide about?
Most of what the industry sold did the second while claiming to do the first. The tell is that more than half of teams still do not track mean time to detect or mean time to respond at all. The metric that would actually expose the problem is rarer still: time to decision — the gap between an alert arriving and a verdict someone will stand behind — as well as time to close the loop. Almost no one measures it. This series will argue that this, not visibility, is the binding constraint, and it will try to earn that claim post by post rather than assert it.
This is why buying the next tool out of anxiety can feel less like navigation than like adding one more ship to a fleet the sea will take anyway. The capability accumulates. The stack grows. And the thing that actually determines whether you get home, the capacity to turn scattered evidence into a decision to close, escalate, or contain, at the volume the sea throws at you, barely moves.
The cheapest first move is not another tool; it is a number: Start measuring time to decision, because you cannot fix a bottleneck you have never put a number on.
Troy fell to force. Ithaca was reached by wits. The rest of this series is all about the wits: how to define maturity by the quality of decisions rather than the size of the arsenal, what changes when reasoning enters the loop, how to let automation act only when it has earned the right, and how to govern it so autonomy strengthens the SOC instead of becoming its next attack surface.
None of that means visibility never matters. Real coverage gaps are real, and sometimes a new tool is the right call. The point is narrower and more useful: for most SOCs, the next unit of value is not another feed of signal; it is the capacity to turn the signal you already have into decisions, faster and more reliably, at scale. That is the voyage. Everything else is just another ship in a fleet the sea is waiting to take.
Next in this series: Why the most mature SOC in your peer group is not the one with the most tools, and how to measure the difference.
For the data behind the shift this series is built on, the 2026 AI SOC Leadership Report captures how 450 security leaders are rethinking tooling, trust, and the decisions that actually move their programs forward.
SEE TORQ IN ACTION
See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.
Financial institutions are some of the hardest environments to secure. They hold the data attackers want most, they run payment rails that a breach can freeze, and they answer to the most overlapping set of regulations in any industry. When one is breached, the damage runs past exposed records into systemic risk and lost customer trust.
The average financial-sector data breach reached $5.56 million in 2025, second only to healthcare and well above the $4.44 million global average. The attacks keep climbing. Nation-state groups tripled their pace against the sector and stole more than $2 billion in crypto over the past year. Over a third of financial services incidents now start with social engineering, and confirmed ransomware in the sector rose about 30% from 2024 to 2025, with the first quarter of 2026 up 76% year-over-year. AI is in the mix now too, showing up in 16% of breaches through automated phishing and deepfake impersonation.
The threat is obvious. Keeping up with it is where the traditional SOC model falls short, and where AI-driven financial services SOC automation earns its place.
Most financial institutions run more security tools and get more alerts than any team can work through by hand, and the compliance load only adds to it. Analysts wake up to a flood of alerts, interpret them manually, gather context across disconnected systems, and run response steps one tool at a time. That worked until the volume outpaced the team, which in finance it already has.
Slow response is what makes the gap between alerts and capacity expensive. Across industries in 2025, organizations took an average of 241 days to identify and contain a breach, and the ones that ran past the 200-day mark cost $5.01 million on average versus $3.87 million for those caught sooner. For a bank, the longer an attacker goes undetected, the higher the odds of a frozen payment rail or a fraudulent wire.
Plenty of institutions turned to legacy SOAR to close the gap and found it added work instead of removing it. Playbooks pile up, each one tied to a couple of integrations, and the maintenance load lands on the detection engineering team. The platform ends up recording manual effort rather than reducing it. That’s a big part of why 85% of security leaders now say they want a single, unified platform they can trust. AI-driven financial services SOC automation, done right, is how they get there without adding headcount.
The Torq AI SOC Platform uses agentic AI and Hyperautomation to run the entire threat lifecycle (triage, investigation, response, and remediation) under your team’s direction, with every decision grounded in context, logged, and reversible. For financial institutions, Torq does three things that matter most.
Together, that lets financial institutions automate their most critical, highest-volume work: fraud and wire-transfer defense, phishing triage and containment, ransomware response, and identity and access management, all with the transparency and control a regulated environment demands.
FICO, the global analytics and financial services company, shows what happens when a financial institution moves to a real AI SOC. Its 24/7 global SOC had been running on a legacy SOAR where 95% of the work inside its playbooks was still done by hand. The team needed integration depth, automation reach, and a real support partnership, and moved to the Torq AI SOC Platform to get all three.
The migration was scoped at 90 days and delivered in about half that time, with more than 100 playbooks moved and consolidated, many collapsing from 10 steps down to a single automation that produced the same output. Today, FICO’s SOC runs on Torq end-to-end, from autonomous phishing investigation to 24/7 monitoring across teams in North America and Asia, with compliance evidence packaged for every workflow.
The results line up with what most financial institutions are after:
“When another security leader asks me whether the move from XSOAR to Torq was worth it, I tell them three things. We have the integrations we need, and when we don’t, we build them. We can run our own AI models inside our own workflows. And the support. The Torq team is in our standup every single week.”
– Ernesto Ugalde, Senior Manager of Detection Engineering at FICO
Financial institutions everywhere face the same squeeze: machine-speed attacks, rising regulatory pressure, and SOC teams that can’t scale by hiring.
What actually helps is an AI SOC that acts across the full threat lifecycle, works with the stack you already own, and can prove every decision to a regulator or a board. Another point tool or a repackaged SOAR won’t get there. That’s what Torq built, and it’s already running in production across some of the most demanding financial environments.
FICO is one of them, and its results show what that looks like in practice.
SEE TORQ IN ACTION
See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.
Most agentic triage solutions hand you a verdict and stop right there. Maybe you get an alert ranking, maybe a severity score, maybe some light investigation, but you, as the analyst, still have to do the cleanup manually. There is still a mountain of evidence that needs to be gathered by hand, and a mountain of cases to dig through on your own. If you’re lucky enough to have cases created for you, great, but you’re still the one logging back into different security solutions to close alerts, tune configurations, and, most importantly, take action.
Whether you work in an emergency room or in a Fortune 100 enterprise security operations center, triage, by definition, tells you what needs attention. The limitation of a triage-only solution in SecOps is that you won’t have visibility into the overall scope of threats or what your team decided the last time a specific indicator of compromise appeared in your environment.
That is why enterprise organizations need a complete, end-to-end AI SOC Platform. Want to hear more about what that looks like? Check out:
Clearly, the AI SOC is one of my favorite things to talk about! But today, we are going to take a turn and actually talk about triage. Not your standard, LLM-wrapped chatbot — but true, agentic auto triage with a brain… Torq Auto Triage.
Here’s the thing about triage: It was always meant to be a compromise. The reason triage exists in the first place is that human analysts don’t have the bandwidth to handle deep investigations into every single alert at enterprise scale, so the triage step was born to differentiate which alerts were worth investigating and which weren’t.
The problem is that most triage-only tools baked that same compromise into their solutions. They applied agentic AI to the problem (too many alerts) but replicated the same old outcome (prioritizing only the most critical alerts).
But using AI to solve the problem means we don’t have to accept the same logic. With AI on our side, “triage” now can, and should, go much deeper than surface-level filtering.
When an alert enters the SOC, the analyst needs a complete picture of what happened, what it means in the context of the organization, and what the right next move is before anyone has to look at it. Sometimes, the move is still to flag it as a false positive and remove it from the queue. Other times, the correct flow is immediate escalation to a Tier 3 analyst or incident responder for critical action.
But between the obvious false positives and the critical escalations lies a bulk of ambiguous alerts that require investigation to resolve. And that middle ground is where Torq Auto Triage shines.
Torq Auto Triage applies organizational context, threat intelligence, and security case history to every single alert it receives, delivering increasingly accurate verdicts and suppressing noise. It is fully integrated with any of the near-limitless security solutions found in your SOC and, most importantly, into the Torq AI SOC Platform to drive deeper investigation, containment, and remediation actions.
Mean time to triage is 60 seconds, and customers running Torq Auto Triage report a 97% reduction in EDR alert noise and a 60x improvement in triage velocity.
Every alert that Torq Auto Triage ingests is normalized to the Open Cybersecurity Schema Framework (OCSF), with observables such as IPs, domains, file hashes, and user identities extracted immediately upon arrival. It then enriches each alert with OSINT and commercial threat intelligence, as well as your organization’s historical case data, before any verdict is even made. This is completely out of the box, meaning there are no manual enrichment playbooks or workflows to maintain.
From there, Torq Auto Triage weighs the observables and attack stage against your SOC’s history of similar activity — using Torq Recall to drive exact, deterministic observable matching and Torq Reflex to align with your SOC’s actual historical judgment calls — before coming to a verdict, all in under 60 seconds.
Each verdict includes a severity score, MITRE ATT&CK mapping, full agentic reasoning logs, and recommended next steps. To ensure VIP users are always treated as critical, regardless of what probability models and agentic reasoning might say, deterministic guardrails created by your team are always running in parallel and baked directly into Torq Auto Triage.
Once a verdict is made with Torq Auto Triage, there are a few paths forward in the Torq platform. True positives automatically become cases in Torq Case Management, with all the evidence, context, and next steps already assembled. The verdict is immediately encoded in the Torq Context Graph, visible for reference in both the Torq Auto Triage alert and the case itself. This means that, regardless of whether the case is assigned to a human analyst or handled by Torq HyperAgents®, neither starts from scratch.
Non-malicious findings do not become cases, but are similarly logged and stored for future reference. And every alert is auditable and reviewable by a human, so every confirmation or correction can become an intelligence signal that trains Torq Auto Triage — powered by the Torq SOC Brain — to continuously learn over time and improve accuracy with each alert.
Most agentic triage solutions perform roughly the same way on day 100 as they do on day 1,000, because every alert is treated as if it’s the first time the system has seen it. Analyst corrections from last week don’t change the way a verdict is made this week, because that institutional knowledge is buried in closed tickets across disparate security tools.
Torq Auto Triage is different because of the Torq SOC Brain™, the learning and memory layer built into every Torq AI SOC Platform. Every analyst confirmation and verdict redirection feeds back into a dedicated, per-tenant model that continuously trains on your human intelligence. The Torq SOC Brain, and in turn, Torq Auto Triage, accumulates your SOC team’s judgment over time and gets more accurate with each case your analysts work on.
The Torq SOC Brain is made up of three underlying technologies:
As a result, Torq Auto Triage accuracy scores improve from roughly 94% to 99% in a matter of weeks, so the longer it runs, the more it becomes your own SOC intelligence model.
Torq’s agentic Auto Triage delivers its full value when verdicts flow directly into the Torq AI SOC Platform — intelligent case management, containment agents, and autonomous incident response.
The investigations are more precise because the triage verdict was accurate and documented in the Torq Context Graph. The response is faster because Socrates and Torq HyperAgents have the full scope of the threat and the historical justification to back it up. The agentic decisions are validated and trusted because they all trace back to the same learning powered by the Torq SOC Brain.
Triage solutions that filter false positives and escalate everything else are stuck in their old ways. Torq Auto Triage takes it further — with every alert garnering the attention it deserves, every verdict improving the system over time, and every case fully ready for the escalation, containment, or response that comes next.
SEE TORQ IN ACTION
See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.
The organization at the center of this story is one of the most visited cultural institutions in the world, dedicated to preserving history and educating the public.
Protecting that mission — and the digital infrastructure behind it — falls to a lean security team responsible for everything: SSO integrations, email, endpoints, servers, applications, websites, and micro-segmentation across the entire organization.
It’s a wide surface for any security team to cover. It’s an even wider one when your institution’s global profile and cultural significance make you a target. Geopolitical tensions have driven an increase in cyberattacks against the institution, demanding a security posture well beyond what the team could deliver manually.
This is the story of how that team went from fully manual operations to automated threat blocking, identity lifecycle management, and endpoint response.
Before the Torq AI SOC Platform, the security team’s day-to-day was what you’d expect from an operation running without automation: reviewing logs by hand, writing custom scripts, pulling reports, working through spreadsheets. Every step required someone to touch it.
That meant threat response moved at human speed. A device querying a malicious URL would get flagged, but by the time an analyst reviewed it, confirmed it, and took action, a week had passed. A week of known, unresolved exposure.
The team initially looked at Torq for security playbooks to automate detection and response workflows that consume analyst time. Two things made it the right fit: it was faster to build in than native tooling, and the whole team could use it without specialized coding skills. For a security operation where everyone covers everything, that accessibility was a requirement.
The museum undertook a major overhaul of its identity infrastructure, migrating from Active Directory–sourced accounts to Okta as the primary identity provider. It’s the kind of migration that touches every user, every application, and every access workflow in the organization.
The problems surfaced almost immediately. When users didn’t respond to Okta’s verification prompts within the predefined time window, their accounts were automatically flagged, and email access was locked. For a museum with staff across departments — curators, educators, researchers, operations — lockouts stalled work, frustrated employees, and generated a cascading queue of support requests.
The obvious fix was to build an automated workflow in Okta itself. But Okta Workflows is its own ecosystem, time-intensive to implement, and creates a knowledge gap for the team. Torq offered a faster path. Through a straightforward API call, the team built a workflow that automatically detects locked-out users and clears the flags, allowing accounts to be onboarded without manual intervention.
That migration fix opened a bigger door. The team discovered that Torq could do things with Okta data that the native dashboard couldn’t. They started pulling error logs through Torq and running analysis to surface root causes, not just the symptoms the dashboard displayed. What started as a migration fix became an ongoing operational layer on top of their identity infrastructure, giving the team better visibility into their identity environment than the identity provider itself.
The team started with security automation and quickly found that Torq’s platform could absorb manual work across security and IT operations alike. What began as a handful of security playbooks has grown into a library of automated workflows spanning threat response, identity management, endpoint security, and infrastructure monitoring.
The team’s very first workflow is still one of the most impactful. The museum’s network monitoring tool continuously watches for suspicious outbound connections. When a device is flagged for querying a potentially malicious URL, Torq automatically sends the indicator to VirusTotal for cross-referencing against dozens of antivirus engines. More than four positive hits? Blocked immediately, without a human in the middle.
Before Torq, an analyst had to review the flag, look up the URL, make a judgment call, and take action. Now it runs in seconds.
When SentinelOne detects a suspicious event on an endpoint, the alert triggers a Torq micro-playbook that automatically enriches the event. Torq pulls the relevant indicators — hashes, IPs, domains — and queries them against VirusTotal and other threat intelligence sources. Based on the results, the playbook either documents the event as benign or executes a blocking action, without requiring an analyst to manually copy indicators between tools.
Tools get deployed with specific security baselines: hardened configurations, required settings, expected states. Over time, those baselines drift. A setting gets changed during troubleshooting and is never reverted. An update overwrites a configuration. A new deployment doesn’t match the standard.
The team uses Torq to scan their tool stack and flag discrepancies against defined baselines. Instead of manually auditing on a schedule — or discovering drift after an incident — Torq surfaces gaps proactively.
Patching is one of the most basic security hygiene practices and one of the easiest to let slip. A critical update lands, but the reboot requires coordination: confirm the asset is clear, schedule a window, and follow up. For a lean team, that coordination competes with every other task on the list.
The team built a Torq workflow that monitors for assets with pending critical updates and triggers an automatic nightly reboot. Patches are applied on schedule, every time, without manual follow-up.
Every tech stack accumulates clutter. Devices get decommissioned but never removed. Endpoints are reimaged, creating duplicates. Orphaned records pile up. Each one is a blind spot — an asset that shows as managed when it isn’t, or a duplicate that skews reporting and wastes license seats.
Torq continuously scans the team’s tech stack, identifies stale or duplicate assets, and cleans them up. What used to be a periodic manual audit is now a continuous hygiene function.
A disabled security agent is an unmonitored endpoint. The disable might be intentional (for troubleshooting), accidental (due to a bad update), or the first sign of compromise. The longer it stays disabled, the bigger the gap.
Torq monitors disabled agents and automatically re-enables them. The team is notified immediately — if the disable was legitimate, they know. If it wasn’t, the gap would be closed before it could be exploited.
“Using Torq, we have the ability to retrieve data from multiple applications and mirror human action in an automated way. That saves time, and where we really need to save time is on the action side. Instead of waiting a week to block a bad IP address, Torq lets us do it almost instantaneously. It’s a major risk reduction.”
– Michael Trofi, CISO
The museum exists to preserve history and make sure the world never forgets. That mission draws millions of visitors, powers a global digital presence, and makes the institution a target.
The security team didn’t automate because it checked a box. They automated because the mission was too important to protect at human speed. The automation this team built is the foundation the AI SOC is built on: the shift from human-speed operations to machine-speed defense. The threats keep evolving, and so does the team.
This major museum’s team is proof of what the data shows: lean SOCs that deploy the right automation get ahead. See how 450 security leaders are thinking about AI, automation, and the future of security operations.
SEE TORQ IN ACTION
See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.
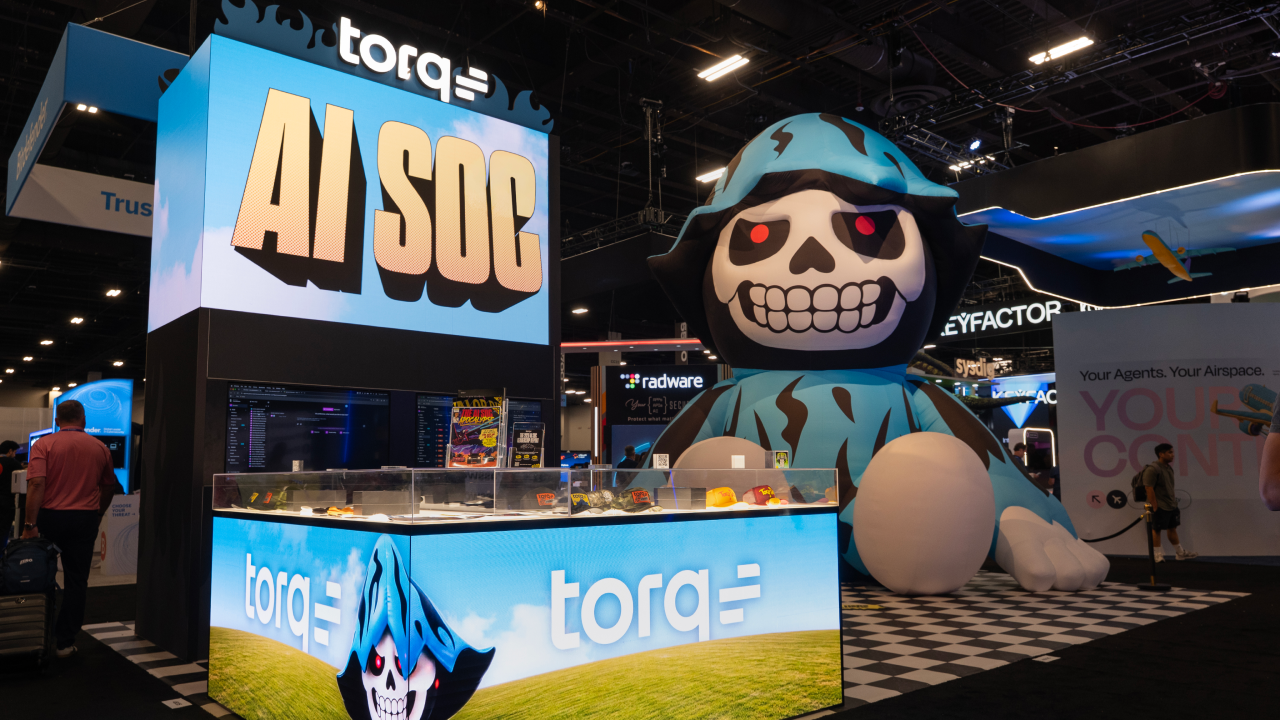
Torq rolled into Black Hat 2026 with a 20-foot inflatable skeleton, free tattoos, hot dogs, the Wizard of Oz, and a live news desk. That’s a lot of conversation starters right there.
But the real talking point was Torq’s AI SOC demo: in-production AI SOC capabilities that reason with organizational context, learn from analyst decisions, get smarter with every case the platform handles, and take action across the full threat lifecycle.
Here’s what really happened in Vegas.

Days before Black Hat, Torq unveiled Torq SOC Brain™, the self-learning layer of the Torq AI SOC Platform. The SOC Brain brings together Recall, Reflex, and Retrospect to help Torq reason from past cases, learn from analyst decisions, and apply that judgment to future triage and investigations.
The launch drew coverage from SiliconANGLE, Channel Insider, MSSP Alert, and more.
“The end goal is to shift as much as possible of a cognitive load required to investigate incoming security alerts.”
Leonid Belkind, Torq CTO and Co-Founder in Channel Insider
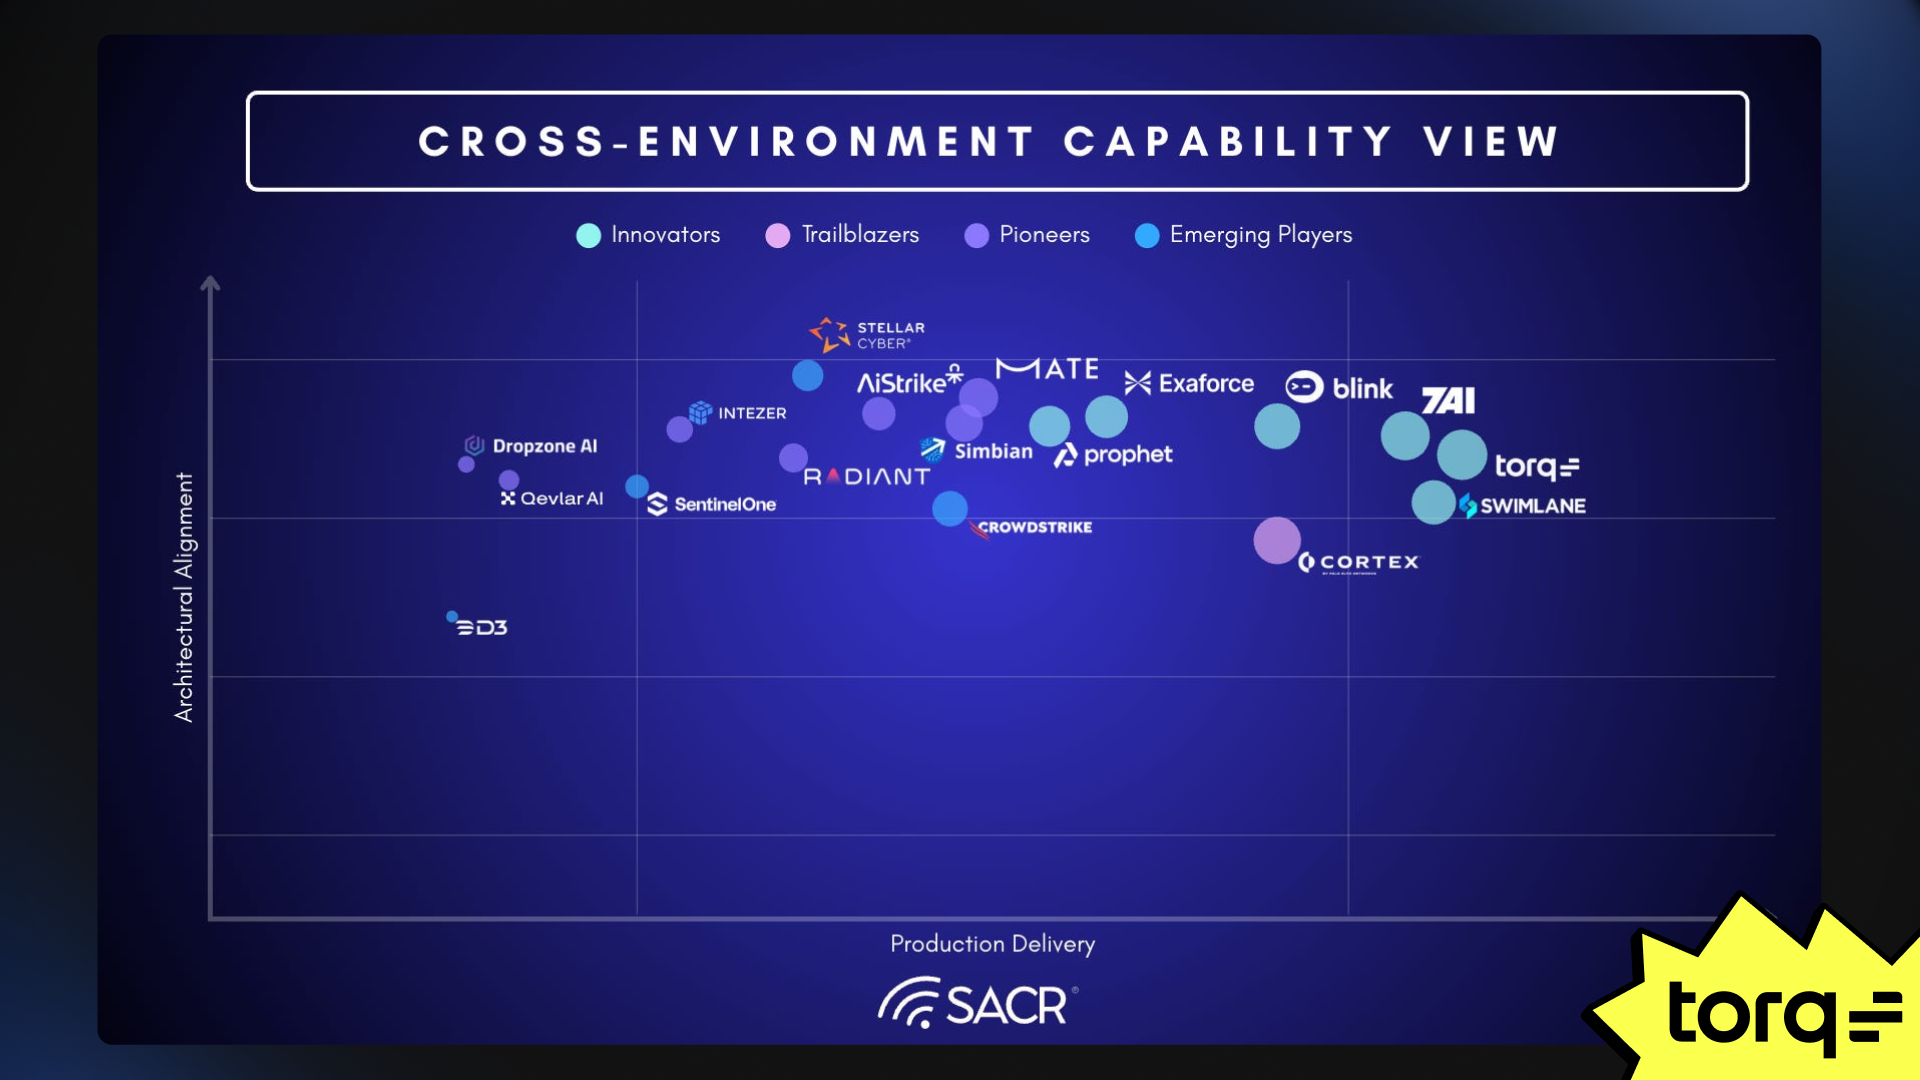
Torq also entered Black Hat with fresh analyst recognition: Software Analyst Cyber Research named Torq a leading Innovator in its AI SOC Market Report, as an “as an AI SOC operating layer that can ingest alerts, classify triage outcomes, construct cases, assign work to Socrates, and route remediation through deterministic or agentic workflows depending on the use case.”
Then we took it to Vegas.
Torq’s demo stations stayed busy as attendees saw hands-on how Torq moves from alerts through investigation and response with context and agentic reasoning built in. Here’s what landed most:
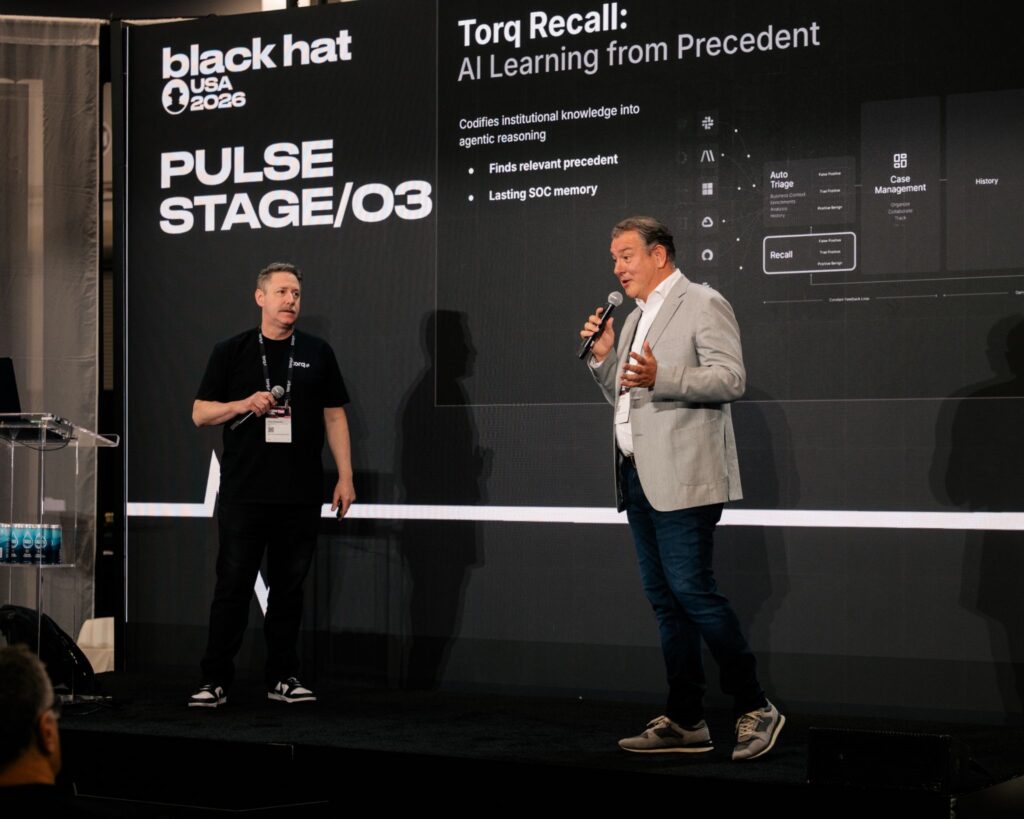
John White, Field CISO EMEA, and Rick Bosworth, Sr. Director of Product Marketing, took the stage to go a level deeper on why those capabilities matter. Together, the Context Graph, Recall, and Reflex form the Torq SOC Brain, the layer beneath the agents that lets the platform reason about your environment, remember your decisions, and learn your team’s judgment.
John and Rick kept coming back to two points:
They also shared advice on how best to get started with an AI SOC platform: Pick the repeatable Tier 1 work that eats the most analyst time, prove it out, then expand. On timing, they were blunt. Waiting is its own risk when attacks already move at machine speed.

Our Junior Media Intern Trevor has traded in his TorqTV van for a news desk.
Trevor and Tony went live from the TTVN desk with boots-on-the-ground Black Hat coverage of the week’s biggest stories: Skelly, Torq Dogs, real (yes, real, actual, permanent) tattoos and piercings, Channimals in the Wild, AMP’d partner highlights, and an exclusive Wizard of Oz screening at the Sphere, co-hosted by Snyk.
The hot dogs were tasty. The tattoos were permanent. But the bigger story was what Torq showed in the booth and on stage: an AI SOC platform that reasons on your environment, remembers your decisions, and learns your team’s judgment across the full threat lifecycle.
Missed the Torq demo at Black Hat, or want a closer look without the show-floor crowd? Watch our live Auto Triage demo webinar.
SEE TORQ IN ACTION
See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.
Cyber risk demands continuous attention. New assets come online, new vulnerabilities surface, and threat actors refine their techniques every day. The organizations that manage cyber risk most effectively treat it as an ongoing business discipline built on a structured, repeatable cycle of mapping, measuring, and mitigating threats proactively.
This guide covers what cyber risk management is, the four-stage process that drives it, the frameworks that give it structure, and the best practices that make it effective. It also covers how an AI SOC platform closes the execution gap between identifying a risk and reducing it.
Effective CRM runs through four continuous stages. Each stage feeds the next, and the cycle repeats as the organization’s asset inventory and the broader threat landscape both evolve.
Every CRM program starts with a complete picture of what the organization is protecting. Security teams identify and document all IT assets: hardware, software, data, networks, cloud resources, and third-party integrations. A complete, current asset inventory is the foundation every other stage of the program depends on.
Prioritization follows the inventory. Organizations classify assets based on business value, legal standing, and operational criticality to identify High-Value Assets (HVAs): the systems and data that would cause the greatest damage if compromised. An unpatched development server carries different risk than an unpatched system processing customer payment data.
Threat modeling rounds out the identification stage. Security teams proactively map attack vectors and identify the specific threats (phishing, ransomware, insider threats, supply chain compromise) and vulnerabilities (misconfigured firewalls, unpatched software, over-permissioned accounts) that could affect each asset. That work turns a static asset list into a dynamic risk map. Explore 12 types of cybersecurity attacks and how AI-driven security operations address each one.
With risks identified, the next stage measures them. Risk assessment analyzes two dimensions for each identified threat: the likelihood it occurs and the potential impact if it does. Combining those dimensions produces a risk score that directs mitigation resources toward the highest-priority exposures.
Modern practice pushes beyond qualitative High/Medium/Low scoring into cyber risk quantification (CRQ): expressing risk in financial terms. When a risk carries a dollar value (expected annual loss, breach scenario cost, regulatory fine exposure), security leaders make investment decisions with the same rigor they apply to other business expenditures. CRQ also makes the ROI of security controls visible. A $200,000 control that reduces a $2 million expected annual loss is a straightforward business case.
Risk assessment findings feed directly into prioritization. The highest-likelihood, highest-impact risks against HVAs get addressed first. Lower-likelihood risks against lower-value assets move into the monitoring queue.
The mitigation stage translates risk assessment findings into action. For each identified risk, security leaders choose a response strategy based on the organization’s risk tolerance:
Control implementation is where mitigation becomes operational. Firewalls, encryption, multi-factor authentication, access controls, and security monitoring tools all reduce the likelihood or impact of specific threat categories. Cybersecurity best practices covers the control categories that deliver the broadest risk reduction across typical enterprise environments.
Document every decision at this stage. Record each risk, the response strategy the team chose, and the owner accountable for execution. All of it belongs in the risk register.
Risk management continues well past control implementation. The threat landscape changes, new assets come online, and controls drift from their intended configuration over time. Continuous monitoring catches those changes before they become incidents.
Ongoing surveillance of the IT ecosystem and the broader threat landscape feeds back into the identification and assessment stages. New vulnerability disclosures, emerging attack techniques, and changes in the regulatory environment all trigger updates to the risk map. The cycle keeps turning.
The risk register is the operational hub of this stage: a live document tracking all identified risks, their current status, assigned owners, and planned or completed mitigation actions. Keeping it current requires discipline and pays off every time leadership asks for a risk posture update or an auditor requests evidence of due diligence.
Residual risk acceptance is a formal, documented step. After controls are implemented, some risk always remains. Senior stakeholders review and formally accept that residual risk, creating documented accountability for the organization’s risk posture. The cybersecurity lifecycle framework maps how this continuous cycle connects detection, response, and recovery into a unified operational model.
Frameworks give CRM programs a structured, recognized methodology, and they matter for compliance. Regulators and auditors frequently ask which framework an organization follows and whether it demonstrates consistent adherence.
The National Institute of Standards and Technology produces two widely adopted frameworks. The NIST CSF organizes cybersecurity activities into five functions: Identify, Protect, Detect, Respond, and Recover. It gives organizations a common language for discussing and improving security posture and applies across industries and organization sizes.
The NIST RMF provides a seven-step process for integrating security and risk management into system development and procurement lifecycles. Federal agencies use it as a compliance requirement; many private-sector organizations adopt it for its rigor and structured approach. The cybersecurity frameworks guide covers how NIST and other frameworks apply to enterprise risk programs.
ISO 27001 defines the requirements for an Information Security Management System (ISMS): the policies, procedures, and controls an organization puts in place to manage information security risk systematically. ISO 27005 provides the risk assessment and treatment methodology that feeds the ISMS.
Together, they give organizations an internationally recognized, auditable framework for demonstrating that a structured risk management program exists and operates as documented. ISO 27001 certification carries weight with enterprise customers, partners, and regulators across global markets.
FAIR is a quantitative risk framework designed to translate cyber risk into financial terms. Where NIST and ISO provide process structure, FAIR provides the analytical methodology for CRQ: how to model threat frequency, vulnerability probability, and loss magnitude to produce a defensible financial risk estimate.
Organizations that adopt FAIR can answer the question boards and CFOs ask most: how much risk does the organization carry, and what does a breach cost? That financial clarity drives better investment decisions and clearer communication with non-technical stakeholders.
Zero-trust security removes implicit trust from the network architecture. Every user, device, and application gets verified before accessing resources, and access gets scoped to the minimum required for each specific task. This approach limits lateral movement after a breach and reduces the blast radius when credentials are compromised.
Zero-trust applies particularly well in hybrid and multi-cloud environments where identity has become the true security perimeter and continuous verification is the enforcement mechanism.
Unpatched vulnerabilities remain one of the most consistent entry points for attackers. A mature vulnerability management program runs continuous scanning across internet-facing systems and internal assets, prioritizes findings by exploitability and asset criticality, and closes patch windows before attackers can exploit newly disclosed vulnerabilities.
Speed matters here. Automated vulnerability management workflows triage findings and route critical patches to the right teams, closing that window faster than manual processes. See how vulnerability management tools and automated triage workflows work together in practice.
Supply chain attacks have demonstrated that an organization’s security posture extends to every vendor, partner, and integration that touches its environment. Managing third-party risk means evaluating vendor security controls at onboarding and monitoring them on an ongoing basis.
Automated workflows that track vendor security questionnaire status, monitor for vendor breach disclosures, and flag integration anomalies give security teams continuous third-party visibility at scale.
A well-defined, regularly tested incident response plan (IRP) and disaster recovery plan (DRP) determine how much damage a breach causes. Organizations that exercise their response plans regularly contain incidents faster and restore operations more completely.
The incident response plan framework covers the components of an effective IRP and how to structure tabletop exercises that surface gaps before attackers do. Incident response automation covers how automated workflows cut response time from detection to containment.
Technical controls address the infrastructure layer of cyber risk. The human layer requires a different approach: regular security training that helps employees recognize phishing, social engineering, and insider threat scenarios, combined with security responsibilities distributed across business units.
Security awareness programs work best when they go beyond annual checkbox training to include simulated phishing campaigns, role-specific training for employees who handle sensitive data, and clear escalation paths when employees encounter something suspicious.
Frameworks and best practices define what cyber risk management requires. Execution speed determines how well it works in practice. The gap between identifying a risk and closing it creates the window attackers exploit, and narrowing that gap is exactly where Torq’s AI SOC Platform delivers.
Torq Hyperautomation™ connects the security tools, identity systems, cloud environments, and endpoint platforms that CRM programs depend on into unified, automated workflows. When a vulnerability scan surfaces a critical finding, Torq automatically enriches it with asset criticality and exploitability context, routes it to the appropriate team, and triggers the remediation workflow, all before the alert reaches a manual review queue.
Torq HyperAgents® bring autonomous action to the risk mitigation stage. HyperAgents are built to execute multi-step response workflows the moment a risk indicator is confirmed, collapsing the detection-to-remediation cycle from hours to minutes. When a misconfigured cloud resource creates exposure, HyperAgents detect the deviation and trigger a remediation workflow immediately.
Torq Socrates™, Torq’s agentic SOC orchestrator, adds intelligent reasoning to risk triage. Socrates evaluates incoming security signals in context, determines which warrant immediate escalation and which route to the remediation queue, and executes or delegates based on the specific risk profile of each finding. Security teams get autonomous triage that scales with their environment.
Torq’s Agentic Builder takes that further. Security architects and operations analysts describe what they need in plain language, and Agentic Builder (part of Socrates, the core orchestrator of the Torq AI SOC Platform) reads your integrations, plans the build, writes the orchestration logic, and deploys a production-ready AI Agent directly into your environment. When frameworks, asset inventories, or threat landscapes evolve, teams update their automation through the same agentic interface, keeping response workflows aligned with the current risk program at the speed the threat landscape demands.
Cyber risk management gives organizations the operational discipline to make intelligent, data-driven security decisions: decisions that align spending with actual business risk, demonstrate due diligence to regulators and stakeholders, and ensure business continuity when incidents occur.
The four-stage cycle of identification, assessment, mitigation, and monitoring creates the structure. Frameworks like NIST, ISO, and FAIR provide the methodology. Best practices address the specific risk categories that matter most. And automation closes the execution gap between knowing a risk exists and acting on it at the speed modern threats require.
Torq’s AI SOC Platform gives security teams the Hyperautomation engine and agentic response to operationalize their CRM program continuously, connecting every tool in their stack, automating risk response workflows, and keeping security posture aligned with a threat landscape that never stops evolving.
Is your cyber risk management program running as a continuous operational discipline, one that catches and closes exposures in real time, or does your team have an opportunity to move beyond periodic review cycles?
Most AI triage judges every alert from scratch; fast, confident, and often wrong. Torq Auto Triage works differently. It learns from your analysts’ decisions and your organization’s history, getting more accurate with every case.
The SOCs winning the AI SOC Apocalypse aren’t just automating triage. They’re building institutional intelligence that compounds over time.
The question is whether yours is one of them.
Cyber risk management is the continuous process of identifying, assessing, mitigating, and monitoring threats to an organization’s digital assets, systems, and operations. It combines threat modeling, risk quantification, control implementation, and ongoing surveillance into a repeatable cycle that keeps security posture aligned with an evolving threat landscape. The goal is protecting business continuity, demonstrating due diligence to regulators and stakeholders, and making security investment decisions based on actual risk. Learn how the cybersecurity lifecycle framework connects CRM to detection, response, and recovery operations.
Risk assessment is one stage within the broader risk management process. A risk assessment analyzes identified threats and vulnerabilities to measure their likelihood and potential impact, producing a prioritized picture of where risk exposure is greatest. Risk management is the full cycle: identifying assets and threats, conducting assessments, choosing and implementing mitigation strategies, and monitoring continuously for new risks and changes in existing ones. Assessment informs management; management drives the decisions that assessment results support.
The four main stages are risk identification (cataloging assets and mapping threats), risk assessment and quantification (measuring likelihood and financial impact), risk mitigation (choosing response strategies and implementing controls), and continuous monitoring (tracking the risk register, surveillance of the threat landscape, and formal acceptance of residual risk). Each stage feeds into the next, and the cycle repeats continuously as the organization’s environment and the broader threat landscape evolve. See how security incident categories inform risk prioritization across each stage.
The most widely adopted frameworks are NIST CSF and RMF (strong in U.S. critical infrastructure and federal environments), ISO 27001/27005 (internationally recognized, audit-ready structure for an ISMS), and FAIR (quantitative methodology for expressing risk in financial terms). Each framework addresses a different dimension of the CRM challenge: NIST and ISO provide process structure, FAIR provides quantitative rigor. Many organizations combine elements of multiple frameworks to match their regulatory environment, risk appetite, and operational maturity. The cybersecurity frameworks guide covers how to choose and apply the right framework for your environment.
SEE TORQ IN ACTION
See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.
Software Analyst Cyber Research (SACR) just published its 2026 AI SOC Market Report, offering an independent assessment of vendors competing in what has rapidly become the most consequential category in enterprise security. Torq features prominently, and the report’s framing is worth unpacking because it illuminates what makes the AI SOC category hard to evaluate and why Torq’s approach is consequential.
SACR’s most pointed observation about Torq is definitional. The firm writes:
“Torq is best understood less as a conventional SOAR vendor with AI features and more as an AI SOC operating layer that can ingest alerts, classify triage outcomes, construct cases, assign work to Socrates, and route remediation through deterministic or agentic workflows depending on the use case.”
That distinction matters. Much of what gets marketed as AI SOC today amounts to copilot functionality that surfaces recommendations and draft summaries, and stops at basic triage that simply moves the bottleneck down the SOC line by an increment. SACR cuts through that framing:
“Torq is trying to own high-volume alert triage and response closure, not simply accelerate analyst review.”
Owning closure requires a different architecture than assisting analysts. It requires accurate alert classification at scale, a context layer deep enough to support trustworthy, autonomous verdicts, case management that carries investigations forward, and response automation that can act, not just advise. But let’s circle back and dwell a bit on the first phase: autonomous alert triage.
Torq Auto Triage classifies incoming alerts as false positive, benign, or malicious, enriches them with threat intelligence and business context, and routes them accordingly, all before a human analyst is involved. True positives become cases automatically. False positives are fed back into the per-tenant AI model.
SACR called out the quality of Torq’s context layer directly:
“Torq is not treating alerts as isolated artifacts. It is building a context pipeline around entities, access history, business role, device state, SaaS activity, and related evidence before determining whether an alert should be closed, escalated, or remediated.”
Three underlying capabilities power that context pipeline.
The results speak volumes. On average, large enterprises achieve a mean time to triage (MTTT) of 1 minute, a 60x improvement over manual triage. A global biotech titan cites a 97% reduction in noise entering the SOC; imagine how much better their security analysts can focus. A well-known financial services enterprise achieved 99% faster threat triage after deploying Torq.
When Auto Triage surfaces a true positive, it flows directly into Torq Case Management, where analysts inherit the full verdict, enrichment context, and proposed next steps. They do not reconstruct context from scratch.
From within the case interface, analysts collaborate with Torq Socrates™, trigger automated response actions, and track investigation continuity across shift handoffs. Each confirmed verdict and analyst correction flows back into Reflex as a training signal, compounding accuracy over time.
This is the mechanism behind what SACR identifies as Torq’s stronger-than-expected investigation story: the platform captures and encodes analyst judgment, rather than relying on individual expertise to repeat the same reasoning shift after shift. The machine clears the noise. The analysts focus on the highest priority items.
Torq Socrates is the agentic reasoning and orchestration layer at the center of the platform. It can be used interactively by analysts, embedded in investigation templates, or assigned cases autonomously. Once on a case, Socrates plans investigations, delegates tasks to specialized Torq HyperAgents®, and coordinates response actions across the security stack.
SACR characterizes Socrates as “the reasoning and planning layer that decides how much work should be agentic, how much should be deterministic, and where the human should approve or intervene.” As SACR notes, “autonomy is a dial, not a binary switch,” and Torq’s model lets security organizations operationalize that dial gradually: starting with triage and recommendation, moving into human-approved action, and eventually automating higher-confidence alert classes.
One Torq customer on PeerSpot describes the cumulative impact: Torq handles a large volume of their alerts autonomously, fundamentally changing the burden placed on their security team.
Torq Hyperautomation is the execution layer that connects AI decisions to real action, supporting both agentic and deterministic workflows across the full security stack. SACR identifies this automation heritage as a structural advantage:
“Compared with AI SOC point solutions, Torq’s advantage is the ability to connect AI decisioning to actual workflow execution.”
That advantage compounds. The same platform that classifies an alert, builds the case, and assigns it to Socrates is the platform that executes containment and remediation at machine speed. Customers have measured a 94% reduction in mean time to respond (MTTR), a metric that requires the full chain, not just faster triage at the front end.
SACR closes its Torq vendor profile with a synthesis that applies beyond Torq specifically:
“Autonomous SOC value will be measured by closed-loop operating capability rather than AI summarization.”
Verdict quality matters. But a verdict quality that does not connect to case construction, investigation, response, and organizational learning is an incomplete story. Torq’s architecture is designed around that full loop.
SEE TORQ IN ACTION
See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Dima Kogan is Director of Product Design at Torq, where he leads the design team building Torq’s AI-powered cybersecurity products. Over 15 years in product design, including design leadership at monday.com, he’s spent his career making complex systems feel simpler to use. He writes regularly about product design, leadership, and designing in the age of AI.
Most enterprise cybersecurity products focus on functionality. That’s fine. It’s the job. But enterprise security teams spend hours inside their core products — real humans, doing really important work, seeing the same thing day after day after day.
As our platform grew, we started asking ourselves a simple question: why should powerful software have to look so…generic? We’d spent years making The Torq AI SOC Platform smarter, faster, and more capable. But visually, it still felt like it could belong to almost anyone.
Torq is known for being bold and fun — and that distinctiveness carries weight. Wear a Torq hat at a security conference, and people stop you to talk. But inside The Torq AI SOC Platform, that personality wasn’t there. We’d poured everything into functionality, and at first, the interface wasn’t really us.
Consumer software figured this out a long time ago: how a product feels is a big part of whether people stick with it. Enterprise software has been slower to catch on, and security software slowest of all.
The assumption in security has always been that personality is frivolous, or worse, unprofessional. The work is high-stakes, so the tools are built to be serious and nothing else. The result is a whole category of products that look interchangeable and feel clinical.
Our design mission made the goal clear: build products that are powerful, category leaders, and unmistakably Torq. The harder part was execution. How do you bring skeletons, lasers, and monster trucks into the leading AI SOC platform without getting in the way of the work?
We started with the people who use Torq: security analysts working under real pressure, and engineers building complex workflows. The work is serious, which is exactly why the experience matters. As one engineer at AppsFlyer put it, “SecOps is a tedious, tiring job. It’s important to have some fun.”
So we got specific about how we wanted them to feel: in control, eager to build, and confident in the system, with a real sense of mastery in what they’d built. One rule anchored everything: Torq is where analysts handle critical incidents all day, so anything we added had to reinforce the experience without interrupting the work.
Thus, a third mode was born alongside Light and Dark modes. Users can choose the standard experience in Light or Dark, or the fully brand-connected one: Torq Mode.
We chose specific flows and interactions where a moment could land: places to encourage someone, mark a win, or draw attention to what matters. A few of them:
Two months of thinking, two weeks of building, and then we launched. The results surprised us: 81% of users who turned on Torq Mode kept it on, month after month.
Customers started bringing it up in demos. One wrote: “The animations bring a lot of energy to the interface and make the experience feel more alive… a strong personality that’s instantly recognizable and memorable.” An engineer even spent his own time extending Torq Mode into more of the product, and a customer asked us to add sound effects. When people ask for more personality, not less, you’ve built something they connect with.
Enterprise products already look alike, and the AI era will only push them closer together. AI will build faster than ever, but it won’t decide how people should feel. That part is still on us. Solving the user’s problem is the baseline; building an experience they remember is the craft.
Torq Mode: on.
SEE TORQ IN ACTION
See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.
Back in June, I wrote a blog making the case that agentic triage alone isn’t an AI SOC. The way I see it, that’s like saying triage is the only responsibility of a SOC team. But as we know, the SOC’s responsibilities extend far beyond that, and these triage-only solutions don’t investigate threats, contain them, or close cases. That work is still left to the SOC team; the bottleneck is just shifting.
The argument is that the bar should be higher, and Torq is setting that bar. Full lifecycle coverage — across triage, investigation, threat hunting, containment, and remediation — enterprise scale within some of the largest Fortune 100 SOCs in the world, and transparent, defensible AI agents grounded in your organization’s business context all point to why Forbes, KuppingerCole Analysts, and Gartner have recognized Torq’s position at the top of the AI SOC market.
That argument still stands, but today… We’re raising the bar again.
Introducing: Torq SOC Brain™ — the memory layer that makes Torq the only AI SOC platform that genuinely learns.
For most “AI SOC” platforms, learning simply means that when an alert fires, the system searches through past cases, finds one that looks similar, and feeds that example into an LLM to help it make a decision. This is more retrieval than actual learning. A system that retrieves past cases from weeks ago has no memory of what decisions were made yesterday, or understands that your senior analyst treats certain scenarios differently than your Tier 1 team does. It doesn’t get better or adapt because it’s pattern matching. And that approach is going to hit the same efficiency wall every single time.
“With Torq SOC Brain and its Torq Recall, Torq Reflex, and Torq Retrospect capabilities, the Torq AI SOC Platform truly learns how a SOC thinks, even from the years of history that predate a Torq deployment. That’s the difference between automation that treats every investigation as if it were on its own and the industry’s first SOC that gets smarter and more accurate with each completed investigation.”
– Ofer Smadari, Torq Co-Founder & CEO
Torq SOC Brain is the learning layer of the Torq AI SOC Platform… that actually learns. Every customer has it built directly into their private workspace, exclusively for their organization. It never pools customer data, never shares model parameters, and never trains one customer’s AI on another customer’s experience. It is a private intelligence layer that ensures your Torq AI SOC Platform becomes your judgment, your model, your intelligence.
Torq SOC Brain is the reason every Torq Auto Triage verdict, every Torq Socrates™ investigation, and every Torq HyperAgents® response action gets more accurate as your team uses the platform. It’s built on three interconnected capabilities: Torq Recall, Torq Reflex, and Torq Retrospect. Together, they do something no other AI SOC platform can: turn your resolved cases, analyst decisions, and years of institutional history into a model that thinks like your team.
The most common form of memory in AI SOC tools is a search interface, powered by an agentic chatbot that runs stateless queries to find semantic similarities. In security, just because something looks roughly similar doesn’t mean anything; to an AI model, two hash values might look semantically close, but point to two completely different files. In a high-stakes environment, “close enough” can be catastrophic.
Recall instead relies on structured retrieval, looking for exact, deterministic overlaps of specific security observables — IPs, file hashes, URLs, hostnames, or emails. If your team has seen an exact indicator before and documented their conclusion, Recall finds it.
If historical cases aren’t automatically fed back into agentic decisions, institutional knowledge stays buried in closed tickets, and verdicts quickly become outdated. A case closed last week tells a very different story than one closed last year. What makes Recall truly game-changing is the understanding of the signal strength, so the AI stays focused on entities that matter.
Recall analyzes analyst notes, weights precedents by recency, and understands that different conclusions hold different weights. And if it finds contradicting records, Recall knows when to say it’s sure and when it isn’t, rather than force an answer it cannot justify. That honesty is what builds trust in agentic decisions at scale. Triage verdicts and response actions are not based on last month’s playbook; they are grounded in how your SOC operates today and automatically applied to every alert.
Often, when AI decision-making misses the mark, it simply lacks the correct context. Recall solves that problem. But research conducted by Torq Labs found that, even with all the context, all the memory, and the same facts a human analyst has, an AI model can make an incorrect decision or even contradict an earlier decision. This isn’t a data gap; it is a judgment gap between humans and machines. While Recall allows agentic verdicts to be based on your most accurate case history (i.e., the data), Torq Reflex gives the AI model access to your team’s judgment.
Reflex is a per-tenant model that trains continuously on your team’s confirmed verdicts and corrections, engineered to operate under asymmetric risk where missing a malicious threat is considered far more costly than mislabeling a benign alert. When an alert fires, Reflex assigns a verdict and, most importantly, a calibrated confidence score — a real mathematical probability that builds trust in verdicts and makes the system safe to run.
When confidence is high, the verdict drives automated output (e.g., filtration, case creation, prioritization, or autonomous remediation). If it isn’t high, the full analysis still runs, the agentic reasoning is documented, and the case is escalated to a human analyst for confirmation. As a result, Reflex helps improve agentic decision making with each alert, because any alert that it’s uncertain about routes back through the human-on-the-loop process you already trust.
Whatever the analyst decides retrains the model, so every correction is worth a little more, and every verdict becomes more trustworthy. Reflex is the key to how the Torq SOC Brain actually learns and becomes more accurate over time. The longer you use Torq, the smarter the Torq SOC Brain gets.
“The longer Torq runs in our environment, the more it sounds like our best analysts. That’s the part no other AI SOC platform delivers.”
– Director of Security Operations, Fortune 500 Financial Services
Recall and Reflex drive the Torq SOC Brain to truly learn over time, becoming your own SOC model based on your own SOC judgment. But given today’s AI-augmented threat landscape, time works against SOC teams in identifying and responding to attacks now more than ever. They need an AI SOC solution that drives value now, today, not 6 months down the road. Enter Retrospect.
Most AI SOC platforms arrive knowing nothing about the environment or how your SOC operates. Deployment is an uphill battle, early verdicts are incorrect, and analysts lose trust before the system has a chance to earn it. Retrospect makes sure you don’t start from scratch. Before Torq sees a single live alert, Retrospect normalizes all your external cases and observables, imports them from your existing case management tool, and makes that history immediately available to Recall and Reflex. Years of analyst decisions, closed cases, and documented outcomes become the foundation of the Torq SOC Brain.
The result is an AI SOC that doesn’t just arrive informed; it’s already smarter than most deployments will hope to achieve after 6 months of production. The learning curve that kills early adoption of agentic decision making collapses entirely. Your SOC’s institutional knowledge doesn’t start accumulating on Day One; it’s already there.
In an enterprise SOC, accuracy is dynamic. Your environment changes. AI models are upgraded. Threat actors adapt. New attack patterns emerge. Your team’s risk posture evolves with every incident you close.
A static AI model calculates the same confidence against the same signal regardless of how many times your team has overridden it on that exact attack pattern. There is no “getting better”; it simply is what it is, never earning the trust of the human analysts responsible for defending and justifying every decision made in the SOC.
In the 2026 AI SOC Leadership Report, 97% of respondents reported confidence in AI’s ability to address alert triage, but only 37% applied AI to the use case. The gap between confidence and adoption, the report found, is largely driven by trust. SOC leaders reported they don’t have full transparency into agentic decision-making, and therefore, can’t defend a missed alert or a false verdict. Analysts find themselves re-checking the agent’s conclusions, doubling the work, and leaving them right back where they started: buried in alerts.
On the other hand, Torq Auto Triage has maintained 100% usage retention across all customers and a steady average MoM increase of 144% in alert volume fed into the system. Torq Auto Triage customers report a 97% reduction in alert noise, a 60x increase in triage velocity, and an improvement in accuracy score from 94% to 99% over an average three-month period.
“Torq Auto Triage was ready for an enterprise of our scale, where a competing solution was not.”
– Global FinTech Enterprise
The Torq SOC Brain drives accuracy in agentic verdicts, acting as the primary engine and memory layer behind Torq Auto Triage. The Torq SOC Brain justifies each Torq Auto Triage verdict with crystal clear evidence and reasoning, documented and cited in the historical truth of how your SOC operates. Those verdict decisions improve in accuracy with every alert and are treated as first-class data, stored in the Torq Context Graph. This, in turn, grounds every agentic decision across the entire Torq AI SOC Platform in your organization’s most accurate and up-to-date truth. Every triage verdict becomes more confident, every investigation becomes more precise, and every autonomous threat remediation becomes more trustworthy.
Most importantly, the Torq SOC Brain is what allows some of the largest enterprise SOCs in the world to achieve such rapid time-to-value with the Torq AI SOC Platform:
Most recently, the InfoSec Director of a Fortune 100 Global Retail Enterprise, who completed a full Torq AI SOC Platform migration in only two weeks, reported: “In just three months, we’ve already accomplished so much more than we ever did in five years with [previous solution].”
Torq has been widely recognized as a leading innovator and a dominant force in the AI SOC landscape (see Forbes, KuppingerCole Analysts, and Gartner). We set the bar for end-to-end threat lifecycle coverage, while others simply triaged threats and shifted the SOC bottleneck further down the line.
Today, the bar is even higher. The question isn’t just whether your AI SOC completes the threat lifecycle; it’s whether it learns how your team wants it done.
Your AI SOC should handle every alert the way your team would, and get better at it over time. That’s the Torq SOC Brain. That’s why Torq Auto Triage is the only agentic triage engine that actually learns. And that’s why the Torq AI SOC platform isn’t just the most complete AI SOC on the market; it’s the only one that becomes your organization’s own AI model.
See it live at Black Hat at Booth #4935, or request a demo today.
SEE TORQ IN ACTION