From Playbooks to Reasoning: What Agentic AI Actually Changes

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.
Request a Demo

David Melamed is Head of Emerging Technologies at Torq. He joined through Torq’s acquisition of Jit, which he co-founded and has led as CTO since 2020, building agentic security on a production Context Graph. A cloud security veteran with 20+ years of experience, David previously held senior technical roles at Cisco (via the CloudLock acquisition) and MyHeritage.

Before Odysseus can find his way home, Circe tells him that the only guidance for the dangers ahead must come from the spirit of a blind prophet, Tiresias. To consult him, Odysseus must sail to the edge of the world and call up the dead. The prophecy itself takes only a few minutes to hear. Reaching the one who can give it takes an entire voyage.

Difficult security decisions work the same way. Getting a verdict once the context has been properly built is cheap and becomes straightforward. The challenge lies in acquiring that context. Acquiring context has been the focus of security automation for the past decade, but automation has only ever reached part of it.

The Part a Playbook Could Never Reach

The previous post in this series was a blunt autopsy: SOAR platforms promised us to automate the SOC, but as we know, you can’t automate open-ended investigation with flowcharts. 

A playbook automates actions you’ve manually laid out. If there is an alert of type X, enrich it with data from source Y, then create a ticket Z. This is all actual valuable work. However, what a Tier 1 analyst really does is look for things that don’t fall into any of the flow branches: Check a user’s recent logins, verify if some file hash was seen anywhere before, evaluate if some specific asset actually matters, or decide if a pattern matches a past incident. 

This requires an open-ended, step-by-step investigation, with each step dependent on the outcome of the previous one, making it almost impossible to represent as a flowchart. So this high-value work remained manual, with analysts acting as the human bridge between siloed systems and connecting the dots.

The Unit of Automation Has Shifted From Enrichment to Investigation

That investigative work is what agentic analysis automates, and it is what sets it apart. A playbook makes analysts faster by running a fixed set of paths more quickly. An agent instead acts like a real analyst, determining what to investigate next based on what it has discovered, collecting evidence across the stack, correlating that evidence, and ultimately providing a verdict with a trace of how it got there for full transparency. The unit of automation has shifted from focusing on signal enrichment to investigating the meaning of alerts. 

This is what turns “machine-speed investigation” from a slogan into something real, and it is the promise this series has been building toward. As we automate the context collection process, volume becomes less of a factor. It still matters, though: as in an emergency room, where nurses triage patients before doctors run full exams, a fast first pass removes duplicates and known-benign noise so that in-depth investigation goes to the alerts that warrant it. 

In many implementations, a team of specialist agents works toward a common goal: one will collect information from various sources, while another collates the timeline. The agents collaborate to provide investigation at machine speed and ensure the alert is processed from the moment it is ingested into the system to a reasoned verdict, without human intervention. This is where the industry is moving, with new terms like ‘agentic AI’ and ‘AI SOC’. And the exact marketing term matters less than the overall underlying mechanism and idea it is based on.

What Burned Analysts Should Care About

If you’ve ever had an AI agent provide a confident, incorrect verdict related to an alert, then you know that the most critical question is not whether it can reason or investigate but rather whether you can verify the reasoning and its grounding, the evidence chain used to get to this conclusion. That verification is not free: According to Torq’s 2026 AI SOC Leadership Report, which surveyed 450 security leaders, analysts already spend an average of 8.6 hours per week overseeing AI outputs. While that oversight time is repaid many times over by the manual work AI takes off analysts’ plates, a platform that makes verification fast is still worth more than one that only speeds up investigation. 

This depends on:

  • How the context was gathered: The agent decides what to look at next, and that planning is probabilistic by nature. The collection must not be: every piece of evidence should come from a deterministic query against your own tools, returning exact observables like an IP, hash, user, or hostname, with a reference you can follow back to the source. This will make a big difference in alerts where plausible-sounding hallucinations can cause the most damage.
  • How and how much transparency is provided: Don’t settle for less than a fully auditable record of the reasoning behind every decision, the evidence it pulled, the sources, and the chain to the verdict. Indeed, while an incorrect verdict coming from a black box is a minefield, one with full transparency is more of a bug that you can find, understand, and fix. 

Transparency is the key difference between the tool that burned you and one you can have in production. It’s the most important thing to verify in your pilot: How transparent are the agents? Can they show the full reasoning chain? Different platforms will yield very different outcomes, so make sure you always substantiate claims with real data. 

Two cautions apply. A reasoning trace written by a model is not guaranteed to reflect what actually drove its output, so verify the evidence links rather than the narrative. And a trace only shows what the agent looked at, not what it skipped, so ask whether the platform shows which sources it didn’t query and why.

  • How deep your integrations are: An agent can only be as good as its foundation. Point it at a shallow, poorly integrated stack, and you will get shallow results: garbage in, garbage out. Context is the fuel, so beyond the quality of the AI model you pick, the depth of your integrations and agentic tools will determine the quality of your results. It also limits what you can verify: an agent can’t cite evidence from a source it can’t reach.

What It Means for the Bar You Set

In the second post of this series, we discussed how maturity is knowing what you are comfortable with when considering automated verdicts vs. manual reviews, and how to be intentional about it. With investigation at machine speed, you can genuinely raise your bar. Alerts that you couldn’t investigate due to fatigue at 2 a.m. can now be investigated with complete traces and full evidence. 

This shrinks the share of alerts you have to intentionally let go of, mostly because investigation is now cheap enough to run around the clock. Be clear about what that implies, though: closing an alert because an agent judged it benign is already a decision, and when that verdict is wrong, it fails silently. So the bar now applies as much to verdicts as to investigations.

What This Post Is Not Claiming

There is something I have carefully set aside until now: letting the machine act on its own. Beyond the verdicts discussed above, trusting it to act on the outcome of an investigation, for example, by containing a host in production, is a whole different ball game. 

This is the biggest question in this series, and we’ll discuss it in our next and final post. If agentic analysis can automate evidence collection and reasoning over it, and provide full transparency into the reasoning chain, then it has earned its place to investigate and help you save a considerable amount of time. In order to act, they need to earn something harder: your trust that the confidence with which AI agents plan to act is justified.

What This Means for You

Odysseus didn’t let Tiresias steer his ship. He made the journey, heard the prophecy, and kept control. But the prophecy was right: when his crew ignored its warning about the cattle of Helios, it cost them their lives. Keeping control does not mean discarding good evidence. This is how you should feel about agentic investigation. Let the AI agents make the journey, gather the context, suggest a verdict, and provide you with full transparency into how they got there. But you should be the one to decide what to do with it, until they’ve earned more. 

Next in this series, we’ll look at how automation earns the right to act and how trust should be determined.
SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Build vs. Buy AI SOC: A Decision Framework for CISOs

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

A Fortune 500 CISO recently told me, “If you are not implementing some form of autonomous threat detection and response, then even your best defenders will fall behind.” Attackers have weaponized AI and automation, driving up alert volume and threat sophistication. The use of agentic AI for defense is an absolute necessity to level the playing field. Security leaders now face a foundational decision: Build a homegrown AI SOC platform or buy a commercial one?

This post breaks the decision into four dimensions: time to value, total cost of ownership, capability ceiling, and organizational risk. It ends with a short test for when building is the right call.

Why Security Leaders Are Tempted to Build an AI SOC

The case for building is intuitive. You get full control over your data, your models, and your roadmap.

For some organizations, that matters a great deal. If you have a unique data environment, bespoke compliance requirements, or a security architecture no commercial vendor can support, a custom build may be the only viable path. A few large enterprises with mature AI/ML teams can sustain that investment.

They are the exception, not the rule.

The Hidden Costs of Building an AI SOC Platform

Most organizations underestimate what building really takes. The initial headcount estimate rarely captures the full operating cost. A homegrown AI SOC carries ongoing work in at least six areas:

  1. Model operations: AI/ML model development, retraining, and drift management
  2. AI harness: Maintaining the chassis, safety controls, and performance evaluation around the model
  3. Support: Internal customer support and analyst enablement as the platform evolves
  4. Infrastructure: Performance tuning, GPU compute, and data pipeline costs at scale
  5. Platform security: Defending the AI layer itself against adversarial inputs, model poisoning, and prompt injection
  6. Governance: Regulatory explainability and audit trail requirements

The Talent Problem

AI/ML engineers who also understand security are scarce, and you will be competing with hyperscalers on compensation. Key-person risk is real. If two people own your model and harness and one leaves, you are running a fragile platform.

The Opportunity Cost

Every engineering cycle spent maintaining software is a cycle not spent on the daily work of security operations. You are now a cybersecurity vendor in addition to your team’s core mission of securing the business. The overwhelming majority of CISOs I speak with — 69 out of 70 in a qualitative July 2026 sample — have no desire for such a distraction. Securing the business is hard enough. For them, it was never a question of “Can I?” but a question of “Should I?”

The Data Ceiling

The most important limitation may be this one: a homegrown AI model begins and ends with your own telemetry.

Commercial vendors train on threat signals from thousands of customer environments. That gives them pattern recognition that a single organization cannot replicate, especially for novel or low-frequency attack techniques.

The Case for Buying an AI SOC Platform

Commercial AI SOC platforms compress time to value realization. Agentic triage can be up and running in hours. Agentic investigation, wired in a little more than a day. Response automation can be implemented in just a few more days. AI SOC platform vendors offer SLA-backed accountability and continuously update detection models as the threat landscape changes. The vendor absorbs the cost of model operations, infrastructure scaling, and talent retention.

For the overwhelming majority of enterprises, that is a better use of capital.

What do you mean by “AI SOC?“
When most people say “AI SOC”, what they mean is agentic alert triage. At Torq, when we say AI SOC, we mean using agentic AI and automation to streamline security operations from alert triage through investigation, risk containment, and root-cause remediation. That is end-to-end SecOps. Words matter. Make sure you are speaking the same language.

What About Vendor Lock-In?

Executives often name vendor lock-in as the main risk of buying. Build lock-in is every bit as real: proprietary schemas, undocumented model logic, and institutional knowledge trapped in a small team. Refer back to the key-person risk mentioned earlier.

Neither path is free of switching costs. The real question is which risk profile you can manage better.

Build vs. Buy AI SOC: Decision Matrix

DimensionBuildBuy
Time to value12–24+ months to production-grade capabilityValue on Day 1, production-scale in days or weeks
Upfront costHigh: headcount, infrastructure, toolingPredictable SaaS subscription
Total cost of ownershipOften underestimated; grows significantly with scaleTransparent; vendor absorbs scale costs
Detection qualityLimited to your own telemetry and historyTrained on signal from thousands of environments
Talent requirementScarce AI/ML and security engineering staffMinimal; vendor manages model operations
CustomizationFull control over models and roadmapConfiguration within vendor capabilities
Accountability on missesInternal only; no contractual backstopVendor SLA with escalation path
Data residency / complianceFull control over data handlingRequires vendor diligence; often solvable

When Building an AI SOC Makes Sense

Building may be justified when all of the following are true:

  1. Regulatory or data residency requirements rule out every commercial option after thorough diligence.
  2. You already have a mature, staffed AI/ML team with security domain expertise.
  3. Leadership accepts a 12–24+ month runway before production-grade capability.

If even one of these is missing, the build case gets much harder to defend.

The Strategic Question for Every CISO

Is building and operating AI platforms your core competency, or is catching threats?

For most security organizations, every dollar and hour spent on platform engineering is a trade-off against detection capability, response speed, and risk management. Buying an AI SOC platform is not a loss of control. It is a deliberate decision to put scarce resources toward the work that matters most.

Evaluating your options?

Get a demo of the Torq AI SOC Platform and see how enterprises triage, investigate, and respond to security events at scale.

FAQs

What is an AI SOC platform?

An AI SOC platform uses AI and automation to triage, investigate, and respond to security events at scale, reducing the manual workload on SOC analysts.

How long does it take to build an AI SOC?

Plan for 12–24+ months to reach production-grade capability. Buying a commercial platform typically cuts deployment to days or weeks.

Is vendor lock-in a reason to build instead?

Not by itself. Homegrown platforms create their own lock-in through proprietary schemas, undocumented model logic, and knowledge concentrated in a few people.

Can a bought AI SOC meet data residency and compliance requirements?

Often, yes, with proper vendor diligence. Building is justified only if diligence rules out every commercial option.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Why I Joined Torq, and What Comes Next

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

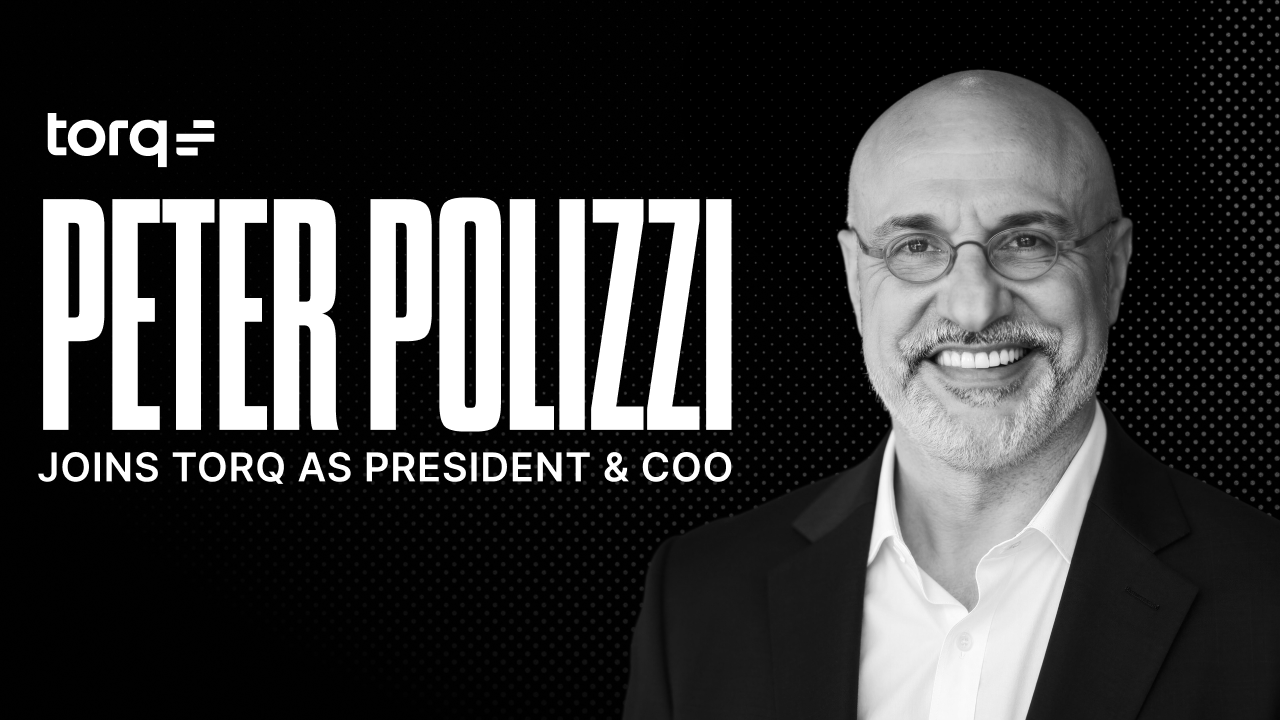
Three times in 28 years of enterprise software leadership, I’ve been inside a company at the exact moment it had to become something bigger. At Palo Alto Networks, I led the Technical Sales and Consulting organization through the company’s platform-to-cloud transformation. At Splunk, I helped scale its cloud transformation and build the operational foundation ahead of its acquisition by Cisco. At HashiCorp, I scaled the global technical field organization and then helped architect its acquisition and integration into IBM.

Each of those companies hit the same inflection point. The product had earned its place, the customers were there, and what mattered next was whether the company could grow fast enough to match the scale of the opportunity in front of it. 

Torq is at that moment right now, and it’s why I joined as President and COO.

The SOC Is Being Rebuilt 

We’re deep into the age of agentic AI, and enterprises are racing to put it to work. That same wave is expanding the attack surface at a rate we haven’t seen before. Generative AI, the spread of autonomous agents, and the massive volumes of data moving between agents and endpoints all create new ground to defend.

For enterprise security teams, that means protecting environments that span machine identities, hybrid infrastructure, distributed data, and a patchwork of security tools. A SOC that runs on human-speed processes and manual triage can’t keep pace with that.

Enterprises need a fundamentally different way to defend themselves, and Torq is built to deliver it. The Torq AI SOC Platform gives security teams the intelligence, automation, and control to operate and defend at machine speed, with specialized AI Agents doing the advanced work and people overseeing the decisions that matter.

What This Team Has Already Built

It would be a miss if I didn’t start by recognizing the people who got Torq here. Torq has accomplished something extraordinary: It built a category-defining platform and won the trust of some of the world’s most discerning enterprises.

Global enterprises like PepsiCo, Siemens, Telefónica, and Virgin Atlantic trust the Torq AI SOC Platform with their security operations. KuppingerCole Analysts named Torq a Leader in its 2026 Leadership Compass for the Emerging AI SOC, and IDC named Torq a Leader in the IDC MarketScape: Worldwide Standalone AI SOC Platforms 2026 Vendor Assessment.

Ofer and the founding team saw the changes coming early and built for it. The rest of the Torq team turned that vision into a platform enterprises trust to run their security operations. To everyone who took Torq from ideation to reality, you should be very proud.

Scale Is A Neuropath

“Scale” is one of the most overused words in our industry, so I’ll be specific. To me, scale is the neuropath that lets a company add a much larger customer base, a broader product portfolio, and a larger global team while adding fly-wheel DNA. It’s the immediate processes, systems, and handoffs built for the company you’ll be in two years.

I come back to two questions with every team I lead: How do we scale ourselves, and how do we enable others to scale around us? Every system we run at Torq has to be ready for many times the number of customers we serve today.

I’m not here to change what’s working. Torq already has all the marbles on the table: the product, the customers, the team. My job is to build the connective tissue that lets us roll faster. 

Our Ambition: Double Every Year

Torq’s plan is ambitious, and I’d rather be direct about it. We intend to double in size annually. That means significantly growing our global workforce and our enterprise customer base, further differentiating our product portfolio, and pursuing a strategic portfolio, partnerships, and acquisitions.

The bad guys are highly automated, and now, in this agentic economy, their capabilities have been expanded upon exponentially. We know our differentiated product-market fit and which enterprise customers benefit from the automation and agentic platform, getting the best MTTC and MTTR. Security is a platform play, not a point product archetype. . We’re aligning every function, from product to go-to-market to customer success, around serving those customers, because that’s where we see exponential returns.

With that alignment in place, we have a clear path to triple-digit growth in 2027 and 2028.

How We’ll Operate: One Team, Flying in Formation

Growth at this pace puts pressure on every part of a company, and culture is what holds it together. As we scale, we’ll run Torq on three principles:

  1. We operate as one team, no matter where you sit in the company.
  2. We help each other toward the common goal. When something breaks, we fix the process instead of looking for someone to blame.
  3. We fly in formation. Everyone knows where we’re headed and how their work fits in, so we can move fast together.

We’ll stay focused on our north stars, and we’ll trust in the mission, the strategy, and each other.

Our digital way of life is under consistent threat. Those protecting it are under continuous pressure to ensure they protect their brand and customers. The risk vectors continue to multiply, and Torq plays a critical role in providing a single point of MTTC and MTTR for all the other security brands doing their individual parts

We proved that the agentic SOC is the future of security operations. Now we’re scaling the company that will define this category for the next decade, and our ambition is clear. Torq will be the platform every SOC runs on. I couldn’t be more excited to build that future alongside this team.

Let’s roll up our sleeves.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

How to Measure AI SOC ROI: Beyond Hours Saved

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to Virgin Atlantic, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.

Every CISO I speak to eventually arrives at the same meeting: the one where you have to show what the investment bought you. And almost everyone walks in to defend their AI SOC ROI with the same number: hours saved.

It’s the weakest number you can bring. It invites the obvious follow-up question about headcount, which you don’t want to answer because the answer is that you aren’t cutting anyone. Worse, it describes a fraction of what actually changed. AI SOC ROI means different things depending on who’s asking, and “how many hours did we save?” is only one form of return.

Here’s how I’d measure it instead.

Measure AI SOC ROI as an Incremental Return

Adding AI agents doesn’t mean firing analysts, so don’t frame it as money saved. Frame it as an incremental return: for the extra you spend on agents, how much more do you get back?

Take an illustrative team of 10 analysts, still overwhelmed by volume and short on coverage across controls and projects. Add an agentic layer at roughly the cost of two or three good analysts, and you can automate the vast majority of your team’s Tier 1 work. Those analysts are released from the mundane and repeatable work and reallocated to higher-value activities. Compliance improves because the team now covers more controls. Risk from machine-speed attacks drops because triage and response happen at machine speed. Re-motivated analysts start engineering and delivering new capability on timeframes you couldn’t have committed to before.

That’s a significant uplift across the board, and it would have taken a team twice the size under a traditional, human-scaled model. That’s the number to bring.

Run Two Dashboards, Not One

One transformation, two audiences. I’d split measurement into a strategic dashboard and an operational one.

The strategic dashboard tracks what the board cares about: what you spent, how headcount was reallocated, how far risk came down, whether control metrics are improving, and whether the auditors are satisfied. If you’re reporting upward, ROI might mean that risk thresholds are met, the likelihood of breach is reduced, the cost of exposure is reduced, and legal and regulatory obligations are satisfied. It might mean showing no increase in committed headcount while efficiency and control coverage both go up. It might mean proving you delivered this transformation alongside a tech debt program or an ERP onboarding without derailing either.

The operational dashboard tracks how the work itself has changed: how many people moved from operations onto projects, which roles were refactored into the new structure, and how far case resolution time has dropped. In one enterprise I know, that went from 30 minutes to two. Quality improves as well, because every case arrives enriched with more context before anyone makes a decision.

The link between the two is capacity. Freed capacity isn’t a saving sitting in a spreadsheet: it’s value you redeploy, and the strategic dashboard is where that shows up.

The Benefits Most CISOs Aren’t Measuring

The secondary effects are where a lot of the real value hides, and most teams never put a number on them.

Reallocated hours change your risk posture. Reduced exposure changes what the business sets aside for cyber insurance. There’s the story you tell a regulator, for example, about running strong, agentic security inside critical national infrastructure, and there’s the evidence you can produce for the EU AI Act and the Cyber Resilience Act. 

None of that is technical, and all of it counts. The business benefits matter as much as the operational ones.

Get the Right People in the Room

The measurement conversation can’t stay inside the SOC, and this is where I see good programs undersell themselves.

You need the GRC team, enterprise risk, and procurement involved. Often, you want your other vendors too, because they’re seeing reduced volumes and faster response on their side, and that’s evidence you can use. Bring in any IT outsourcing team that owns part of the process. Don’t forget the regulators. Each of them measures your success differently, and if you’re the only one defining the measure, you’ll define it too narrowly.

Score AI SOC ROI Across All Three Layers

I’ve written before about the three layers you’re buying with an AI SOC: outcome, judgment, and execution. Measurement works the same way, and each layer has a tangible, measurable benefit.

  1. At the outcome layer, you set risk reduction targets, machine-speed defense requirements, compliance obligations, and the confidence you need to demonstrate to your board, your regulators, and your insurers. These get defined up front and measured within the judgment function.
  2. At the execution layer, you measure the incremental return described above. That’s where the leverage lives, as long as you measure it the right way.
  3. At the judgment layer, you measure continuous improvement, decision quality, and audit transparency. Can the system show you its reasoning? Can you tune it? Does it get better? That’s the layer that tells you whether you bought a capability or just a tool.

If a vendor can only show you the execution layer and can’t speak to judgment or outcomes, the relationship will stall. That’s worth knowing before you sign rather than after.

The Org Change That Makes the Metrics Move

There’s a hard truth underneath all of this. Without organizational change, the metrics plateau no matter how good the technology is.

Adopt the three-layer model as a product approach. Lay out your services, define the capabilities that deliver them, and measure how every capability performs. Move people into roles that understand this approach — something service- and capability-oriented — and split them into connected teams that deliver on outcomes, execution, and judgment. 

The technology gives you the capacity. The organization decides whether that capacity turns into results.

Inaction Is Its Own Risk

At the very least, after all of this, have a plan. If your plan is not to adopt an AI SOC yet, you need a justification that stands up to scrutiny, and I’d challenge you to find one. Are you saying machine-speed threats aren’t a risk to your organization? Do you have the resources to cope with current alert volumes, let alone next year’s?

Look at how fast a machine-speed attack actually moves. If your first line of defense runs at human speed, you’re handing attackers the dwell time they need before you’ve begun to respond. The exposure that comes from standing still outweighs the risk of taking a first step in the right direction. A tentative, risk-based, well-planned move forward beats waiting for a certainty that isn’t coming.

Whatever you choose, run it like a program rather than a purchase. Start with the repeatable Tier 1 work that eats the most time, prove it, measure it in terms your board and your auditors care about, and expand as trust builds.

You need a plan. Start building it now.

The full AI SOC Buyer’s Guide has the measurement dashboards, the incremental AI SOC ROI model, and the questions to bring into the room with every vendor on your shortlist.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Torq For Good: Bringing GO Kart Gaming Stations to Niswonger Children’s Hospital 

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Maycie Belmore is Senior Content Marketing Manager at Torq, where she helps lead content strategy across the blog, social, and website. Maycie focuses on SEO and AEO content and turning complex topics like agentic AI and security automation into clear, practical content for security teams. Maycie is also a voice for the Torq brand through video, live webinars, and events.

Some days remind you why you do what you do, and sometimes that has nothing to do with your actual job.

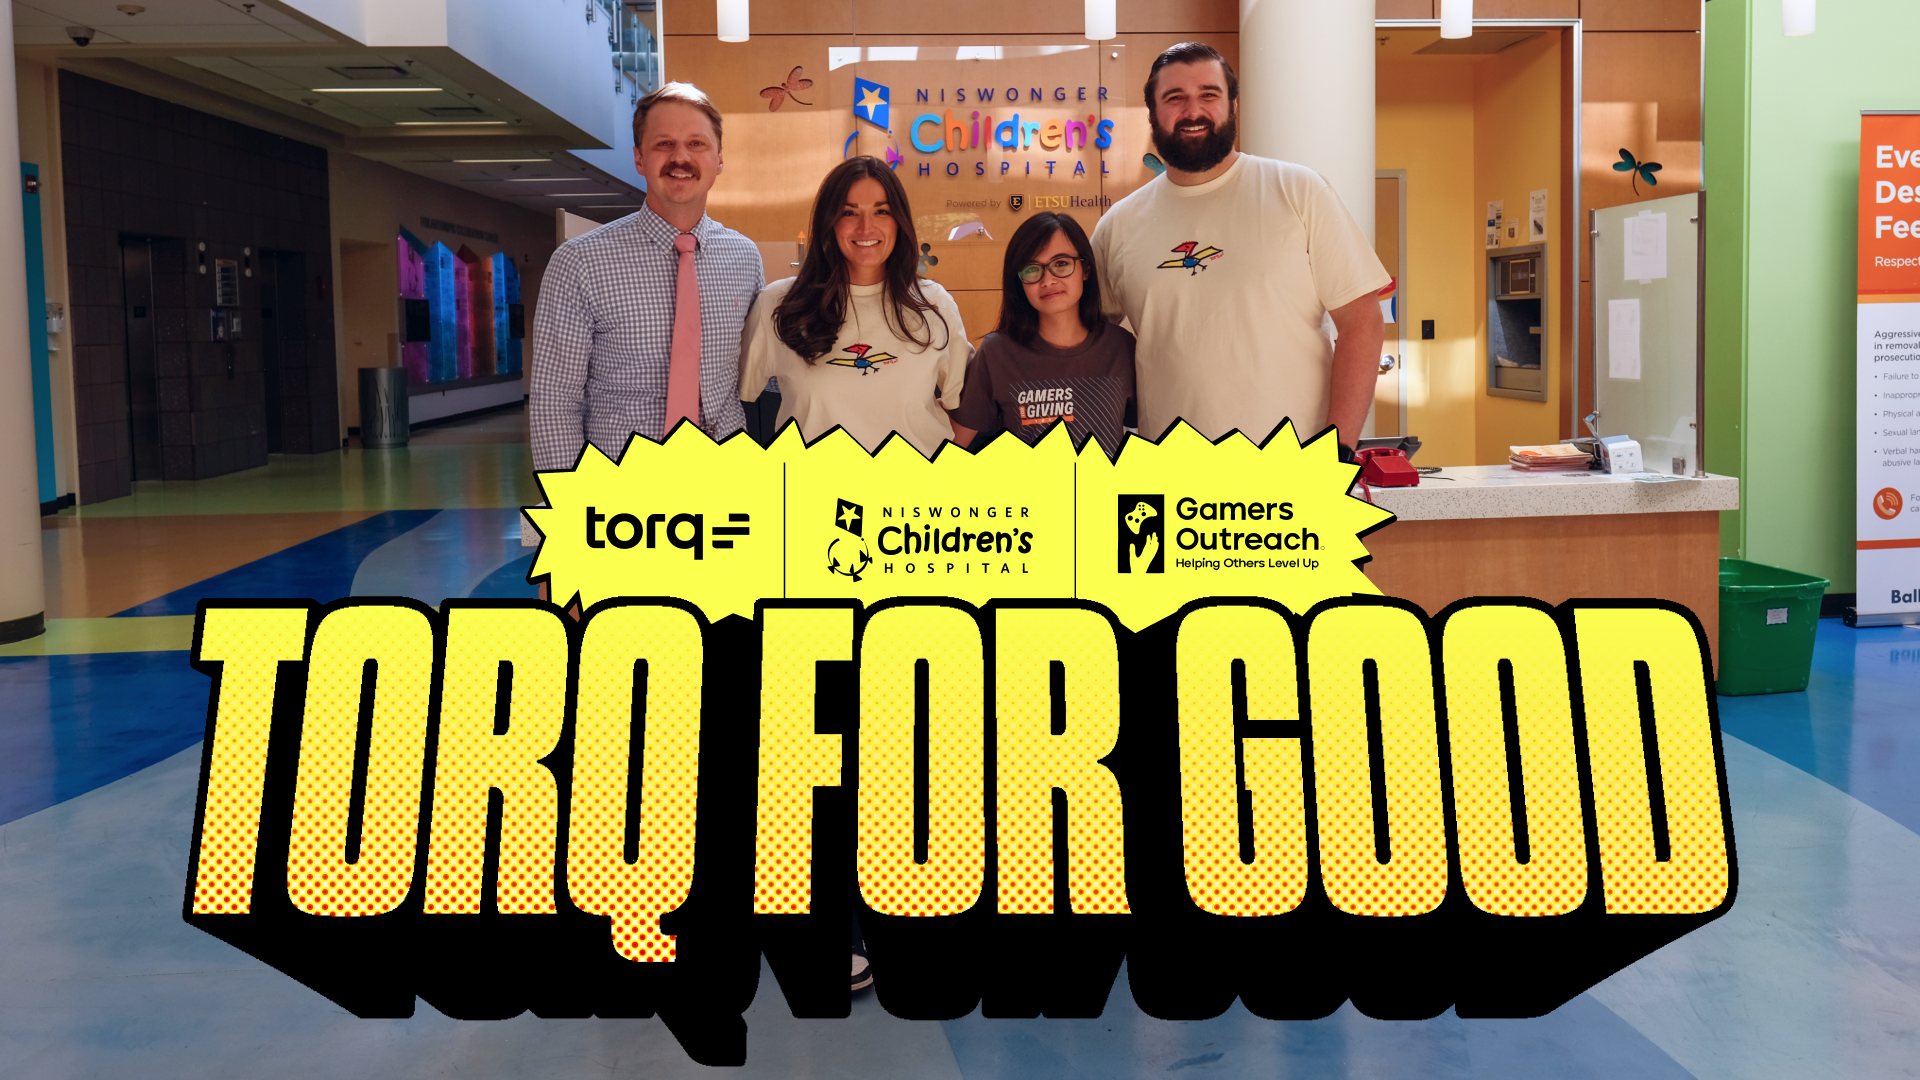
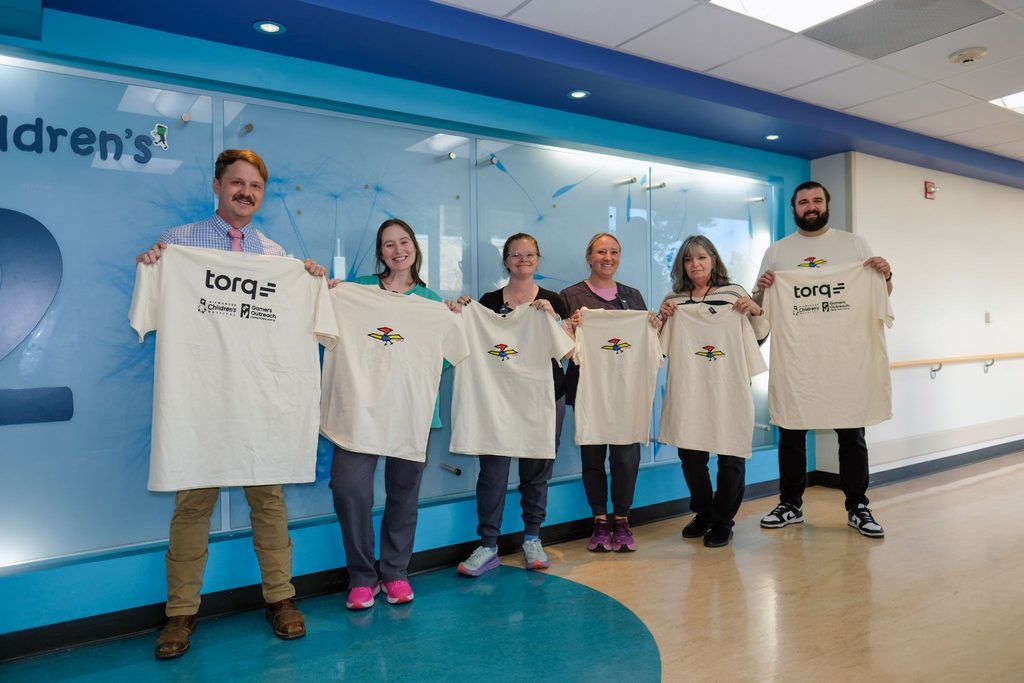
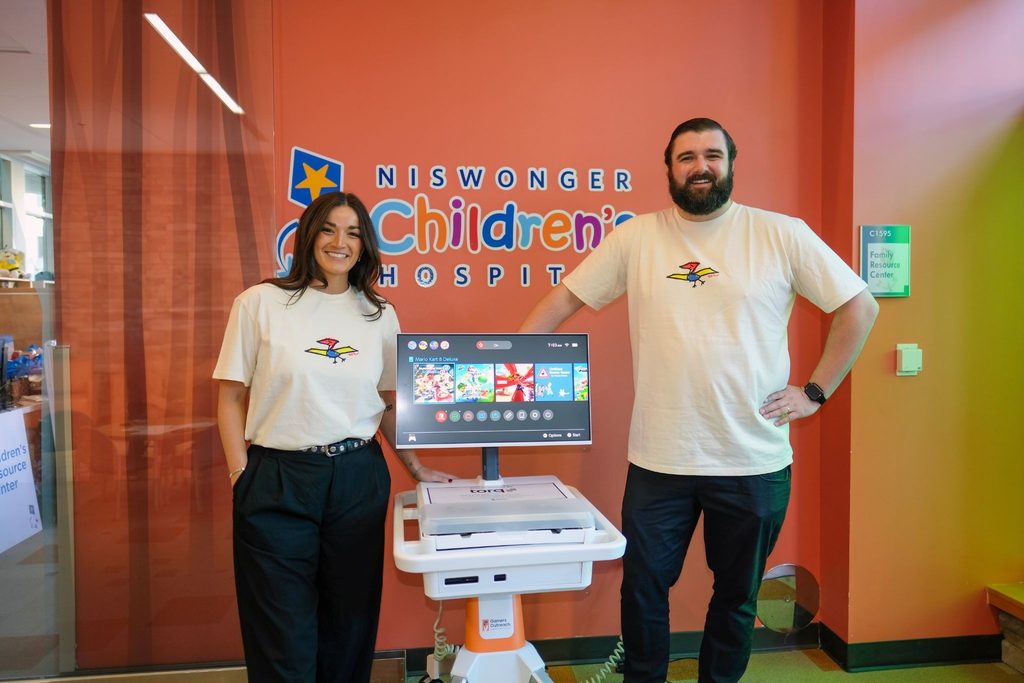
Torq For Good is our internal initiative to give back to local communities around the world. It builds on Torq’s previous investments in supporting young people and the next generation. This October, it sent my colleague Bob Boyle and me to Johnson City, Tennessee, to join something really special at Niswonger Children’s Hospital. It’s rare to have such an incredible opportunity to do something we don’t get to do every day. And I’m so thankful to work for a company that makes an effort to make a difference. 

Torq teamed up with Gamers Outreach, a charity that empowers hospitalized families through play, to donate GO Kart multi-platform video gaming stations that roll right up to a patient’s bedside. Both GO Karts are permanent for the hospital, so patients can keep playing long after our visit. Gamers Outreach’s programs, including the GO Karts, support more than 350 hospitals and deliver over 8.4 million gaming experiences each year. 

Playing a video game might seem like the most ordinary thing in the world. But when a hospital stay keeps a child from school, birthday parties, and everything else that makes childhood feel like childhood, a game becomes something bigger. It gives them a chance to feel like a kid again. 

Our co-founder and CEO, Ofer Smadari, said it best: 

“Our team knows what great technology can do, but the best of it brings people together. For a child in the hospital, a video game is more than a game. It’s a way to connect with others, and forget for a little while where you are. Partnering with Gamers Outreach to put GO Karts in Niswonger Children’s Hospital is our way of giving back to a community that matters to us. We hope these patients and their families get a morning full of fun, and that the GO Karts keep that fun going long after we leave.”

– Ofer Smadari, Co-founder and CEO, Torq

Meeting The Team

Bob and I kicked off the morning at Niswonger Children’s Hospital, part of Ballad Health and the only children’s hospital in the region. It serves children and teens across East Tennessee and Southwest Virginia with state-of-the-art medical care in a family-centered environment, and it has been the region’s Children’s Miracle Network Hospitals affiliate for more than 30 years. There, we met Rodney Rhodes, the hospital’s Child Life Manager, and Jessica Fuller, the Media Relations Manager.

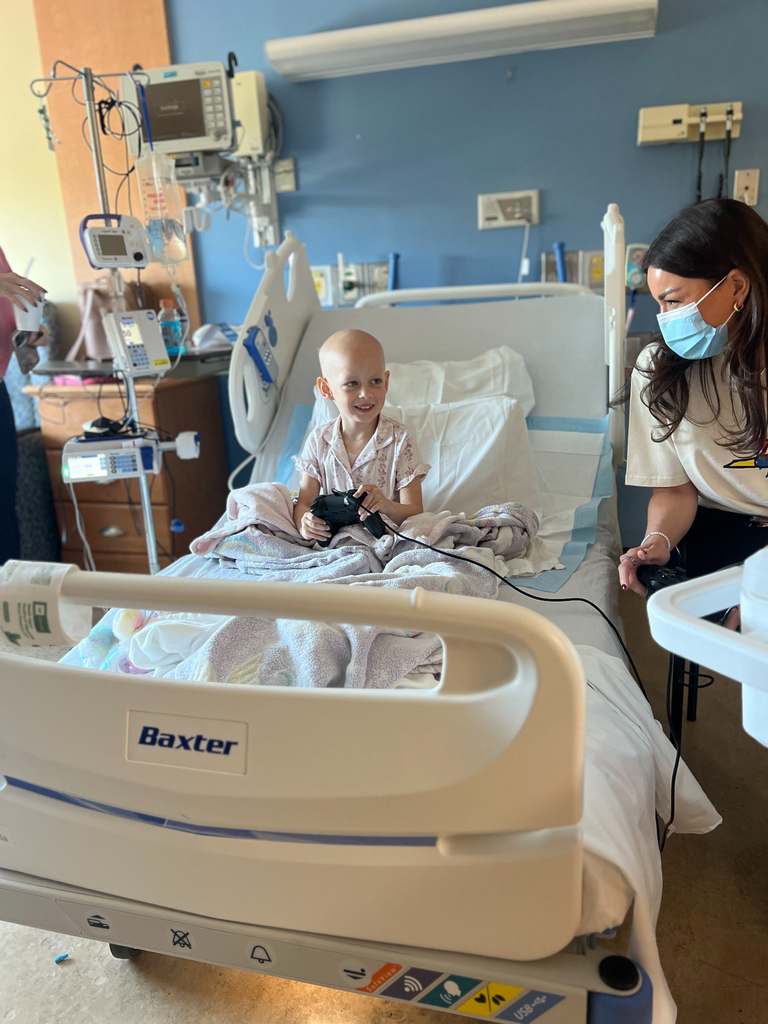
Next, Shanna Talaban from Gamers Outreach showed us around the GO Karts. These medical-grade video game kiosks are built for hospitals. Each one comes with Xbox and Nintendo Switch consoles, a monitor, controllers, and games, so patients can enjoy play as therapy during their hospital stay. Best of all, both GO Karts now live at Niswonger Children’s Hospital, so the kids there can keep playing every day, not only on event day.

The event also drew local media. Reporters from ABC TV affiliate WJHL News Channel 11 and Johnson City Press stopped by to hear about the joint initiative between Torq, Niswonger, and Gamer’s Outreach. I’d like to thank our fantastic PR agency Highwire for their help in creating community awareness for all the great work Niswonger and Gamers Outreach do.

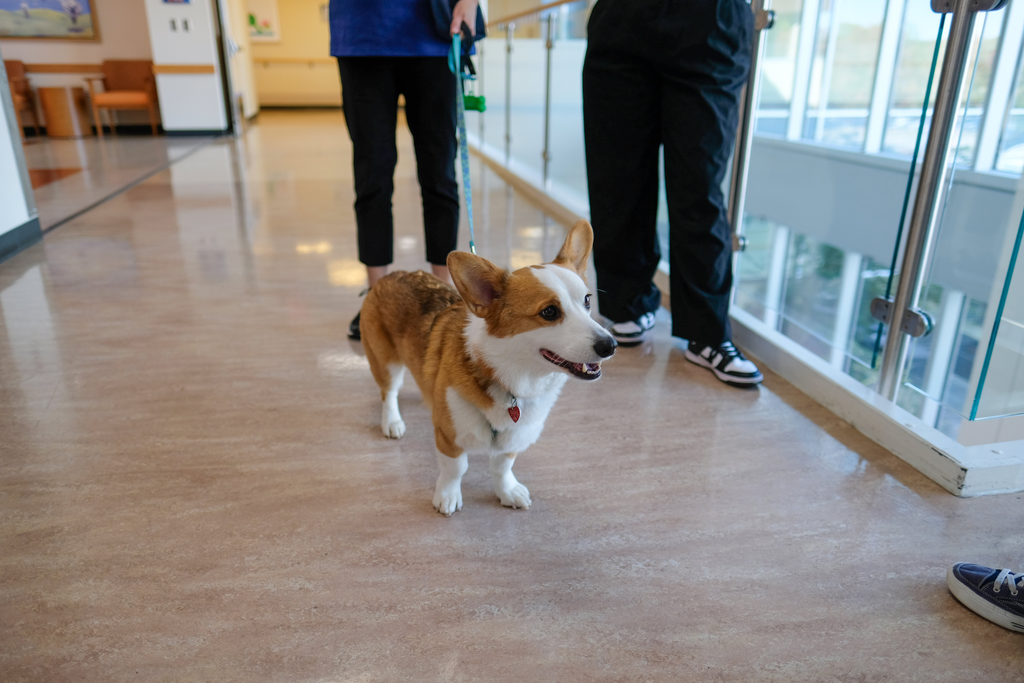
Everyone welcomed us so warmly, and their excitement to have us there was obvious. We even got to meet Rigby, the hospital’s therapy dog. He roams the hallways and bedsides and arguably has one of the most important jobs in the hospital.

Bedside with the Bravest Kids I’ve Ever Met

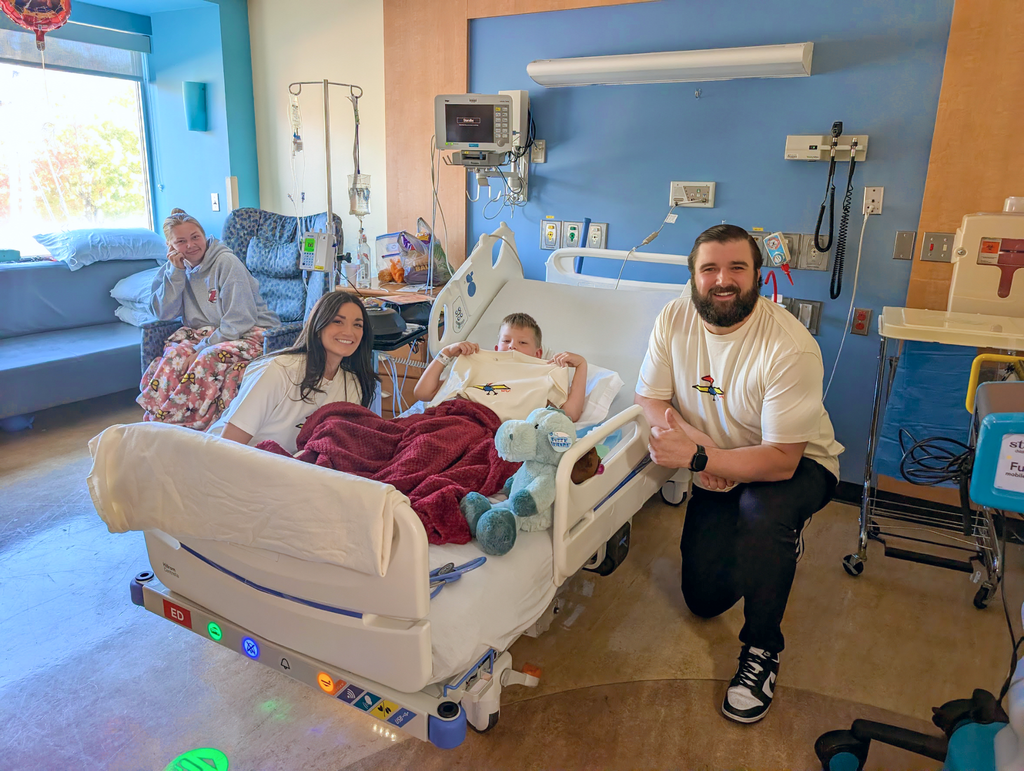
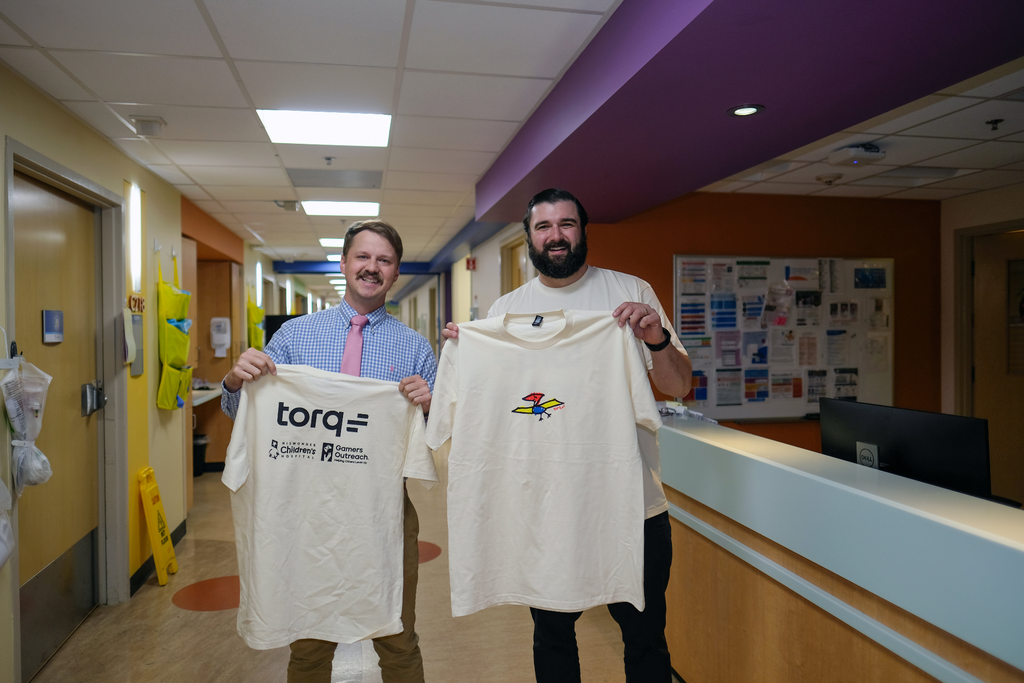
Then came the part I’ll carry with me the longest. We spent the day having bedside conversations with kids between the ages of 4 and 15. We built rapport, laughed, and passed out custom-made Niswonger Children’s Hospital + Torq t-shirts. 

Seeing these children show so much bravery and strength through illnesses they shouldn’t have to face at such a young age was tough. But when we wheeled in the GO Kart and their faces lit up like Christmas Day, our hope came true: these kids got a moment to feel like kids again. 

That feeling stayed with me all day, especially when I met Isla, one of the younger patients I spent time with. She was new to Mario Kart Racing but after a quick lesson and a few giggles, she picked it up, and by the end, she was beating me! 

Rodney Rhodes, the hospital’s Child Life Manager, told WJHL that a gaming system can turn a day full of missed school and missed birthday parties into the highlight of a child’s week. 

And Bob and I watched that happen in real time. 

Giving Back Matters

Stepping out of our cybersecurity world and into a completely different one to give back showed me exactly why Torq For Good exists. Torq’s funding made this day possible, and it shows how businesses, nonprofits, and healthcare providers can work together to support hospitalized children, their families, and a wider community.

“True community support means showing up where it matters most. Thanks to our partnership with Torq and Gamers Outreach, our patients get an incredible experience filled with gaming, excitement, and shared fun. Bringing gaming right to the bedside brings so much joy to our children and reminds them how many people across Tennessee are working to help support their healing.”

– Rodney Rhodes, MHA, CCLS, Manager of Child Life Program at Ballad Health Niswonger Children’s Hospital

I’m grateful to work for a company that wants to make a difference. Torq spends its days protecting enterprises from security threats, but it also invests in the communities around us. Being part of Torq’s initiative of giving back, and traveling to Johnson City, Tennessee to see it firsthand, was a once-in-a-lifetime experience that Bob and I will carry with us forever. 

Thank you to Gamers Outreach, to Rodney and the team at Niswonger Children’s Hospital, and to every patient and family who welcomed us in. We hope the GO Karts keep the fun going long after we leave. They’ll stay right there at the bedside, ready for the next kid who needs it.

Want to read more? Check out the coverage from the Johnson City Press and WJHL (also on MSN).

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Torq Retrospect: Your SOC’s Past Shouldn’t Be the Price of Switching

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Noam Cohen is Head of Artificial Intelligence at Torq, where he leads the AI research and engineering work that powers the platform’s agentic SOC capabilities. Noam’s work at Torq spans the core AI systems behind autonomous threat investigation, SOC memory, confidence-based decision thresholds, and the guardrails that make agentic AI trustworthy enough to act in production security environments.

Key Takeaways

  • Moving to an AI SOC shouldn’t wipe out the case history your analysts spent years building.
  • Torq Retrospect uses an LLM once to learn the schema mapping, then copies records deterministically. It never rewrites them.
  • Unmapped fields are measured, and a human checks a sample before anything is called done.
  • One customer’s 2,000+ cases went from export to triage-ready in under an hour.

The new platform is approved. The pilot went well, the budget is signed, and the team is ready to move. Then someone in the kickoff asks the question nobody planned for: what happens to our history?

Three years of closed cases. Every alert someone already proved benign. Every host that turned out to be the red team’s box. Every incident write-up that explains why a particular 2am login pattern is fine for that one service account. That history is where most of a SOC’s hard-won knowledge lives, and it sits in a schema the new platform has never seen.

The usual approaches are both bad. Spend a month building a migration pipeline, or go live with an AI that knows nothing about you and let your analysts re-teach it from scratch. Plenty of teams pick a third option: they don’t switch.

We built Torq Retrospect so that the question has a short answer. Retrospect takes your case history from whatever system holds it today and rapidly makes it usable in Torq, already validated, indexed, and recency-weighted.

Every SOC Switch Starts With Amnesia

Think about the last time you set up a new phone. Ten years ago, that meant losing half your contacts and emailing yourself photos. Now you put the two phones next to each other, and twenty minutes later, your apps, messages, and photos are just there. Nobody would buy a phone that made them start over.

SOC platforms are still in the ten-years-ago era. Switching tools, whether from a legacy SOAR, a ticketing system, another AI SOC, or an MDR’s case portal, usually means your new system starts with an empty case history.

That matters more for an AI SOC than it did for older tools. A playbook engine doesn’t care what happened last year. An AI that triages alerts does. When it sees a suspicious PowerShell execution on a finance workstation, the most useful thing it can know is that your team saw the same pattern forty times last quarter, and every one of them was a patching script. Without that precedent, the AI reasons from first principles every time (and first principles are exactly what produces the false positives your analysts are tired of closing).

Traditional Migrations Move Data and Lose the Meaning

So teams migrate. Someone exports the old cases. Then the bespoke pipeline work starts: cleaning malformed records, matching the old fields to the new ones, deduplicating cases that were merged or reopened, and converting formats that never quite line up. Teams we’ve talked to say this takes anywhere from weeks to a month, and that’s when it goes well.

Time isn’t the only problem. A traditional migration has three ways to fail quietly:

  1. Loss in conversion. A field that doesn’t map cleanly gets dropped, flattened into a free-text blob, or truncated. Nobody notices until an investigation needs it.
  2. No proof it worked. Ensuring nothing is lost means building a validation process alongside the pipeline. Most teams spot-check a few cases and hope for the best.
  3. Imported isn’t usable. Even if every record arrives intact, the new system still has to find the right one at the right moment. Dump three years of cases into an index with equal weight, and the 2023 incident tied to a decommissioned server competes with last week’s case on the same alert type. The history is all there, and it’s mostly noise.

In 2026, there’s an obvious shortcut: Point an LLM at the old cases and have it rewrite each one in the new format. It sounds efficient. It also means a probabilistic model is regenerating thousands of records you may one day need in an audit or a post-incident review. One invented hostname or one “summarized” timeline, and your history is no longer your history.

We wanted neither.

Torq Doesn’t Recreate Your Data. We Learn How to Copy-Paste It.

The hard part of a migration was never moving bytes. It’s translation: working out that a field called src in one system, Attacker Address in another, and Origin IP in a third all mean the same thing in Torq’s data model. Field names across security tools agree only loosely. Some are obvious synonyms. Some mean the same thing only in context. Some look alike and mean different things.

That kind of loose-similarity matching is exactly what LLMs have become good at. So Retrospect uses the model where it’s strong, on the schema, and keeps it away from the records.

Retrospect works in four steps:

  1. The LLM reads both schemas. It sees your source system’s fields and Torq’s case data model.
  2. It proposes a mapping. Each source field has a destination in Torq’s model, including cases where the names are only mildly similar.
  3. The mapping becomes deterministic. Once validated (more on that below), it’s a fixed translation. Every record goes through the same rules.
  4. The records are copied, not regenerated. The value in your old system is the same as the value in Torq. The model wrote the instructions for the move. It didn’t touch the cargo.

The LLM’s work happens once per source schema, not once per case. That’s why the job takes minutes instead of weeks. It also means the thing you have to get right is the mapping, and you check it once instead of auditing every record.

Nothing Falls Through Without Someone Seeing It

A deterministic copy still raises the obvious question: what about the fields that don’t map?

Retrospect measures them. Every field the mapping doesn’t cover is counted as unmapped data, so coverage is a number you can read, not something you find out about three months later. If a source field has no home in Torq’s model, it shows up on that list. It doesn’t vanish quietly.

Then a human looks. Before the migration is called done, someone checks a representative sample of migrated cases against the source. The person checking reviews the translation on cases they recognize. They aren’t auditing a black box.

Silent drops and flattened fields, the things that make traditional migrations risky, show up before go-live instead of in the middle of an investigation.

Imported Isn’t Ready Until It’s Indexed

Getting the records across solves the first problem. Retrospect’s definition of done is stricter: the history has to be usable in triage and investigations the moment the migration finishes.

Migrated cases land in Torq’s case management already indexed, and the index knows when each case was created. Recent cases are more relevant than older ones. When Torq Recall looks for precedent on a new alert, last month’s resolution of the same pattern outweighs a two-year-old case from before your environment changed.

That keeps old data from turning into noise. You don’t need to curate your history before migrating it or decide which years are still trustworthy. Bring all of it. Recency weighting means the old cases are there when nothing newer matches, and stay out of the way when something newer does.

Two Thousand Cases, Under an Hour

One customer brought over 2,000 cases from the past year. With Retrospect, those cases went from export to imported, indexed, and ready for alert triage and investigations in under an hour. Compare that to the traditional, legacy path we described above — bespoke pipelines, cleaning, matching, and dedupe — which takes weeks to a month.

That’s just one customer’s migration. A messier source schema or many more years of history will take longer. The expensive part — translating the schema — still happens once, so more cases don’t mean more translation work.

Next, Your History Becomes Judgment

Torq Recall uses your history as memory: when a new alert comes in, it finds the precedent. That’s the first payoff, and it’s live from the hour the migration finishes.

The second payoff is Torq Reflex, which trains a model on your analysts’ past decisions, so that the AI actually learns your team’s judgment, instead of matching cases one at a time. It picks up the “we always escalate this one” instinct that no prompt captures.

A model like that needs decisions to learn from. Retrospect brings them across, each case with its analyst’s verdict attached. Your migrated history is the material Reflex learns your team’s judgment from, so it doesn’t have to start from zero after a switch.

What Torq Retrospect Means for Your Team

  • Switch without starting over. Your closed cases and their verdicts come with you, in Torq’s data model, from day one.
  • Minutes, not a migration project. No bespoke pipeline, no month of cleaning and matching. In the customer case above, it took under an hour.
  • Your records stay your records. The LLM translates the schema once. Your data is copied, never regenerated.
  • Coverage you can see. Unmapped fields are counted, and a human checks a sample, so gaps surface before go-live.
  • History without noise. Recency-weighted indexing puts recent precedent first, so you can bring everything without curating it.
  • The foundation for learning. The same history powers Recall today and gives Reflex the decisions it learns from.

Bring Your SOC’s Past With You

The reason teams stay on tools they’ve outgrown is rarely the tool itself. It’s everything they’ve built inside it. Every SOC that has switched platforms knows the cost: weeks of migration work, or a new system that has to be taught everything again.

The cost of adopting better technology is a thing of the past. With Retrospect, it doesn’t have to be.

Torq Retrospect is part of our series on Context, Memory, and Learning in the AI SOC, alongside Recall, Reflex, and the Torq Context Graph.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Everyone Says Context Matters. I Wanted Proof.

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Amir Kessler is Director of Product Management at Torq, where he leads the Context Engine and Data Fabric, the layer that gives the AI SOC Platform the organizational context it needs to investigate and act. He joined Torq with its acquisition of Jit, where he was VP of Product. Amir has spent more than 15 years in cyber, starting in IDF intelligence and going on to lead product teams at several security companies.

Before Jit became part of Torq, we built our product on one bet: an AI agent investigating a security issue is only as good as what it knows about your organization, including who an account really belongs to, what a server connects to, and what breaks if it’s compromised.

When Torq acquired Jit in May, I brought that bet into the SOC as the foundation of the Torq Context Graph and promptly hit a wall. “Context” is one of the most overused words in AI SOC marketing. Vendor after vendor claims it, with no details on what their ‘context’ contains and no proof of what it changes. To a SOC leader, my vision sounded like everyone else’s pitch.

So here’s what ours actually is. The Torq Context Graph is a live model of your organization that sits underneath every autonomous triage verdict in the Torq AI SOC platform, and it does three jobs: 

  1. Resolves the same person, device, or service across every tool in your stack into a single entity
  2. Maps the relationships between them (which service account can reach which privileged group)
  3. Computes the conclusions an analyst would otherwise work out by hand, like whether an account is dormant, a host is critical, or a user is a VIP 

All of it is kept current as the organization changes, and agents query it during triage instead of reconstructing it from raw logs on every alert.

That’s what separates the Torq Context Graph from most of what gets sold as context. An inventory tells you what you have, and enrichment adds a few fields to an alert. The graph tells the agent what those things mean together, before it makes the call.

Building context that holds up at enterprise scale is hard: every identity, device, and relationship must be resolved across the whole security stack and kept current as the organization changes. That’s the know-how Jit pioneered. But even a well-built graph doesn’t prove itself. I had to show where it moves the needle for an enterprise SOC. So I stopped making the argument and went looking for proof.

At one customer, the same alert kept firing: a Python script churning through batches of GIS map files. Without context, the Torq Auto Triage agent flagged it as suspicious scripting every time. With context, it came out three different ways, depending on what the graph knew about the user and host behind it. One of the three should have been escalated immediately. I’ll come back to it below.

Proof Starts With Real Alerts

ABOUT THE DATA
Every alert in this research came from a customer organization that opted in to share it with us, and every environment was anonymized. These are the alerts real enterprise SOCs face, with all their noise and edge cases — not a dataset built to make a slide look good. To every team that said yes: Thank you. You turned a claim into evidence.

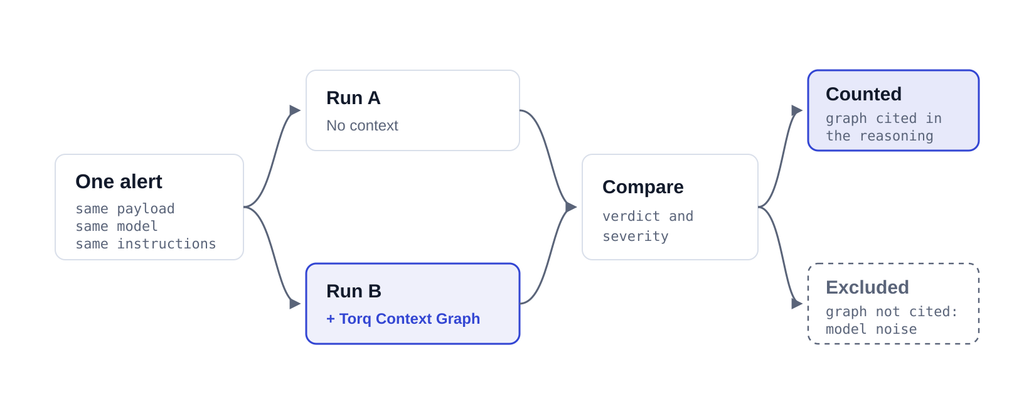
We sampled 400 alerts across customer environments of different sizes and verticals and ran the Torq Auto Triage agent on each one twice: same payload, same model, same instructions. One variable: access to the Context Graph.

The rule was strict. A change in verdict or severity only counted if the graph context appeared in the agent’s reasoning. Anything else was model noise, and we threw it out. Because the Auto Triage agent queries the graph during its analysis to test specific hypotheses, every change leaves a chain-of-reasoning trail: what the agent asked and what it learned.
FIG. 1   Each alert ran twice. Only changes the agent attributed to graph context were counted.
Nearly One in Four Verdicts Changed

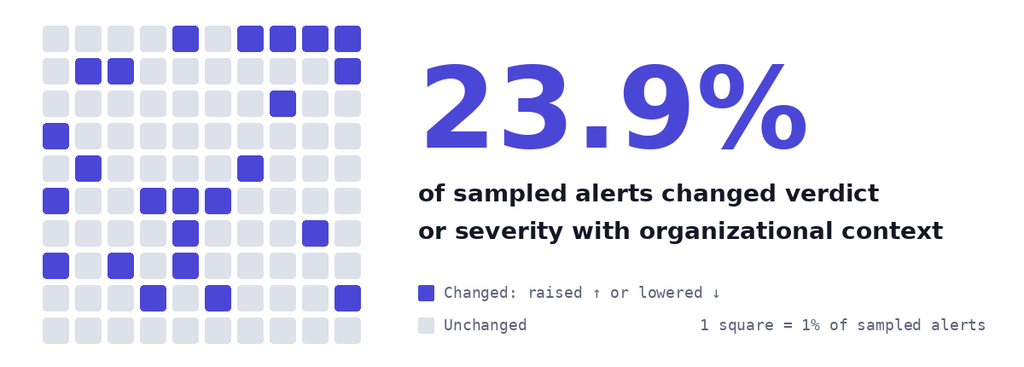
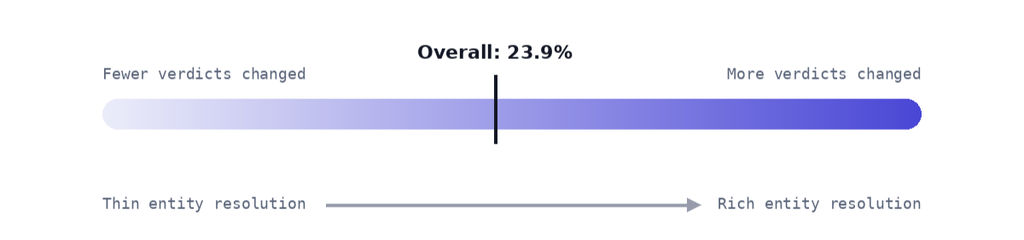
23.9% of verdicts changed. That’s where the risk lives. 23.9% of alerts changed verdict or severity once the agent had organizational context. Roughly one in every four.
FIG. 2   Share of sampled alerts whose verdict or severity changed with context. Square placement is illustrative.

That 23.9% is far greater than a rounding error. It’s the slice of the alert queue where the verdict was actually in play, and it’s where a SOC gets hurt. For every alert in it, the verdict, without context, was at risk of being misclassified, requiring human oversight. When that error runs in the dangerous direction, a real threat gets closed as benign or left at the bottom of the queue. That’s how attacks get missed.

The rate varied by environment. The spread tracked one thing: how many of the alert’s users and devices the graph could resolve to known entities. Environments where the graph could identify most of them saw the most changes in verdicts.

FIG. 3   The more of an alert’s users and devices the graph could resolve, the more verdicts moved.

Not Every Change Weighs the Same

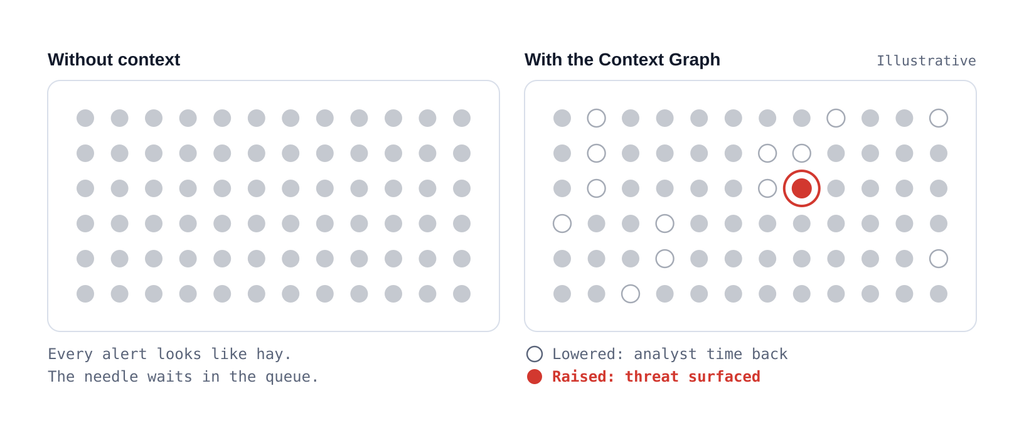
Context pushed verdicts in both directions. Of the alerts whose verdict flipped between close and escalate, 53% went up to escalate, and 47% went down to close. Those two moves carry very different costs.

↓ Context lowers a verdict
Closed, deduplicated, or deprioritized. The SOC stops spending analyst hours on alerts that don’t need them, and at enterprise volume, that adds up fast.

Cost of the old verdict: Wasted time
↑ Context raises a verdict
An alert that looked routine gets pulled out of the noise and put in front of a defender, fast.


Cost of the old verdict: A missed attack

Lowering a verdict (e.g., to benign) shrinks the alert haystack. Raising a verdict finds the needle. Both matter, but the second is the reason a SOC exists. Every escalation that context drives is a defender one step closer to a threat that could otherwise have slipped through.

FIG. 4 Illustrative. Lowered verdicts take hay off the pile. A raised verdict moves the needle to the top of the queue.

What Moved the Verdicts

Almost none of the deciding signals were a field in a single tool. Each was a join, a path, or a computed conclusion.

SIGNALVERDICTGRAPH LAYER
Activity fits the user’s role↓ LowerResolution
“Suspicious” IP is the user’s own managed workstation↓ LowerResolution
Entities already part of an open incident↓ DedupeRelationship
Dormant service account suddenly active↑ RaiseInsight
Server on a privileged admin path, MFA missing↑ RaiseRelationship + Insight
User or device the graph can’t attribute↑ RaiseResolution gap

Each context layer answers a question analysts already ask:

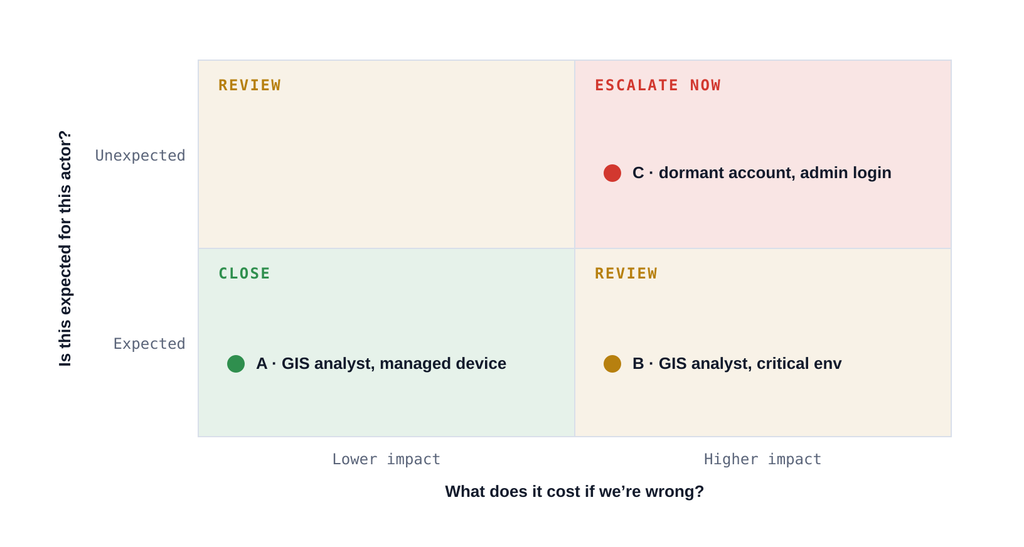
  • Is this expected for this actor? Resolution.
  • What does it cost if we’re wrong? Insights: privilege, VIP status, criticality, posture.
  • Is this already known? Relationships. Closing here means “don’t escalate twice,” not “harmless.”

The first two did most of the work together. Expected activity, low impact: Close. Unexpected activity, high impact: Escalate now. Everything in between: Review.

FIG. 5   How the two main questions combine. The dots are the three alerts in the next section.

One Alert, Three Verdicts

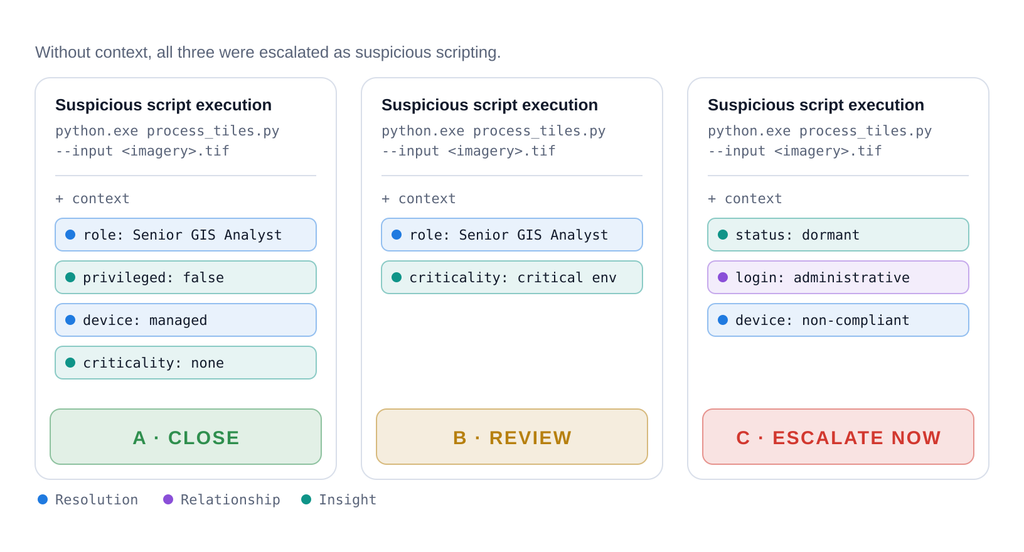
The clearest case was a recurring alert on Python scripts processing map imagery. Without context, these were escalated as suspicious scripting. With context, they split three ways.

FIG. 6   Identical process, arguments, and file types. Every fact that separates them comes from the graph.

A suppression rule or an allowlist would have closed all three, including the one that should ring the Batphone. Nothing in the alert distinguishes them. Everything that does is in the Context Graph.

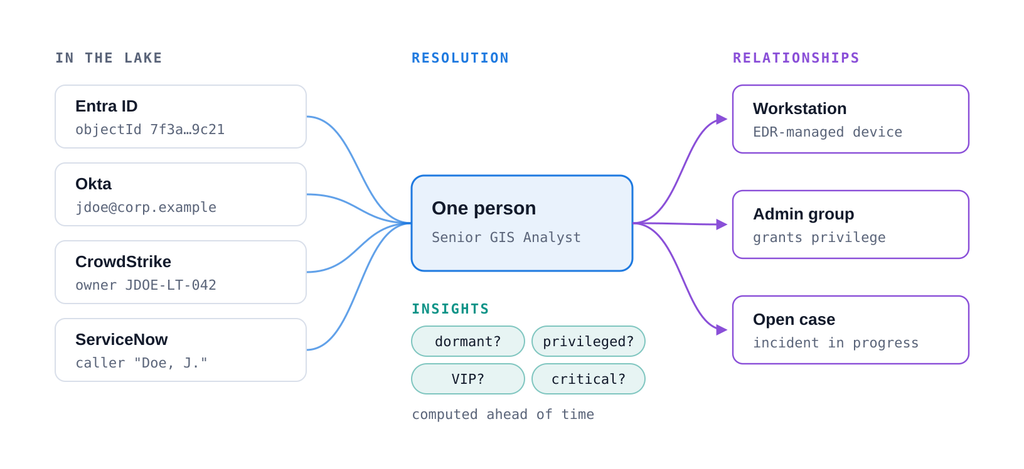
“Can’t I Just Point an Agent at My Data Lake?”

Your lake probably holds every source behind that table, but lacks what changes the verdict.

FIG. 7   Illustrative identifiers. The lake stores the records. The Context Graph knows who they belong to, what they connect to, and what that means.
  • Resolution. In a lake, one person is an Entra object ID, an Okta login, a CrowdStrike owner string, and a ServiceNow caller, with no reliable key between them. The agent would rebuild that match for every alert.
  • Relationships. “Tied to a privileged admin group” isn’t a row. It’s a path: host → service account → group → privilege. A lake stores the hops, not the path.
  • Insights. Dormant, privileged, VIP, and critical are conclusions, not fields. They must be computed in advance and kept current, not improvised within a triage prompt.
  • Rebuilding all of that per alert is also expensive and unstable. The agent spends tokens and time redoing the same joins on every alert, and two runs on the same alert can land on different answers. Whether two records belong to the same person, or whether a host sits on an admin path, should be a stored yes or no that the agent looks up.

Three Questions For Any Vendor, Including Torq

These are sampled, preliminary results. We measured whether and why verdicts changed, not yet whether every new verdict was right. Scoring both runs against analyst-confirmed outcomes is next, and we’ll publish it. I’m holding us to the same standard I’d ask of any vendor.

If a vendor tells you context matters, ask them:

  1. Which entities and relationships moved the verdict, and can I see them?
  2. Is the context resolved and computed ahead of time, or assembled from raw data per alert?
  3. What does the agent do when the data is missing?

If the answer is a claim without proof, keep asking.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

REV’d Up: Partner Stories

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

AI SOC Adoption: Where to Start in the First 90 Days

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to Virgin Atlantic, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.

You’ve signed the AI SOC contract. The question I get next is always the same: where do I start? What can I turn on without worrying about it, and what do I need to watch closely?

The instinct at the start of any AI SOC adoption is to boil the ocean, to point AI at everything at once and prove the whole thesis in a quarter. That’s how good rollouts stall. The faster path is narrower. Lead with agentic triage on the work that’s drowning your team, prove it, then expand as trust builds. Here’s how the first 90 days should go.

The First 90 Days of AI SOC Adoption

Start with why you bought the platform. What are you trying to deliver, and how will you know it’s working? Get your objectives on paper, look at the processes and the team you have, and start designing the plans, automations, and agent roles that will deliver them.

Deploy agentic triage on your highest-volume Tier 1 alerts. You’re putting the plan into practice, pulling people together on a project basis, and working out whether it’s performing. Some of them will start moving into roles that aren’t in their current job description yet, designing the new structure as they go.

The basics are working, and you see real movement from human process to machine speed. Lead with agentic triage to shut the door on machine-speed threats before the noise ever crosses into your SOC, because that noise is what overruns the team first. In parallel, pick a handful of your most time-consuming use cases and automate them. That combination gives you the fastest return. This is also your first review period. You’ll have a board meeting inside these 90 days, and the C-suite, board, and audit committee will want to know what you spent, what you’re getting out of it, what the risks are, and whether there have been mistakes. Positive answers get you the green light to expand.

Start AI SOC Adoption With Triage

The best starting point for an AI SOC deployment is your highest-volume Tier 1 work: triage. It has clear processes, a clear track record of how alerts have been handled, and it’s the single biggest time sink in the SOC. Manually clearing noise is exactly the kind of high-volume, repeatable work agentic AI is built for, so agentic triage is the right first move rather than something you save for later.

There’s a compounding effect here that’s easy to miss. Automating your biggest time sink frees up hours your team can put into the next layer. You spend time now to get far more of it back later.

While triage is coming online, pick a few use cases that eat the most analyst time and automate them too. Whether each one is agentic or deterministic depends on the process. This is the quickest path to visible ROI, and it gives you something concrete to show the board alongside the triage numbers. From there, you pick off the next candidates one at a time.

When you measure it for that board conversation, be careful how you frame it. Adding agents rarely means cutting analysts, so this isn’t a story about money saved. It’s an incremental return: for the extra you invest, how much more do you get back in threats handled, time to contain, and work closed within SLA? The capacity you free up gets redeployed into higher-value work, and that redeployment is its own line of value.

Build Trust Process by Process

You don’t earn autonomy in one move. You earn it one process at a time. When outcomes match expectations and nothing goes sideways, trust builds. You’ve shown your C-suite it works, so you can sell the next phase with evidence instead of enthusiasm. Continual results earn continual buy-in.

This is also where the org starts to change, and it’s worth planning for deliberately. The analysts who set up autonomous triage are the ones who understand it best, and they move into Tier 2, engineering, and assurance roles as the layer matures. I wrote about that shift in detail in the AI SOC org chart, so I won’t repeat it here, but keep it in view: the platform handles the work, and you redesign the team around what that frees up.

The Mistake That Stalls AI SOC Adoption

The common failure I see with AI SOC adoption is handing everything to AI agents at once, without a risk-based approach. Shore up the front door first, then expand deliberately. Try to do it all in one go, and you run out of resources, and you start confusing what’s running agentically versus manually, doing part of a process one way and part another.

Shore up the front door means exactly what it says. Machine-speed attacks are already here, and human-speed response is the lag attackers exploit. Get your highest-volume triage running at machine speed, prove it, measure it in terms your board and your auditors care about, and grow from there. That’s how you turn a tool into an operating model and bring the organization with you.

The full guide lays out the 90-day plan, the measurement dashboards, and the questions to ask a vendor about how they’ve done this with other teams.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

REV’d Up: GuidePoint Security on the Modern SOC

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

REV’d Up is our series on the partners we team up with to help customers modernize their security operations — the resellers, distributors, GSIs, and MSSPs in Torq REV (Revenue Enablement Velocity), our channel partner program. Each post shares a partner’s perspective: who they are, the customer problems they focus on, and how we work together to solve them.

First up: GuidePoint Security.

It’s a fitting place to start. Security teams are stretched thin, facing rising alert volumes and threats that move faster than manual processes can handle. Helping customers navigate that and reach the outcomes they need is exactly the kind of work GuidePoint focuses on.

Meet GuidePoint Security

GuidePoint Security works with organizations of every size, from a few hundred employees up through Fortune 100 companies. Its approach is deliberately vendor-objective: the firm evaluates a wide range of security technologies so it can recommend what best fits a customer’s environment and goals. That work is backed by a team of certified engineers, architects, and consultants.

GuidePoint and Torq bring complementary strengths to the table. GuidePoint provides advisory and services expertise to help customers assess, deploy, and operationalize security technology, and the Torq AI SOC Platform gives them agentic AI and automation across the threat lifecycle, from triage through investigation and response, with analysts in the loop for decisions that require human judgment. Working together, the focus is the same: helping customers reach the security outcomes they’re after.

That partnership mindset is what Mateo Gutierrez, Senior Account Executive at Guidepoint, keeps coming back to. “It’s not just here you go, see you later,” Gutierrez said. “It’s much more of a true partnership with our customers: step by step, how is this going to impact your roadmap over the next three to five years, and how do we help you get there?”

Gutierrez is candid that customers face a lot of complexity, and they lean on GuidePoint for the expertise to work through it.

Focused on Customer Outcomes

Many security teams are fielding more alerts than they can clear and running more tools than they have the headcount to operate. Working together, GuidePoint and Torq help customers operationalize their existing resources so their teams can respond faster and focus on the work that matters most.

“Security teams have been underwater for a long time,” Gutierrez said. “When you can accelerate and automate the threat detection, investigation, and response lifecycle, organizations reach the outcomes they’re after without exhausting their resources.”

For GuidePoint, much of the value is in helping customers get more out of what they’ve already invested in. “So much of our job is helping customers operationalize what they’ve already bought,” Gutierrez said, “and get mean time to respond and mean time to resolve down from days to, hopefully, minutes.”

That time-to-outcome is what customers care about most. “What customers really care about is the ROI from a time perspective,” Gutierrez said. “How much investigation and containment can happen before a human even has to step in?”

As an example of what that can look like, a Torq live demo resolved an incident that would normally take two to three days start to finish in 15 minutes or less, with several integrations handling containment automatically.

Support That Continues After Go-Live

GuidePoint doesn’t hand customers a platform and walk away. They back the partnership with a technical bench that keeps tuning the deployment after go-live. “We have people who can support it from a services standpoint and continuously fine-tune it to reach those outcomes,” Gutierrez said. Because GuidePoint often helped the customer select the tools involved, it’s well positioned to bring everything together for them. “It’s lockstep,” he said.

Customers are modernizing their security operations, whether their partner leads that conversation or not, and GuidePoint is choosing to lead it. “I only see this partnership [with Torq] growing,” Gutierrez added. “It comes up in more and more of our customer conversations.”

Interested in partnering with Torq to solve customer challenges?

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO