Cloud Managed Services: What They Are and How an AI SOC Takes Them Further

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • Cloud managed services shift day-to-day cloud operations to specialized providers, freeing internal teams to focus on strategic security work.
  • Key benefits include cost efficiency, scalability, resilience, and stronger compliance posture across multi-cloud and hybrid environments.
  • Managed environments still create security challenges: misconfiguration at scale, access sprawl, and fragmented visibility. Providers surface findings, but someone still has to triage, investigate, and respond.
  • The Torq AI SOC Platform closes that gap. Agentic AI acts across triage, investigation, and response, so managed cloud findings become closed cases instead of growing queues.
  • Enterprises that pair cloud managed services with an agentic SOC move from reactive cloud management to continuously optimized, autonomous operations.

Enterprise cloud environments have moved well past the point where manual management scales. Multi-cloud footprints span dozens of services, hybrid architectures blend on-premises and cloud workloads, and attackers now use AI to move faster and at greater scale. Cloud managed services address the operational side of that complexity by putting specialized providers in charge of the infrastructure layer.

But a managed provider detecting a problem is not the same as a security team resolving it. Alerts still pile up, tools stay disconnected, and the work doesn’t end once a threat is triaged. The agentic SOC has to manage the entire threat lifecycle, from triage through response. Paired with an AI SOC, cloud managed services stop generating work for your analysts and start generating closed cases.

What Are Cloud Managed Services?

Cloud managed services put a third-party provider in charge of some or all of an organization’s cloud infrastructure, applications, and operations. That typically includes migration, configuration management, security monitoring, performance optimization, backup and recovery, and maintenance, so internal teams can stop running the environment day to day.

The difference between managed and unmanaged comes down to responsibility. With an unmanaged cloud, your team handles configuration, security, patching, and monitoring. With managed services, a provider owns those functions under a service agreement, bringing specialized expertise and around-the-clock coverage.

For multi-cloud and hybrid enterprises, managed services bring operational consistency. AWS, Azure, and GCP each have their own interfaces, security models, and compliance tooling. A provider that spans all three delivers standardized processes, centralized visibility, and unified reporting that individual cloud portals rarely match.

A managed services provider doesn’t close your security cases, though. It generates telemetry, alerts, and findings. The Torq AI SOC Platform picks up from there, ingesting and normalizing signals across your cloud and security stack and acting across the full threat lifecycle, autonomously.

Key Benefits of Cloud Managed Services for Enterprises

Cloud managed services deliver value across four dimensions that matter directly to CISOs and security architects managing complex cloud ecosystems.

Cost Efficiency and Predictable Spending

Managed cloud services convert unpredictable infrastructure costs into predictable service fees. Organizations gain enterprise-grade tooling, 24/7 operational coverage, and specialized expertise through the service agreement, investing in outcomes instead of the infrastructure to produce them. For security teams, that efficiency extends to coverage: monitoring that would take multiple full-time analysts to replicate internally becomes a line item in a service agreement.

Scalability and Operational Efficiency

Cloud environments need to scale with business demand, and managed services providers build that elasticity into their service models. The security operation has to scale with them. An AI SOC expands SOC capacity without expanding headcount at the same rate: specialized AI Agents take on triage, evidence gathering, and routine response, so coverage stays proportional as the cloud footprint grows.

Resilience and Business Continuity

Managed service providers build redundancy, failover, and disaster recovery into their service delivery. For security teams, that resilience means faster recovery, better-documented incident response procedures, and continuous monitoring that catches issues before they become outages. Agentic response actions on top of managed services compress the detection-to-containment timeline even further.

Continuous Compliance Coverage

Compliance in multi-cloud environments is an ongoing operational discipline. Managed service providers maintain compliance frameworks across cloud platforms, but the evidence collection, control validation, and reporting that auditors require demands consistent execution. A platform that records every action, evidence item, and case summary in one place keeps compliance posture current between audit cycles instead of scrambling at the end of them.

Security Challenges in Managed Cloud Environments

Managed cloud environments introduce security complexity alongside their operational benefits. Security teams already operate under constant alert overload, and disconnected tools delay investigation and response. These are the three most common challenges in managed cloud environments, and how an AI SOC addresses each.

Misconfiguration at Scale

Cloud misconfiguration is one of the most common causes of cloud security incidents, and managed environments amplify it. As providers provision and modify resources across multiple platforms, each change creates potential exposure. A misconfigured storage bucket, an overly permissive IAM role, or an open security group can persist for weeks when manual review cycles lag behind deployment velocity.

When a cloud security posture management tool or the provider’s own monitoring flags a deviation from your baseline, Torq ingests the finding, analyzes risk context and threat intel, and delivers a verdict that separates false positives from actual risk. Confirmed misconfigurations move straight to agentic remediation instead of waiting in a queue.

Access Sprawl and Identity Risk

Managed cloud environments involve multiple providers, teams, and service accounts, each accumulating permissions over time. Teams provision roles for specific projects and leave them in place indefinitely, so over-permissioned accounts build up and least-privilege enforcement demands continuous attention.

Torq integrates with IAM platforms and cloud identity tools to surface entitlement risks, open cases for unauthorized or anomalous access, and trigger access reviews and remediation. AI Agents gather the evidence and assemble the timeline, so analysts review a finished investigation instead of starting one.

Limited Visibility Across Services

Each managed service generates its own logs, alerts, and reporting. Correlating those signals across providers, services, and security tools takes more than another dashboard.

Torq ingests and normalizes telemetry from across your security stack, correlating and deduplicating events to reduce noise. Socrates, the quarterback of the agentic SOC, coordinates specialized AI Agents and manages cases end to end. Security teams get one correlated view and one automated response path across their full managed cloud footprint, instead of fragmented signals from disconnected tools.

How the Torq AI SOC Platform Closes the Loop on Managed Cloud Security

The gap between what managed cloud services detect and what security teams can act on is where operational risk accumulates. The Torq AI SOC Platform closes it by managing the complete threat lifecycle, taking action and closing cases autonomously. 

Today, the platform remediates over 90% of cases completely autonomously.

Triage: Filter Out the Noise

Managed cloud environments generate heavy alert volume across configuration monitoring, access management, performance telemetry, and security tools. Torq’s Universal Auto Triage is the agentic AI engine that prioritizes threats and separates noise from actual risk. It ingests alerts from managed service providers, cloud security posture management tools, and connected security platforms, then correlates, deduplicates, and enriches each finding with asset criticality, risk context, and threat intel. Proprietary technology learns and remembers how your SOC works, so verdicts get sharper over time.

Investigate: Focus on the Biggest Risks

Once a finding is confirmed as real risk, Torq opens a case and assigns it to specialized, customizable AI Agents. Torq HyperAgents® gather evidence, assemble timelines, and summarize findings at your team’s direction, removing manual bottlenecks without giving up control. The balance between human and AI decision-making is a dial, not a switch: agents access only the data and tools you specify and perform only the tasks you authorize, with built-in RBAC and human-on-the-loop reviews. In an environment where third parties already touch your cloud, that least-privilege approach applies to your AI Agents too. Socrates coordinates those agents and manages the case end to end, and your team can direct it through natural language.

Case Management, native to the platform, keeps an always-updated single source of truth: evidence, timelines, and case summaries from investigation through remediation. Torq logs every action and makes it attributable.

Respond: Expedite Response Actions

When Torq confirms a threat in a managed environment, such as a compromised credential, a runtime anomaly in a managed container, or an active exfiltration attempt, agentic response actions contain it. Torq isolates affected resources, notifies the managed service provider and your internal team, opens a case with full incident context, and starts remediation. Detection-to-containment shrinks from hours to minutes, and critical threats still reach the right people.

Built on Hyperautomation and 300 Integrations

Underneath the agents, Torq Hyperautomation unifies and accelerates workflow automation at scale. With 300 pre-built integrations and 4,000+ pre-built steps spanning cloud providers, managed service platforms, SIEMs, IAM, and ticketing, the platform turns alerts into action across your whole stack. Teams can also use AI Agents to build new integrations, workflows, and custom use cases in minutes.

Auditable Decisions and Continuous Compliance Evidence

Torq HyperAgents aren’t black boxes. Torq logs every reasoning step, verdict, and action, and grounds each one in the Torq Context Graph, so your team can see what an agent did, why it did it, what was true about the environment at that moment, and what happened next. Evidence collection becomes a byproduct of the work. When an audit asks for proof of control validation or incident handling, the data is already there.

For MSSPs and MDRs building cloud security practices on top of managed services, Torq for MSSPs/MDRs delivers the efficiency and margin improvement that scales with customer growth.

Choosing the Right Managed Cloud Strategy and AI SOC Partner

Selecting a managed cloud provider and an AI SOC partner means evaluating criteria that directly affect long-term security and operational outcomes.

Integration Depth

A managed cloud provider’s value depends on how well it integrates with your existing security stack. Providers that integrate natively with your SIEM, EDR, IAM, and ticketing systems deliver the unified value that makes managed services a strategic asset. The same applies to your AI SOC platform: Torq’s 300 pre-built integrations and 4,000+ pre-built steps span cloud providers, managed service platforms, security tools, and business applications, giving agents the data they need to act across your full environment.

Autonomy and Transparency

The most important differentiator is what happens after a finding surfaces. A provider that logs incidents delivers value; an AI SOC that triages, investigates, and responds delivers outcomes. Ask how many cases the platform closes without human intervention, and ask what oversight you keep. Torq HyperAgents are autonomous, transparent, and customizable, working in a clear direction your team controls. Dozens of out-of-the-box agent templates cover typical security tasks, and the Agentic Builder in Socrates lets engineers describe an outcome in natural language, then plans, builds, and tests the agent using your actual tools, workflows, and runbooks. Nothing goes live until you approve it. Not every “AI SOC” solves the full problem, so look for a platform that manages the whole lifecycle, not just analysis.

Context and Learning

Evaluate whether the platform learns how your SOC works. Torq’s Context Graph and Memory let the platform remember your environment, decisions, and preferences, so accuracy and speed improve with use.

Scalability

Cloud environments grow, and managed service coverage and security operations need to grow with them. Evaluate both your managed cloud provider and your AI SOC platform on how they handle rising alert volumes, expanding cloud footprints, and new compliance requirements without a matching increase in manual effort or engineering overhead.

Cloud Managed Services Work Best When an AI SOC Closes the Case

Cloud managed services have grown from reactive IT outsourcing into a strategic layer of enterprise infrastructure. The organizations that get the most from them pair that layer with an agentic SOC that turns provider findings into triaged, investigated, and resolved cases, with transparency, oversight, and control.

The Torq AI SOC Platform delivers that capability. Auto Triage filters the noise, Torq HyperAgents investigate, Socrates coordinates, and agentic response contains and remediates, all backed by Hyperautomation and 300 integrations. In its May 2026 report, AI Vendor Race: Torq Is the Company to Beat in AI SOC Agents for Threat Investigation, Gartner names Torq the Company to Beat.

Not every AI SOC closes cases, and buying one is unlike any purchase most security leaders have made. You’re choosing an execution layer that will reshape your team and your operating model, not just another tool.

Torq’s AI SOC Buyer’s Guide gives you a framework for that decision. John White, Torq’s Field CISO EMEA, wrote it from the buyer’s seat, drawing on more than 20 years building and running security functions, including SecOps transformations at Virgin Atlantic, ASOS, and Liberty Global. It covers what you’re actually buying, the context, memory, and autonomy questions that separate real platforms from marketing, and how to roll out and prove value with a 90-day plan, true ROI, and a vendor checklist. Pair it with the criteria above to pressure-test any AI SOC partner.

Gartner, AI Vendor Race: Torq Is the Company to Beat in AI SOC Agents for Threat Investigation, Tom Powledge, Matt Milone, 25 May 2026. GARTNER is a trademark of Gartner, Inc.

FAQs

What are cloud managed services?

Cloud managed services involve a third-party provider taking on partial or complete management of an organization’s cloud infrastructure, applications, and operations. That scope typically includes configuration management, security monitoring, performance optimization, backup and recovery, and compliance maintenance. Organizations gain specialized expertise and around-the-clock operational coverage while freeing internal teams for higher-value security work. Learn how the Torq AI SOC Platform extends managed cloud services with autonomous triage, investigation, and response.

What is the difference between managed and unmanaged cloud services?

With unmanaged cloud services, the organization handles all configuration, security, patching, monitoring, and operational management. With managed cloud services, a provider takes ownership of those functions under a defined service agreement. Managed services deliver operational coverage, specialized expertise, and consistent processes across cloud environments, and the security value compounds when an AI SOC converts managed service findings into closed cases.

What are the main security challenges in managed cloud environments?

The three most common challenges are misconfiguration at scale, access sprawl and identity risk, and limited visibility across services. Each grows with cloud footprint size and the number of providers in the stack. An AI SOC addresses all three: Auto Triage separates real risk from noise as findings arrive, AI Agents investigate entitlement drift and misconfigurations, and cross-platform correlation gives security teams one view. See how Torq HyperAgents handle investigation and response with transparency and oversight.

How does Torq integrate with cloud managed services?

Torq connects with managed cloud service providers, cloud platforms (AWS, Azure, GCP), cloud security posture management tools, identity platforms, SIEMs, and ticketing systems through 300 pre-built integrations and 4,000+ pre-built steps. When a managed service provider surfaces a finding, Torq enriches it with context, prioritizes it against other active findings, assigns it to AI Agents for investigation, and executes agentic response actions. For MSSPs and MDRs building on managed cloud infrastructure, Torq delivers efficiency that scales as customer environments grow.

What should enterprises evaluate when choosing a managed cloud provider and AI SOC partner?

The key criteria are integration depth (how well the provider and platform connect with your existing stack), autonomy and transparency (how many cases are closed without human intervention, and what oversight you keep), and scalability (how well both grow with your cloud footprint). Enterprises that evaluate both together as one cloud security strategy build programs that scale more effectively. Explore the Torq AI SOC Buyer’s Guide for a deeper look at what to ask.
SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

How A Leading Museum Automated Its Security Operations with Torq

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

The organization at the center of this story is one of the most visited cultural institutions in the world, dedicated to preserving history and educating the public.

Protecting that mission — and the digital infrastructure behind it — falls to a lean security team responsible for everything: SSO integrations, email, endpoints, servers, applications, websites, and micro-segmentation across the entire organization.

It’s a wide surface for any security team to cover. It’s an even wider one when your institution’s global profile and cultural significance make you a target. Geopolitical tensions have driven an increase in cyberattacks against the institution, demanding a security posture well beyond what the team could deliver manually.

This is the story of how that team went from fully manual operations to automated threat blocking, identity lifecycle management, and endpoint response.

When Every Security Action Depends on a Human, Nothing Moves Fast Enough

Before the Torq AI SOC Platform, the security team’s day-to-day was what you’d expect from an operation running without automation: reviewing logs by hand, writing custom scripts, pulling reports, working through spreadsheets. Every step required someone to touch it.

That meant threat response moved at human speed. A device querying a malicious URL would get flagged, but by the time an analyst reviewed it, confirmed it, and took action, a week had passed. A week of known, unresolved exposure.

The team initially looked at Torq for security playbooks to automate detection and response workflows that consume analyst time. Two things made it the right fit: it was faster to build in than native tooling, and the whole team could use it without specialized coding skills. For a security operation where everyone covers everything, that accessibility was a requirement.

Migrating to Okta: The Problem Torq Solved in Hours

The museum undertook a major overhaul of its identity infrastructure, migrating from Active Directory–sourced accounts to Okta as the primary identity provider. It’s the kind of migration that touches every user, every application, and every access workflow in the organization.

The problems surfaced almost immediately. When users didn’t respond to Okta’s verification prompts within the predefined time window, their accounts were automatically flagged, and email access was locked. For a museum with staff across departments — curators, educators, researchers, operations — lockouts stalled work, frustrated employees, and generated a cascading queue of support requests.

The obvious fix was to build an automated workflow in Okta itself. But Okta Workflows is its own ecosystem, time-intensive to implement, and creates a knowledge gap for the team. Torq offered a faster path. Through a straightforward API call, the team built a workflow that automatically detects locked-out users and clears the flags, allowing accounts to be onboarded without manual intervention.

That migration fix opened a bigger door. The team discovered that Torq could do things with Okta data that the native dashboard couldn’t. They started pulling error logs through Torq and running analysis to surface root causes, not just the symptoms the dashboard displayed. What started as a migration fix became an ongoing operational layer on top of their identity infrastructure, giving the team better visibility into their identity environment than the identity provider itself.

Security Automation That Grew into Something Bigger

The team started with security automation and quickly found that Torq’s platform could absorb manual work across security and IT operations alike. What began as a handful of security playbooks has grown into a library of automated workflows spanning threat response, identity management, endpoint security, and infrastructure monitoring.

Automated Threat Blocking

The team’s very first workflow is still one of the most impactful. The museum’s network monitoring tool continuously watches for suspicious outbound connections. When a device is flagged for querying a potentially malicious URL, Torq automatically sends the indicator to VirusTotal for cross-referencing against dozens of antivirus engines. More than four positive hits? Blocked immediately, without a human in the middle.

Before Torq, an analyst had to review the flag, look up the URL, make a judgment call, and take action. Now it runs in seconds.

Endpoint Enrichment and Response

When SentinelOne detects a suspicious event on an endpoint, the alert triggers a Torq micro-playbook that automatically enriches the event. Torq pulls the relevant indicators — hashes, IPs, domains — and queries them against VirusTotal and other threat intelligence sources. Based on the results, the playbook either documents the event as benign or executes a blocking action, without requiring an analyst to manually copy indicators between tools.

Baseline Scanning and Configuration Monitoring

Tools get deployed with specific security baselines: hardened configurations, required settings, expected states. Over time, those baselines drift. A setting gets changed during troubleshooting and is never reverted. An update overwrites a configuration. A new deployment doesn’t match the standard.

The team uses Torq to scan their tool stack and flag discrepancies against defined baselines. Instead of manually auditing on a schedule — or discovering drift after an incident — Torq surfaces gaps proactively.

Automatic Reboot for Critical Updates 

Patching is one of the most basic security hygiene practices and one of the easiest to let slip. A critical update lands, but the reboot requires coordination: confirm the asset is clear, schedule a window, and follow up. For a lean team, that coordination competes with every other task on the list.

The team built a Torq workflow that monitors for assets with pending critical updates and triggers an automatic nightly reboot. Patches are applied on schedule, every time, without manual follow-up.

Stale Asset and Duplicate Cleanup 

Every tech stack accumulates clutter. Devices get decommissioned but never removed. Endpoints are reimaged, creating duplicates. Orphaned records pile up. Each one is a blind spot — an asset that shows as managed when it isn’t, or a duplicate that skews reporting and wastes license seats.

Torq continuously scans the team’s tech stack, identifies stale or duplicate assets, and cleans them up. What used to be a periodic manual audit is now a continuous hygiene function.

Automatic Re-Enablement of Disabled Agents 

A disabled security agent is an unmonitored endpoint. The disable might be intentional (for troubleshooting), accidental (due to a bad update), or the first sign of compromise. The longer it stays disabled, the bigger the gap.

Torq monitors disabled agents and automatically re-enables them. The team is notified immediately — if the disable was legitimate, they know. If it wasn’t, the gap would be closed before it could be exploited.

The Impact

  • Threat response moved from days to seconds. Malicious activity that used to sit in a queue waiting for human action is now caught and blocked the moment it’s confirmed.
  • Routine bottlenecks disappeared. Okta onboarding issues that required tickets, callbacks, and meetings are resolved automatically. Endpoint events that waited for manual enrichment are handled in the background. The team focuses on work that requires human judgment, not work that was waiting for someone to get to it.
  • Security hygiene runs continuously. Critical updates are applied overnight. Stale assets are cleaned up. Disabled agents are re-enabled. The team doesn’t have to remember to do these things; they just happen.
  • The platform expanded beyond security. The team came to Torq for SOC automation. The fact that it’s now embedded across multiple operations says something about how much manual work was hiding in plain sight across the organization.

“Using Torq, we have the ability to retrieve data from multiple applications and mirror human action in an automated way. That saves time, and where we really need to save time is on the action side. Instead of waiting a week to block a bad IP address, Torq lets us do it almost instantaneously. It’s a major risk reduction.”

– Michael Trofi, CISO

Defending History Requires Modern Defense

The museum exists to preserve history and make sure the world never forgets. That mission draws millions of visitors, powers a global digital presence, and makes the institution a target.

The security team didn’t automate because it checked a box. They automated because the mission was too important to protect at human speed. The automation this team built is the foundation the AI SOC is built on: the shift from human-speed operations to machine-speed defense. The threats keep evolving, and so does the team.

This major museum’s team is proof of what the data shows: lean SOCs that deploy the right automation get ahead. See how 450 security leaders are thinking about AI, automation, and the future of security operations.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Black Hat 2026: AI SOC with a Brain, Tattoos, and Hot Dogs

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

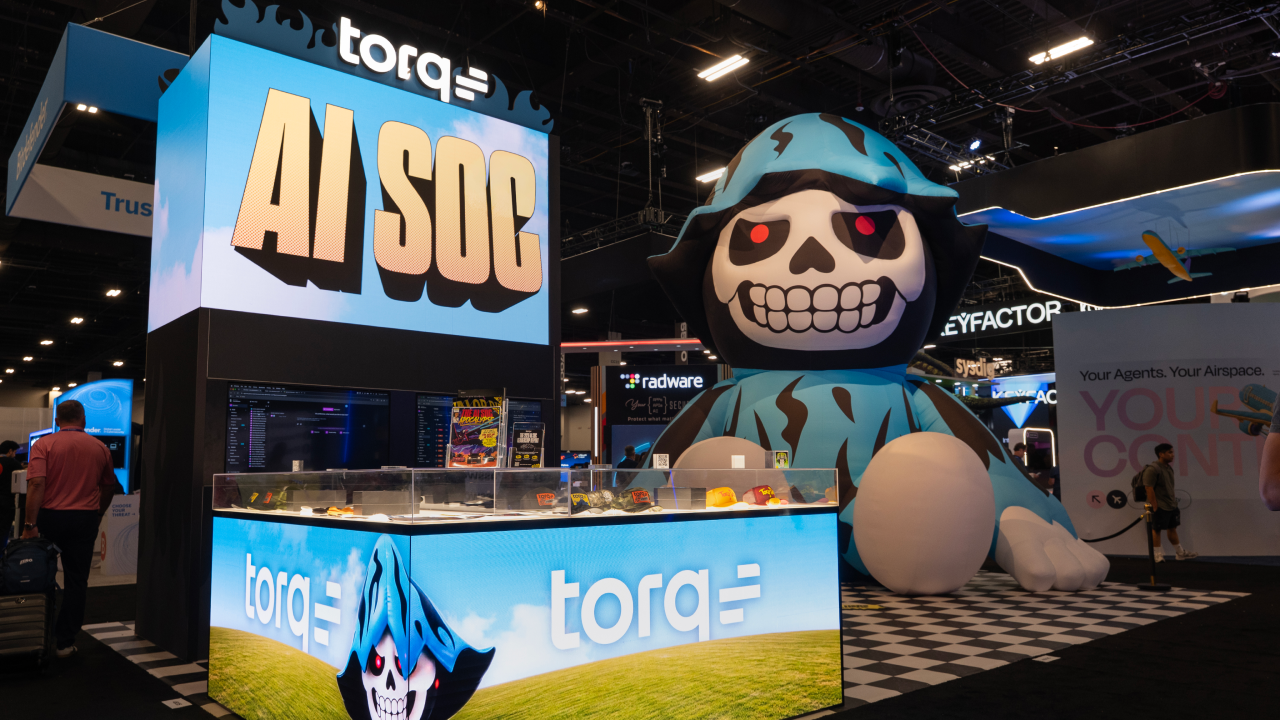
Torq rolled into Black Hat 2026 with a 20-foot inflatable skeleton, free tattoos, hot dogs, the Wizard of Oz, and a live news desk. That’s a lot of conversation starters right there. 

But the real talking point was Torq’s AI SOC demo: in-production AI SOC capabilities that reason with organizational context, learn from analyst decisions, get smarter with every case the platform handles, and take action across the full threat lifecycle.

Here’s what really happened in Vegas.

Pre-Show Buzz: Torq SOC Brain™ and a SACR AI SOC Innovator

Days before Black Hat, Torq unveiled Torq SOC Brain™, the self-learning layer of the Torq AI SOC Platform. The SOC Brain brings together Recall, Reflex, and Retrospect to help Torq reason from past cases, learn from analyst decisions, and apply that judgment to future triage and investigations.

The launch drew coverage from SiliconANGLE, Channel Insider, MSSP Alert, and more.

“The end goal is to shift as much as possible of a cognitive load required to investigate incoming security alerts.”

Leonid Belkind, Torq CTO and Co-Founder in Channel Insider

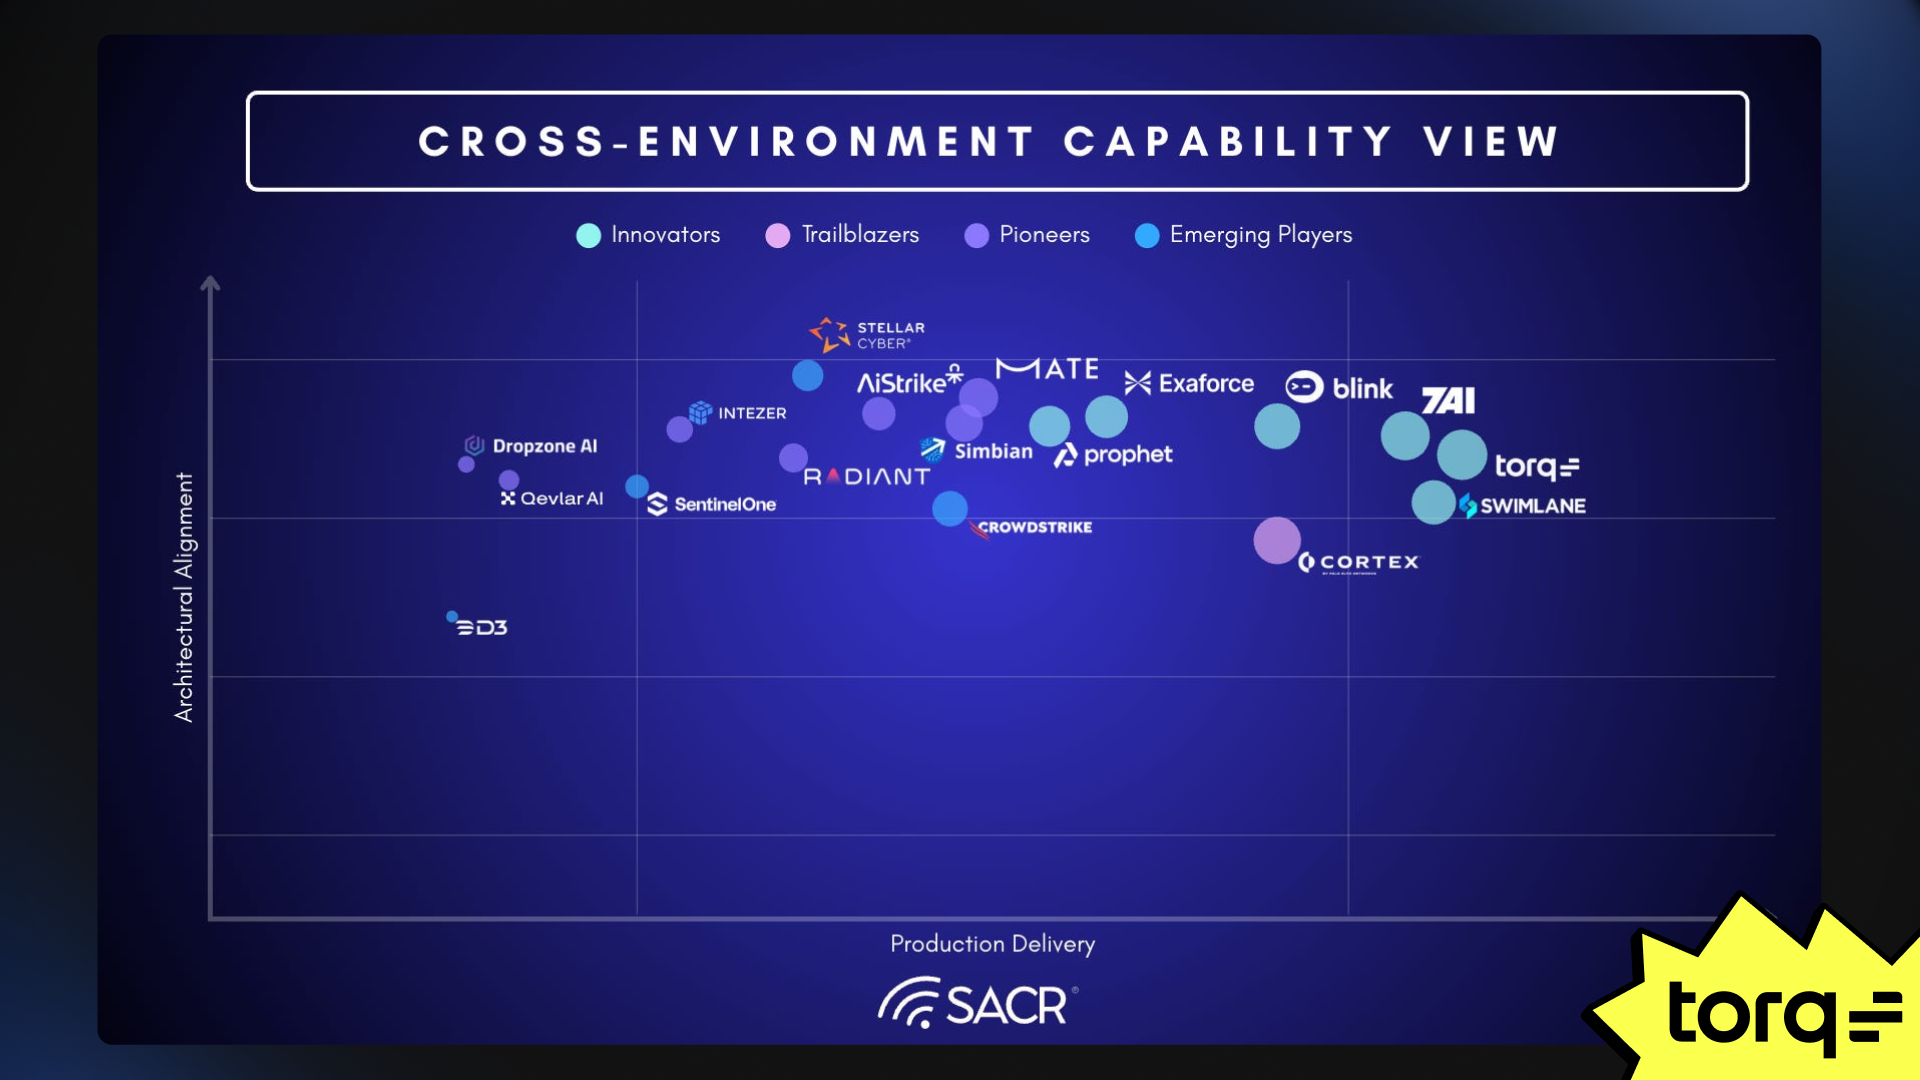
Torq also entered Black Hat with fresh analyst recognition: Software Analyst Cyber Research named Torq a leading Innovator in its AI SOC Market Report, as an “as an AI SOC operating layer that can ingest alerts, classify triage outcomes, construct cases, assign work to Socrates, and route remediation through deterministic or agentic workflows depending on the use case.”

Then we took it to Vegas.

The AI SOC Demo

Torq’s demo stations stayed busy as attendees saw hands-on how Torq moves from alerts through investigation and response with context and agentic reasoning built in. Here’s what landed most:

  • Torq Context Graph drew a strong reaction. It’s a live model of your environment (identities, assets, policies, and the reasoning behind past decisions) so every verdict is grounded in the full picture, not a single alert in isolation. The blast-radius and pivot-point views hit hardest, showing how far one compromised identity could reach and why organizational context changes what an alert actually means.
  • Torq Auto Triage classifies every alert as false positive, benign, or malicious with explainable reasoning, turning real threats into cases automatically and cutting noise before an analyst engages. The most common question was what it weighs to reach a call, and showing that reasoning is the difference between a black box and a platform a SOC will trust to act.
  • Recall and Reflex were where the conversation moved past triage. Recall brings your own case history to every new alert, and Reflex learns your team’s judgment, so the platform gets more accurate the longer it runs instead of resetting to zero each shift.
  • Torq Socrates lets teams prompt workflows. Describe the outcome you want in plain language, and Socrates plans, builds, and orchestrates the automation across your stack, deciding what runs agentically versus deterministically and coordinating the right HyperAgents to carry it out.

On Stage: Context, Memory, and Learning in the AI SOC

John White, Field CISO EMEA, and Rick Bosworth, Sr. Director of Product Marketing, took the stage to go a level deeper on why those capabilities matter. Together, the Context Graph, Recall, and Reflex form the Torq SOC Brain, the layer beneath the agents that lets the platform reason about your environment, remember your decisions, and learn your team’s judgment.

John and Rick kept coming back to two points:

  1. First, autonomy is a dial you widen as trust builds, not an all-or-nothing switch.
  2. Second, every customer’s SOC Brain stays isolated, so what one team’s platform learns is never shared with another.

They also shared advice on how best to get started with an AI SOC platform: Pick the repeatable Tier 1 work that eats the most analyst time, prove it out, then expand. On timing, they were blunt. Waiting is its own risk when attacks already move at machine speed.

TTVN, Live from Las Vegas

Our Junior Media Intern Trevor has traded in his TorqTV van for a news desk.

Trevor and Tony went live from the TTVN desk with boots-on-the-ground Black Hat coverage of the week’s biggest stories: Skelly, Torq Dogs, real (yes, real, actual, permanent) tattoos and piercings, Channimals in the Wild, AMP’d partner highlights, and an exclusive Wizard of Oz screening at the Sphere, co-hosted by Snyk.

Didn’t Catch Us in Vegas?

The hot dogs were tasty. The tattoos were permanent. But the bigger story was what Torq showed in the booth and on stage: an AI SOC platform that reasons on your environment, remembers your decisions, and learns your team’s judgment across the full threat lifecycle.

Missed the Torq demo at Black Hat, or want a closer look without the show-floor crowd? Watch our live Auto Triage demo webinar.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

What Is Cyber Risk Management? The Continuous Process of Managing Digital Risk

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • Cyber risk management (CRM) is the continuous process of identifying, assessing, mitigating, and monitoring threats to an organization’s digital assets and information systems.
  • The CRM cycle runs through four pillars: risk identification and asset inventory, risk assessment and quantification, risk mitigation and strategy, and continuous monitoring.
  • Frameworks like NIST CSF, ISO 27001/27005, and FAIR give organizations a structured, repeatable methodology for managing risk at scale.
  • Modern best practices combine zero-trust architecture, vulnerability management, third-party risk controls, formalized incident response, and security culture.
  • The Torq AI SOC Platform automates the detection, triage, and response workflows that turn a CRM framework into a continuous operational reality.

Cyber risk demands continuous attention. New assets come online, new vulnerabilities surface, and threat actors refine their techniques every day. The organizations that manage cyber risk most effectively treat it as an ongoing business discipline built on a structured, repeatable cycle of mapping, measuring, and mitigating threats proactively.

This guide covers what cyber risk management is, the four-stage process that drives it, the frameworks that give it structure, and the best practices that make it effective. It also covers how an AI SOC platform closes the execution gap between identifying a risk and reducing it.

The Four Pillars of the Cyber Risk Management Process

Effective CRM runs through four continuous stages. Each stage feeds the next, and the cycle repeats as the organization’s asset inventory and the broader threat landscape both evolve.

1. Risk Identification and Asset Inventory

Every CRM program starts with a complete picture of what the organization is protecting. Security teams identify and document all IT assets: hardware, software, data, networks, cloud resources, and third-party integrations. A complete, current asset inventory is the foundation every other stage of the program depends on.

Prioritization follows the inventory. Organizations classify assets based on business value, legal standing, and operational criticality to identify High-Value Assets (HVAs): the systems and data that would cause the greatest damage if compromised. An unpatched development server carries different risk than an unpatched system processing customer payment data.

Threat modeling rounds out the identification stage. Security teams proactively map attack vectors and identify the specific threats (phishing, ransomware, insider threats, supply chain compromise) and vulnerabilities (misconfigured firewalls, unpatched software, over-permissioned accounts) that could affect each asset. That work turns a static asset list into a dynamic risk map. Explore 12 types of cybersecurity attacks and how AI-driven security operations address each one.

2. Risk Assessment and Quantification

With risks identified, the next stage measures them. Risk assessment analyzes two dimensions for each identified threat: the likelihood it occurs and the potential impact if it does. Combining those dimensions produces a risk score that directs mitigation resources toward the highest-priority exposures.

Modern practice pushes beyond qualitative High/Medium/Low scoring into cyber risk quantification (CRQ): expressing risk in financial terms. When a risk carries a dollar value (expected annual loss, breach scenario cost, regulatory fine exposure), security leaders make investment decisions with the same rigor they apply to other business expenditures. CRQ also makes the ROI of security controls visible. A $200,000 control that reduces a $2 million expected annual loss is a straightforward business case.

Risk assessment findings feed directly into prioritization. The highest-likelihood, highest-impact risks against HVAs get addressed first. Lower-likelihood risks against lower-value assets move into the monitoring queue.

3. Risk Mitigation and Strategy

The mitigation stage translates risk assessment findings into action. For each identified risk, security leaders choose a response strategy based on the organization’s risk tolerance:

  • Avoid the risk by eliminating the activity or asset that creates it
  • Transfer the risk through cyber insurance or contractual liability shifts to third parties
  • Mitigate the risk by implementing technical, administrative, or physical controls that reduce likelihood or impact
  • Accept residual risk when the cost of mitigation exceeds the expected impact and senior stakeholders formally acknowledge the exposure

Control implementation is where mitigation becomes operational. Firewalls, encryption, multi-factor authentication, access controls, and security monitoring tools all reduce the likelihood or impact of specific threat categories. Cybersecurity best practices covers the control categories that deliver the broadest risk reduction across typical enterprise environments.

Document every decision at this stage. Record each risk, the response strategy the team chose, and the owner accountable for execution. All of it belongs in the risk register.

4. Monitoring, Review, and Improvement

Risk management continues well past control implementation. The threat landscape changes, new assets come online, and controls drift from their intended configuration over time. Continuous monitoring catches those changes before they become incidents.

Ongoing surveillance of the IT ecosystem and the broader threat landscape feeds back into the identification and assessment stages. New vulnerability disclosures, emerging attack techniques, and changes in the regulatory environment all trigger updates to the risk map. The cycle keeps turning.

The risk register is the operational hub of this stage: a live document tracking all identified risks, their current status, assigned owners, and planned or completed mitigation actions. Keeping it current requires discipline and pays off every time leadership asks for a risk posture update or an auditor requests evidence of due diligence.

Residual risk acceptance is a formal, documented step. After controls are implemented, some risk always remains. Senior stakeholders review and formally accept that residual risk, creating documented accountability for the organization’s risk posture. The cybersecurity lifecycle framework maps how this continuous cycle connects detection, response, and recovery into a unified operational model.

Essential Frameworks for Standardizing CRM

Frameworks give CRM programs a structured, recognized methodology, and they matter for compliance. Regulators and auditors frequently ask which framework an organization follows and whether it demonstrates consistent adherence.

NIST Cybersecurity Framework (CSF) and Risk Management Framework (RMF)

The National Institute of Standards and Technology produces two widely adopted frameworks. The NIST CSF organizes cybersecurity activities into five functions: Identify, Protect, Detect, Respond, and Recover. It gives organizations a common language for discussing and improving security posture and applies across industries and organization sizes.

The NIST RMF provides a seven-step process for integrating security and risk management into system development and procurement lifecycles. Federal agencies use it as a compliance requirement; many private-sector organizations adopt it for its rigor and structured approach. The cybersecurity frameworks guide covers how NIST and other frameworks apply to enterprise risk programs.

ISO/IEC 27001 and ISO 27005

ISO 27001 defines the requirements for an Information Security Management System (ISMS): the policies, procedures, and controls an organization puts in place to manage information security risk systematically. ISO 27005 provides the risk assessment and treatment methodology that feeds the ISMS.

Together, they give organizations an internationally recognized, auditable framework for demonstrating that a structured risk management program exists and operates as documented. ISO 27001 certification carries weight with enterprise customers, partners, and regulators across global markets.

FAIR (Factor Analysis of Information Risk)

FAIR is a quantitative risk framework designed to translate cyber risk into financial terms. Where NIST and ISO provide process structure, FAIR provides the analytical methodology for CRQ: how to model threat frequency, vulnerability probability, and loss magnitude to produce a defensible financial risk estimate.

Organizations that adopt FAIR can answer the question boards and CFOs ask most: how much risk does the organization carry, and what does a breach cost? That financial clarity drives better investment decisions and clearer communication with non-technical stakeholders.

Modern Best Practices for Effective Cyber Risk Mitigation

Adopt a Zero-Trust Model

Zero-trust security removes implicit trust from the network architecture. Every user, device, and application gets verified before accessing resources, and access gets scoped to the minimum required for each specific task. This approach limits lateral movement after a breach and reduces the blast radius when credentials are compromised.

Zero-trust applies particularly well in hybrid and multi-cloud environments where identity has become the true security perimeter and continuous verification is the enforcement mechanism.

Prioritize Vulnerability Management

Unpatched vulnerabilities remain one of the most consistent entry points for attackers. A mature vulnerability management program runs continuous scanning across internet-facing systems and internal assets, prioritizes findings by exploitability and asset criticality, and closes patch windows before attackers can exploit newly disclosed vulnerabilities.

Speed matters here. Automated vulnerability management workflows triage findings and route critical patches to the right teams, closing that window faster than manual processes. See how vulnerability management tools and automated triage workflows work together in practice.

Manage Third-Party Risk

Supply chain attacks have demonstrated that an organization’s security posture extends to every vendor, partner, and integration that touches its environment. Managing third-party risk means evaluating vendor security controls at onboarding and monitoring them on an ongoing basis.

Automated workflows that track vendor security questionnaire status, monitor for vendor breach disclosures, and flag integration anomalies give security teams continuous third-party visibility at scale.

Formalize Incident Response and Disaster Recovery

A well-defined, regularly tested incident response plan (IRP) and disaster recovery plan (DRP) determine how much damage a breach causes. Organizations that exercise their response plans regularly contain incidents faster and restore operations more completely.

The incident response plan framework covers the components of an effective IRP and how to structure tabletop exercises that surface gaps before attackers do. Incident response automation covers how automated workflows cut response time from detection to containment.

Cultivate a Risk-Aware Culture

Technical controls address the infrastructure layer of cyber risk. The human layer requires a different approach: regular security training that helps employees recognize phishing, social engineering, and insider threat scenarios, combined with security responsibilities distributed across business units.

Security awareness programs work best when they go beyond annual checkbox training to include simulated phishing campaigns, role-specific training for employees who handle sensitive data, and clear escalation paths when employees encounter something suspicious.

Accelerating Cyber Risk Mitigation

Frameworks and best practices define what cyber risk management requires. Execution speed determines how well it works in practice. The gap between identifying a risk and closing it creates the window attackers exploit, and narrowing that gap is exactly where Torq’s AI SOC Platform delivers.

Torq Hyperautomation™ connects the security tools, identity systems, cloud environments, and endpoint platforms that CRM programs depend on into unified, automated workflows. When a vulnerability scan surfaces a critical finding, Torq automatically enriches it with asset criticality and exploitability context, routes it to the appropriate team, and triggers the remediation workflow, all before the alert reaches a manual review queue.

Torq HyperAgents® bring autonomous action to the risk mitigation stage. HyperAgents are built to execute multi-step response workflows the moment a risk indicator is confirmed, collapsing the detection-to-remediation cycle from hours to minutes. When a misconfigured cloud resource creates exposure, HyperAgents detect the deviation and trigger a remediation workflow immediately.

Torq Socrates™, Torq’s agentic SOC orchestrator, adds intelligent reasoning to risk triage. Socrates evaluates incoming security signals in context, determines which warrant immediate escalation and which route to the remediation queue, and executes or delegates based on the specific risk profile of each finding. Security teams get autonomous triage that scales with their environment.

Torq’s Agentic Builder takes that further. Security architects and operations analysts describe what they need in plain language, and Agentic Builder (part of Socrates, the core orchestrator of the Torq AI SOC Platform) reads your integrations, plans the build, writes the orchestration logic, and deploys a production-ready AI Agent directly into your environment. When frameworks, asset inventories, or threat landscapes evolve, teams update their automation through the same agentic interface, keeping response workflows aligned with the current risk program at the speed the threat landscape demands.

Cyber Risk Management Is a Business Imperative

Cyber risk management gives organizations the operational discipline to make intelligent, data-driven security decisions: decisions that align spending with actual business risk, demonstrate due diligence to regulators and stakeholders, and ensure business continuity when incidents occur.

The four-stage cycle of identification, assessment, mitigation, and monitoring creates the structure. Frameworks like NIST, ISO, and FAIR provide the methodology. Best practices address the specific risk categories that matter most. And automation closes the execution gap between knowing a risk exists and acting on it at the speed modern threats require.

Torq’s AI SOC Platform gives security teams the Hyperautomation engine and agentic response to operationalize their CRM program continuously, connecting every tool in their stack, automating risk response workflows, and keeping security posture aligned with a threat landscape that never stops evolving.

Is your cyber risk management program running as a continuous operational discipline, one that catches and closes exposures in real time, or does your team have an opportunity to move beyond periodic review cycles?

Most AI triage judges every alert from scratch; fast, confident, and often wrong. Torq Auto Triage works differently. It learns from your analysts’ decisions and your organization’s history, getting more accurate with every case.

The SOCs winning the AI SOC Apocalypse aren’t just automating triage. They’re building institutional intelligence that compounds over time. 

The question is whether yours is one of them.

FAQs

What is cyber risk management?

Cyber risk management is the continuous process of identifying, assessing, mitigating, and monitoring threats to an organization’s digital assets, systems, and operations. It combines threat modeling, risk quantification, control implementation, and ongoing surveillance into a repeatable cycle that keeps security posture aligned with an evolving threat landscape. The goal is protecting business continuity, demonstrating due diligence to regulators and stakeholders, and making security investment decisions based on actual risk. Learn how the cybersecurity lifecycle framework connects CRM to detection, response, and recovery operations.

What is the difference between risk assessment and risk management?

Risk assessment is one stage within the broader risk management process. A risk assessment analyzes identified threats and vulnerabilities to measure their likelihood and potential impact, producing a prioritized picture of where risk exposure is greatest. Risk management is the full cycle: identifying assets and threats, conducting assessments, choosing and implementing mitigation strategies, and monitoring continuously for new risks and changes in existing ones. Assessment informs management; management drives the decisions that assessment results support.

What are the main steps in the cyber risk management process?

The four main stages are risk identification (cataloging assets and mapping threats), risk assessment and quantification (measuring likelihood and financial impact), risk mitigation (choosing response strategies and implementing controls), and continuous monitoring (tracking the risk register, surveillance of the threat landscape, and formal acceptance of residual risk). Each stage feeds into the next, and the cycle repeats continuously as the organization’s environment and the broader threat landscape evolve. See how security incident categories inform risk prioritization across each stage.

What cybersecurity frameworks are used for risk management?

The most widely adopted frameworks are NIST CSF and RMF (strong in U.S. critical infrastructure and federal environments), ISO 27001/27005 (internationally recognized, audit-ready structure for an ISMS), and FAIR (quantitative methodology for expressing risk in financial terms). Each framework addresses a different dimension of the CRM challenge: NIST and ISO provide process structure, FAIR provides quantitative rigor. Many organizations combine elements of multiple frameworks to match their regulatory environment, risk appetite, and operational maturity. The cybersecurity frameworks guide covers how to choose and apply the right framework for your environment.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Torq Named a Leading Innovator in SACR 2026 AI SOC Market Report

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Software Analyst Cyber Research (SACR) just published its 2026 AI SOC Market Report, offering an independent assessment of vendors competing in what has rapidly become the most consequential category in enterprise security. Torq features prominently, and the report’s framing is worth unpacking because it illuminates what makes the AI SOC category hard to evaluate and why Torq’s approach is consequential.

Torq’s AI SOC: From Alert Triage Through Remediation

SACR’s most pointed observation about Torq is definitional. The firm writes:

“Torq is best understood less as a conventional SOAR vendor with AI features and more as an AI SOC operating layer that can ingest alerts, classify triage outcomes, construct cases, assign work to Socrates, and route remediation through deterministic or agentic workflows depending on the use case.”

That distinction matters. Much of what gets marketed as AI SOC today amounts to copilot functionality that surfaces recommendations and draft summaries, and stops at basic triage that simply moves the bottleneck down the SOC line by an increment. SACR cuts through that framing: 

“Torq is trying to own high-volume alert triage and response closure, not simply accelerate analyst review.”

Owning closure requires a different architecture than assisting analysts. It requires accurate alert classification at scale, a context layer deep enough to support trustworthy, autonomous verdicts, case management that carries investigations forward, and response automation that can act, not just advise. But let’s circle back and dwell a bit on the first phase: autonomous alert triage.

Auto Triage: Context Is the Differentiator

Torq Auto Triage classifies incoming alerts as false positive, benign, or malicious, enriches them with threat intelligence and business context, and routes them accordingly, all before a human analyst is involved. True positives become cases automatically. False positives are fed back into the per-tenant AI model.

SACR called out the quality of Torq’s context layer directly: 

“Torq is not treating alerts as isolated artifacts. It is building a context pipeline around entities, access history, business role, device state, SaaS activity, and related evidence before determining whether an alert should be closed, escalated, or remediated.”

Three underlying capabilities power that context pipeline.

  1. Torq Reflex is a per-tenant ML model trained continuously on your team’s confirmed verdicts.
  2. Torq Recall retrieves the most relevant prior cases from your environment’s history and applies an LLM to determine how those precedents apply to the current alert.
  3. Torq Context Graph provides the unified substrate both depend on: a continuously updated map of identities, assets, networks, policies, and analyst decisions, normalized across your entire security stack.

The results speak volumes. On average, large enterprises achieve a mean time to triage (MTTT) of 1 minute, a 60x improvement over manual triage. A global biotech titan cites a 97% reduction in noise entering the SOC; imagine how much better their security analysts can focus. A well-known financial services enterprise achieved 99% faster threat triage after deploying Torq.

Case Management: The Operating Unit

When Auto Triage surfaces a true positive, it flows directly into Torq Case Management, where analysts inherit the full verdict, enrichment context, and proposed next steps. They do not reconstruct context from scratch.

From within the case interface, analysts collaborate with Torq Socrates™, trigger automated response actions, and track investigation continuity across shift handoffs. Each confirmed verdict and analyst correction flows back into Reflex as a training signal, compounding accuracy over time. 

This is the mechanism behind what SACR identifies as Torq’s stronger-than-expected investigation story: the platform captures and encodes analyst judgment, rather than relying on individual expertise to repeat the same reasoning shift after shift. The machine clears the noise. The analysts focus on the highest priority items.

Socrates: Reasoning and Orchestration

Torq Socrates is the agentic reasoning and orchestration layer at the center of the platform. It can be used interactively by analysts, embedded in investigation templates, or assigned cases autonomously. Once on a case, Socrates plans investigations, delegates tasks to specialized Torq HyperAgents®, and coordinates response actions across the security stack.

SACR characterizes Socrates as “the reasoning and planning layer that decides how much work should be agentic, how much should be deterministic, and where the human should approve or intervene.” As SACR notes, “autonomy is a dial, not a binary switch,” and Torq’s model lets security organizations operationalize that dial gradually: starting with triage and recommendation, moving into human-approved action, and eventually automating higher-confidence alert classes.

One Torq customer on PeerSpot describes the cumulative impact: Torq handles a large volume of their alerts autonomously, fundamentally changing the burden placed on their security team.

Hyperautomation: Execution Depth

Torq Hyperautomation is the execution layer that connects AI decisions to real action, supporting both agentic and deterministic workflows across the full security stack. SACR identifies this automation heritage as a structural advantage: 

“Compared with AI SOC point solutions, Torq’s advantage is the ability to connect AI decisioning to actual workflow execution.”

That advantage compounds. The same platform that classifies an alert, builds the case, and assigns it to Socrates is the platform that executes containment and remediation at machine speed. Customers have measured a 94% reduction in mean time to respond (MTTR), a metric that requires the full chain, not just faster triage at the front end.

What SACR’s Assessment Means for Buyers

SACR closes its Torq vendor profile with a synthesis that applies beyond Torq specifically: 

“Autonomous SOC value will be measured by closed-loop operating capability rather than AI summarization.” 

Verdict quality matters. But a verdict quality that does not connect to case construction, investigation, response, and organizational learning is an incomplete story. Torq’s architecture is designed around that full loop.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Enhancing SOC Efficiency with Autonomous Alert Investigation Tools

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • Autonomous alert investigation uses AI agents to enrich, analyze, and reach a verdict on every alert, then close routine alerts or escalate real threats with the case assembled.
  • It reduces analyst workload, speeds up response, and keeps investigations consistent from shift to shift.
  • Effective solutions classify alerts in real time, integrate threat intelligence, and explain every verdict.
  • Most teams get there in stages, moving from AI assistance to supervised autonomy, with humans approving high-impact actions.
  • The Torq AI SOC Platform pairs Torq Auto Triage with investigation, case management, and response, with humans in control.

Every alert is a small investigation. Who is this user? What did this process do? Has anyone seen this before? Multiply those questions by thousands of alerts a day, and a SOC spends most of its energy answering the same questions in the same order.

Autonomous alert investigation hands those questions to AI agents that find the answers, reach a verdict, and show their work. Analysts keep their attention on the alerts that need a human. Read on to learn how it works, what it changes for SOC efficiency, how to adopt it step by step, and where the Torq AI SOC Platform fits in.

Understanding Autonomous Alert Investigation in SOCs

Autonomous alert investigation moves the first pass of every investigation from analysts to AI agents.

Definition and Core Concepts

Autonomous alert investigation is the use of AI agents to enrich an alert, analyze the evidence, and reach a verdict. The agent then closes routine alerts or hands real threats to an analyst with the case already assembled. It is the working core of an autonomous SOC, where AI handles high-volume, low-complexity work and humans oversee the decisions that matter.

How Autonomous Alert Investigation Tools Work

Most tools follow the same four steps:

  1. Ingest and normalize. Alerts arrive from across the security stack in one consistent format.
  2. Enrich. The agent adds business context, threat intelligence, and history from similar cases.
  3. Reason and decide. The agent assigns a verdict and severity, with its reasoning attached.
  4. Act. The agent closes the alert, escalates it with a full case, or runs an approved response.

Key Terminology for SOC Teams

A few terms come up in every conversation about autonomy:

  • Alert triage. Sorting alerts into real threats and noise, and ranking them by risk.
  • Alert investigation. Gathering and analyzing evidence to confirm what happened and how far it spread.
  • Verdict. The conclusion an agent reaches, such as malicious, benign, or needs review.
  • Human-in-the-loop. A model where the agent waits for a person to approve an action before it runs.
  • Human-on-the-loop. A model where the agent acts on its own within defined limits, and people review its work after the fact.
  • MTTI and MTTR. Mean time to investigate and mean time to respond, the core efficiency metrics.

Evolution of SOC Efficiency: Manual vs. Autonomous Methods

SOC efficiency has moved in steps, from analysts working queues by hand to AI agents investigating alongside them.

Traditional Alert Investigation Approaches

In a traditional SOC, analysts pull alerts from a queue, pivot across consoles to gather context, and write up their findings. Scripts and playbooks speed up repeatable steps, and the analyst’s judgment ties everything together.

Limitations of Manual SOC Operations

That model scales with headcount, and alert volume grows faster than hiring. Queues age, quality varies by analyst and shift, and knowledge stays locked in people’s heads. Each limit points to the same opportunity: remove repetitive investigation work so SOC teams can spend time where judgment counts.

Interest has shifted from scripted automation toward agentic approaches that reason through an investigation. Analyst firms now publish dedicated research on autonomous SOC solutions, and buyers increasingly ask for transparent reasoning, deep integrations, and clear human controls.

The Role of AI in Modern Alert Investigation

AI agents supply the reasoning that lets an investigation run without waiting on a person.

AI-Powered Accuracy and Speed Improvements

AI agents work through an alert in seconds and improve as they learn from feedback. Torq Auto Triage averages 42 seconds per alert and reaches 94% accuracy out of the box, improving as analysts confirm or correct its verdicts.

Machine Learning Models for Alert Triage

Machine learning models learn which alerts matter most from historical cases and analyst feedback. Large language model agents add reasoning: they read the alert, weigh the context, and explain the verdict. Deterministic guardrails keep high-stakes decisions within limits your team defines.

Integrating AI with Existing SOC Tools

Agents connect to your SIEM, EDR, identity, email, and ticketing tools through APIs, so your current stack stays in place. The Torq AI SOC Platform connects to more than 400 tools out of the box, and Torq HyperAgents® brings specialized AI Agents to investigation and response.

Major Benefits of Autonomous Alert Investigation Tools

The payoff shows up in three places: analyst time, response speed, and the quality of every investigation.

Reducing Analyst Workload and Burnout

Agents take over the repetitive Tier 1 work that fills analyst queues. The Torq AI SOC Platform can auto-remediate 95%+ of alerts, so analysts spend their days on threat hunting, detection tuning, and complex cases, the work that keeps people engaged.

Faster Incident Response Times

Agents start investigating the moment an alert arrives and gather evidence from every tool in parallel, the core promise of incident response automation. Torq delivers a 90%+ reduction in mean time to respond (MTTR).

Improved Consistency Across Alert Investigations

Every alert gets the same investigation logic, whoever is on shift. Verdicts arrive with full reasoning and evidence, so reviewers can quickly check the work, and the SOC’s best practices apply to every case.

Core Features of Effective Autonomous Alert Investigation Solutions

Three capabilities separate strong solutions from tools that only summarize alerts.

Real-Time Alert Classification

Effective tools normalize and classify alerts the moment they land. They extract observables such as IPs, domains, file hashes, and user identities, label each alert by type, assign a severity, and map each alert to MITRE ATT&CK so analysts can see where it fits in an attack.

Threat Intelligence Integration

Every alert should arrive enriched with commercial and open-source threat intelligence, historical case data, and business context. Rules keep crown-jewel data and VIP users at critical priority, so the most important business risks never depend on a model’s guess alone.

Agentic Response and Remediation Capabilities

Verdicts should turn into action through agentic response. In a phishing investigation, for example, agents analyze the message and its links, find similar emails across mailboxes, remove them, and flag users who clicked, with approval gates on high-impact steps such as password resets.

Autonomous SOCs: Operational Differences from Traditional SOCs

An autonomous SOC changes who does the first pass, how decisions get made, and how work is recorded.

Agentic Alert Triage Processes

In an autonomous SOC, every alert is triaged on arrival, and none waits its turn in a queue. Agents suppress noise, prioritize real threats, and open cases for the ones that matter, so analysts start their shifts with a short list of verified issues.

Human-in-the-Loop vs. Fully Autonomous Models

Autonomy works like a dial. Human-in-the-loop models have people approve the agent’s actions, which builds trust early on. More autonomous models allow agents to act on their own within defined limits and to escalate when a case crosses a risk threshold. Torq Socrates™, Torq’s agentic SOC orchestrator, coordinates specialized agents and follows the off-ramps your team defines, so humans step in exactly where you want them.

Case Management and Documentation Enhancements

Torq Case Management keeps the evidence, timeline, and summary for each case in one place. AI-generated summaries give analysts the full picture in seconds, and every agent decision lands in an auditable log, so handoffs and reviews start with complete context.

Maturity Model for Autonomous SOC Adoption

Autonomy grows in stages, and each stage earns the trust needed for the next.

Stages of Alert Investigation Automation

Most teams move through four stages:

StageWhat AI doesWhat analysts do
1. AI assistanceSummarizes alerts and answers questions in plain languageInvestigate and act on every alert
2. Enriched recommendationsEnriches alerts and recommends a verdictReview the verdict and decide
3. Supervised autonomyInvestigates and resolves routine alerts and escalates the restApprove high-impact actions and review samples
4. Broad autonomyHandles most Tier 1 and Tier 2 cases end-to-endFocus on critical incidents, threat hunting, and tuning

Scaling from AI Assistance to Full Autonomy

Move up a stage when the data says you are ready. For each use case, track agent accuracy, the share of verdicts analysts override, and MTTI and MTTR. When accuracy holds steady and overrides stay low, raise the autonomy level and shrink review to a sample. Even at the top stage, humans set the goals, keep override control, and approve high-impact actions.

Incremental Roadmap for U.S. Organizations

A phased roadmap suits US organizations that balance lean teams against audit and compliance expectations:

  1. Choose one or two high-volume alert types, such as phishing and endpoint alerts.
  2. Connect your core tools and establish baselines for MTTI, MTTR, and false-positive rate.
  3. Run agents in recommendation mode, with analysts reviewing every verdict.
  4. Enable autonomous closure for routine alerts, with approval gates on high-impact actions.
  5. Expand to new alert types and review results with leadership and compliance stakeholders on a regular cadence.

Challenges in Building Fully Autonomous SOCs

Every challenge below has a practical fix, and most teams solve them in the same order they appear.

Data Quality and Normalization Issues

Agents reason over the data they receive, so inconsistent alert formats and missing asset context limit their accuracy. Normalizing alerts into a common schema and keeping asset and identity inventories current gives agents a solid foundation.

Addressing Skills Gaps in Security Teams

Autonomy changes the analyst’s job from working queues to supervising agents. Teams can upskill analysts to write agent guidelines in plain language, review reasoning, and tune detections. Natural-language tools such as Agentic Builder, which turns plain-language requests into deployed AI Agents, make that shift easier for junior analysts.

Overcoming Organizational Resistance

Trust grows with evidence. Start with an analyst review of every verdict, share accuracy and time-saved metrics with the team, and frame agents as capacity that extends the team’s reach. Transparent reasoning and auditable logs help skeptical stakeholders see exactly how decisions get made.

A More Efficient SOC Starts with the First Investigation

Autonomous alert investigation gives SOC teams a practical way to raise efficiency without adding headcount. AI agents handle the first pass, and analysts focus on the threats that need human judgment.

The platform you choose decides how far that goes, so evaluate options against clear criteria and grow autonomy as trust builds.

Ready to find the right AI SOC for your team? Download the AI SOC Buyer’s Guide by John White for guidance on what to look for before you buy.

FAQs

What Is Autonomous Alert Investigation?

Autonomous alert investigation is the use of AI agents to enrich an alert, analyze the evidence, and reach a verdict without waiting for an analyst. The agent closes routine alerts and escalates real threats with a complete case, while humans set the goals and approve high-impact actions.

What Makes Autonomous Alert Investigation More Effective Than Manual Methods?

Autonomous investigation covers every alert on arrival, gathers evidence across tools in parallel, and applies the same logic each time, so coverage, speed, and consistency improve together. Torq Auto Triage, for example, averages 42 seconds per alert. Analysts keep their time for complex cases.

Can Autonomous Alert Investigation Tools Work Alongside Human Analysts?

Yes. The tools handle routine alerts and hand complex cases to analysts with the evidence already assembled. Approval gates guard high-impact actions, auditable logs show every decision, and analyst corrections make the agents more accurate over time.

How Are AI-Powered Tools Changing the Future of SOC Operations in the United States?

AI-powered tools are shifting US SOCs from working queues to supervising agents. Agents handle routine investigation, and analysts focus on threat hunting, detection tuning, and high-impact decisions. That shift lets lean teams cover more alerts without adding headcount.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Turning On Torq Mode

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Dima Kogan is Director of Product Design at Torq, where he leads the design team building Torq’s AI-powered cybersecurity products. Over 15 years in product design, including design leadership at monday.com, he’s spent his career making complex systems feel simpler to use. He writes regularly about product design, leadership, and designing in the age of AI.

Most enterprise cybersecurity products focus on functionality. That’s fine. It’s the job. But enterprise security teams spend hours inside their core products — real humans, doing really important work, seeing the same thing day after day after day.

As our platform grew, we started asking ourselves a simple question: why should powerful software have to look so…generic? We’d spent years making The Torq AI SOC Platform smarter, faster, and more capable. But visually, it still felt like it could belong to almost anyone.

Torq is known for being bold and fun — and that distinctiveness carries weight. Wear a Torq hat at a security conference, and people stop you to talk. But inside The Torq AI SOC Platform, that personality wasn’t there. We’d poured everything into functionality, and at first, the interface wasn’t really us.

Why So Serious?

Consumer software figured this out a long time ago: how a product feels is a big part of whether people stick with it. Enterprise software has been slower to catch on, and security software slowest of all.

The assumption in security has always been that personality is frivolous, or worse, unprofessional. The work is high-stakes, so the tools are built to be serious and nothing else. The result is a whole category of products that look interchangeable and feel clinical.

Our design mission made the goal clear: build products that are powerful, category leaders, and unmistakably Torq. The harder part was execution. How do you bring skeletons, lasers, and monster trucks into the leading AI SOC platform without getting in the way of the work?

Introducing Torq Mode

We started with the people who use Torq: security analysts working under real pressure, and engineers building complex workflows. The work is serious, which is exactly why the experience matters. As one engineer at AppsFlyer put it, “SecOps is a tedious, tiring job. It’s important to have some fun.”

So we got specific about how we wanted them to feel: in control, eager to build, and confident in the system, with a real sense of mastery in what they’d built. One rule anchored everything: Torq is where analysts handle critical incidents all day, so anything we added had to reinforce the experience without interrupting the work.

Thus, a third mode was born alongside Light and Dark modes. Users can choose the standard experience in Light or Dark, or the fully brand-connected one: Torq Mode.

We chose specific flows and interactions where a moment could land: places to encourage someone, mark a win, or draw attention to what matters. A few of them:

  • Switch to Torq Mode, and a pterodactyl flies across the screen to welcome you in.
  • Create your first workflow, and a skeleton fires a laser to draw it into being.
  • Close a case, and a monster truck rolls across the screen, pulling a “DONE AND DUSTED!” flag.
  • Flag a case as urgent, and the label catches fire on hover.

The Outcome

Two months of thinking, two weeks of building, and then we launched. The results surprised us: 81% of users who turned on Torq Mode kept it on, month after month. 

Customers started bringing it up in demos. One wrote: “The animations bring a lot of energy to the interface and make the experience feel more alive… a strong personality that’s instantly recognizable and memorable.” An engineer even spent his own time extending Torq Mode into more of the product, and a customer asked us to add sound effects. When people ask for more personality, not less, you’ve built something they connect with.

Beyond Functionality

Enterprise products already look alike, and the AI era will only push them closer together. AI will build faster than ever, but it won’t decide how people should feel. That part is still on us. Solving the user’s problem is the baseline; building an experience they remember is the craft. 

Torq Mode: on.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Torq SOC Brain™: The AI SOC That Learns, Not Just Remembers

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Back in June, I wrote a blog making the case that agentic triage alone isn’t an AI SOC. The way I see it, that’s like saying triage is the only responsibility of a SOC team. But as we know, the SOC’s responsibilities extend far beyond that, and these triage-only solutions don’t investigate threats, contain them, or close cases. That work is still left to the SOC team; the bottleneck is just shifting. 

The argument is that the bar should be higher, and Torq is setting that bar. Full lifecycle coverage — across triage, investigation, threat hunting, containment, and remediation — enterprise scale within some of the largest Fortune 100 SOCs in the world, and transparent, defensible AI agents grounded in your organization’s business context all point to why Forbes, KuppingerCole Analysts, and Gartner have recognized Torq’s position at the top of the AI SOC market.

That argument still stands, but today… We’re raising the bar again. 

Introducing: Torq SOC Brain™ — the memory layer that makes Torq the only AI SOC platform that genuinely learns.

The Self-Learning Torq SOC Brain

For most “AI SOC” platforms, learning simply means that when an alert fires, the system searches through past cases, finds one that looks similar, and feeds that example into an LLM to help it make a decision. This is more retrieval than actual learning. A system that retrieves past cases from weeks ago has no memory of what decisions were made yesterday, or understands that your senior analyst treats certain scenarios differently than your Tier 1 team does. It doesn’t get better or adapt because it’s pattern matching. And that approach is going to hit the same efficiency wall every single time. 

“With Torq SOC Brain and its Torq Recall, Torq Reflex, and Torq Retrospect capabilities, the Torq AI SOC Platform truly learns how a SOC thinks, even from the years of history that predate a Torq deployment. That’s the difference between automation that treats every investigation as if it were on its own and the industry’s first SOC that gets smarter and more accurate with each completed investigation.”

– Ofer Smadari, Torq Co-Founder & CEO

Torq SOC Brain is the learning layer of the Torq AI SOC Platform… that actually learns. Every customer has it built directly into their private workspace, exclusively for their organization. It never pools customer data, never shares model parameters, and never trains one customer’s AI on another customer’s experience. It is a private intelligence layer that ensures your Torq AI SOC Platform becomes your judgment, your model, your intelligence.

Torq SOC Brain is the reason every Torq Auto Triage verdict, every Torq Socrates™  investigation, and every Torq HyperAgents® response action gets more accurate as your team uses the platform. It’s built on three interconnected capabilities: Torq Recall, Torq Reflex, and Torq Retrospect. Together, they do something no other AI SOC platform can: turn your resolved cases, analyst decisions, and years of institutional history into a model that thinks like your team. 

Torq Recall: Memory That Actually Works

The most common form of memory in AI SOC tools is a search interface, powered by an agentic chatbot that runs stateless queries to find semantic similarities. In security, just because something looks roughly similar doesn’t mean anything; to an AI model, two hash values might look semantically close, but point to two completely different files. In a high-stakes environment, “close enough” can be catastrophic. 

Recall instead relies on structured retrieval, looking for exact, deterministic overlaps of specific security observables — IPs, file hashes, URLs, hostnames, or emails. If your team has seen an exact indicator before and documented their conclusion, Recall finds it. 

If historical cases aren’t automatically fed back into agentic decisions, institutional knowledge stays buried in closed tickets, and verdicts quickly become outdated. A case closed last week tells a very different story than one closed last year. What makes Recall truly game-changing is the understanding of the signal strength, so the AI stays focused on entities that matter. 

Recall analyzes analyst notes, weights precedents by recency, and understands that different conclusions hold different weights. And if it finds contradicting records, Recall knows when to say it’s sure and when it isn’t, rather than force an answer it cannot justify. That honesty is what builds trust in agentic decisions at scale. Triage verdicts and response actions are not based on last month’s playbook; they are grounded in how your SOC operates today and automatically applied to every alert.

Torq Reflex: Your Team’s Judgment Applied 

Often, when AI decision-making misses the mark, it simply lacks the correct context. Recall solves that problem. But research conducted by Torq Labs found that, even with all the context, all the memory, and the same facts a human analyst has, an AI model can make an incorrect decision or even contradict an earlier decision. This isn’t a data gap; it is a judgment gap between humans and machines. While Recall allows agentic verdicts to be based on your most accurate case history (i.e., the data), Torq Reflex gives the AI model access to your team’s judgment. 

Reflex is a per-tenant model that trains continuously on your team’s confirmed verdicts and corrections, engineered to operate under asymmetric risk where missing a malicious threat is considered far more costly than mislabeling a benign alert. When an alert fires, Reflex assigns a verdict and, most importantly, a calibrated confidence score — a real mathematical probability that builds trust in verdicts and makes the system safe to run.  

When confidence is high, the verdict drives automated output (e.g., filtration, case creation, prioritization, or autonomous remediation). If it isn’t high, the full analysis still runs, the agentic reasoning is documented, and the case is escalated to a human analyst for confirmation. As a result, Reflex helps improve agentic decision making with each alert, because any alert that it’s uncertain about routes back through the human-on-the-loop process you already trust. 

Whatever the analyst decides retrains the model, so every correction is worth a little more, and every verdict becomes more trustworthy. Reflex is the key to how the Torq SOC Brain actually learns and becomes more accurate over time. The longer you use Torq, the smarter the Torq SOC Brain gets.  

“The longer Torq runs in our environment, the more it sounds like our best analysts. That’s the part no other AI SOC platform delivers.”

– Director of Security Operations, Fortune 500 Financial Services

Torq Retrospect: Informed Decisions From Day Zero

Recall and Reflex drive the Torq SOC Brain to truly learn over time, becoming your own SOC model based on your own SOC judgment. But given today’s AI-augmented threat landscape, time works against SOC teams in identifying and responding to attacks now more than ever. They need an AI SOC solution that drives value now, today, not 6 months down the road. Enter Retrospect. 

Most AI SOC platforms arrive knowing nothing about the environment or how your SOC operates. Deployment is an uphill battle, early verdicts are incorrect, and analysts lose trust before the system has a chance to earn it. Retrospect makes sure you don’t start from scratch. Before Torq sees a single live alert, Retrospect normalizes all your external cases and observables, imports them from your existing case management tool, and makes that history immediately available to Recall and Reflex. Years of analyst decisions, closed cases, and documented outcomes become the foundation of the Torq SOC Brain. 

The result is an AI SOC that doesn’t just arrive informed; it’s already smarter than most deployments will hope to achieve after 6 months of production. The learning curve that kills early adoption of agentic decision making collapses entirely. Your SOC’s institutional knowledge doesn’t start accumulating on Day One; it’s already there.

What The Torq SOC Brain Looks Like In Practice

In an enterprise SOC, accuracy is dynamic. Your environment changes. AI models are upgraded. Threat actors adapt. New attack patterns emerge. Your team’s risk posture evolves with every incident you close. 

A static AI model calculates the same confidence against the same signal regardless of how many times your team has overridden it on that exact attack pattern. There is no “getting better”; it simply is what it is, never earning the trust of the human analysts responsible for defending and justifying every decision made in the SOC. 

In the 2026 AI SOC Leadership Report, 97% of respondents reported confidence in AI’s ability to address alert triage, but only 37% applied AI to the use case. The gap between confidence and adoption, the report found, is largely driven by trust. SOC leaders reported they don’t have full transparency into agentic decision-making, and therefore, can’t defend a missed alert or a false verdict. Analysts find themselves re-checking the agent’s conclusions, doubling the work, and leaving them right back where they started: buried in alerts.    

On the other hand, Torq Auto Triage has maintained 100% usage retention across all customers and a steady average MoM increase of 144% in alert volume fed into the system. Torq Auto Triage customers report a 97% reduction in alert noise, a 60x increase in triage velocity, and an improvement in accuracy score from 94% to 99% over an average three-month period. 

“Torq Auto Triage was ready for an enterprise of our scale, where a competing solution was not.”

– Global FinTech Enterprise

The Torq SOC Brain drives accuracy in agentic verdicts, acting as the primary engine and memory layer behind Torq Auto Triage. The Torq SOC Brain justifies each Torq Auto Triage verdict with crystal clear evidence and reasoning, documented and cited in the historical truth of how your SOC operates. Those verdict decisions improve in accuracy with every alert and are treated as first-class data, stored in the Torq Context Graph. This, in turn, grounds every agentic decision across the entire Torq AI SOC Platform in your organization’s most accurate and up-to-date truth. Every triage verdict becomes more confident, every investigation becomes more precise, and every autonomous threat remediation becomes more trustworthy. 

Most importantly, the Torq SOC Brain is what allows some of the largest enterprise SOCs in the world to achieve such rapid time-to-value with the Torq AI SOC Platform: 

  • “We use Torq to automate triage across multiple attack surfaces. It performs better than other solutions. [Torq’s] AI capabilities provide immediate ROI by reducing manual effort and significantly improving operational efficiency.” – Senior Cybersecurity Engineer, Tech Vendor (10,001+ employees)

Most recently, the InfoSec Director of a Fortune 100 Global Retail Enterprise, who completed a full Torq AI SOC Platform migration in only two weeks, reported: “In just three months, we’ve already accomplished so much more than we ever did in five years with [previous solution].”

Your Judgment. Your Model. Your Intelligence.

Torq has been widely recognized as a leading innovator and a dominant force in the AI SOC landscape (see Forbes, KuppingerCole Analysts, and Gartner). We set the bar for end-to-end threat lifecycle coverage, while others simply triaged threats and shifted the SOC bottleneck further down the line. 

Today, the bar is even higher. The question isn’t just whether your AI SOC completes the threat lifecycle; it’s whether it learns how your team wants it done. 

Your AI SOC should handle every alert the way your team would, and get better at it over time. That’s the Torq SOC Brain. That’s why Torq Auto Triage is the only agentic triage engine that actually learns. And that’s why the Torq AI SOC platform isn’t just the most complete AI SOC on the market; it’s the only one that becomes your organization’s own AI model. 

See it live at Black Hat at Booth #4935, or request a demo today.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

The 2026 AI SOC Roadmap: Where SOC Teams Are Headed and How to Get There

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Every conversation our team has with security leaders begins the same way. Nobody is backing off on AI in the SOC. The direction of the lean is what’s shifting.

Torq’s 2026 AI SOC Leadership Report surveyed more than 450 CISOs and SOC leaders. The data confirms what those conversations were already telling me. We’ve left the adoption phase. The market is now in the architecture phase and the implications for how teams plan, buy, and build are significant.

The first wave of AI in the SOC came down to a few questions: Does it work? Can a large language model read an alert? Can an agent investigate a case? Can autonomous reasoning extend triage without breaking trust? All three are answered. Answered well enough that 94% of security leaders now use AI in at least one SOC function, and the report found that the average SOC runs more than seven AI-powered tools at once.

The architecture phase is about different questions. Which platform anchors the operation? What gets consolidated, and what gets replaced? Where does AI extend next, and what kind of trust framework lets it? The teams moving fastest right now aren’t running more AI experiments. They’re making architectural commitments — commitments that will shape the SOC through 2026 and beyond.

Where Teams Are Expanding AI in the Next 12 Months

Two expansion frontiers stand out in the data. Both are large, both are intentional, and both point in the same architectural direction.

  1. Cloud security: 40% of security leaders plan to expand AI here in the next 12 months — the largest expansion category in the report, and it’s not close. Cloud security is the cleanest use case for AI in the SOC because it’s the area where manual coverage has fallen furthest behind operational reality.
  2. Incident response automation: 28% of leaders plan to expand AI into response. Detection automation has been broadly accepted. Response automation is the next earned step — extending AI from “tell me what happened” to “act on what happened.” It’s a smaller percentage because it’s a higher-stakes commitment, but the direction is clear.

Underneath those headline numbers is a more telling pattern. Security leaders said they want 51% of daily SOC tasks automated on average — and the teams furthest along on AI deployment are also the teams setting the highest targets for the next 12 months. That correlation is the architectural payoff. Early adopters who built on the right foundation are now expanding from it.

Why Cloud Security Leads the Expansion

Cloud security generates orders of magnitude more telemetry than legacy infrastructure. The volume problem alone forces the issue: a team that can only review a small fraction of cloud signals manually needs AI to handle the rest. Hiring doesn’t close that gap, and CISOs know it.

The second reason cloud leads AI expansion plans is configuration drift. Cloud environments change continuously — new services spun up, identities rotated, workloads scaled across regions overnight. A static playbook for cloud detection is obsolete the moment the environment changes beneath it. AI that reasons across the current state of the environment adapts in ways static logic cannot.

The third reason is that in the cloud, finding a problem and fixing it are two different jobs owned by two different teams. Security can embed control points in the delivery pipeline and continuously scan cloud assets, but it can’t remediate unilaterally — the production environment belongs to DevOps and engineering. So every finding kicks off a lifecycle: detect the issue, identify the owner, get them to commit to a fix, and validate that the fix actually resolved it. That coordination loop, not the detection, is where the enormous operational load of cloud security comes from, and it’s exactly the kind of multi-step, multi-owner work AI orchestration is built to carry.

This is the structural reason cloud security is the strongest signal in the expansion data. The architecture that handles it has to orchestrate the full remediation lifecycle across teams, not just detect within a single team.

Why Incident Response Is the Trust Frontier

Detection automation was adopted broadly because it keeps a human in the loop: the AI surfaces risk, and a person still decides what to do about it. It’s the most common error, a false positive, that costs little more than analyst time. Response automation removes that buffer — the AI acts on the environment itself, so a wrong call doesn’t just waste time, it hits production. A contained endpoint that shouldn’t have been contained breaks a workflow, a revoked credential disrupts a legitimate session, and an auto-blocked IP can take down a production service. The stakes move outside the SOC, and the trust required to cross that threshold rises with them.

The data shows leaders are ready to cross it, but only on specific terms. The conversations behind the 28% expansion number make those terms clear.

  • Transparent reasoning: Every action an AI takes must be supported by a documented chain of reasoning. Black-box decisions don’t earn trust in response, and they shouldn’t.
  • Configurable autonomy: The team decides which actions AI can take autonomously, which require human approval, and which never run without analyst sign-off. The trust model is set by the operator, not by the platform vendor.
  • Continuous learning: Actions taken under AI direction are logged, auditable, and recoverable. When an agentic verdict is overturned, the decision becomes precedent, and the system improves. 

This is the architecture we built at Torq for response automation. Agentic action earns the right to expand into incident response when the decisions behind it are grounded in organizational context, not just a siloed signal triggering a cookie-cutter response workflow. 

The Torq Context Graph makes that trust possible, giving Torq AI Agents a single source of truth to reason over before any runbook planning or execution. What is true about the environment now? What exceptions have been made since this response plan was first crafted? Every response is executed exactly as an analyst would — with context, without improvisation. 

Socrates, Torq’s AI SOC orchestrator, makes the trust boundary visible: when it encounters a step it can’t perform, it stops, names the limitation in plain language, and routes the work to a human. That’s the architecture that earns the right to expand AI into response.

What the Architecture Phase Requires

The teams that will win the next 12 months won’t be the teams with the most AI tools. They’ll be the teams with the best-architected AI platform. Three commitments separate the platforms that will define the AI SOC from the vendors that will get stuck.

1. A platform, not a stack. The report found that 80% of security leaders say their SOC is still fragmented across too many tools. The architecture phase rewards unification. The teams that pick a single platform to anchor the AI SOC and start unifying around it will move faster than the teams continuing to stitch together point solutions.

2. Trust by design. 90% of security leaders want explainable AI decisions before they’ll trust AI with more autonomy. The platforms that make AI reasoning visible — every step, every decision, every action documented — will earn the trust required to keep extending. The platforms that don’t, won’t.

3. Learning that compounds. The AI you deploy today should be measurably better six months from now, and it should be better because of your team’s specific corrections. Static AI plateaus, but adaptive AI compounds. The architectural commitment is to a platform whose returns scale with the team using it.

These are the foundations on which the architecture phase is built on. Platforms that ship them as design principles will define the AI SOC through the next few years. Platforms that bolt them on later won’t. 

The 12-Month AI SOC Playbook

Below is some concrete guidance for the security leaders reading this with a budget cycle ahead of them.

Audit the gap. Map your current AI  coverage against the end-to-end SecOps lifecycle that 89% of respondents identified as a key factor to increasing agentic trust, producing better-informed conclusions, and higher-confidence recommendations. Does your architecture cover triage, investigation, threat hunting, and response? Most AI point solutions are missing coverage, claiming to be something they are not. 

Choose your unification anchor. If your stack runs more than seven different AI-powered tools (and the data says it probably does), pick one as the unification anchor and start measuring the others against it. The architecture phase rewards conviction. Indecision rewards no one.

Extend AI into response on your terms. Pick the two highest-volume response workflows your team handles manually today. Move them to AI-led execution, with analyst oversight for actions that require it. Measure the trust gap and the operational impact over 30 days. Expand or roll back based on the data. That’s how trust gets built — case by case, with the operator in control.

The AI SOC Roadmap Through 2026 and Beyond

The architecture phase isn’t a single year of work. It’s the foundation for what the AI SOC looks like by 2026 and beyond. The decisions made over the next 12 months compound — which platform anchors the SOC, which workflows get extended into AI, which trust framework earns the team’s confidence.

The teams that get this right won’t be the teams with the most AI tools. They’ll be the teams whose AI gets measurably better the longer it runs, on a platform built for that trajectory. The 2026 AI SOC Leadership Report has the full data behind where 450 security leaders are headed — what they’re prioritizing, what they’re walking away from, and what the architecture phase looks like across industries and team sizes.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

20 Questions Every Security Leader Should Ask Before Buying an AI SOC

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Most “AI SOC” demos out there can look great. The polished dashboard, the confident verdict, the slide that says “autonomous.” A demo is built to show the platform at its best, on clean data, in a controlled environment, answering a question the vendor already knew was coming. The differences only show up after you’ve signed, when the platform meets your real stack, alert volume, and compliance requirements.

That’s why your AI SOC evaluation can’t end at the demo. The questions below are designed to surface what a polished walkthrough may hide. They’re grouped by what each cluster actually tests, with the kind of answer that should reassure you and the kind that should worry you. 

If a vendor dodges, over-promises, or answers a different question than the one you asked, you’ve learned something the demo wouldn’t have told you.

Integration and Context

A SOC doesn’t run on one tool. It runs on a stack — SIEM, EDR, identity, cloud, email, ticketing — and an AI SOC is only as good as its ability to reason across the whole stack. A platform that can’t see your whole environment will make confident decisions on partial information, which is worse than no decision at all. 

Context is what separates a verdict that’s right in general from one that’s right for you: the same login anomaly is benign for a contractor on a known VPN and critical for a finance director near the M&A data room. Ask:

  1. Does the platform integrate with your existing stack as a unified orchestration and case management layer, instead of forcing a rip-and-replace?
  2. Can it correlate signals, context, threat intelligence, and historical activity across SIEM, EDR, identity, cloud, email, and your other systems?
  3. Does it maintain a continuously updated context model, a single source of truth for your environment?
  4. Does it provide native case management, investigation timelines, and cross-tool evidence correlation?

What a strong answer sounds like: The platform layers on top of what you own, builds a living model of your environment, and continuously improves its understanding as more systems are connected.

Red flag: The vendor wants to replace tools you just bought, or treats “integration” as a one-way alert feed with no context flowing back.

Memory and Learning

When a senior analyst leaves, their judgment usually walks out with them. The same is true of most “AI SOC” tools: every alert is evaluated from scratch, and the hard-won verdict your team reached last week is buried in a closed ticket. 

A real AI SOC turns past decisions into precedent, so the platform gets sharper the longer it runs, rather than repeating the same mistakes at machine speed. If a vendor can’t explain how their system learns from your analysts specifically, what you’re buying is static automation with a better logo. Ask:

  1. Can the AI reference prior investigations, analyst decisions, and case outcomes when evaluating a new alert?
  2. Does it maintain persistent organizational memory, so analyst decisions improve future verdicts?
  3. Can it explain which prior cases, decisions, or patterns influenced a recommendation?
  4. Does it learn from analyst feedback, verdict changes, and case resolutions to calibrate confidence over time?

What a strong answer sounds like: The platform shows you the past cases behind a verdict and measurably improves as your team corrects it. 

Red flag: “It learns from feedback” with no explanation of how, or learning that lives in prompts rather than a model that actually remembers.

Action and Autonomy

This is the line most “AI SOCs” can’t cross, and it’s the one that matters most. Triage prioritizes risk; it tells you what’s real and what’s next. But if the platform then hands a to-do list to a human, it hasn’t reduced the workload. The investigation still happens by hand, the response still requires logging into another tool, and the case still closes on human time. 

A true AI SOC carries the alert through to resolution and escalates to a person only when judgment is genuinely required. Ask:

  1. Does the platform go beyond triage to autonomously investigate, contain, remediate, and close incidents?
  2. Can it update cases in real time, adapting from autonomy to escalation the moment a threshold is met?
  3. Does it support human-on-the-loop operations, where analysts step in only when needed instead of driving every workflow?
  4. Can you set adjustable autonomy levels based on severity, confidence, business context, and risk tolerance?

What a strong answer sounds like: The platform closes a meaningful share of cases end-to-end, and you control where it acts versus escalates. 

Red flag: “Autonomy” that stops at a recommendation, or an all-or-nothing switch with no dial for severity and confidence.

Customization and Control

No vendor’s out-of-the-box agents know your policies, your escalation paths, or your risk tolerance on day one. The platforms that work are the ones you can shape to your environment without a team of engineers babysitting them. 

This is also where the trust conversation lives: security leaders are right to be cautious about handing authority to a system, and the answer isn’t less automation, it’s more control over what the automation is allowed to do. Ask:

  1. Can analysts customize agent behavior, workflows, permissions, escalation boundaries, and objectives?
  2. Can they do it in natural language, without weeks of engineering?
  3. Can agents access only the systems, data, and tools an administrator explicitly authorizes?
  4. Does the platform include enterprise-grade RBAC, governance controls, approval workflows, and policy guardrails?

What a strong answer sounds like: You define each agent’s role, scope, and authority, and you can adjust it as trust grows. 

Red flag: Agents that can only be tuned by the vendor, or broad access with no granular permission model.

Transparency and Accountability

In the SOC, trust isn’t automatic… It’s earned. According to Torq’s 2026 AI SOC Leadership Report, 92% of security leaders cite at least one factor reducing their trust in AI, and black-box reasoning ranked among the top concerns, and was the number-one concern for SOC directors specifically. 

An AI that hands down a verdict without showing its work doesn’t solve the trust problem. It defers it until the first false positive takes down a production system at 2am. Transparency is also what makes the platform defensible to auditors and boards. Ask:

  1. Can the AI explain its reasoning for every verdict, recommendation, escalation, and action?
  2. Are all actions, reasoning chains, overrides, and outputs captured in immutable audit logs?

What a strong answer sounds like: Every decision comes with its reasoning and evidence, and nothing happens that isn’t logged. 

Red flag: “Trust the model” with no inspectable reasoning, or audit trails that capture outcomes but not the why behind them.

Scale and Proof

A demo runs in a sandbox. Your SOC runs in the complex real world at volume, under compliance requirements, with multiple business units and data residency rules. Plenty of new entrants look impressive on stage and fall apart on contact with that reality. 

The only real proof is production: named customers, hard numbers, and metrics a CISO can take upstairs without a caveat. Ask:

  1. Can the platform operate reliably at enterprise scale, with high alert volumes, real-time response, multi-tenancy, segmentation, and data residency support?
  2. Can it prove operational impact — MTTR reduction, case closure rates, analyst time recovered, false positives eliminated — with the metrics a CISO can take to the board?

What a strong answer sounds like: Referenceable enterprise customers and specific, verifiable outcomes. 

Red flag: Logos with no numbers, or numbers with no named customers behind them.

It All Comes Down to One Question

Read them together, and a single question emerges: Can the platform take action across your stack with reasoning you can see and controls you can govern, at the scale you actually operate? A triage-only tool answers “no” to half of these. A repackaged legacy product answers “no” to the rest.

If it can’t take action, it’s not an AI SOC. It’s one more thing to manage.

The Torq AI SOC Platform was built to answer yes to all 20. Auto Triage increases verdict velocity 60x, cutting MTTR and exposure time. Socrates builds, deploys, and orchestrates Torq HyperAgents® across triage, investigation, response, and remediation, with transparent reasoning, adjustable autonomy, and enterprise-grade governance, all grounded in the Torq Context Graph. The platform runs more than one billion automated actions a week and is trusted in Fortune 500 production, with native metrics that a CISO can take to the board.

Ask any competitor to answer all 20. Torq does.

Survive the AI SOC Apocalypse. Read the blog series.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO