From Buying Torq to Building Torq

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

It keeps happening.

Someone implements Torq. They see what it does to their SOC. They start evangelizing it internally. And when their own career path eventually points somewhere new, they reach out.

This is the second time we’ve written this blog, and this time, four more former customers came to us: Austin Dix, Nate Thompson, Casey Howard, and Jeremy Herzog.

Different companies, different industries, and different team sizes. But the same arc: they hit a wall with their existing tools, found Torq, saw what was possible, and eventually decided they wanted to be part of building it.

Meet the Team That Left Manual Security Behind

Casey Howard, Sales Engineer

Casey has spent his career in security operations, automation, and AI-assisted workflows, building programs focused on what actually moves the needle: speed, clarity, and measurable outcomes. His take: most SOC teams aren’t short on talent or tools — they’re short on connected systems and time. After his team cut MTTR by 90% with Torq in the first month, he came here to make that the norm, not the exception.

Jeremy Herzog, Manager, Solutions Engineering Lab

Jeremy spent eight years at an MSSP, joining as an individual contributor engineer and rising to Director of Engineering — scaling their small enterprise segment from zero to 120 customers and leading implementation, detection engineering, and Tier 2/3 operations. After his team finally got automation off the ground with Torq (and solved problems that had been stuck for six years), he came here to build the environments that help the sales engineering team win deals.

Nate Thompson, Sales Engineer

Nate is a cybersecurity leader with 18+ years of experience transforming security operations at Dana Incorporated, a global Fortune 500 automotive supplier. A founding member of the cybersecurity program, Nate was one of the driving forces behind modernizing the company’s security stack — replacing legacy platforms, building automation and analytics capabilities, and championing the adoption of AI across security operations. As a Sales Engineer for Strategic Accounts at Torq, Nate helps security teams solve the same problems he spent his career living.

Austin Dix, Customer Success Engineer

Austin spent years running a lean SOC in the defense industrial space, where data misclassification carries real legal consequences. His team manually pulled CSVs and uploaded data classification reports to a DLP platform until he found Torq during a second evaluation round and saw what automation could actually do. As a Customer Success Engineer at Torq, Austin now helps lean teams skip the years he spent reinventing the wheel.

How It Started

Every story starts the same way: a security team doing its best with tools that weren’t built for what they actually needed.

Austin was running a five-person SOC in the defense industrial space. His SIEM vendor’s SOAR offering was poorly implemented, and his ticketing platform required an act of Congress to make any changes. The team was manually running data classification reports, pulling CSVs, cross-referencing project lists, and uploading them to a DLP platform. In an industry where misclassified data isn’t just a mistake — it’s a liability — that kind of manual work was untenable.

Nate’s team at an automotive manufacturer was automating with homegrown Python and PowerShell scripts. “While they worked, it was very limited,” he said. “We would have to maintain all of that ourselves.” The team was a skeleton crew — Nate, one or two others, and an engineer who knew Python. That was it.

Casey was managing an MSSP and a legacy case management ticketing module at a financial services company. Three integrations the team wanted, three additional line items. Edge-case integrations? Not possible at all. The team needed bi-directional sync between source systems and case management. Their tooling couldn’t deliver it.

Jeremy was Director of Engineering at an MSSP. His SOC team had tried and failed to implement a SOAR that got rebranded and folded into a larger platform before it even started. “They had it for a year and never really got it off the ground.” The result: an MSSP with limited automation or response capabilities — a distinct disadvantage for winning new business and retaining existing clients.

The Breaking Point

Austin’s breaking point wasn’t technical. It was a vendor who refused to give him a demo. His team had run a formal bake-off, picked a winner, completed a POC, and gotten approval. Then Austin tried to bring in his infrastructure team to buy additional licenses. The vendor said, “No demo until you sign a purchase order.” Austin said, “All right, I’m going to go find somebody else that will.”

Nate’s company got XSOAR added on for free during a renewal cycle, which killed the evaluation they were already running. It helped at first, but they hit a wall fast. “All we really did was give our scripts a pretty interface. We could draw boxes, but if we wanted to do something that wasn’t a box, we had to engage professional services. That took weeks and months.” With a two-person team and a growing backlog, everything froze.

Casey evaluated every major SOAR and automation on the market. Two were eliminated solely due to licensing models — user-based pricing with an MSSP was prohibitive. Another charge per execution run. It came down to Torq and one other vendor.

Jeremy’s SOC team couldn’t get their SOAR working, so leadership handed the project to his engineering group. He evaluated three options. Torq floated to the top.

The Switch to Torq

Austin got introduced to Torq on his second evaluation round, and it was “night and day.” The team automated data classification for their DLP platform and used Torq as a consolidation layer for alerts from across endpoint tools, the SIEM, and identity systems. “This was before case management, so we basically used Torq to recreate case management. It brought everything together for us.”

Nate will never forget opening the Torq interface for the first time. “It was very intuitive. It just clicked.” He converted most of his legacy workflows during the POC alone. “I fell in love with the platform.” When the competing vendor came in for the bake-off, the contrast was immediate: “I sat there and was like, I don’t know which box I’m supposed to drag over. And when you finally drag one over, there are like 12 configuration steps inside.” If he couldn’t figure it out — and this was 80% of his job — his SOC analysts never would.

“I’ll never forget getting into the Torq interface for the first time. It was very intuitive. It just clicked.”
– Nate

Casey’s team chose Torq because it was a security-focused platform built for security operations teams.  The feature that delivered the most impact was the AI-generated case summary — pulling everything into one view so analysts could quickly triage and decide: true positive, escalate, or close.

“AI was an afterthought back then, but once we saw the AI capabilities in Torq, it became where most of our value actually came from.”
– Casey

Jeremy made a bet with his VP of Operations: “I’m putting my credibility on the line — if you buy this product, we will have this implemented in under 30 days.” They signed. They were operational in two weeks. “After that, I just started using Torq to solve all of the problems I’d had for years. Problems I’d been dealing with for six years — Torq let me build workflows to solve in a matter of weeks.”

Favorite Torq Features

Ask any of them what stood out, and it comes back to speed, simplicity, and the ability to make non-engineers productive.

At Austin’s organization, the Torq platform was so accessible that interns were able to build. “We even had interns building automations in the platform, because the no-code interface was that simple.” Nate could go from a use case — a sentence or two — to a production-ready workflow in less than 24 hours. Other teams saw what the SOC was doing and wanted in. He extended Torq into GRC, built just-in-time USB access workflows, and started automating firewall changes for IT operations.

Casey loved the universal connectivity — API calls, webhooks, SSH, AWS, email ingestion. “Being able to connect with everything in any way we wanted to was amazing.” 

After a month on Torq, the team reduced MTTR by about 90%.

Jeremy knocked out years-old problems with project management style and democratized access so more engineers could build. “It just took off from there.” By the time he left, Torq was ingrained in all four of the MSSP’s managed services.

“I democratized it, got more engineers building in the Torq platform. It just took off from there. We saved everybody time. We made everybody’s lives easier.”
– Jeremy 

The Move to Torq

Austin had already left his SOC role and joined a different organization when the Torq team called. He’d told them years earlier: if you ever need anybody, let me know. They took him up on it.

Nate became a Torq evangelist before he became an employee — talking up the platform at events and demoing to other teams. “I wanted it to be for a product I was truly invested in. There are only a handful of those in my career.”

Casey saw the business outcomes from Torq and felt like everyone deserved access. “Being a security analyst and having to do alert triage — it’s mind-numbing. If I can help anyone else not have to do that low-value work, that’s what I wanted to do.”

Jeremy’s motivation started with the people. “This team is hands down the best customer relations team I’ve ever worked with in my career.” But it was also the product. “It was my first foray into automation, and it’s kind of become my native language.”

What They Didn’t Know as Customers

Every one of them says the same thing from the inside: the platform is even further along than they knew as customers.

Nate expected deterministic automation. What he found was that AI capabilities had leaped forward. “To have that as a native part of the platform — I was surprised with how quickly the R&D and product team were able to move forward.” 

Casey didn’t have AI Agents as a customer and was trying to build his own agent workflows through an LLM API. “It was janky, it was so hard to work with. I’ve built so many agents now that I wanted to build when I was a customer, because it’s so easy to do it now.” 

Jeremy says case management was the revelation — far more robust than he expected. And Austin wishes he’d leaned on the Torq community more. “We did a lot of reinventing the wheel that I wish we hadn’t.” 

“Torq is going to make a night and day difference for any security operations team within weeks, if not days.”
– Austin

As for what’s next, they all land on the same two things: Auto Triage and the Agentic Builder.

Austin: “If I was back buying Torq again and Auto Triage was a thing, I would buy it 100 times over.” Nate sees the Agentic Builder collapsing time-to-value: “What I could do in 24 hours, you could almost do in a single meeting.” Casey sees Torq pulling away from the pack: “There are a bunch of AI SOCs now, but they only do alert triage. We can do the full incident lifecycle.” And Jeremy sees the Agentic Builder as the convergence of everything he loves: “The fact that we’re extending that into building workflows is amazing.”

We’re moving fast, and the team is growing. If you want in — we’re hiring.
SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Automating Data Leakage Response: Beyond Traditional DLP

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • Data leakage is the unintentional or malicious exposure of sensitive information, and traditional DLP tools alone leave significant gaps in detection and response.
  • Leakage risks span human error, misconfigurations, insider threats, and sophisticated exfiltration across cloud, email, and endpoint environments.
  • Detection requires cross-system visibility, behavioral anomaly monitoring, and automated enrichment that legacy tools struggle to deliver at scale.
  • The Torq AI SOC Platform automates data leakage detection, triage, and response workflows, cutting alert fatigue and accelerating containment.
  • No-code automation and 300+ out-of-the-box integrations let SOC teams build and deploy leakage response playbooks without engineering overhead.

Data leakage has a way of hiding in plain sight. It shows up in a misconfigured S3 bucket, an employee forwarding sensitive files to a personal email, an overly permissive API, or a third-party integration that quietly exposes more data than it should. By the time a traditional data loss prevention (DLP) tool flags it, the exposure has often been active for hours, days, or longer.

For SOC teams managing complex, multi-cloud environments, fast detection and even faster response both matter. This article covers what data leakage is, the risks it creates, how to detect and prevent it, and how automated workflows transform response from a reactive scramble into a coordinated, autonomous operation.

Understanding Data Leakage

What Is Data Leakage?

Data leakage is the unauthorized or unintentional exposure of sensitive, confidential, or protected information to parties who should not have access to it. It differs from a data breach in an important way: a breach typically involves a deliberate attack by a malicious actor, while leakage often results from human error, misconfiguration, or overly permissive controls that create exposure without anyone intending it.

That distinction matters operationally. Detection and response strategies built around known attack patterns miss the leakage scenarios that originate inside the organization. Information leakage in enterprise environments spans a wide range: sensitive documents shared with the wrong distribution list, API keys embedded in public code repositories, cloud storage buckets left open to the internet, or employee credentials exposed through third-party breaches.

Traditional DLP tools address a portion of this risk by scanning for sensitive data patterns and blocking certain outbound transfers. The coverage gap emerges in the scenarios DLP was not designed for: lateral movement between internal systems, exfiltration through authorized channels, or leakage that occurs at the infrastructure layer rather than the application layer. Closing that gap requires a broader detection strategy and automated response that operates across your full security stack.

Types and Models of Leakage

Data leakage takes several forms depending on the source, the mechanism, and whether the exposure is intentional.

Unintentional leakage accounts for the majority of incidents. Employees misdirect emails, misconfigure cloud storage permissions, or unknowingly install software that exfiltrates data in the background. Misconfigurations in IAM policies, network segmentation, or cloud resource settings create persistent exposure that may go undetected for extended periods.

Malicious insider leakage involves a trusted employee or contractor deliberately exfiltrating sensitive data, often using authorized channels and access that DLP tools are configured to allow. Detection requires behavioral baselines and anomaly monitoring rather than simple policy enforcement.

Third-party and supply chain leakage occurs when vendors, partners, or integrated services handle sensitive data with weaker controls than your own environment enforces. A single over-permissioned API integration can expose more data than a targeted attack.

In machine learning and AI development contexts, model leakage (also called data leakage in ML) refers to a separate but related problem: training data or target information bleeding into model evaluation in ways that inflate performance metrics and produce unreliable models. For security teams building AI-powered detection systems, model leakage undermines the validity of the models they rely on. Rigorous data pipeline controls are an operational security concern and a data science discipline.

Common Risks and Impacts

Data leakage creates risk across three dimensions that matter directly to security architects and operations analysts.

Regulatory exposure is immediate and quantifiable. GDPR, HIPAA, PCI DSS, and CCPA all impose notification requirements and potential penalties when personal or sensitive data is exposed. The timeline from discovery to regulatory notification is often measured in days, and organizations that lack automated detection and evidence collection consistently struggle to meet it. Security incident categories that involve personal data carry the most acute regulatory consequence.

Operational disruption compounds the initial exposure. A leakage event that requires manual investigation across dozens of systems pulls analyst time away from active threats, creates a backlog in the alert queue, and often surfaces secondary findings that extend the response timeline significantly. SOC teams without automated enrichment and triage workflows face a compounding workload effect when leakage events coincide with other active incidents.

Reputational and financial damage follows discovery, whether the organization discovers the leakage internally or learns about it from an external reporter or regulator. The cost of a data breach extends across immediate remediation, customer notification, legal fees, and the longer-term erosion of trust that affects enterprise relationships and sales cycles.

The common factor across all three risk dimensions: speed of detection and response determines the magnitude of impact. Every hour a leakage event goes unaddressed expands the potential exposure.

Detection and Prevention Strategies

Data Leakage Detection Tools and Methods

Effective data leakage detection requires visibility across the full data path: where sensitive data lives, how it moves, who accesses it, and whether that access matches established behavioral patterns.

Traditional DLP tools provide a foundation by scanning outbound traffic and cloud storage for sensitive data patterns like credit card numbers, Social Security numbers, or proprietary document formats. They work well for known data types moving through monitored channels. The detection gaps emerge at the edges: encrypted traffic, authorized channels used for unauthorized transfers, and data that has been transformed to avoid pattern matching.

Advanced SOC detection approaches layer behavioral anomaly monitoring on top of DLP coverage. Rather than matching data patterns, behavioral detection establishes baselines for how users and systems normally interact with sensitive data, then flags deviations. An employee who downloads 10 times their normal weekly volume of files on a Friday afternoon triggers an anomaly alert regardless of whether the files match a DLP signature.

Torq Socrates™, Torq’s agentic SOC orchestrator, brings AI-powered reasoning to data leakage detection. Socrates evaluates alerts across connected systems, correlates signals indicating leakage activity, and autonomously initiates investigation workflows. When an email gateway flags a large outbound attachment, Socrates cross-references the sender’s recent access history, the sensitivity classification of the attached files, and any concurrent anomalies on the same user account. The result is a contextualized, investigation-ready alert rather than a raw signal requiring manual lookup.

Torq’s automated SOC incident response capabilities extend detection into case management: when a leakage event is confirmed, Torq automatically opens a case, assigns it to the appropriate team, and populates it with the full evidence trail gathered during investigation. Analysts arrive at a case that is already enriched and ready for decision-making.

These detection strategies represent a significant improvement over DLP alone, and they share one challenge: without automation, they still require substantial manual effort to operationalize at scale. The next section covers how automated workflows close that gap.

Prevention Best Practices

Prevention operates at several layers simultaneously. The most effective programs combine technical controls, policy enforcement, and automated monitoring into a defense-in-depth posture that addresses both unintentional and malicious leakage vectors.

Access control is the most foundational prevention layer. Applying the principle of least privilege across cloud resources, internal systems, and third-party integrations limits the blast radius when credentials are compromised or an insider acts maliciously. Automated non-human identity security and regular access reviews ensure that permissions reflect current need rather than accumulating over time.

Encryption of sensitive data at rest and in transit ensures that exposure due to misconfiguration or interception does not directly result in readable data loss. Encryption controls work in combination with DLP and behavioral monitoring: they reduce the value of data that leaks, while detection controls reduce the likelihood that leakage occurs undetected.

Proactive workflow automation fills the gaps left by manual processes. Torq Hyperautomation™ continuously monitors connected systems for misconfigurations, permission drift, and anomalous access patterns that precede leakage events. When a cloud storage bucket is created with public access enabled, or when an API key is committed to a code repository, Torq detects the exposure and triggers a remediation workflow immediately, before the window of vulnerability extends.

No-code automation makes these workflows accessible to security architects and operations analysts without requiring custom development. Torq’s drag-and-drop workflow builder lets teams configure, test, and deploy leakage prevention playbooks rapidly and adapt them as environments and threat patterns evolve.

Automating Response to Data Leakage Events

Real-Time Response Workflows

Speed is the defining variable in data leakage response. The difference between a contained incident and a material breach often comes down to whether response actions (access revocation, session termination, data quarantine, stakeholder notification) execute in minutes or hours.

Torq HyperAgents® enable real-time response across email, cloud storage, endpoint, and identity environments simultaneously. HyperAgents is built to execute multi-step response workflows autonomously the moment a leakage event is confirmed: revoking the affected user’s access, quarantining flagged files, capturing a forensic evidence snapshot, notifying the security team, and opening a case management record with full incident context attached.

This response architecture addresses the coordination overhead that slows manual response. Rather than an analyst manually working through a runbook across five different consoles, Torq executes the full response sequence in parallel, with each action logged and auditable. The analyst’s role shifts from execution to oversight and decision-making on the escalated findings that require human judgment.

Agentic AI makes response workflows adaptive. When an investigation surfaces unexpected context, such as a leakage event that appears connected to a broader credential compromise, Socrates dynamically adjusts the response scope, expanding the investigation and response actions to cover the full extent of the incident.

Integrating Across Tools

Data leakage spans every layer of the enterprise environment: email systems, cloud storage, endpoint devices, identity providers, code repositories, SaaS applications, and network infrastructure. Effective detection and response require coordinated action across all of them, which is why point solutions with limited integration coverage consistently leave gaps in detection.

Torq’s Hyperautomation platform provides 300+ out-of-the-box integrations across the security tool ecosystem, including DLP platforms, SIEM, CASB, EDR, IAM, and cloud providers, allowing SOC teams to build unified leakage detection and response workflows without custom API development. When your email security platform, cloud access security broker, and endpoint detection tool all feed into a single automated workflow, correlation happens at machine speed.

Integration depth also reduces vendor sprawl. Teams that consolidate leakage detection and response orchestration through Torq replace point-solution complexity with a single automation layer that connects existing investments rather than adding new tools. That architectural simplicity translates directly into lower maintenance overhead, faster onboarding for new team members, and measurable KPI improvement on detection and response time metrics.

For teams building or expanding their detection coverage, Torq’s agentic coding for SecOps capabilities extend workflow customization further, letting security engineers build and iterate on automation logic rapidly without leaving the Torq environment.

Automate the Gap Between Detection and Containment

Data leakage is too fast, too varied, and too consequential to manage with manual triage and static DLP policies. The organizations that are able to contain leakage events quickly, share one operational characteristic: automated workflows that detect, enrich, and respond across the full data environment without waiting for analyst intervention.

Torq’s AI SOC Platform gives SOC teams the automation layer to close the gap between detection and containment, reduce alert fatigue from leakage-related false positives, and maintain a defensible, auditable response posture across every environment where sensitive data lives.

The AI SOC Apocalypse is underway. Data leakage is exactly the kind of fast-moving, cross-system threat that exposes the limits of manual SOC operations. The organizations closing that gap are doing it with agentic AI and automated response workflows. Torq is the only true AI SOC platform built to detect, investigate, and contain threats like data leakage at machine speed, across every environment where your sensitive data lives.

If your security program still depends on analysts to catch what automation should be stopping, the AI SOC Apocalypse has already started for you.

FAQs

What is data leakage in cybersecurity?

Data leakage is the unintentional or unauthorized exposure of sensitive, confidential, or protected information to parties outside its intended audience. It differs from a deliberate data breach in that leakage often results from human error, misconfiguration, or overly permissive controls rather than an external attack. Common examples include misconfigured cloud storage, misdirected emails containing sensitive attachments, exposed API keys, and over-permissioned third-party integrations. Leakage events can carry the same regulatory and reputational consequences as breaches, making detection and rapid response critical. Learn how Torq automates data leakage incident response workflows.

What are the types of data leakage?

Data leakage falls into three broad categories. Unintentional leakage results from human error or misconfiguration, including misdirected emails, public cloud storage buckets, or credentials committed to code repositories. Malicious insider leakage involves a trusted user deliberately exfiltrating data through authorized channels, often in ways that standard DLP policies allow. Third-party leakage occurs when vendors or integrated services expose data through weaker controls than the organization enforces internally. Each type requires different detection approaches: pattern matching for known data types, behavioral anomaly detection for insider activity, and vendor risk monitoring for supply chain exposure. Explore how security incident categories inform response prioritization across leakage types.

What is information leakage in cybersecurity?

Information leakage in cybersecurity refers broadly to any unintended disclosure of sensitive data, including system configuration details, network topology, application error messages, and personal or business-critical information. At the application layer, information leakage can expose details that attackers use to refine subsequent attacks: stack traces that reveal software versions, verbose error messages that disclose internal path structures, or API responses that return more data than the requesting user should see. At the enterprise level, information leakage encompasses the broader category of data exposure events that create regulatory, operational, and reputational risk.

Does a data leak mean I was hacked?

A data leak and a hack are related but distinct events. A hack involves an external attacker deliberately breaching your systems to steal data. A data leak can occur without any external attack: a misconfigured server, an employee error, or an overly permissive access control can expose sensitive data without any malicious actor involved. That said, data leaks create the conditions that make successful attacks more likely. Exposed credentials, visible system configurations, or accessible sensitive data all lower the cost and complexity of a subsequent targeted attack. Detecting and remediating leakage events promptly reduces both the immediate exposure and the downstream attack surface. See how Torq’s high-security automation workflows support proactive leakage detection and remediation.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

AI Security and Trust: Why SOC Teams Don’t Trust AI

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

92% of security leaders say something is actively reducing their trust in AI within the SOC. These aren’t skeptics, they’re people who have already adopted AI and believe in its ability to enhance security operations. We know from the 2026 AI SOC Leadership Report that AI is already widely adopted in the SOC, with 94% of organizations using it in some capacity. 

And yet, there’s still an AI security and trust gap in the SOC. Why?

Confidence Isn’t the Issue. Deployment Is. 

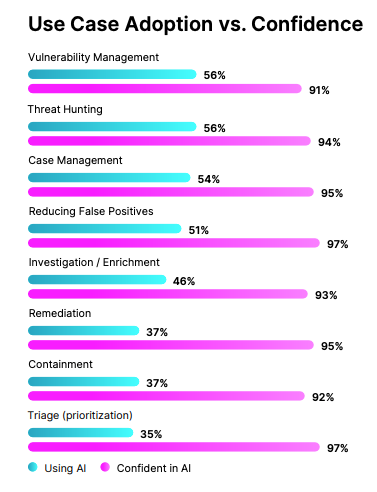
Digging into the data from Torq’s AI SOC Leadership Report, one gap stood out as the most shocking. Across every SOC use case we measured, confidence in AI’s ability to get the job done is nearly universal, ranging from 91% to 97%. CISOs and security leaders aren’t sitting around debating whether AI can handle the work; they know it can. But actual adoption tells a different story.

Vulnerability management and threat hunting lead AI adoption metrics at 56% each. Followed by case management, reducing false positives, investigation, and remediation. What was surprising is that triage is the least deployed AI use case, with only 37% adoption — even though triage is arguably the most obvious fit for AI. SOC teams are overwhelmed with massive amounts of false-positive–riddled alerts, making triage one of the most repetitive and time-consuming tasks analysts face. 

If the use case best suited for AI in the SOC is the one organizations have been slowest to adopt, what does that say?

When we dove deeper into each use case, the responses helped pinpoint exactly what challenges SOC teams were experiencing that led to the adoption vs. confidence gap. The top response for triage was the need for too much human review (34%); for investigation, manual enrichment (32%) and unreliable conclusions (31%) were neck and neck; and for response, the most common answer was lack of trust (33%).  

It’s not a capability problem. It’s a lack of trust in the products themselves. 

What’s Actually Reducing Trust in AI?

When we asked 450 CISOs and security leaders this question, the answers weren’t what you might expect (or maybe they were, given how universal they were). Nobody led with “I’m worried that AI will take my analysts’ jobs” or “I’m not comfortable with the idea of autonomous remediation”. These are the answers other vendors are telling you to have, but the reality is, the top concerns were far more fundamental than that, and included: 

  1. Data privacy concerns: 45%
  2. False negatives (missed threats): 40%
  3. Data governance: 37%
  4. Black-box AI: 32%

Looking at these four top concerns together paints a pretty clear picture. Security leaders aren’t questioning whether or not AI works; they’re asking:

  • What data is AI accessing? 
  • What is AI doing with that data? 
  • Why is AI making the decisions it’s making? 

When we break down the responses by seniority level, the story remains the same. The top concerns surrounding AI in the SOC were:

  • Executives: False negatives 
  • VPs: Data privacy
  • Directors: Black-box AI
  • Senior Managers: Loss of control

These responses aren’t contradictory;they’re all expressions of the same need: visibility and control at every level. 

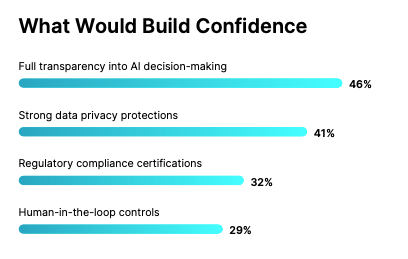
What Would Build Confidence in AI in the SOC? 

We asked what was reducing trust in AI, so it only made sense to ask what would build that confidence too and the answers were just as telling. 

Security teams aren’t looking for less AI; they are looking for more visibility into the AI they already have. They want to understand the planning and reasoning that goes into agentic execution. They want to be able to report to their executives that the AI solutions they’ve invested in are protecting their data and meeting their organization’s unique regulatory and compliance requirements. 

And most importantly, they want to maintain the flexibility of human-in-the-loop control. Not human intervention at every step, but the ability to control and customize where and when human analysts should step in, either as overseer or final decision maker. High-severity incident with a critical system on the line? Humans make the call. Low-severity, high-confidence attack pattern? AI handles end-to-end.

Rearchitecting AI for Security and Trust

90% of security leaders say that explainable AI decisions are critical to a true AI SOC platform. The current gap between confidence and deployment exists because too many AI SOC solutions can’t provide the type of transparency that builds trust. As a result, SOC teams are spending their time double-checking AI decisions, doubling the work, and not realizing the time savings that AI in the SOC was intended for. 

A true AI SOC platform needs to inherently answer the simple questions that SOC teams are asking — what tools is the AI accessing, what data is the AI looking at, and why did the AI reach the conclusion it did? Until those questions have clear, verifiable answers built into the platform architecture, the ceiling on AI expansion in the SOC isn’t the technology. It’s trust. 

What Transparent AI Looks Like

The Torq AI SOC Platform was built with these concerns in mind. We understand the importance of transparency in building trust in human-AI collaboration. Here’s how the Torq AI SOC Platform addresses each one directly. 

Declarative instruction: Torq HyperAgents® work under your explicit direction. You give each agent a role, an objective, behavioral guidelines, and specific instructions. You define the tools that they can use (as broadly as a workflow or as granularly as a single step), the data they can access, and the decisions they are authorized to make. Control is built in from the start, not bolted on as an afterthought. 

AI reasoning and output visibility: Every agentic action is documented in a transparent timeline view that maps the reasoning leading to each execution. Analysts aren’t left guessing why a verdict was reached, or what evidence supports a specific conclusion. The planning, reasoning, and execution are reviewable and structured for human validation — in real time — with manual override always available. 

Immutable audit logs: Every AI decision, action, and reasoning chain is recorded and uneditable. Not just for compliance purposes, but because auditability is what builds trust in AI across the organization. When a CISO asks “What did the AI do, and why?”, the answer is already written, traceable, and defendable.

Human-AI collaboration: Torq Socrates coordinates the full platform, with humans on the loop by design. Response actions can execute completely autonomously for high-volume, high-confidence scenarios or with human-in-the-loop confirmation when severity or business context demands it. Analysts set the boundaries and build in off-ramps for human intervention, while Socrates documents and learns over time. As confidence in AI grows, SOC teams can grant greater autonomy across day-to-day use cases. Trust is earned, after all. 

The Confidence SOC Teams Need

The #1 confidence booster in A isn’t more features or better algorithms — it’s transparency. Show how AI reached its decisions, and teams will trust it more. Give them the ability to dial autonomy based on context, and they’ll grant more of it.  AI security and trust come down to architecture, not marketing. A true AI SOC platform is built for trust from the inside out.

For more on how the Torq AI SOC Platform is the only enterprise-ready AI SOC that security leaders can actually trust, check out the complete blog series below. 

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

How to Choose the Best API Automation Tool for Your Security Team

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • API automation tools handle testing, integration, and orchestration across your security stack — reducing manual work and accelerating response.
  • For SOC teams, the right tools connect every platform in your environment and keep those connections validated and running.
  • Tools like Postman, SoapUI, and Apache JMeter each cover specific testing needs — and the Torq AI SOC Platform ties them into unified, automated security workflows.
  • The next frontier in API automation is agentic AI: systems that test APIs and act on them autonomously to contain threats in real time.

Security teams today manage hundreds of integrations from tools like SIEMs, EDR platforms, ticketing systems, threat intelligence feeds, cloud environments, and more. Every one of those connections runs on APIs. Every API that goes untested, unmonitored, or manually managed is a gap in your security posture.

API automation tools close that gap. They handle testing, orchestration, and integration at a speed and scale that empowers modern SOC teams to stay ahead of threats and operate with real confidence.

This article covers what API automation tools are, why they matter for IT and security operations, how to evaluate the leading options, and how the Torq AI SOC Platform extends API automation into full agentic SOC orchestration.

What Are API Automation Tools?

API automation tools are software platforms or frameworks that automatically execute, validate, monitor, and integrate API-based interactions, without any manual intervention required for each task.

In a traditional IT or development context, that means running automated test suites against endpoints, validating responses, and generating reports. In a security context, it means something more powerful: connecting disparate tools, triggering automated responses to threats, and orchestrating complex multi-step workflows across your entire stack.

API requests form the connective tissue of modern security infrastructure. Every time your SIEM fires an alert, your ticketing system logs an incident, or your threat intelligence platform flags an indicator of compromise, APIs carry that data between systems. Automating how those requests are handled — the testing, validation, routing, and response — transforms a reactive security team into a proactive one.

Software API testing tools generally fall into four categories:

  • Functional testing tools that validate APIs return correct responses under expected conditions
  • Performance testing tools that measure speed, throughput, and behavior under load
  • Security testing tools that probe APIs for vulnerabilities, misconfigurations, and unauthorized access vectors
  • Integration and orchestration platforms that connect APIs across tools and automate end-to-end workflows

Security teams need all four and increasingly, they need them unified under a single automation layer.

Key Benefits of Using API Automation in Security Workflows

Improved Efficiency and Scalability

Manual API management doesn’t scale. A growing enterprise SOC can easily manage 50 to 100+ integrated tools, each exposing dozens of API endpoints. Testing and monitoring those connections by hand consumes engineering hours that should be spent on higher-value security work.

API automation tools let teams scale testing and monitoring across every integration simultaneously. When you add a new tool to your stack, automated security workflows validate its API connections, check for expected behavior, and flag anomalies — all without analyst intervention. That scalability compounds over time: the larger your stack grows, the more value automation delivers.

Enhanced Accuracy and Reduced Risk

Misconfigured API endpoints are a real and underappreciated attack surface. An overly permissive authentication scope or an untested edge case in an API response can create vulnerabilities that go undetected for months. Automated testing catches those issues at the point of integration, before they reach production.

Automated testing also reduces alert fatigue from false positives. When your incident response automation relies on clean, validated API data, analysts spend time on genuine threats instead of chasing noise. Consistent, repeatable test execution means the same checks run every time, with full coverage and reliable results.

Faster Integration and Deployment

Security teams operate in a vendor ecosystem that never stops changing. New tools enter the stack, existing tools release API updates, and threat landscapes shift in ways that demand rapid workflow adjustments. API automation tools accelerate that cycle by automatically handling integration validation.

When your automation layer can test a new integration and confirm it’s working correctly in minutes, your team stays agile. Connecting tools to your security stack becomes a low-friction process, and your workflows update in real time as your environment evolves.

API Automation With Torq AI SOC Platform

The Torq AI SOC Platform approaches API automation from a security operations perspective. Torq Socrates™, Torq’s agentic SOC orchestrator, builds, monitors, and maintains API integrations across any security solution, using these API connections to orchestrate workflows across your entire security stack — SIEM, EDR, ticketing, threat intelligence, and beyond. 

Torq Socrates’ Agentic Builder lets analysts use natural language to build and modify API-driven Torq HyperAgents® without engineering support.Rather than validating whether an API works, Torq uses APIs as the foundation for automated security work. When an alert fires, Torq HyperAgents autonomously gather context from multiple API sources, evaluate the threat, and execute a response — without waiting for analyst intervention. Torq HyperAgents are built to handle the speed and complexity that modern SOC environments demand.

Torq Socrates goes further by reasoning across API-connected data sources to make intelligent decisions about alert triage, investigation priority, and response actions. Socrates adapts to the specifics of each incident — pulling data from the right APIs at the right time — rather than following a fixed playbook.

Torq Hyperautomation™ is the engine that powers containment, remediation, and response action through API driven flows. By leveraging the vast network of APIs, Torq provides security teams with a full AI-driven SOC orchestration platform — covering end-to-end threat detection and response, from integration validation to autonomous action.

How to Implement API Automation in Your Security Operations

Moving from manual API management to full automation is a process. These five steps give security teams a structured path forward.

1. Audit Your Current Integrations

Start with a complete inventory of every API connection in your security stack. Map which tools connect to which, what data they exchange, and how those connections are currently tested and monitored. This audit surfaces gaps — integrations without test coverage, endpoints that haven’t been validated recently, and connections carrying sensitive data without proper authentication controls. Your incident response plan is a useful reference for identifying which integrations are most critical to your response workflows.

2. Define Your Automation Objectives

API automation can serve several goals: reducing manual testing effort, accelerating incident response, improving integration reliability, or enabling agentic AI workflows. Prioritize based on where your team spends the most time and where failures carry the most impact. SOC teams typically find the highest immediate value in automating alert enrichment and incident triage workflows.

3. Select Tools Matched to Your Use Cases

Match tools to objectives using the framework above. Pure testing needs fit tools like Postman, SoapUI, or JMeter. Orchestration and workflow automation across your full security stack calls for a platform like Torq. Many teams run both layers: testing frameworks for integration validation, and an orchestration platform for operational automation. Explore Torq’s integration library to see how your existing stack maps to available connectors.

4. Build and Test Incrementally

Start with two or three high-priority integrations rather than attempting to automate everything at once. Build your first automated workflows, validate their outputs against expected behavior, and refine before expanding. Automated SOC incident response workflows benefit from this incremental approach — test each step before connecting them end-to-end.

5. Measure and Iterate

Define success metrics before you go live: mean time to detect, mean time to respond, analyst hours saved, and false positive rate. Measure against those baselines after implementation and use the data to guide the next round of automation. API automation compounds in value over time — each new automated workflow frees capacity for the next one. Check out Torq’s guide to security incident categories to help prioritize which response workflows to automate first.

Your Security Stack Deserves Better Than Manual

API automation tools are foundational infrastructure for modern security operations. They eliminate the manual overhead of managing hundreds of integrations, accelerate testing and deployment cycles, and enable the real-time orchestration that today’s threat landscape demands.

The right stack combines purpose-built testing frameworks for integration validation with a full orchestration platform for operational automation. The Torq AI SOC Platform brings both together — giving security teams the connectivity to link every tool in their stack and the agentic AI capabilities to act on what those connections reveal.

The AI SOC Apocalypse is already here. Security teams that automate their API workflows, integrate their toolchains, and deploy agentic AI are ahead. 

Are you ready to see what’s reshaping how enterprise security leaders think about AI, automation, and the future of the SOC?

FAQs

Does API testing need coding?

Modern API testing platforms are built for accessibility. Tools like Torq’s agentic workflow builder let security analysts build and run API tests and automation without writing code. Torq’s customizable automation and workflow builder makes API-driven workflow building available to analysts at every technical level.

What are the two types of API testing?

The two primary categories are functional testing — validating that an API returns correct responses under expected conditions — and non-functional testing, which covers performance, security, and reliability. Security testing of APIs (checking authentication, authorization, input validation, and vulnerability exposure) falls under non-functional testing and is especially critical for SOC teams managing complex integrations.

Is API testing the same as automation testing?

API testing and automation testing are related but distinct. API testing specifically validates the behavior of API endpoints. Automation testing is a broader category — it means using software to execute tests automatically rather than manually. API automation testing is the intersection: using automated tools to run API tests without manual execution. In a security context, API automation extends beyond testing to include orchestrating workflows and triggering automated responses across integrated tools.

How do I choose an API testing tool?

Start by identifying your primary use case: functional testing, performance testing, security scanning, or full workflow orchestration. Evaluate tools against your team’s technical skill level (some require coding, others offer low-code interfaces), your integration requirements, and your scalability needs. For security teams, look for tools that connect with your existing SOC stack and support the automated incident response workflows your analysts depend on. A platform like Torq addresses the orchestration layer that pure testing tools don’t cover.

What are examples of API-based automation in security?

Common examples include automated alert enrichment (pulling threat intelligence data via API when an alert fires), automated ticket creation in systems like Jira or ServiceNow when incidents are detected, automated containment actions (isolating endpoints or blocking IPs via EDR APIs), and automated case management. Torq’s case management capabilities and HyperAgents execute these workflows autonomously, reducing mean time to respond across the full security incident lifecycle.

What is the role of agentic AI in API automation for security?

Agentic AI takes API automation from rule-based execution to intelligent, adaptive response. Rather than following a fixed script, an agentic AI SOC platform like Torq — powered by Socrates, Torq’s agentic SOC orchestrator — reasons across API-connected data sources in real time, decides which actions to take based on the specifics of each incident, and executes multi-step response workflows autonomously. This is where modern AI SOC platforms are headed: APIs as the foundation, agentic AI as the decision layer on top.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

SOC Automation Framework: How Agentic AI Powers the AI SOC

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • Agentic AI is the engine that powers every stage of the threat lifecycle from triage to resolution.
  • A five-step AI SOC automation framework gives SOC directors a practical, structured path to faster, smarter security operations.
  • Customers running on the Torq AI SOC Platform have seen 100% of Tier 1 cases auto-triaged (Carvana) and phishing responses drop from hours to minutes (Lennar Corp).
  • Academic research published in April 2026 independently validated this same architectural direction — agentic detection, enrichment, and resolution — confirming what leading SOCs are already running in production.

The best SOCs in 2026 resolve alerts before most teams have finished triage. Agentic AI makes that possible — handling the full threat lifecycle with transparent reasoning and documented action at every step, so analysts spend their time on the work that actually requires human judgment.

The Torq AI SOC Platform was built around exactly this architecture. Results from customers like Carvana and Lennar Corp show what it looks like in production.

What’s Driving the Shift Toward AI SOC Automation

SOC teams have more tools than ever. That’s part of the challenge. According to the 2026 AI SOC Leadership Report, 80% of security leaders say their SOC is still fragmented across too many platforms, which means analysts carry the burden of connecting context that the toolstack never hands them in one place.

Three forces are accelerating the need for a smarter SOC automation framework:

  • Threat volume has outpaced manual triage capacity. The alerts keep coming faster than any human team can process them at the pace attackers now operate.
  • Tool fragmentation places the burden of context on the analyst. When detection lives in one platform, enrichment in another, and response in a third, speed is the first casualty.
  • Agentic AI has matured to the point where it can handle reasoning and action — not just scripting. This is the shift that makes a true AI SOC automation framework possible.

Independent research is catching up to where leading SOCs already operate. In April 2026, researchers Md Hasan Saju and Akramul Azim published “Toward Autonomous SOC Operations”, a peer-reviewed framework for automating SOC operations that reduced average incident triage time from hours to under ten minutes using ensemble detection, retrieval-augmented investigation, and grounded automated resolution. The architecture the paper describes maps directly to what the Torq AI SOC Platform delivers.

What the Research Gets Right and What Real-World SOCs Still Need

The Saju and Azim paper achieved strong results under lab conditions:

  • 82.8% detection accuracy with a 0.120 false positive rate
  • Resolution code prediction accuracy improved from 78.3% to 90.0% with evidence-grounded reasoning
  • Average incident triage time reduced from hours to under 10 minutes

These numbers validate the architectural direction: ensemble detection, automated enrichment, and grounded resolution all belong in a modern SOC automation framework. What the research doesn’t address is what deployments actually require — integration breadth across thousands of tools, multi-tenant case management, compliance evidence packaging, transparent agentic reasoning that analysts can audit, and continuous learning that improves accuracy over time. That’s what the five-step framework below is built around.

A Practical AI SOC Automation Framework Powered by Agentic AI

The five-step AI SOC automation framework is a structured, repeatable approach to building SOC automation that actually closes cases rather than one that just moves alerts from one queue to another. Each step maps to a phase of the threat lifecycle, and each one is anchored by agentic AI working transparently alongside your team.

1. Ingest Detection Signals Across Every Layer of the Stack

Effective SOC automation starts with coverage. Endpoint, network, identity, cloud, email, and threat intelligence all need to feed into a single system — because gaps in ingestion mean gaps in detection. A framework that only sees part of the stack will only automate part of the problem. The more signal sources unified in one place, the more context an AI system has to make accurate decisions downstream. The Torq AI SOC Platform connects across 1,000+ native integrations, giving every subsequent step the full picture from the start.

2. Apply Agentic Triage With Transparent Reasoning

Not every alert is a threat. The triage layer needs to separate real incidents from noise — fast, at scale, and without burying critical signals under false positives. The strongest triage systems apply business context, known activity history, and threat intelligence together to produce a verdict that an analyst can actually trust and act on. Explainability matters here: if the system can’t show its work, the analyst can’t verify it. Torq Auto Triage does exactly this — an agentic engine that delivers verdicts with full reasoning surfaced at every step.

3. Auto-Enrich the Case With Grounded Evidence

Once a real threat surfaces, the investigation should move immediately, without waiting for an analyst to manually pull context from multiple tools. The system should automatically gather the evidence needed to understand scope: querying threat intelligence sources, cross-referencing internal activity, and assembling a complete picture before a human ever opens the case. The sooner the evidence package is ready, the sooner the right decision is made. Torq HyperAgents® handle this enrichment layer, with specialized AI Agents that investigate and gather context across the full threat lifecycle — transparently and with full visibility into every action taken.

4. Resolve or Escalate With Documented Reasoning

Resolution is where most SOC automation frameworks leave room to grow. Getting to a verdict is one thing; taking the right action — or knowing when to hand off to a human — requires reasoning that’s both accurate and auditable. The system needs to surface what it found, what it recommends, and why, so the analyst reviewing it can approve with confidence. Escalations should carry full context, not just a ticket number. Torq Socrates™, Torq’s agentic SOC orchestrator, coordinates HyperAgents, generates a structured plan for analyst review, and executes only what’s been approved — keeping the human in the loop at every decision point that matters.

5. Close the Loop With Audit Trails and Continuous Learning

A framework that stops at resolution leaves the hardest operational problems unsolved. Production SOCs need every action logged for compliance (PCI DSS, SOX, GDPR), feedback mechanisms that improve accuracy over time, and case management that connects related incidents into a coherent picture. This is also where the business case gets built — the data that shows the board what automation is actually delivering. Torq Case Management and Torq Hyperautomation™ close this loop natively, packaging audit trails, linking related cases, and continuously tuning the system based on analyst feedback and resolved outcomes.

Step 5 is where deployments diverge from research frameworks. Lab results show what’s achievable. Compliance packaging, multi-tenant case management, and a system that gets smarter over time — that’s what makes automation sustainable at scale.

Real-World Outcomes From an Agentic AI SOC 

Torq customers are running the AI SOC today and the outcomes reflect what happens when agentic AI is applied across every step of the threat lifecycle.

Carvana: 100% of Tier 1 and Tier 2 cases are auto-triaged by the Torq AI SOC Platform. 

Lennar Corp: Phishing response dropped from hours to minutes after consolidating workflows on Torq. 

The research describes what’s possible. These outcomes prove it has been operational at scale and in production with real organizations.

A Five-Step Checklist for Evaluating Your SOC Automation Today

Use this checklist to assess where your current SOC automation stands against the framework:

  1. Audit detection signal coverage across endpoint, network, identity, cloud, email, and threat intelligence
  2. Confirm agentic triage capability — does business context, activity history, and threat intelligence apply together to every alert?
  3. Map automated enrichment paths — what percentage of cases receive full evidence packages without analyst effort?
  4. Evaluate resolution decision support — does the system surface verdicts with documented reasoning that the analyst can review and approve?
  5. Verify audit trails and feedback loops — does every action log for compliance, and does the system improve accuracy over time?

If the answer is “uncertain” on more than two of these, your SOC has the gaps that this AI SOC automation framework is designed to help close.

The Future is an Agentic AI SOC

The 2026 AI SOC Leadership Report covers how 450 security leaders are building toward AI SOC automation at scale — the tools they’re using, the outcomes they’re measuring, and the decisions that separate the leading SOCs from the rest.

Want the Data Behind AI SOC Automation?

FAQs

What is SOC automation?

SOC automation is the use of agentic AI and workflow orchestration to detect, investigate, and respond to security threats across an organization’s full technology stack — without relying on manual analyst effort for every step. Modern SOC automation goes beyond running scripted playbooks; it uses agentic AI that reasons and acts across the threat lifecycle, unified case management, and cross-stack orchestration that closes cases — not just moves them.

What does an AI SOC automation framework look like in practice?

An AI SOC automation framework ingests alerts from across the stack, applies agentic triage to determine severity with transparent reasoning, auto-enriches the case with grounded evidence from threat intelligence and internal sources, resolves or escalates with documented reasoning, and closes the loop with audit trails and continuous learning.

How does automation improve SOC efficiency?

Automation improves SOC efficiency by eliminating manual handoffs between detection, investigation, and response. Data shows the impact at scale: Carvana auto-triages 100% of Tier 1 and Tier 2 cases. Lennar Corp cut phishing response from hours to minutes.

What are the main challenges in security operations today?

The three biggest challenges in security operations today are tool fragmentation (80% of security leaders say their SOC is split across too many platforms), alert volume that exceeds manual triage capacity, and the difficulty of grounding AI outputs in trustworthy, auditable evidence.

How does agentic AI handle complex SOC investigations?

Agentic AI handles complex SOC investigations through a plan-and-execute model. Torq Socrates™, Torq’s agentic SOC orchestrator, reads the case, coordinates specialized HyperAgents® to gather evidence and assess scope, generates a structured plan the analyst reviews, and executes only the approved actions — with full audit trails at every step. The result is agentic reasoning with human oversight at the decision points that matter.

What makes an AI SOC platform different from legacy security automation tools?

Legacy security automation tools execute predefined playbooks against known conditions. An AI SOC platform like Torq applies agentic AI that reasons across novel scenarios, adapts to new threat patterns, and takes action across the full threat lifecycle — from auto triage through case closure — with transparency at every step. For teams looking to go deeper on how Hyperautomation™ powers this approach, the Torq platform combines agentic AI with an enterprise-grade automation engine purpose-built for security operations teams.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Cloud Security Architecture: How to Design and Implement a Multi-Cloud Security Strategy

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • Cloud security architecture is the framework of policies, controls, and technologies that protect data, applications, and infrastructure across cloud environments
  • Multi-cloud adoption is accelerating; 87% of organizations run multi-cloud
  • The five pillars of modern cloud security architecture: identity and access management, network security, data protection, workload security, and continuous monitoring
  • Manual cloud security processes present opportunities for automation to reduce bottlenecks, alert fatigue, and response delays
  • Torq AI SOC Platform enables 75% faster alert processing, 90% duplicate alert reduction, and 60% faster cross-cloud MTTR

Cloud environments expand faster than security teams can protect them. Every new workload, every configuration change, and every API endpoint creates potential exposure. With organizations now operating across AWS, Azure, GCP, and hybrid environments simultaneously, the attack surface multiplies while visibility fragments.

This is the reality of modern cloud security architecture: complexity at scale, threats at machine speed, and security teams stretched thin trying to maintain consistent protection across distributed infrastructure.

This guide breaks down what cloud security architecture means in 2026, the core components every organization needs, the challenges that create opportunities for improvement in multi-cloud security strategies, and how AI-driven automation transforms cloud security operations into proactive defense.

What is Cloud Security Architecture?

Cloud security architecture is the comprehensive framework of policies, controls, technologies, and processes that protect cloud-based systems, data, and infrastructure. It defines how security integrates across every layer of your cloud environment, from identity and access management to network segmentation to data encryption to threat detection and response.

A well-designed cloud security architecture accomplishes three things:

  1. Protects assets: Safeguards data, applications, and infrastructure from unauthorized access, breaches, and attacks
  2. Enables compliance: Maintains adherence to regulatory requirements like SOC 2, PCI DSS, HIPAA, and GDPR across cloud platforms
  3. Supports business velocity: Allows development teams to move fast while managing risk appropriately

Cloud security architecture differs fundamentally from traditional on-premises security. Static perimeters dissolve. Workloads spin up and down in seconds. Data flows across regions and providers. Every cloud platform, whether AWS, Azure, or GCP, implements security controls differently, creating opportunities for unified approaches.

Five Pillars of Modern Cloud Security Architecture

Effective cloud security architecture rests on five interconnected pillars. Strength in each one builds a resilient security posture across the entire environment.

1. Identity and Access Management (IAM)

Identity is the new perimeter. In cloud environments, every access request, whether human or machine, requires verification. Strong IAM architecture includes:

  • Zero trust principles: Verify every access request regardless of source
  • Least privilege access: Grant minimum permissions required for each role
  • Just-in-time (JIT) access: Provide temporary elevated permissions only when needed
  • Multi-factor authentication (MFA): Require multiple verification factors for sensitive resources
  • Service account governance: Monitor and control machine-to-machine authentication

Identity threat detection and response becomes critical as organizations strengthen defenses against credential-based attacks.

2. Network Security

Cloud network security extends beyond traditional firewalls to encompass:

  • Micro-segmentation: Isolate workloads and limit lateral movement
  • Virtual private clouds (VPCs): Create logically isolated network sections
  • Security groups and network ACLs: Control inbound and outbound traffic
  • Web application firewalls (WAFs): Protect applications from common exploits
  • DDoS protection: Mitigate volumetric and application-layer attacks

3. Data Protection

Data protection in cloud environments requires encryption at rest and in transit, plus robust access controls:

  • Encryption management: Implement consistent encryption across cloud platforms
  • Key management: Maintain secure, auditable key lifecycle management
  • Data classification: Identify and protect sensitive data based on classification
  • Data loss prevention (DLP): Monitor and prevent unauthorized data exfiltration
  • Backup and recovery: Ensure data resilience across regions and providers

4. Workload Security

Protecting cloud workloads, including VMs, containers, and serverless functions, requires:

  • Cloud Security Posture Management (CSPM): Continuously monitor for misconfigurations
  • Cloud Workload Protection Platforms (CWPP): Secure runtime environments
  • Container security: Protect Kubernetes clusters and container images
  • Serverless security: Monitor and secure function-as-a-service deployments
  • Infrastructure as Code (IaC) scanning: Catch vulnerabilities before deployment

5. Continuous Monitoring and Response

Security visibility across cloud environments demands:

  • Centralized logging: Aggregate logs from all cloud platforms and services
  • Security Information and Event Management (SIEM): Correlate events and detect threats
  • Cloud-native detection: Leverage AWS GuardDuty, Microsoft Sentinel, GCP Security Command Center
  • Automated response: Orchestrate containment and remediation at machine speed
  • Compliance monitoring: Continuously verify adherence to security policies

Cloud Security Architecture Challenges

Building and maintaining cloud security architecture across multi-cloud environments is hard, and most of that difficulty is exactly what automation and unified tooling are built to solve.

Consolidating Alerts Across Clouds

Security alerts arrive from AWS Security Hub, MicrosoftSentinel, Google Cloud Security Command Center, and third-party tools. Each has unique formats, severity scales, and contextual data structures. This creates an opportunity for unified platforms that normalize and correlate alerts automatically.

Organizations operating in multi-cloud environments can achieve 75% faster alert processing with centralized correlation.

Improving Cross-Cloud Visibility

Multi-stage attacks can span AWS EC2, Azure VMs, and GCP instances. Unified correlation across cloud boundaries enables security teams to detect these attack patterns and respond comprehensively.

Accelerating Triage Through Automation

SOC teams invest significant time manually enriching alerts, correlating events, and determining response actions. Automation accelerates these processes, reduces analyst burnout, and enables faster threat response through automated SOC incident response.

Addressing Configuration Drift

Cloud misconfigurations are one of the most common causes of cloud breaches. Security groups, storage bucket permissions, and IAM configurations benefit from continuous monitoring and automated remediation across multi-cloud environments.

Streamlining Compliance

Maintaining compliance across multiple cloud platforms requires continuous monitoring, documentation, and remediation. Automation transforms compliance from a manual burden into a continuous, auditable process.

How Automation Transforms Cloud Security Architecture

Automation addresses manual process challenges and enables security teams to operate at the speed of cloud infrastructure. Cloud-native security automation delivers these capabilities:

Unified Multi-Cloud Alert Management

Modern cloud security architectures benefit from platforms that automatically ingest, normalize, and correlate security alerts from disparate cloud-native security tools. This provides centralized visibility and intelligent triage across your entire multi-cloud infrastructure.

Key capabilities include:

  • Real-time alert ingestion from AWS Security Hub, Microsoft Sentinel, GCP Security Command Center, and any of the cloud security tools in your stack.
  • Cross-platform correlation that reconstructs attack timelines across cloud boundaries.
  • Automatic deduplication that eliminates redundant alerts and reduces noise.
  • Normalized severity scoring that enables consistent prioritization regardless of source.

Automated Threat Response

Cloud-native response automation triggers coordinated containment actions across AWS, Azure, and GCP simultaneously:

  • Security group modifications
  • VM isolation
  • IAM policy enforcement
  • Cross-cloud network segmentation
  • Evidence collection and preservation

Continuous Compliance Automation

Automated compliance monitoring detects drift, generates audit-ready documentation, and implements corrective controls. This maintains adherence to SOC 2, PCI DSS, GDPR, HIPAA, and other frameworks across multi-cloud environments.

Torq for Cloud Security Operations

Torq for Cloud & AppSec teams delivers the automation layer that modern cloud security architecture requires. The Torq AI SOC Platform connects to major cloud platforms, container orchestrators, SIEMs, and application security tools, achieving complete visibility across hybrid and multi-cloud environments.

Torq helps enterprises detect and respond to security events at scale, instantly and precisely.

Multi-Cloud Event Ingestion

Torq connects to AWS, Azure, GCP, Kubernetes, Docker, and 300+ security tools using native APIs, webhooks, and streaming integrations. This eliminates visibility gaps and enables comprehensive threat detection.

Intelligent Alert Correlation

Cloud security events are correlated across infrastructure layers, from IaaS misconfigurations to container vulnerabilities to application-level threats. Torq Socrates™, Torq’s agentic SOC orchestrator, contextually enriches alerts, grouping them by resource and application for complete incident context.

Automated Remediation

Torq HyperAgents® enable security teams to remediate threats in minutes. SOC analysts can assign incidents for autonomous remediation or collaborate in natural language for complex scenarios requiring human oversight.

Agentic Workflow Building

The Torq Agentic Builder empowers security teams to create and modify automation workflows using natural language, accelerating time to value and enabling continuous improvement of cloud security processes.

Measurable Results

Organizations using Torq for multi-cloud security operations achieve:

  • 75% faster alert processing
  • 90% duplicate alert reduction
  • 60% faster cross-cloud MTTR

Building Your Cloud Security Architecture: Key Considerations

When designing or modernizing your cloud security architecture, prioritize these elements:

  • Start with visibility: You cannot secure what you cannot see. Ensure comprehensive logging and monitoring across all cloud platforms, services, and workloads before implementing advanced controls.
  • Embrace automation early: Manual security processes create technical debt that compounds over time. Integrate automation into your cloud security architecture from the start, particularly for alert triage, enrichment, and routine response actions. Explore security automation workflow tools to accelerate your journey.
  • Design for multi-cloud reality: Even if you primarily use a single cloud provider today, architect for multi-cloud flexibility. Avoid vendor-specific implementations that create lock-in and limit future options.
  • Integrate security into DevOps: Cloud security architecture succeeds when security integrates into CI/CD pipelines, infrastructure as code, and development workflows. Agentic coding for SecOps enables security teams to build and modify automations at the speed of development.
  • Measure what matters: Track metrics that demonstrate security effectiveness: mean time to detect (MTTD), mean time to respond (MTTR), alert-to-case ratio, and compliance posture over time.

Cloud Security Architecture is a Continuous Process

Cloud environments evolve constantly. New services launch, workloads scale, attack techniques advance. Cloud security architecture requires continuous assessment, adaptation, and improvement.

The organizations that succeed treat cloud security as an ongoing operational discipline, powered by automation that scales with their infrastructure. 

The AI SOC Apocalypse manifesto explores how leading organizations are transforming their security operations for this new reality. 

Ready to modernize your cloud security architecture? 

FAQs

What is cloud security architecture?

Cloud security architecture is the comprehensive framework of policies, controls, technologies, and processes that protect cloud-based systems, data, and infrastructure across public, private, and hybrid cloud environments. Learn more about how security operations teams implement these frameworks.

What are the five pillars of cloud security architecture?

The five pillars are: identity and access management (IAM), network security, data protection, workload security, and continuous monitoring and response. Each pillar addresses critical aspects of protecting cloud environments and benefits from incident response automation.

How does multi-cloud security differ from single-cloud security?

Multi-cloud security requires unified visibility, correlation, and response across different cloud platforms (AWS, Azure, GCP), each with unique security controls, alert formats, and APIs. This complexity creates opportunities for automation to maintain consistent protection through multi-cloud security operations.

What is the biggest opportunity in cloud security architecture?

Alert fragmentation and cross-cloud correlation represent the biggest opportunities for improvement. Unified platforms that correlate security events across multiple consoles enable detection of multi-stage attacks that span cloud boundaries.

How does automation improve cloud security architecture?

Automation enables unified alert correlation across clouds, accelerates triage processes, speeds threat response, maintains continuous compliance, and scales security operations alongside infrastructure growth. The Torq AI SOC Platform delivers these capabilities.

What is cloud security posture management (CSPM)?

CSPM continuously monitors cloud environments for misconfigurations, compliance violations, and security risks. It identifies issues like publicly exposed storage buckets, excessive permissions, and unencrypted data, enabling proactive cloud misconfiguration detection and remediation.

How do you secure a multi-cloud environment?

Securing multi-cloud environments requires centralized visibility, consistent security policies across platforms, automated threat detection and response, continuous compliance monitoring, and unified identity management. Cloud-native security automation accelerates these capabilities.

What is an incident response plan for cloud security?

An incident response plan defines the processes, roles, and procedures for detecting, responding to, and recovering from security incidents in cloud environments. Automation enhances these plans by enabling faster, more consistent response actions.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Container Security at Scale: Automating Cloud Container Threat Response

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • Container security protects containerized applications across their full lifecycle, from image build through runtime in production.
  • Key risks include misconfigurations, supply chain vulnerabilities, privilege escalation, and ephemeral workload blind spots.
  • Compliance frameworks like PCI DSS, HIPAA, and GDPR apply directly to containerized environments and require continuous enforcement.
  • Container security tools like Aqua and Prisma Cloud deliver strong detection, and pairing them with automated orchestration multiplies their impact.
  • The Torq AI SOC Platform connects your container security stack, automates triage-to-remediation workflows, and keeps your SOC operating at cloud scale.

Containers redefined how enterprises build, ship, and run software. They’re fast, portable, and purpose-built for cloud-native environments. For SOC teams, that speed and scale bring a new class of security demands that call for equally modern defenses.

Managing hundreds of containerized workloads across dynamic, ephemeral environments means the attack surface shifts constantly. Alerts stack up, compliance requirements stay demanding, and the window between detection and response needs to shrink. The teams winning at this are the ones that have automated the hardest parts.

What Is Container Security?

Container security is the practice of protecting containerized applications and their underlying infrastructure from threats and vulnerabilities throughout their full lifecycle, from development through deployment and into runtime. It brings together strategies, tools, and policies designed to minimize risk across containerized environments at every stage.

Containers differ fundamentally from traditional virtual machines. They share a host OS kernel, spin up in seconds, and scale on demand. That agility powers modern application delivery and requires security controls that move just as fast. A vulnerability in a container image, a misconfigured network policy, or a runtime anomaly can propagate across your environment before manual review catches it.

Cloud container security requires visibility that spans the full container lifecycle, from the moment an image is built to every second it runs in production.

Core Components of Container Security

A strong container security posture rests on several interconnected pillars. Each one addresses a distinct layer of risk, and SOC teams in cloud-native environments need all of them working together.

Image Security: Every container starts as an image. Scanning images for known vulnerabilities, malware, and misconfigurations before they reach production is the first line of defense. This includes verifying base images, auditing dependencies, and enforcing policies on what images are permitted to run.

Runtime Protection: Once a container is live, runtime security monitors for anomalous behavior, such as unexpected process execution, privilege escalation attempts, and unusual network connections. Runtime protection catches active threats and behavioral anomalies that emerge after deployment.

Container Network Security: Containers communicate constantly across your environment. Enforcing least-privilege network policies, segmenting workloads, and monitoring east-west traffic keep lateral movement contained if a workload is compromised.

Secrets and Access Management: Hardcoded credentials and improperly managed secrets rank among the most common and most exploitable container vulnerabilities. Proper secrets management using dedicated vaults and automatic credential rotation closes this gap at the source.

Compliance and Policy Enforcement: Containers running in regulated industries must continuously meet specific standards. Automated policy enforcement keeps your environment compliant even as workloads scale and configurations evolve.

Key Security Challenges in Container Environments

Container environments create distinct risk patterns that SOC teams need to plan for proactively.

  • Misconfigurations: Containers deployed with overly permissive settings, exposed ports, or unnecessary privileges create exploitable gaps. Automated configuration enforcement is what keeps pace with deployment velocity at scale.
  • Supply chain vulnerabilities: Modern applications depend on dozens of third-party components. A vulnerability introduced upstream in a base image or open-source library can affect every container built on top of it.
  • Privilege escalation: Containers running as root or with excessive capabilities give attackers a path to break out of the container and reach the host system. Enforcing least privilege at runtime closes this attack vector.
  • Inter-container ntwork threats: Proper network segmentation limits what a compromised container can reach. Enforcing strict traffic policies between workloads contains lateral movement before it spreads.
  • Ephemeral workload visibility: Containers often live for seconds or minutes. SOC teams need logging and monitoring tools purpose-built for short-lived workloads to maintain full visibility across ephemeral activity.

Common Risks, Compliance, and Operational Impact

Container vulnerabilities create more than security risks. They create operational and business risk too. A single misconfigured container can expose sensitive data, cause service outages, or trigger a compliance violation with material regulatory consequences.

For SOC teams, the challenge is scale. Managing container security monitoring across hundreds or thousands of containers, spanning multiple cloud environments, while keeping pace with alerts from across your full tool stack — that’s where automation creates the biggest operational lift, turning high-volume manual processes into manageable, repeatable workflows.

Container Compliance Requirements

Organizations running containerized workloads in regulated industries face direct compliance obligations. Meeting them manually, across environments that change constantly, creates significant operational burden.

  • PCI DSS requires strict controls around cardholder data, including network segmentation, access controls, and continuous monitoring of payment-processing systems.
  • HIPAA mandates safeguards for protected health information, including audit logging, access controls, and documented incident detection and response capabilities.
  • GDPR requires organizations to protect personal data and demonstrate the ability to identify and report breaches within defined timeframes.
  • SOC 2 evaluates controls across security, availability, and confidentiality, all directly relevant to containerized environments.

Automation transforms compliance from a reactive, periodic effort into a continuous, built-in output. Every response gets logged, very policy gets enforced and every audit trail builds itself.

7 Best Practices for Container Security

Securing containers means building security into every stage of the lifecycle, proactively, and with enough automation to keep pace with cloud-native deployment speeds.

  1. Shift security left: Integrate image scanning and policy checks into your CI/CD pipeline. Addressing vulnerabilities before deployment reduces risk and remediation cost downstream.
  2. Enforce least privilege: Run containers with the minimum permissions required. Drop unnecessary Linux capabilities, avoid running as root, and use read-only file systems wherever feasible.
  3. Implement network segmentation: Define and enforce network policies that limit container-to-container communication to only what the application requires. Tight segmentation limits blast radius when a workload is compromised.
  4. Manage secrets properly: Use a dedicated secrets manager. Credentials hardcoded in container images or passed as plain-text environment variables are an avoidable exposure.
  5. Monitor runtime behavior continuously: Static scanning identifies known vulnerabilities at a point in time. Runtime monitoring adds continuous coverage, catching behavioral anomalies that signal active exploitation or emerging misconfiguration across live workloads.
  6. Automate vulnerability and patch management: When a new CVE surfaces, your team needs to know which images are affected and move fast. Automated vulnerability management workflows that detect, prioritize, and trigger remediation dramatically compress exposure windows.
  7. Maintain immutable infrastructure: Treat containers as immutable artifacts. Rebuild and redeploy from updated images rather than patching running containers. This keeps your environment consistent, auditable, and free of configuration drift.

Container Security Tools and Monitoring

A well-equipped container security stack includes specialized tools for every layer of protection:

  • Aqua Security delivers full lifecycle container security, including image scanning, runtime protection, and compliance reporting. Aqua’s depth of visibility into container behavior makes it a high-value detection layer for SOC teams.
  • Prisma Cloud provides cloud-native security across the full application stack, with strong container workload protection and compliance capabilities built in.
  • Sysdig focuses on runtime security and deep observability, giving teams granular visibility into what’s happening inside running containers in real time.

These tools generate rich telemetry and high-fidelity alerts. The opportunity is in what happens next: when those alerts need to be triaged, enriched, and acted on across your broader SOC ecosystem. Centralized orchestration is what turns detection into response at speed. For teams managing cloud infrastructure and containerized applications together, Torq is purpose-built for exactly this challenge.

Prevention and Threat Mitigation

Prevention and response work together in container security. Building strong prevention into your workflows reduces alert volume and response pressure downstream.

  • Policy enforcement at build time: Use admission controllers like Open Policy Agent or Kubernetes admission webhooks to block non-compliant workloads before they deploy.
  • Risk-based vulnerability prioritization: Focus remediation on CVEs that are exploitable in your specific environment. Risk-based prioritization helps your team work on what matters most.
  • Automated remediation workflows: When a vulnerability is confirmed, automatically trigger the appropriate response: quarantine the container, initiate a rebuild, or create a developer ticket, and keep remediation moving at machine speed. Explore automated SOC incident response to see how this works end to end.
  • Threat intelligence enrichment: Enrich alerts with external threat intelligence to contextualize risk, separate genuine threats from noise, and accelerate the path to response.

Automating Container Security with Torq

Container security tools excel at detection. The real operational opportunity is in everything that follows: triage, enrichment, escalation, remediation, and documentation. Automation handles each of those steps in seconds, consistently, at any scale.

The Torq AI SOC Platform powers that automated response layer. Torq connects your container security tools to your broader SOC ecosystem through a hyperautomation engine, enabling your team to build and deploy full response lifecycle workflows entirely in a visual, code-free environment.

Torq Hyperautomation™ drives orchestration across 300+ pre-built integrations, including Aqua, Prisma Cloud, Sysdig, Jira, Slack, and your SIEM. Torq Socrates™, Torq’s agentic SOC orchestrator, adds an intelligent reasoning layer that analyzes incoming alerts, determines the appropriate response, and executes workflows in real time. Torq HyperAgents® extend that intelligence further, enabling specialized AI Agents to handle discrete tasks like enrichment, case creation, notification, and remediation as part of a coordinated, automated response.

For Cloud and AppSec teams, Torq delivers a set of capabilities purpose-built for containerized environments: 

  • Container and Kubernetes security integration for runtime threat detection and workload policy enforcement
  • Cloud compliance automation that continuously monitors and enforces PCI DSS, HIPAA, GDPR, and SOC 2 across multi-cloud environments
  • Automated vulnerability triage that correlates CVE data with runtime context and asset criticality
  • DevSecOps pipeline integration with CI/CD platforms like GitHub Actions, GitLab, and Jenkins, so security gates run at full development speed

Real-Time Response and Orchestration

Here’s what automated container security response looks like in practice.

The scenario: Aqua Security detects a critical CVE in a container image running in production.

  1. Enrichment: Torq receives the alert from Aqua and enriches it automatically. It pulls CVE details, assesses the affected image’s deployment scope, and queries threat intelligence to evaluate exploitability.
  2. Case creation: Torq opens a structured incident case, pulling in all relevant context: the affected containers, impacted services, compliance implications, and a prioritized severity score.
  3. Notification and escalation: The right stakeholders receive immediate notification via Slack or email, with full context already included. Every relevant detail is ready for action the moment the alert lands.
  4. Remediation trigger: Based on severity and your team’s configured policy rules, Torq triggers the appropriate remediation action: quarantining the container, initiating an image rebuild, or creating a Jira ticket for the engineering team with everything they need to act.
  5. Documentation and compliance: Every action gets logged automatically, building an auditable record that supports compliance reporting, all generated as a built-in part of the response.

What would take an analyst 30-45 minutes of manual work happens in seconds, every time, regardless of alert volume. That’s the operational impact of security automation workflows applied to container environments. For a broader look at what’s driving urgency around SOC automation right now, the AI SOC Apocalypse report lays out the full picture.

Closing the Gap Between Detection and Action

Container environments scale faster than security teams can staff. Smarter orchestration is the answer.

Torq eliminates the vendor sprawl that creates friction in modern SOC operations. A single automation layer connects your container security tools, ticketing system, SIEM, and communication platforms, so your team manages orchestrated workflows instead of point-to-point integrations. API-based and cloud-native, Torq extends the value of the tools you already use. Learn more about how SOC teams use Torq to scale their operations.

Compliance becomes a continuous output. Torq’s workflows enforce policy, log every action, and generate audit-ready documentation, automatically, as part of every response. For cloud-native environments, that means faster MTTR, reduced analyst burden, and a security posture that scales with your infrastructure.

The Future of Container Security Is Automated

Container security at cloud scale requires speed, consistency, and the ability to act across a distributed environment the moment a threat surfaces. The teams that operate most effectively combine strong detection tools with automated orchestration that closes the gap between alert and action, enriching, triaging, and remediating at the speed the threat environment demands.

Torq’s AI SOC Platform gives your team that capability. Built for cloud-native environments, integrated with the container security tools you rely on, and engineered to scale with your infrastructure as it grows.

The data backs it up. The 2026 AI SOC Leadership Report surveyed 450 CISOs and SOC leaders and found 94% already use AI somewhere in the SOC, yet 80% still run fragmented point solutions, and 85% say they’d prefer a unified platform. The security leaders closing the detection-to-action gap fastest are the ones who’ve made automation the connective tissue across their entire stack.

Container security at scale demands more than monitoring — it demands automation that connects your entire stack.

See what 450 CISOs and SOC leaders say is the missing link in the 2026 AI SOC Leadership Report.

FAQs

What is container security?

Container security is the practice of protecting containerized applications and their infrastructure from threats and vulnerabilities across the full lifecycle, from image build through deployment and runtime. It covers image scanning, runtime protection, network segmentation, secrets management, and compliance enforcement. For cloud-native SOC teams, strong container security pairs detection tools with automated response workflows to keep pace with the speed and scale of modern environments.

What are the biggest container security risks?

The most common container security risks include misconfigurations, supply chain vulnerabilities in base images or third-party dependencies, privilege escalation from containers running with excessive permissions, lateral movement through insufficient network segmentation, and blind spots in ephemeral workloads. Addressing these risks requires both preventive controls and real-time container security monitoring.

How do you secure containers in cloud environments?

Securing containers in cloud environments means applying security at every stage: scanning images in your CI/CD pipeline, enforcing least-privilege access, segmenting container networks, managing secrets properly, and monitoring runtime behavior continuously. Pairing these practices with automated incident response ensures threats get detected and remediated at the speed cloud-native environments demand.

What container security tools do SOC teams use?

SOC teams commonly use Aqua Security, Prisma Cloud, and Sysdig for container-specific detection and visibility. These tools integrate directly with the Torq AI SOC Platform, which orchestrates alert triage, enrichment, case creation, and remediation across the full SOC ecosystem through Torq Hyperautomation.

What compliance frameworks apply to container security?

PCI DSS, HIPAA, GDPR, and SOC 2 all have direct implications for containerized environments. Each requires ongoing controls, logging, and the ability to detect and respond to security events within defined timeframes. Automated compliance enforcement built into your response workflows makes continuous adherence achievable at scale.

What is container security for DevOps?

Container security for DevOps means integrating security into the development and deployment pipeline from the start: scanning images at build time, enforcing policies through admission controllers, and giving developers fast feedback on vulnerabilities before code reaches production. This approach, often called DevSecOps, enables security to move at the pace of development. Agentic coding for SecOps explores how AI-powered tooling is accelerating this further.

How does Torq help with container security automation?

Torq connects your container security tools, including Aqua, Prisma Cloud, and Sysdig, to your broader SOC stack and automates the full response workflow: enrichment, case creation, notification, remediation, and compliance logging. Torq Socrates, Torq’s agentic SOC orchestrator, reasons over alerts and executes responses in real time. Explore Torq HyperAgents to see how the platform handles container threats at enterprise scale.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

What Is CNAPP? Understanding Cloud-Native Application Protection

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • A Cloud-Native Application Protection Platform (CNAPP) unifies CSPM, CWPP, and CIEM into a single framework that secures cloud environments from development through production.
  • CNAPP gives security teams unified visibility and risk context across cloud infrastructure, replacing the fragmented, multi-tool approach that leaves gaps between detection and response.
  • Modern SOC teams that extend CNAPP with automated orchestration gain the most from their investment: alert volume, tool sprawl, and the detection-to-action gap all become problems that automation closes.
  • The Torq AI SOC Platform connects directly to CNAPP tools and turns their findings into automated, agentic response workflows, closing the gap between insight and action.
  • Torq customers running CNAPP integrations achieve 10x faster time to resolve cloud security issues, with 90%+ of cloud alerts handled autonomously.

Cloud environments change constantly. Infrastructure spins up and down in minutes. Developers push configurations that create new exposure faster than manual review cycles can keep pace. Applications deploy across dozens of containers, serverless functions, and microservices spanning multiple clouds simultaneously. Securing all of it with disconnected point tools is an organizational challenge that grows faster than the teams tasked with managing it.

Cloud-Native Application Protection Platforms emerged to solve that problem by unifying the core layers of cloud security under a single framework. This article explains what CNAPP is, how its components work together, why it matters for modern SOC operations, and how the Torq AI SOC Platform amplifies CNAPP value by turning cloud security findings into automated action.

Cloud-Native Application Protection Platform (CNAPP) Meaning

A Cloud-Native Application Protection Platform is a unified security solution that combines multiple cloud security disciplines into a single, integrated framework. CNAPP consolidates cloud configuration monitoring, workload protection, and identity risk management into a single platform that provides continuous visibility and protection from code development through production operations.

The components most closely associated with CNAPP are Cloud Security Posture Management (CSPM), Cloud Workload Protection Platform (CWPP), and Cloud Infrastructure Entitlement Management (CIEM). Gartner’s definition also covers infrastructure-as-code scanning and vulnerability scanning, and many platforms add Kubernetes security posture management (KSPM) and data security posture management (DSPM). 

CNAPP also supports the “shift left” principle in DevSecOps: embedding security earlier in the development lifecycle so teams catch vulnerabilities before they reach production, when remediation is far simpler and less costly than addressing them post-deployment. Torq’s cloud and AppSec teams page covers how this shift-left approach works in practice across modern cloud environments.

How CNAPPs Work: Core Components and Capabilities

The three core components at the center of most CNAPPs each cover a different layer of cloud risk. Here is what each one does and where automation turns its findings into action.

Cloud Security Posture Management (CSPM)

CSPM continuously monitors cloud environments for misconfigurations, policy drift, and compliance gaps. In a typical enterprise multi-cloud environment, cloud resources get created and modified constantly, and each change carries the potential to introduce a misconfiguration that creates exposure. A publicly accessible S3 bucket, an EC2 instance with open SSH access, an unencrypted storage volume: these are real findings that CSPM surfaces across AWS, Azure, GCP, and other cloud platforms.

The opportunity for CSPM teams is in the response layer. A mature multi-cloud environment generates CSPM findings continuously, and automated triage keeps those findings moving toward resolution rather than accumulating in a manual review backlog. Torq Hyperautomation™ connects directly to CSPM tools and automates the triage, prioritization, and remediation of cloud risk. Each finding is validated, scored for asset criticality and exposure, and either remediated automatically or routed to the right team with full context attached, so it moves from detection to resolution at machine speed. 

Cloud Workload Protection Platform (CWPP)

CWPP secures the workloads running in cloud environments: containers, virtual machines, serverless functions, and the workloads running in Kubernetes. CWPP delivers runtime threat detection, vulnerability scanning of workload images, and behavioral monitoring that catches anomalous activity inside deployed workloads.

Container security represents one of the highest-value CWPP use cases for security teams managing cloud-native applications. A container image that passes an initial vulnerability scan may later have newly disclosed vulnerabilities in its dependencies. Runtime monitoring catches that exposure in deployed containers and in production, extending coverage well past the build stage.

Torq HyperAgents® automates CWPP incident response. HyperAgents is built to respond the moment a runtime threat is confirmed in a container or Kubernetes workload: quarantining the affected container, notifying the development team, correlating the finding with other alerts across the environment, and escalating to the SOC with full incident context. What previously required manual coordination across container platform, SIEM, and ticketing systems now runs as an automated, end-to-end response sequence.

Cloud Infrastructure Entitlement Management (CIEM)

CIEM manages permissions and identities across cloud environments, where over-permissioned accounts, unused credentials, and excessive IAM roles create a meaningful attack surface. In large enterprise environments running hundreds of cloud services, automated entitlement management is the practical path to maintaining least-privilege access at scale. Entitlement drift accumulates over time as teams add permissions to unblock urgent work and then leave those permissions in place indefinitely.

CIEM surfaces those entitlement risks: accounts with permissions they have never used, service accounts with excessive privileges, cross-account access that violates the principle of least privilege. Torq Socrates™, Torq’s agentic SOC orchestrator, integrates with IAM platforms and CIEM tools to automatically enforce least-privilege access. Socrates evaluates entitlement findings in context, determines the appropriate remediation action, and executes it: revoking unused permissions, triggering access reviews, or escalating to a human approver for changes that require business judgment.

Why CNAPP Matters for Today’s SOC Teams 

Security teams operating in multi-cloud or hybrid environments face three compounding challenges that CNAPP directly addresses.

First, visibility depth. Point tools provide strong coverage in their specific domain, and CNAPP extends that coverage across domains by correlating signals across infrastructure layers (from IaaS misconfigurations to container vulnerabilities to application-layer) into a unified risk picture that gives security teams the cross-layer context they need to prioritize effectively.

Second, alert scale. Cloud environments generate security events at a volume that rewards automated triage. Each misconfiguration finding, runtime anomaly, and entitlement risk arrives as a separate alert, and analysts triaging them across disconnected tools spend significant time building context that an integrated platform provides automatically. CNAPP platforms correlate and contextualize alerts, grouping them by resource and application to reduce the triage burden. Torq amplifies this further by automating triage entirely for the majority of cloud alerts, giving analysts a prioritized queue with investigation-ready context.

Third, the gap between detection and action. CNAPP platforms excel at finding and surfacing risks, and many can remediate common misconfigurations inside the cloud environment itself. What they are not built to do is orchestrate the response across the rest of the stack: routing tickets, coordinating with identity systems, notifying resource owners, managing the case, and verifying the fix. That cross-stack gap is where the Torq AI SOC Platform delivers the most direct operational value. Visit Torq’s cloud misconfiguration detection and remediation page to see how this runs in practice.

CNAPP and the AI SOC: Closing  Cloud Security Risk at Scale With Torq

CNAPP provides risk visibility. Torq provides the action layer that turns visibility into outcomes, investigating and fixing that risk.

The Torq AI SOC Platform  connects natively with leading CNAPP and cloud security tools, including Wiz, Prisma Cloud, Orca Security, and Sysdig, as well as cloud platforms (AWS, Azure, GCP), container platforms (Kubernetes, Docker), SIEMs, and IAM platforms. Torq HyperautomationTM provides the connective foundation and data it needs for agentic AI to plan, reason and execute automated response across the full cloud security stack.

The operational model that Torq and CNAPP tools establish together follows four stages:

  1. Triage: Torq ingests and correlates security events from CNAPP platforms, vulnerability scanners, and cloud infrastructure via native APIs, webhooks, and streaming integrations. Torq Auto Triage enriches each finding with asset management context, threat intelligence, and CMDB data scored by exploitability, asset criticality, and grounded in business-specific organizational context. Torq delivers a prioritized action queue where the most consequential risks surface first, giving analysts clear direction on where to focus.
  2.  Investigate: Torq’s Case Management capabilities, combined with integrations across ticketing, communications, and project management tools, coordinate investigation across cloud and AppSec teams. Every finding drives toward resolution with clear ownership, escalation paths, and SLA tracking.
  3. Respond: Torq Socrates coordinates and deploys agents that drive response actions. Torq HyperAgents work in parallel to update access policies, notify asset owners, and open cross-functional change management tickets complete with evidence, timelines, and SLA tracking. Agents can only act based on the tools and guidance they are approved to access, while humans are called in to approve changes that require business judgment, streamlining the process to meet your organizations preferences and standard operating procedures.
  4. Verify: Torq closes the loop automatically, re-verifying that remediation actions fully resolved the original finding and confirming the risk is gone before closing the case. 

The Torq and Wiz integration illustrates how this works in practice. When Wiz detects a publicly exposed AWS S3 bucket containing sensitive data, Torq receives the alert, validates the bucket’s exposure status, assesses the data sensitivity and asset criticality, and either updates access policies automatically or routes the finding through a human-in-the-loop approval via Slack. When Wiz surfaces an unencrypted EBS volume, or a bucket using default encryption where policy requires customer-managed KMS keys, Torq prompts the resource owner to fix it or handles it automatically based on policy. Opening SSH access on EC2 instances triggers Torq HyperAgents that confirm the owner’s identity and remove the risky access rule. Every action is logged and auditable.

The results: Torq customers running CNAPP integrations achieve 10x faster time to resolve cloud security issues and handle 90%+ of cloud alerts autonomously. 

Choosing the Right CNAPP Tools and AI SOC Partners

Evaluating CNAPP vendors and AI SOC partners involves three criteria that matter most to SOC directors and security architects.

Integration depth determines how much of your cloud environment a platform covers end-to-end. A CNAPP platform with native support across your cloud providers, container platforms, and CI/CD toolchain gives security teams the comprehensive visibility that matters for catching threats before they escalate. Prioritize platforms whose breadth matches your actual cloud footprint.

Automation readiness separates CNAPP platforms that surface findings from those that enable action. A finding that sits in a dashboard waiting for manual review has diminishing value as cloud environments change continuously. Evaluate both the CNAPP platform and its AI SOC partner on how quickly a confirmed finding translates into a remediation action, what that process looks like when agentic AI handles execution autonomously, and how much visibility and control the AI SOC partner gives your security team.

Scalability determines whether the solution grows with your environment or becomes a bottleneck. Cloud-native environments expand rapidly; a security stack that works at current scale often hits performance and coverage limits as workload volumes increase. Torq’s elastic, horizontal architecture scales with data pipeline demands and maintains performance at enterprise workload volumes. Torq’s integrations page covers the full ecosystem of CNAPP and cloud security tools that Torq connects with out of the box, and Torq’s agentic building capabilities expand that integration depth even further. Your team simply describes the desired outcome, and Torq Socrates builds the framework

For security architects building out their cloud security capability, Torq’s cloud-native security automation framework blog covers the strategic approach to layering automation across CNAPP, DevSecOps pipelines, and multi-cloud operations.

CNAPP Turns Cloud Visibility Into Competitive Security Advantage

CNAPP gives security teams unified cloud visibility and risk context that compounds in value when findings drive automated, coordinated response. A detected misconfiguration is remediated within minutes. A runtime threat becomes a contained incident before it escalates.

Torq’s AI SOC Platform is the action layer that makes that happen at scale. With native CNAPP integrations, agentic AI that reasons across cloud security data spanning detection, triage, remediation, and verification, Torq turns CNAPP insights into security outcomes at machine speed.

Is your team getting the full value out of your CNAPP investment, and does every cloud finding move automatically from detection to remediation?

The AI SOC Apocalypse is underway. Cloud environments move at a speed that rewards the security teams that are building machine speed defense to fight back against machine speed attacks, and establishing a compounding advantage today. Torq is the only true AI SOC platform built to operationalize CNAPP at the speed and scale modern enterprises require.

The teams winning the AI SOC Apocalypse automate the gap between CNAPP detection and cloud remediation. The question is whether yours is one of them.

FAQs

What is CNAPP in simple terms?

A Cloud-Native Application Protection Platform (CNAPP) is a unified security solution that combines cloud configuration monitoring, workload protection, and identity risk management into a single platform. Traditional security tools handled each domain separately: one tool for cloud configurations, another for containers, and another for IAM. CNAPP provides continuous, correlated visibility across the full cloud environment from development through production. Learn how Torq’s cloud and AppSec capabilities extend CNAPP with agentic triage, investigation, and response.

How is CNAPP different from CSPM or CWPP?

CSPM and CWPP are components within the broader CNAPP framework. CSPM (Cloud Security Posture Management) monitors cloud infrastructure configurations for misconfigurations and policy drift. CWPP (Cloud Workload Protection Platform) secures the workloads running in cloud environments, including containers, VMs, and serverless functions. CNAPP unifies all three, including CIEM (Cloud Infrastructure Entitlement Management), into a single platform that provides correlated visibility and risk context across all layers. Torq’s Hyperautomation engine connects with CNAPP platforms to automate response across all three components.

How does CNAPP support DevSecOps?

CNAPP supports DevSecOps by embedding security visibility earlier in the development lifecycle. CNAPP platforms integrate with CI/CD pipelines to scan infrastructure-as-code configurations before deployment, flag vulnerable container images before they reach production, and monitor runtime behavior after deployment. Torq extends this DevSecOps integration through AI agents that automatically block deployments with critical vulnerabilities, create developer-friendly remediation tickets, or approve low-risk changes based on contextual risk assessment and the specific tools they are granted access to take action with. Explore Torq’s DevSecOps pipeline integration capabilities.

How does Torq enhance CNAPP capabilities?

Torq amplifies CNAPP value by leveraging agentic AI to respond across the rest of the security stack, beyond the cloud environment where CNAPP findings originate. When a CNAPP tool surfaces a misconfiguration, runtime threat, or entitlement risk, Torq Auto Triage enriches the finding with asset criticality and threat intelligence context, prioritizes it against other active findings. Then, Torq HyperAgents plan, reason, and execute a complete investigation and response, either autonomously or through a human-in-the-loop approval process. Torq customers running CNAPP integrations achieve 10x faster time to resolve cloud security issues, with 90%+ of cloud alerts handled autonomously. See Torq’s cloud misconfiguration detection and remediation use case for a concrete example.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Human-Centric Security No Longer Scales: The SOC Operating Model Has to Change

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to that, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.

Many security functions today still rely heavily on humans for detection, triage, and response, often by design. But as environments grow more complex and alert volumes explode, it raises a hard question: Can this approach scale on its own?

Adopting AI in security operations isn’t just about adding tools. It means rethinking the SOC operating model itself — roles, workflows, and team structures. Here’s why, and how.

Human Speed Is Not Enough

AI-powered attackers are rewriting malware in hours, not weeks. They don’t sleep, don’t take holidays, and don’t slow down between shifts. The uncomfortable truth for every security leader: a defense built around human reaction times is already structurally defeated.

Earlier this year, Check Point documented a threat actor who used AI to build an entire malware platform. What had previously required a 30-week development cycle was executed in hours. Let that land for a moment. A months-long engineering effort, compressed to a morning. And the defenders on the other side? Still triaging alerts by hand. Still waiting for a human analyst to open the ticket.

I’ve spent more than 20 years in this industry. I’ve led security transformations at Virgin Atlantic, ASOS, Liberty Global, and others. I’ve seen every generation of the threat landscape evolve — from script kiddies to organized crime to nation-state actors. But I have never seen a shift as fundamental as this one. The emergence of agentic AI on the offensive side has broken the basic assumption that human defenders, given enough tools and talent, can keep pace. They cannot. Not anymore.

94% of organizations are using AI in the SOC in some capacity80% are still running fragmented toolsThe average SOC runs 7 different AI tools — most of them disconnected

Source: 2026 AI SOC Leadership Report

The Math Stopped Working

Security teams have always faced a staffing problem. The talent shortage is not new. But something changed recently: the gap between the attack surface and the available defense capability stopped being a hiring problem and became a physics problem. You cannot hire your way to machine speed. You cannot add a third shift to match an adversary that operates continuously, at scale, without fatigue or error.

Consider what a machine-speed attack looks like in practice. An AI-assisted attacker is not simply running faster phishing campaigns. It is dynamically adapting malware signatures to evade detection. It is scanning and correlating exposed credentials across the internet in real time. It is probing your attack surface while your analysts are writing up last night’s incident report. The asymmetry is not modest. It is categorical.

“You cannot fight machine-speed threats with human-speed defense. A security organization built around 9-to-5 shifts and human triage cycles is, structurally, indefensible against what’s coming.”

– John White, Field CISO, Torq

Why “More Tools” Is the Wrong Answer

The instinctive response to a growing threat landscape has always been procurement. Add a new detection layer. Buy the next-generation endpoint solution. Subscribe to another threat intelligence feed. The average SOC today runs seven AI-powered tools. 10% are managing 10 or more. Across the enterprise, organizations deploy an average of 83 security tools from 29 different vendors.

And yet analysts are more overwhelmed than ever. Not because the tools don’t work in isolation, but because a human being sits at every integration point — manually bridging context between platforms, fighting alert fatigue, and making triage decisions that should have been automated years ago. More tools without a unified execution layer don’t multiply capability. It multiplies noise.

85% of security leaders say they want consolidation over fragmented point solutions. Yet 80% are still running exactly that. The intention exists. The SOC operating model to support it does not, because those models were designed for a slower, more forgiving threat environment.

The analysts on your team are not unhappy because they dislike security. They’re unhappy because they’re not doing security work. They’re drowning in noise instead of solving problems. I’ve seen this firsthand. When AI handles triage at scale, something remarkable happens: you look out at your team, and they don’t seem overwhelmed anymore. They have time to think. They apply quality, not just throughput. The work they were hired to do becomes possible again.

Accountability Has Changed

Here is the harder conversation I have been having with CISOs across EMEA: the accountability framing has fundamentally shifted.

A decade ago, a CISO’s culpability was largely reactive — did you have reasonable controls in place at the time of breach? That question has not gone away. But a new question has emerged alongside it: Did you fail to adopt capabilities that would have materially reduced your exposure?

Failing to govern and deploy AI-driven security is no longer a conservative choice that preserves safety. It is a strategic decision to remain structurally behind. And boards, insurers, and regulators are beginning to understand the difference. CISOs who treat 2026 as a transition year — a year to watch and learn — will find that window has already closed around them.

I want to be clear: this is not an argument for removing humans from the loop. Quite the opposite. The decisions that require genuine human authority are the ones that demand business context — your organization’s risk appetite, the political environment you’re operating in, and the board’s strategic direction. That judgment layer cannot and should not be automated.

But the execution layer — the triage, the enrichment, the initial containment, the correlation of signals across your stack — that needs to run at machine speed. And it can.

What the New SOC Operating Model Looks Like

When I evaluate security platforms now, I use a simple filter: does this require constant human intervention to function? If yes, it becomes a bottleneck, not a defense. Any tool that cannot operate autonomously within clearly defined constraints, while still providing real-time observability, will not scale against the threat environment we are describing.

The strongest platforms I have seen do three things well:

  1. They reduce cognitive load. They interpret volumes of data and surface the insights that matter, rather than adding to the noise.
  2. They move beyond detection into recommendation and, where appropriate, remediation.
  3. They are continuously self-measuring, turning security from a reactive function into an optimizing system that can demonstrate its own effectiveness.

This is the SOC operating model I spent years trying to build from the inside at Virgin Atlantic, and the reason I moved to Torq. The agentic SOC — where machines fight machines, where AI Agents handle the execution layer at the speed the threat requires, and where human analysts focus on the judgment calls that actually need them — is not a vision document. It is deployable today.

The question for every security leader reading this is not whether this future is coming. It is whether you will be leading it or responding to it.

Here’s what happens when the SOC operating model is redesigned around the execution layer running at machine speed:

8.2x faster incident detection-to-containment75% reduction in MTTR for common security incidents95% decrease in manual tasks for Tier 1 SOC analysts
100% of Tier 1 tickets auto-remediated without human involvement4x capability to handle security alerts with the same-sized team80% alert fatigue reduction

“AI isn’t a tool you bolt onto your existing SOC. It’s forcing us to fundamentally rethink how security organizations are structured, staffed, and measured. The CISOs who redesign their SOC operating model now will build teams that operate at machine speed.”

– John White, Field CISO, Torq

A Call to Action: Redesign Your SOC Operating Model

Start with your current state, but do not think in disciplines. Think in outcomes. Where does human latency create an unacceptable gap? Where are your analysts spending time on decisions that should be automated? Where is the absence of 24/7/365 coverage leaving you exposed in the hours between shifts?

Design the SOC operating model of the future with AI and automation at its heart — not layered on top of a legacy model, but embedded from the foundation. That means 24/7 coverage that never sleeps, consistent execution that never fatigues, and human judgment applied exactly where it adds irreplaceable value.

The threat is already operating at machine speed. The only rational response is to meet it there.

Keep reading John’s CISO to CISO Blog Series on Redesigning SecOps for AI.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

AI SOC Metrics That Actually Matter: How to Measure Whether AI Is Working in Your SOC

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR:

  • Track what matters. MTTI, MTTR, autonomous case closure rate, analyst hours reclaimed, false positive suppression, and escalation accuracy. Not vanity metrics like “alerts processed.”
  • Baseline before you deploy. Without pre-deployment benchmarks, any improvement is anecdotal and indefensible at budget time.
  • Benchmark against real results. Carvana automated 100% of Tier-1 alerts. HWG Sababa improved MTTI and MTTR by 95%. Valvoline saved 6 to 7 analyst hours per day within 48 hours.
  • Report in board language. Translate AI SOC metrics into risk reduction, increased capacity, improved coverage, and greater trust maturity.

Every security vendor shipping an AI product in 2026 makes the same promises. Faster triage. Shorter response times. Fewer false positives. Reclaimed analyst hours. But, six months after deployment, most security leaders still cannot answer a straightforward question from the board: Is this thing actually working?

The problem is not necessarily that AI in the SOC fails to deliver (although in many cases, when the AI is immature or bolted-on, it does). The core problem is that most organizations never defined what “working” looks like before they deployed it. They skipped baselines, tracked the wrong metric, or failed to build a reporting framework that connects SOC performance to business outcomes. So when the CFO asks what the organization got for its AI investment, the CISO is left pointing at vendor dashboards full of numbers that mean nothing to anyone outside the SOC.

That is the accountability gap. It is the difference between an AI deployment that earns expanded investment and one that gets quietly deprioritized at the next budget cycle.

This article provides the AI SOC metrics framework to close that gap: the metrics that indicate whether AI is delivering real value, the baselines you should have captured before deployment (and how to reconstruct them if you did not), the benchmarks from real production environments that show what “good” looks like, and the reporting model that translates AI SOC metrics into the language your board already speaks.

What AI SOC Metrics Actually Matter?

Not every number your SOC produces tells you whether AI is delivering value. The right AI SOC metrics are genuinely diagnostic. 

The AI SOC metrics that matter:

  • Mean Time to Investigate (MTTI) measures whether AI is accelerating the part of the workflow where analysts spend most of their time. Faster triage speed has become table stakes for AI SOC tools. The real test is investigation speed — whether the AI is doing meaningful work like enriching data, correlating events, and building timelines, instead of  just routing alerts to the same queue slightly faster.
  • Mean Time to Respond (MTTR) is the end-to-end metric: from alert to resolution. This is the number boards understand because it maps directly to risk exposure. Every minute between detection and response is a minute an attacker has to move laterally, exfiltrate data, or escalate privileges. When AI compresses MTTR, it compresses the window of exposure.
  • Autonomous case closure rate tracks the percentage of cases that resolve without human intervention and the accuracy of that resolution. This is the metric that separates agentic AI from assisted tooling. If a human still has to review every case the AI touches, you haven’t automated anything.
  • Analyst hours reclaimed measures the time your team got back for higher-value work. Not “alerts processed” but actual hours. The distinction matters because it connects directly to capacity, which in turn connects to what your team can now do that it couldn’t before: deeper investigations, threat hunting, proactive risk reduction, and new automation development.
  • False-positive suppression rate indicates whether the AI is genuinely filtering noise or merely relabeling it. If your analysts are still manually reviewing the same volume of cases under a different status label, false-positive suppression isn’t working.
  • Escalation accuracy measures whether the AI makes the right call when it does hand a case to a human. High autonomous closure rates mean nothing if the cases that are escalated are wrong, incomplete, or lack context. Escalation accuracy is a direct proxy for analyst trust.

The metrics that mislead:

  • “Alerts processed” counts volume without outcomes. Processing 10,000 alerts means nothing if 9,500 of them didn’t need investigation.
  • “Time saved per alert” ignores whether the alert warranted investigation. Saving 30 seconds on a false positive isn’t time savings.
  • “AI accuracy” without context hides the failures that matter most. Consider this scenario: 99% accuracy on easy cases and 60% on hard ones isn’t 99% accuracy. It’s a weighted average that misleads the buyer.

Baselining Your AI SOC Metrics Before Deployment

This is the step that’s all too easy to skip, but without it, you can’t prove improvement later. Before deploying AI in your SOC, capture current-state baselines for MTTI by case type (phishing, malware, identity compromise, etc.), MTTR by severity level, analyst hours spent on Tier 1 triage, investigation, and strategic work, case backlog depth and aging, and escalation volume and accuracy.

Without these baselines, any post-deployment improvement is anecdotal. Your MTTR dropped? Compared to what — last month, which happened to be a quiet threat period? You’re closing more cases autonomously? Were you tracking closure rates before, or just estimating?

With baselines, you have a before-and-after story that boards understand. Not “we think things are better” but “our MTTI for phishing cases dropped from 45 minutes to six minutes, and here’s the data.”

If you’ve already deployed AI without capturing baselines, you’re not out of options. Pull historical data from your SIEM and ticketing system for the 90 days prior to deployment. Reconstruct approximate MTTI and MTTR by case type using ticket timestamps. Survey your analysts on how they spent their time pre-deployment — their estimates won’t be precise, but they’ll give you a good comparison point..

AI SOC Metrics Benchmarks: What “Good” Looks Like in Real Deployments

This is where the conversation shifts from theory to evidence. Most vendors publishing AI SOC content can tell you what metrics to track, but very few can tell you what the numbers should actually look like because they don’t have customer data to back it up.

Here’s what production deployments have demonstrated.

MTTR trajectory: HWG Sababa, a managed security services provider, achieved a 95% improvement in MTTI and MTTR for medium- and low-priority cases, and 85% for high-priority cases — with investigation and response now occurring nearly simultaneously in under eight minutes. That’s a measurable, repeatable benchmark across priority tiers. If your AI has been live for six months and your MTTR curve is flat, the platform isn’t learning.

Autonomous closure rates. Carvana automated 100% of Tier 1 alert handling and 41 different runbooks within one month of deployment. Bloomreach‘s SOC uses Torq’s AI SOC Orchestrator, Socrates, to handle Tier 1 and Tier 2 tasks autonomously, freeing analysts from entirely repetitive triage. These results establish the benchmark: leading organizations are closing the majority of Tier 1 and even Tier 2 cases autonomously within months of deployment. If your autonomous closure rate has stalled after six months, review your confidence thresholds, workflow design, and the scope of cases you’re allowing the AI to handle.

Analyst hours reclaimed. Valvoline saved 6-7 analyst hours per day after deploying Torq — and saw measurable ROI within 48 hours of go-live. That’s not a percentage on a dashboard. That’s time analysts can point to on their calendars — hours redirected from repetitive triage to investigation, threat hunting, and automation development.

SOC throughput without headcount growth. HWG Sababa nearly doubled SOC throughput with no new hires. Agoda compressed incident report generation from seven hours to 40 minutes. These results matter because they answer the question every CISO faces: Can I scale my SOC without scaling my team? The data says yes — if the AI is measured and managed correctly.

Use these benchmarks not as targets to hit on day one, but as reference points for your own deployment curve. 

Turning AI SOC Metrics into a Board-Ready Reporting Framework

CISOs who successfully justify AI investment don’t present raw AI SOC metrics to the board. They translate those metrics into the four things boards care about: risk, cost, capacity, and trajectory.

1. MTTR reduction → Risk exposure reduction. Frame it as: “Our mean time to respond dropped from four hours to 12 minutes. That means an attacker’s window to operate inside our environment shrank by 95%.” Boards understand windows of exposure; they might not understand MTTR.

2. Analyst hours saved → Capacity gained. Don’t frame this as headcount reduction; frame it as coverage expansion. Instead: “We recovered the equivalent of 1.5 full-time analysts in capacity. That capacity is now allocated to threat hunting and proactive risk reduction work that we couldn’t staff before.” Boards understand that doing more with the same team is possible.

3. Autonomous closure rates → Coverage improvement. Frame it as: “Before AI, we could meaningfully investigate approximately 60% of incoming alerts. We now investigate 100%. Every alert gets full triage and, when warranted, a complete investigation — without adding headcount.” Boards understand coverage gaps. Telling them you closed the gap is more powerful than any MTTR chart.

4. Escalation accuracy → Trust maturity. This is the trend line that matters most for long-term buy-in: “In month one, the AI escalated cases at 82% accuracy. By month six, it was 96%. The system is measurably getting better at knowing when to act and when to ask for help.” Boards understand learning curves — show them one.

For reporting cadence, deliver monthly operational AI SOC metrics to SOC leadership — MTTI, MTTR, closure rates, escalation accuracy, and analyst utilization. These are your tuning instruments. Quarterly, deliver business impact summaries to the CISO and board — risk reduction, capacity gained, coverage improvement, cost avoidance, and the trend curves that show compounding returns. 

How Long Does It Take for AI to Show Measurable Results in a SOC?

Tracking AI SOC metrics isn’t a one-time exercise. It’s a maturity journey, and the metrics should reflect that.

  • Month 1–3: Validate performance in shadow mode. Run AI decisions in parallel with analysts. Compare what the AI would have done against what analysts actually did. Establish accuracy baselines and identify where the AI agrees with your team and where it diverges. This phase builds internal confidence. If the AI matches analyst decisions a majority of the time on Tier 1 cases, you have the evidence to increase autonomy.
  • Month 3–6: Increase autonomy. Expand autonomous closure. Track escalation accuracy weekly. Tune confidence thresholds based on real outcomes, not theoretical risk models.
  • Month 6–12: Expand use cases. Benchmark against industry data. Extend AI into Tier 2 investigation, cross-team workflows, and compliance reporting. Demonstrate compounding improvement — not just in speed, but in scope.
  • Month 12+: Activate AI-driven insights. The AI surfaces trends humans couldn’t detect at scale — detection rule gaps, recurring misconfiguration patterns, team capacity forecasting, and emerging attack vector correlation. At this stage, the AI isn’t just executing your security strategy; it’s informing it.

The key signal to watch across all stages: AI SOC metrics should compound before they plateau. An early flat line means the platform isn’t learning. A late plateau after months of sustained improvement is what a mature deployment looks like. MTTR should keep dropping. Autonomous closure rates should keep climbing. Escalation accuracy should keep tightening. If your numbers plateau after month three, something is wrong. Either the AI isn’t learning from new data, the use cases aren’t expanding, or the confidence thresholds need adjustment. 

The AI SOC Metrics Imperative

The organizations getting the most from their AI investment aren’t running the most sophisticated models. They’re running the clearest measurement frameworks — and they have the discipline to track them.

Define your baselines. Track the metrics that connect to outcomes. Build the dashboard your board actually wants to see. And benchmark against organizations that have already proven what’s possible.

Explore our 90 Days to SOC Autonomy roadmap.

FAQs

What are the most important AI SOC metrics to track?

The AI SOC metrics that matter most are MTTI, MTTR, autonomous case closure rate, analyst hours reclaimed, false positive suppression rate, and escalation accuracy. Baseline these metrics before deployment and track them monthly. Organizations using Torq have demonstrated MTTI/MTTR improvements of 95%, autonomous alert management of 55%+ of total volume, and full Tier 1 automation within months of deployment.

What is a good autonomous case closure rate for an AI SOC?

Leading organizations achieve 55–100% autonomous case closure rates for Tier 1 and Tier-2 cases. HWG Sababa automatically manages approximately 55% of total monthly alert volume end-to-end. Carvana automated 100% of Tier 1 alert handling and 41 runbooks within one month. If your AI has been live for six months and autonomous closure is stagnant, review your confidence thresholds and workflow design.

How do you report AI SOC metrics to the board?

Translate AI SOC metrics into business language: MTTR reduction maps to reduced risk exposure, analyst hours saved maps to capacity gained (not headcount cut), autonomous closure rates map to coverage improvement, and escalation accuracy maps to trust maturity. Report operational metrics monthly to SOC leadership and quarterly business impact summaries to the CISO and board.

How long does it take for AI to show measurable results in a SOC?

Most organizations see initial results within weeks. Valvoline saw ROI within 48 hours of deploying Torq. However, the compounding value of agentic AI — improving accuracy, expanding use cases, surfacing operational trends — builds over 3-12 months. HWG Sababa achieved a 95% MTTI/MTTR improvement and nearly doubled SOC throughput without adding headcount, with the steepest gains occurring in the early months of deployment.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO