What Is a Dictionary Attack? Everything You Need to Know to Stay Safe

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • A dictionary attack is a credential-cracking method where attackers systematically test lists of common passwords and phrases against login systems.
  • Dictionary attacks, brute force attacks, and rainbow table attacks each use distinct methods, speeds, and detection signatures. Understanding the differences sharpens your defense.
  • Real-world dictionary attacks have compromised major organizations by exploiting weak or reused passwords at scale.
  • SOC teams face real detection challenges: high login volumes, alert fatigue, and identity signals that span multiple systems make manual monitoring a bottleneck.
  • The Torq AI SOC Platform automates real-time detection and response to credential-based attacks, stopping them before they escalate.

Passwords are still the most common door into an organization’s systems, and attackers know exactly how to pick that lock. Dictionary attacks rank among the most effective and widely used credential-based attack techniques, because most people rely on familiar words and predictable patterns when choosing passwords.

For SOC analysts and security architects, understanding how dictionary attacks work, how they differ from other password-cracking techniques, and how to detect them before damage occurs is foundational knowledge. 

Understanding Dictionary Attacks in Cybersecurity

A dictionary attack is a type of cyberattack where an adversary uses a pre-compiled list of words, phrases, and common passwords (the “dictionary”) to systematically guess login credentials. The attacker works through a curated list of high-probability passwords: common words, popular phrases, and known variations like “password123” or “P@55word.”

The logic behind a dictionary password attack is straightforward: people gravitate toward familiar, memorable passwords. Attackers exploit that predictability by starting with the most likely candidates and working outward. Wordlists used in dictionary attacks can range from thousands to hundreds of millions of entries, often sourced from previous data breaches, public password dumps, and custom-built collections targeting specific industries or geographies.

Dictionary Attack Example

Picture a threat actor targeting the employee login portal of a mid-size financial services firm. The attacker loads a wordlist containing the 10 million most commonly used passwords from prior breach datasets and begins cycling through them against employee email addresses scraped from LinkedIn. Because the firm lacks rate limiting on its authentication endpoint, the attacker submits thousands of credential combinations per minute and goes undetected.

Within hours, the attacker successfully authenticates as three employees who reused passwords from other breached services. That access becomes the foothold for lateral movement deeper into the network.

A second common dictionary attack example targets APIs directly. Developers sometimes leave API authentication endpoints with weaker protections than primary login portals. Attackers run dictionary attacks against these endpoints, knowing that API credentials often follow predictable patterns tied to service names or team conventions.

Both scenarios share a common thread: password predictability and detection gaps are what open the door. The attack requires no technical sophistication to succeed.

Dictionary Attack vs. Brute Force vs. Rainbow Table

Understanding how these three attack types differ helps SOC teams tune detection rules and prioritize defenses appropriately.

Attack TypeMethodSpeedSophisticationDetection Complexity
Dictionary attackTests pre-compiled wordlists of likely passwordsFast; targets high-probability passwords firstLow to medium; relies on human password patternsMedium; high login volume can blend with normal traffic
Brute force attackTries every possible character combinationSlow; exhaustive by designLow; pure computationLower; extreme login volume is easier to flag
Rainbow table attackMatches stolen password hashes against precomputed hash tablesVery fast once hashes are obtainedMedium to high; requires prior hash theftHigh; operates offline against stolen data

The dictionary attack vs. brute force distinction matters operationally: brute force attacks generate obvious login volume anomalies, while dictionary attacks can stay under threshold-based detection by pacing requests carefully. Rainbow table attacks often occur entirely offline after a breach. When that happens, the focus shifts to protecting hashes through salting.

How Dictionary Attacks Impact SOC Operations

Why Credential-Based Attacks Are Hard to Detect

Dictionary attacks are difficult to distinguish from legitimate login behavior at scale. A real user who forgets their password and tries several variations before succeeding looks similar, in raw log data, to an attacker working through a wordlist. Multiply that ambiguity across hundreds of employees and dozens of applications, and the signal gets noisy fast.

High-velocity dictionary attacks that spread attempts across multiple accounts, rather than hammering a single account, stay below standard account-lockout thresholds. Slow-and-low dictionary attacks deliberately throttle request rates to avoid triggering velocity-based alerts entirely. Both techniques exploit the gap between what detection rules expect and how real attacks behave.

Manual Detection Limitations

Legacy security information and event management (SIEM) systems and static rule sets struggle to keep pace with credential-based attacks for a few key reasons.

First, identity signals and endpoint signals live in separate systems. A SIEM might flag unusual login volume, but correlating that signal with endpoint behavior, geolocation anomalies, and user behavior baselines in real time requires cross-system analysis that static rules handle poorly.

Second, alert fatigue compounds the problem. SOC analysts managing hundreds of daily alerts often deprioritize authentication alerts, particularly in environments where password-reset noise is high. Attackers count on that deprioritization.

Third, manual triage takes time. By the time an analyst investigates a credential alert, correlates it across identity and endpoint data, and confirms the attack pattern, the attacker may already have authenticated successfully. Speed matters in credential-based intrusion response, and manual workflows introduce latency that attackers exploit.

Modern Techniques to Detect and Prevent Dictionary Attacks

Credential Hardening and Authentication Defense

Strong credential hygiene remains the most reliable foundation for preventing dictionary attacks. Several controls work in combination to raise the cost of a successful dictionary password attack significantly:

  • Password length and complexity requirements that push users away from common dictionary words and phrases
  • Multi-factor authentication (MFA) on all external-facing systems, so attackers need a second verified factor to complete authentication, even with a correct password
  • Account lockout and rate limiting on authentication endpoints, capping failed login attempts before an attacker can work through a meaningful wordlist volume
  • Passphrase policies that favor length and randomness over character substitution, which attackers already account for in modern wordlists
  • Credential breach monitoring that alerts users and security teams when an employee’s credentials appear in known breach datasets

These controls address the attack before it reaches the detection layer. MFA, in particular, transforms credential exposure into a contained risk: a correct password becomes one piece of a two-factor requirement that the attacker still needs to clear.

Behavioral Detection and Cross-System Correlation

Prevention controls build a strong foundation, and behavioral detection extends that coverage further. Analyzing login patterns against historical baselines catches dictionary attacks that operate below threshold-based detection rules.

Effective behavioral detection looks for signals like unusual login times, geographic anomalies, device fingerprint changes, and velocity patterns that deviate from a user’s established baseline. Correlating those signals across identity providers, endpoint detection tools, and network logs produces a much clearer picture of whether unusual authentication activity represents a threat.

This is where automated SOC incident response makes a decisive difference. Automated workflows pull signals from identity, endpoint, and network systems simultaneously, evaluate them against behavioral baselines, and trigger a response. That response could be an account lockout, an MFA challenge, or an analyst escalation with full context attached, all in seconds rather than minutes.

Threat Intelligence Integration

Modern dictionary attacks often use wordlists built from credential dumps tied to specific industries or geographies. Threat intelligence feeds that surface newly published breach datasets give security teams advance warning when their users’ credentials are likely in circulation.

Integrating threat intelligence into your identity monitoring workflow, automatically cross-referencing employee email addresses against breach datasets and triggering credential reset workflows when matches appear, transforms passive awareness into active defense. Torq’s vulnerability management tools blog explores how this kind of proactive integration fits into a broader security posture.

Building a Proactive Defense Strategy with Torq

Dictionary attacks succeed when detection is slow, response is manual, and credential hygiene is inconsistent. Torq’s AI SOC Platform addresses all three.

Torq Hyperautomation™ connects identity providers, endpoint detection platforms, SIEMs, and threat intelligence feeds into unified, automated workflows. When authentication anomalies are triggered, Torq acts immediately. Torq HyperAgents™ autonomously gather context across connected systems, including login history, device posture, geolocation, and behavioral baselines, then execute a response in real time. HyperAgents are built to operate at the speed attacks move.

Torq Socrates™, Torq’s agentic SOC orchestrator, adds an additional layer of intelligent reasoning. Socrates evaluates the specific context of each authentication anomaly, determines the appropriate response action, and executes it, whether that means locking an account, triggering an MFA challenge, notifying the user, or escalating to a Tier 2 analyst with full context attached.

For SOC teams managing high volumes of authentication alerts, the shift from manual to autonomous triage is transformational. Analysts focus on confirmed threats and complex investigations. Routine credential-based alert handling runs continuously in the background, without human intervention, at a scale and speed that autonomous workflows deliver consistently.

Torq also offers a no-code workflow builder, so security architects can configure detection-and-response workflows for dictionary attacks and adapt them as attacker techniques evolve. Explore how SOC teams use Torq to build and manage these workflows at enterprise scale.

Want to see how Torq handles credential-based attacks, such as dictionary and brute-force attempts, in practice? Take a closer look at automated SOC incident response workflows built on Torq.

Your SOC Deserves a Defense That Moves at Attack Speed

Dictionary attacks thrive on predictable passwords and slow response times. Harden credentials, layer in behavioral detection, and automate triage. Your team takes away the two things attackers count on most.

Torq’s AI SOC Platform gives security teams the automation layer to detect credential-based attacks in real time, respond autonomously, and close the window of exposure before damage occurs. Security teams that automate credential threat detection and response are setting a new standard for speed, coverage, and resilience. 

The AI SOC Apocalypse manifesto is reshaping how enterprise security leaders think about autonomous defense.

FAQs

What is a dictionary attack?

A dictionary attack is when an attacker uses a list of common passwords and words to guess login credentials, testing them one by one against a target system. The attacker works through the most likely passwords first: common words, well-known phrases, and popular variations, moving systematically through the wordlist. It works because many people choose predictable passwords. Strong password policies and MFA are the most reliable defenses. Learn how Torq automates credential threat response to stop these attacks before they succeed.

What is the difference between a dictionary attack and a brute force attack?

The core difference is scope. Brute force attacks try every possible character combination up to a given length, exhaustive by design. Dictionary attacks work from a curated list of likely passwords: common words, known credentials from breach datasets, and predictable variations. Dictionary attacks are faster and more targeted, succeeding against human-chosen passwords more efficiently. From a SOC perspective, brute force attacks generate more obvious volume anomalies, while dictionary attacks can be tuned to stay below standard detection thresholds. See how Torq’s security automation workflows catch both attack types in real time.

What is a real-life example of a dictionary attack?

One well-documented scenario involves attackers using credential lists compiled from prior data breaches, often containing hundreds of millions of username and password pairs, to target corporate login portals. When employees reuse passwords across personal and work accounts, a breach at a third-party service can become the entry point for a corporate network compromise. This technique, called credential stuffing, is a closely related attack that uses real leaked credentials rather than generic wordlists. Automated breach monitoring and credential reset workflows are effective countermeasures. Explore how Torq’s incident response automation helps teams respond fast when credential attacks are detected.

How can we protect against dictionary attacks?

Effective protection layers several controls together: enforce strong password policies that steer users toward length and randomness over common words; require MFA on all external-facing systems; implement rate limiting and account lockout on authentication endpoints; monitor for credential breaches and trigger automated password resets when employee credentials appear in breach datasets; and deploy behavioral detection that flags authentication anomalies in real time. Torq’s AI SOC Platform automates the detection and response layer, connecting identity, endpoint, and threat intelligence systems into workflows that act autonomously when credential attacks are detected. Learn more about building a proactive defense by exploring Torq’s automated SOC incident response capabilities.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

The CISO’s Role Is Rapidly Changing

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to that, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.

AI isn’t just reshaping the threat landscape or how we defend against attacks; it’s redefining what leadership in security looks like. The CISO of the near future is less a chief technologist and more a strategic architect of business outcomes, designing human-machine teams that reimagine the target operating model in response to both risk and opportunity.

I want to dwell on that last word for a moment. Opportunity. We talk endlessly about risk in this industry, and for good reason. But we don’t talk nearly enough about the opportunity sitting right in front of us. For the first time in my career, CISOs have an enabler that can take a strategic vision from concept to operations, end-to-end, faster and more securely than ever before. That’s not a risk to manage. That’s an extraordinary moment to seize.

This piece is about what that means in practice for CISOs — for the role, for the skills we need to develop, and for the mindset we need to let go of. Some of it I’ve learned from watching the industry shift in real time. Some of it I’ve learned the hard way in the trenches. And some of it I’ve only realized after stepping out of an operational role and gaining an outside perspective as what I call “a recovering CISO.

What Does “Strategic Architect” Actually Mean?

There have been lots of technology waves in security — on-prem to cloud, SaaS, zero trust. Each one changed how we worked. But the AI wave is different in kind, not just degree. Quantum will have its own impact, but AI does something quantum doesn’t: it builds things for you. That’s a fundamentally different proposition for a CISO.

Historically, you put together your strategy — risk reduction targets, maturity gains — and executed it over a steady two- or three-year change program. You needed armies of people with specific skill sets. The gap between strategic intent and operational reality was measured in months, sometimes years.

Agentic AI is closing that gap.

With the right AI tooling, CISOs can articulate intent in natural language and have autonomous systems build, deploy, and iterate the operational response. Auto-triage events. Enrich and prioritize cases. Investigate and resolve incidents. What once took months now takes days or hours. And the kicker: you no longer need to depend on large teams of skilled resources to deliver it.

The day-to-day changes fundamentally. It’s no longer about managing activity. It’s about leading agentically — articulating intent, shaping outcomes, and building an organization capable of autonomous, agile execution.

Gone are the days of long, rigid three-year plans. The model is shifting: agree on an outcome, execute over a short sprint, come back to senior leadership with what you’ve built, review together, iterate, and go again. It’s a product lifecycle, not a security program. CISOs are becoming more product-focused, more like marketers, constantly selling a vision and delivering it in pieces.

The greatest skill a CISO can develop right now is the ability to articulate intent clearly and pivot fast. Everything else follows from that.

Two Starting Points, One Destination

I’ve worked on both sides of the Atlantic, and the regional differences in how CISOs are approaching this shift are real:

  • U.S. CISOs have typically had greater freedom to experiment — with higher risk tolerance, faster technology adoption, and earlier moves toward automation-first models. They try things, swap them out if they don’t stick, and move on. Less governance bureaucracy, more speed.
  • In EMEA, the starting point has been different. Regulation, data protection, and supervisory scrutiny drive a more cautious, governance-first mindset. CISOs there prioritize control and defensibility before innovation. Investments are more measured. The instinct is to get it right the first time and maximize the return on every dollar spent.

Neither approach is better. They’re different responses to different environments.

But AI is forcing convergence. U.S. leaders are realizing that agentic security without strong governance doesn’t scale safely. EMEA CISOs are recognizing that manual, people-heavy models can’t meet regulatory expectations at speed or scale. Automation is no longer optional; it’s becoming a prerequisite for compliance, resilience, and cost control.

The result is a shared destination from different starting points: security organizations that are outcome-driven, automated by default, and governed by design. The U.S. needs to think harder about governance. EMEA needs to shift from resilience-first to bolder, more innovative moves. Both are on the same journey.

The Skills Nobody Trained Us For

If I were mentoring someone who wants to be a CISO in five years, here’s what I’d tell them. And almost none of it maps to traditional career development.

First of all, don’t become a CISO. I’m joking. Mostly.

Agentic and AI systems literacy is non-negotiable. You need to be genuinely literate in the agentic world, not just aware of it. Keep up with emerging technologies, understand how things are being built, and know the movers and shakers. If you don’t understand how agentic systems work, you can’t re-architect a target operating model around them. You need enough depth to be an intelligent buyer, governor, and architect, even if you’re not building.

Product ownership mentality over technical depth. Think like a product owner, not a program manager. Shorter cycles, continuous iteration, outcome-based delivery. Think unified platform, not individual tools in silos. You can’t have silos of people and silos of tools and expect it to scale. The security organization of the future is a platform that integrates your existing stack while automating tasks that would otherwise require human intervention — which is exactly what the 2026 AI SOC Leadership Report found that 85% of today’s security leaders want: a unified, end-to-end AI SOC platform.

The ability to articulate intent and translate it into business outcomes. This surprises people the most. You no longer need deep technical knowledge to be an effective CISO. What you absolutely need is the ability to define what success looks like, communicate it in terms the board understands, and evangelize it across the organization. The modern CISO is more of a marketer than an engineer. You need a vision, and you need to keep selling it as you deliver it piece by piece.

Governance of autonomous workforces. As we create machine identities with real authority — for containment decisions, incident resolution, and workflow execution — we need governance models for them. How do hybrid human-machine teams operate? Who’s accountable when the machine gets it wrong? These are questions we were never trained for, and we need to start answering them now.

What I Had to Unlearn

I describe myself as a “recovering CISO.” That’s not a punchline; it’s an honest acknowledgment of what stepping away from 20-plus years of operational readiness actually feels like.

As CISOs, we like to keep a very tight grip on things. If we’ve got a grip, we can control it. Control means protection. That instinct gets deeply wired in. The phone rings at 3am and you’re already running through the response before you’re fully awake. Working weekends becomes normal. Getting pulled into every significant incident, every escalation? That’s just the job.

That constant readiness is hard to shake off. Even now, I catch myself with the operational muscle memory — the reflex to want to be in the room, the discomfort of not knowing exactly what’s happening on the front line. That’s why I call it ‘recovering’. I’m still pulling away.

But the distance has given me something valuable: the headspace to think about what security leadership actually means when you’re not drowning in operational noise. And what I see clearly now is that the tight operational grip, as much as it felt like protection, is also what holds CISOs back.

With autonomous and agentic delivery, we need to get comfortable releasing that grip and letting machine-led execution take its place. That’s not losing control. It’s reallocating where human judgment adds the most value. The machine handles execution. Humans handle intent, governance, and contextual judgment that AI can’t replicate.

CISOs still in the role will need to make the same mindset shift without the luxury of stepping back to reflect. The ones who do it well will thrive. The ones who stay stuck in their ways will be in survival mode.

The Pivot That Changes Everything

Ultimately, everything comes down to one fundamental shift — from controls to outcomes.

Think about how we’ve historically measured success. Risk scores. Maturity assessments. Compliance certifications. Patch percentages. These are measures of activity and operational hygiene. They’re not useless, but they’re no longer sufficient.

There’s a new target operating model built on three distinct layers: 

  1. Outcomes: What the organization is trying to achieve, in business terms
  2. Execution: Where automated and agentic capabilities deliver at scale, at machine speed
  3. Judgment: Where human oversight, context, and accountability are applied where they genuinely matter

When you design this model properly, the things CISOs have always cared about become byproducts. Risk reduces, compliance follows, maturity improves. Not as the sole focus, but as the natural consequence of building something that actually works at the speed the threat landscape demands.

We need to rethink what success looks like. Not the next rung up the maturity ladder. Not the next compliance certification. But have we equipped the organization with a platform that can address future threats faster than before? Are we agile enough to adapt when the landscape shifts again… which it will?

Maintaining the norm is not an option. No one is going to thank you for a clean compliance scorecard if you’ve been hit by a machine-speed attack and couldn’t respond because you hadn’t built a machine-speed defense.

The CISO role is changing. Not incrementally but fundamentally. The question isn’t whether it will change. It’s whether you’ll change with it.

Want the data behind the shift? 450 security leaders weighed in.

Keep reading John’s CISO to CISO Blog Series on Redesigning SecOps for AI.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

The 2026 AI SOC Leadership Report: What 450 Security Leaders Told Us

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

When we started building Torq four years ago, we had a thesis: the SOC was broken, and automation — real automation, not another tool bolted onto the stack — was the way to fix it. AI has since changed the game entirely. But has it streamlined the SOC, or introduced new complexity?

We wanted to find out. We partnered with Sapio Research to survey more than 450 CISOs and SOC leaders across four countries.

The short answer: AI is everywhere. It’s delivering real value. And it’s creating a new set of problems that nobody planned for.

AI Works. The Way It’s Deployed Doesn’t.

I’ll start with the good news, because there is plenty of it. 90% of security leaders say AI has positively impacted SOC workload. 85% say it’s reduced stress and burnout. 83% agree their AI tools deliver on vendor promises. That’s not a market that’s disappointed with AI. That’s a market that’s seen what it can do.

But underneath those numbers, a more complicated picture is emerging. The average SOC is running 7 AI-powered tools. 80% still rely on fragmented point solutions rather than a unified platform. And 92% of leaders cite at least one factor actively reducing their trust in AI.

This is the paradox we keep hearing in every customer and prospect conversation: AI is working, but the way it’s been deployed — tool by tool, vendor by vendor — is creating the same complexity it was supposed to eliminate.

5 Findings from 450 Security Leaders

We organized the findings around five themes that surfaced consistently across geographies, company sizes, and seniority levels.

1. AI Is Everywhere in the SOC, But Unified Nowhere

Teams are running 7 tools with AI on average, but 80% depend on disconnected point solutions. 85% say they’d prefer consolidation. The tools have multiplied. The integration between them hasn’t. This is the finding that hit closest to home for me; it’s the exact problem we set out to solve when we founded Torq.

2. AI Is Carrying the Load; Analysts Are Making the Calls

72% of teams are comfortable with fully autonomous AI on medium-severity incidents and below — the alerts that make up the bulk of SOC volume. Analysts aren’t being replaced. They’re being freed up for the work that actually requires human judgment. 

But to push autonomy further, 9 in 10 say they need to see how AI reaches its decisions before they trust it. I hear this constantly from CISOs: “I’d let AI do more if I could see why it’s doing what it’s doing.”

3. The Analyst Role Is Evolving

Analysts spend an average of 8.6 hours per week overseeing AI outputs. That sounds like a problem… until you see that 9 in 10 say AI has positively impacted their workload. Those hours aren’t busywork. They represent a role shift from execution to judgment. This is the future of the SOC analyst: not replaced by AI, but elevated by it. AI handles the processing; analysts make the calls that matter.

4. Trust Is the Limiting Factor on AI Expansion

92% of security leaders cite at least one barrier to trusting AI in the SOC — from data privacy to black-box decision-making. And the #1 thing that would change that? Transparency. 46% say the ability to see how AI reaches its conclusions would be the single biggest confidence booster. 

Not more features. Not more AI. Just show AI that shows its work. We took this to heart early at Torq; explainability isn’t a feature we added. It’s how we built the platform.

5. The Market Knows What It Wants

85% of security leaders would prefer a unified AI SOC platform over managing multiple point solutions. 92% say AI must continuously learn and adapt to evolving attack patterns. The desired end state is remarkably consistent across every seniority level, company size, and geography: unified, explainable, and adaptive. This data validates the architectural bet the entire industry needs to make.

What This Means for the Security Industry

97% of CISOs and security leaders are confident AI can handle triage. Only 35% are actually using it there. That gap keeps me up at night — not because teams lack ambition, but because their tools aren’t giving them a way to act on it. Teams won’t extend AI into high-stakes functions unless they can set autonomy thresholds, see how decisions are made, and adjust as confidence grows.

The organizations that close this gap first will be the ones that unlock what AI in the SOC was always supposed to deliver.

That’s what we’re building. This report shows why it matters.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

RSAC 2026: Oops, We Did It Again.

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

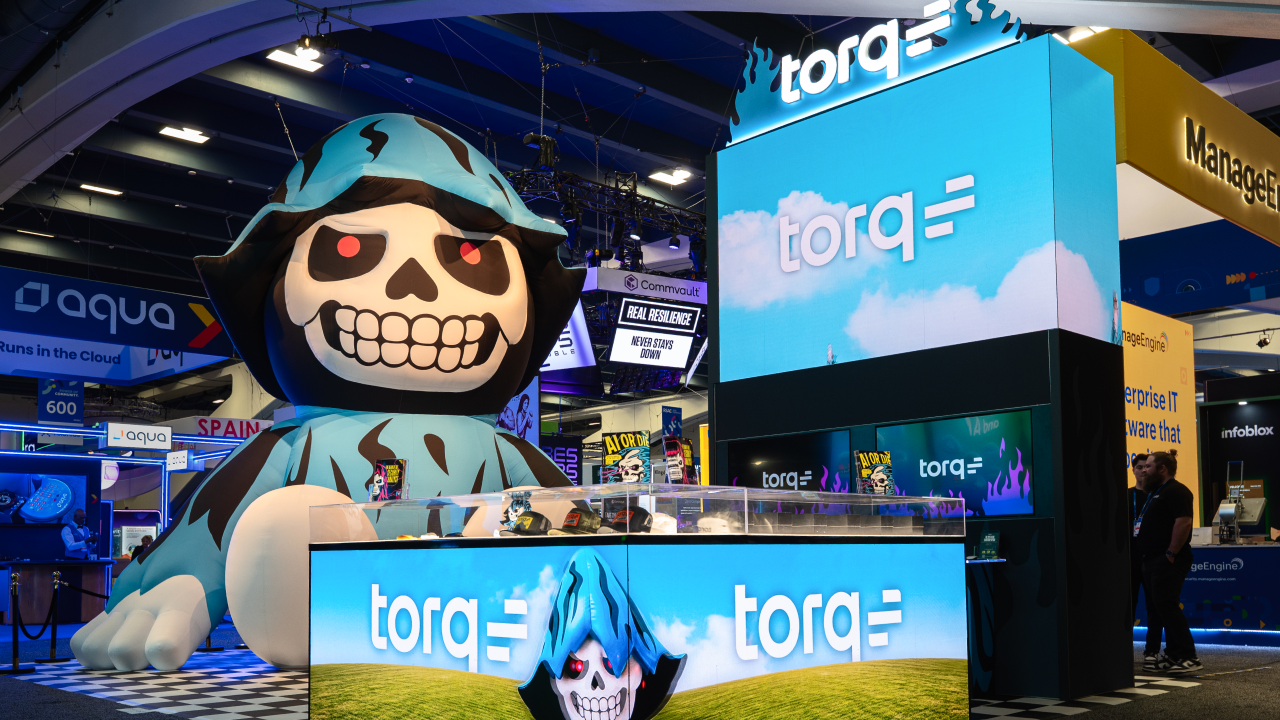
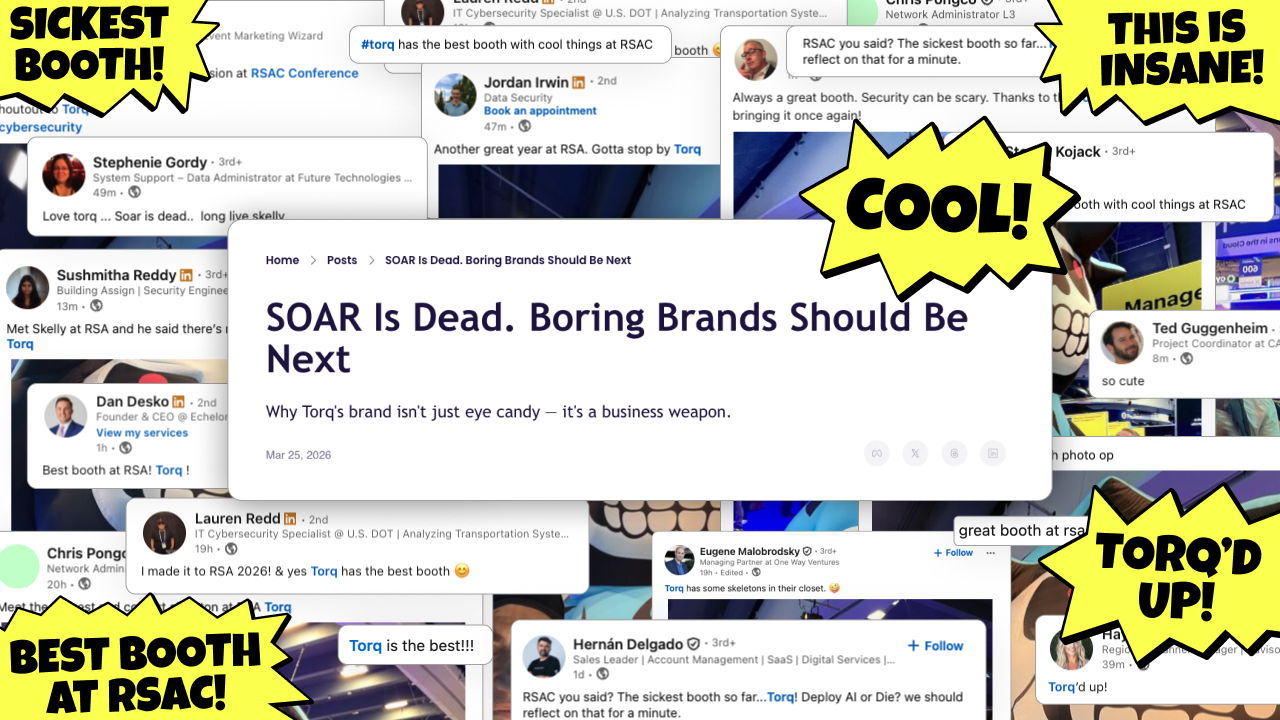
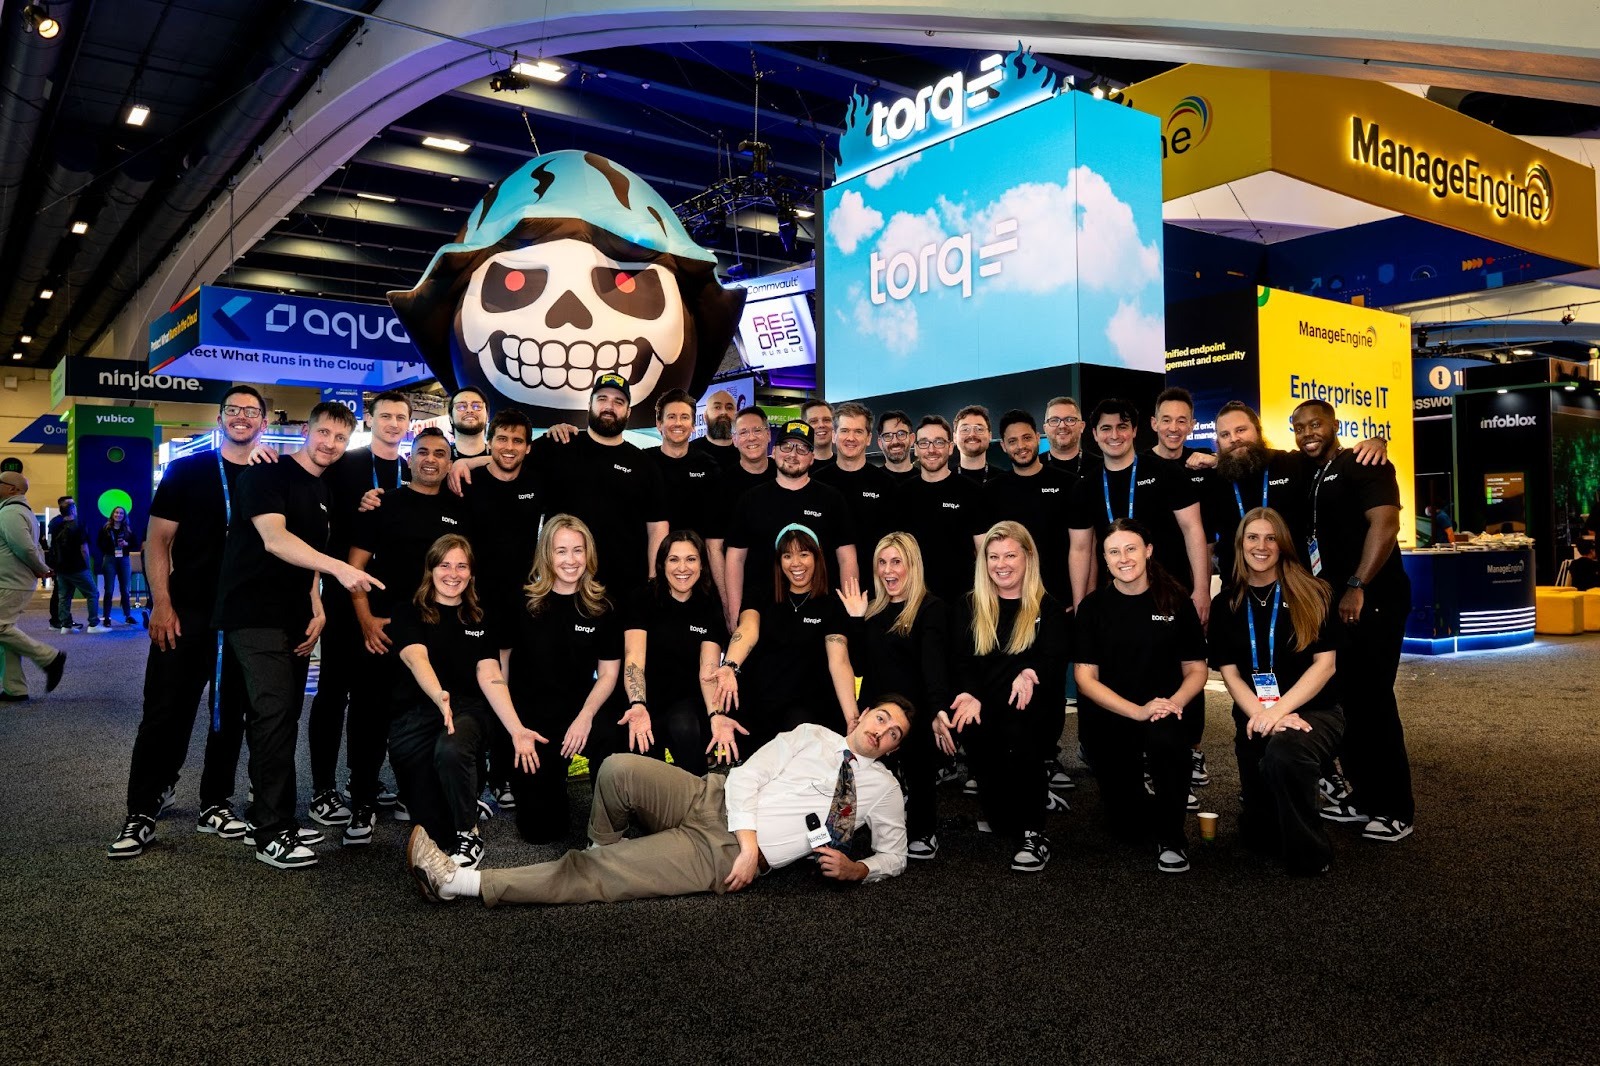
Torq rolled into RSAC 2026 at Booth #527 with the same energy that made us the talk of the show last year — except this time, everybody was just waiting to see how we could top a monster truck.

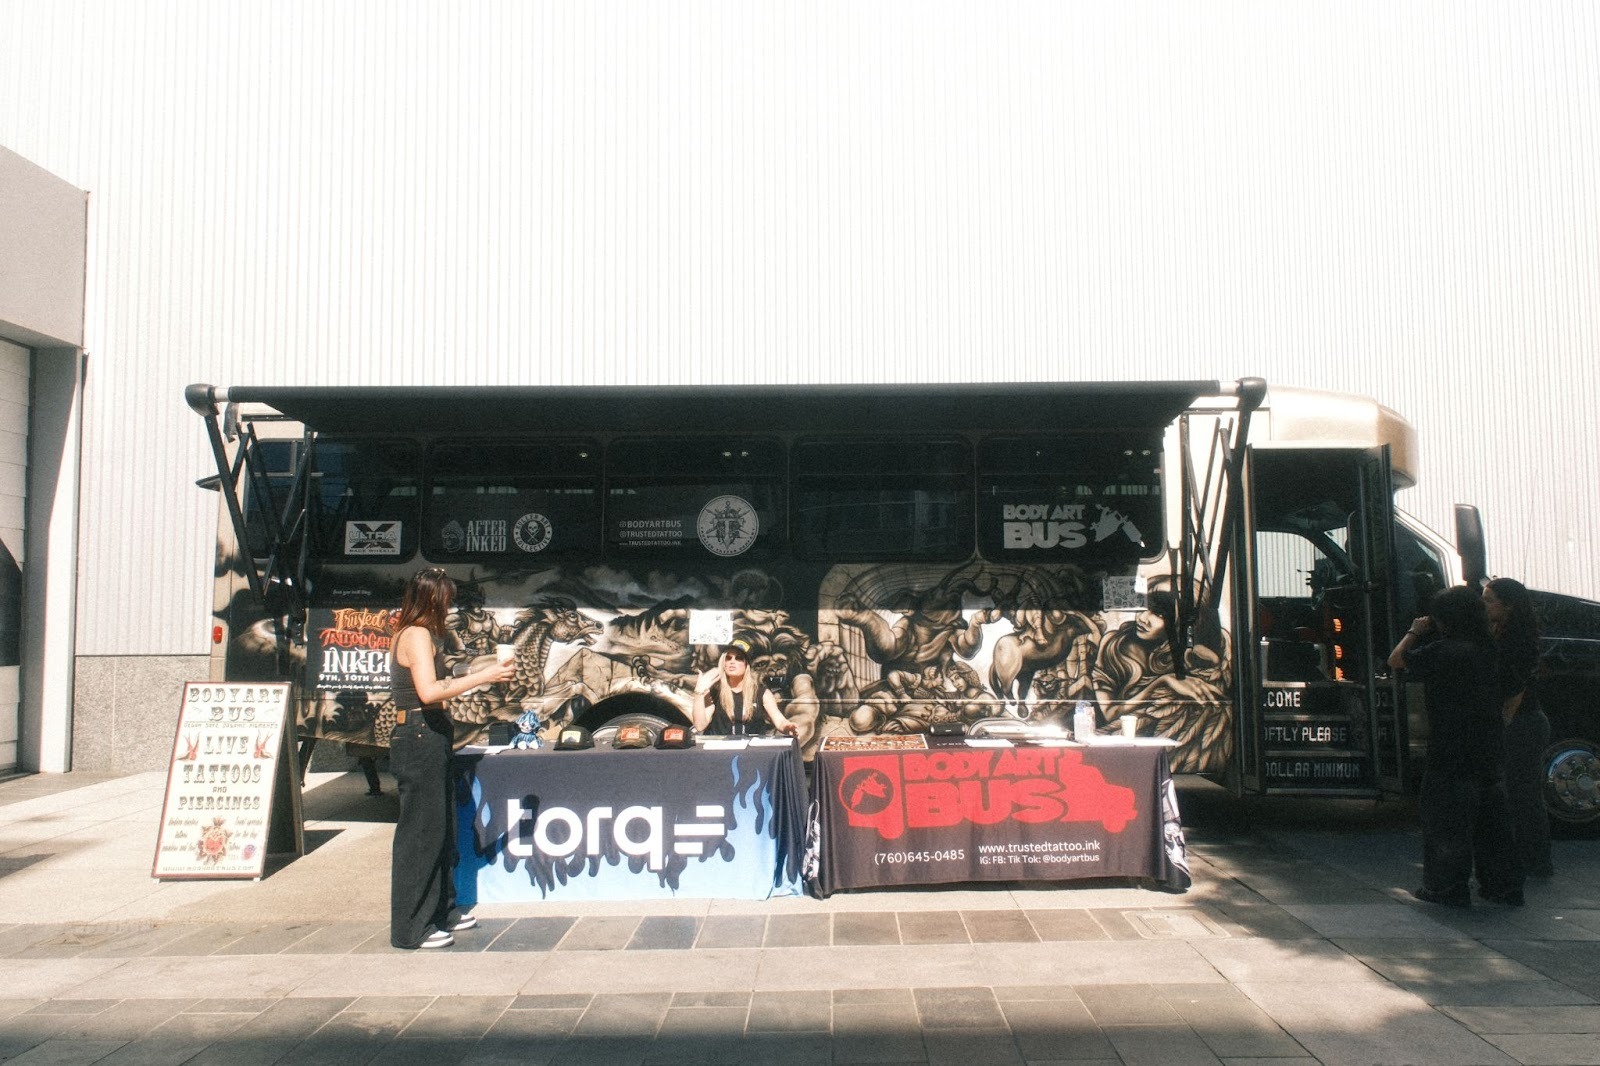
So, we brought a 20-foot inflatable skeleton that towered over the Moscone floor. A fully operational tattoo bus giving out permanent ink. A product announcement that turned heads across the industry. And the 2026 AI SOC Leadership Report — new research from 450 CISOs and security leaders on what AI is actually doing inside the SOC (and where it’s falling short).

Here’s everything that happened.

RSAC 2026

The Booth That Broke RSAC (Again)

Last year, it was 12,000 pounds of Grave Digger. This year, it was the world’s largest inflatable skeleton  — and somehow, it still wasn’t the most memorable thing we did.  The skeleton got them to stop. The tattoo bus got them talking. But the Torq AI SOC Platform is what had security professionals coming back for demo after demo.

In a sea of AI-powered sameness, Torq’s demo stood out as the only AI SOC that covers the entire threat management lifecycle. AI Agents that actually take action, saving analyst hours at every stage of SecOps and closing the loop on threats — autonomously.

The demo highlighted Torq ingesting and normalizing security events from many of the other big-name vendors on the show floor — CrowdStrike, Wiz, Okta, etc. — correlating and prioritizing alerts to reduce the noise. But the demo didn’t stop at analysis. Torq HyperAgents™ dug deep, investigating cases by querying data lakes and cross-referencing third-party threat intelligence, before Socrates’ agentic response actions contained threats and remediated the root cause. 

The benefits clicked immediately for booth visitors, who were already thinking ahead to what they could accomplish with the time savings Torq would provide. What about agentic vulnerability management? How can HyperAgents expedite threat hunting? With the Torq AI SOC Platform removing mundane, repetitive work that bogged down security analysts, the conversation quickly shifted to the world of possibility. 

One attendee said, “I can see how this platform could really help us scale my MSSP. 

The wow factor came from the agentic transparency. No black box decision making; clean, detailed, and transparent reasoning logs documented in real time as Torq AI Agents triaged, investigated, and responded. This was a breaking point that led a majority of demo viewers to schedule follow-up time for the rest of their team to see the hype.

Part of that hype? A week before RSAC, Torq announced Agentic Builder, which led CRN to name us one of the “20 Coolest AI and Security Products at RSAC 2026.” Think Cursor, but for the SOC. A security engineer describes what they need in plain language — “correlate EDR alerts with suspicious logins and known malicious IPs, map to MITRE ATT&CK, escalate by severity” — and Agentic Builder does the rest. 

The announcement was covered by SecurityWeek, SiliconANGLE, and Channel Insider, but Valvoline CISO Corey Kaemming, who previewed Agentic Builder before the show, said it best: “It feels less like configuring an application and more like collaborating with a counterpart that understands your SecOps objectives and delivers a ready-to-run agent without the rework.”

RSAC 2026

Tatted with Torq

Forget tote bags. At RSAC 2026, people walked away with permanent ink. 

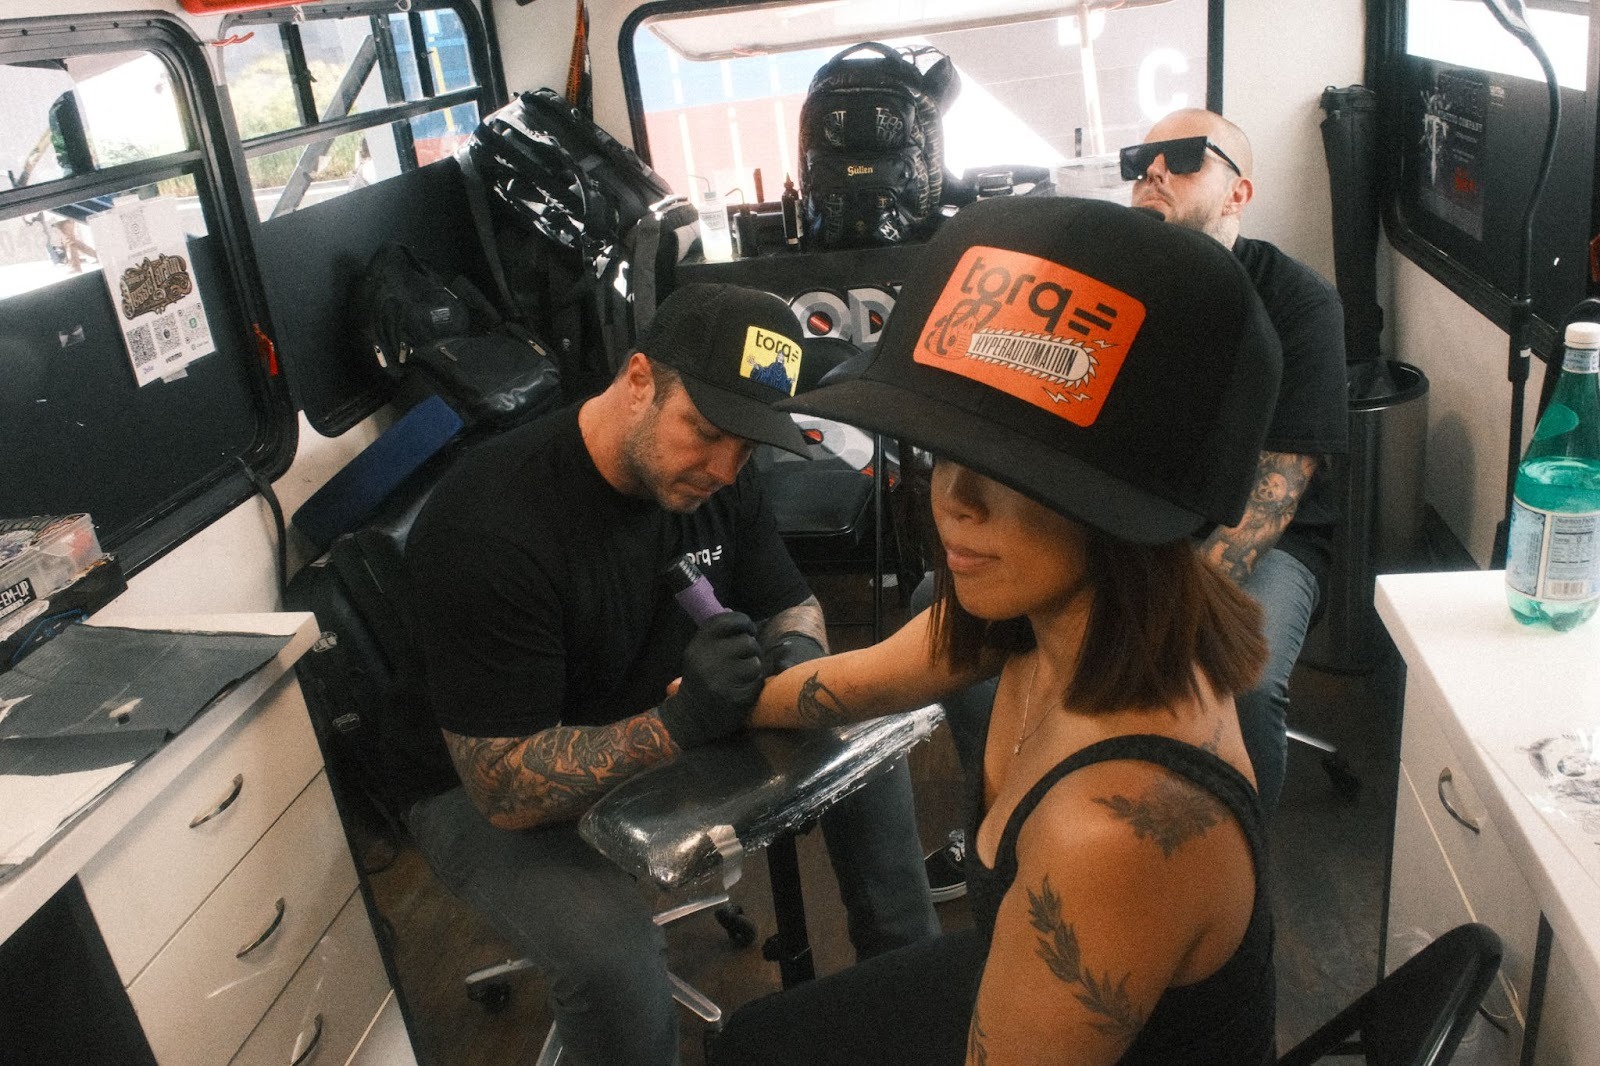
The Torq Tattoo Bus ran walk-in sessions for RSAC attendees on Tuesday and Wednesday. Real tattoo artists. Actual permanent tattoos. Pre-set flash designs, including Trevor and the Torq skeleton. 

The line wrapped around the bus both days. By Tuesday afternoon, we had security professionals rolling up their sleeves who told us they’d specifically planned their RSAC schedule around getting in the chair. The final count: we gave out 155 real (and a few temporary) tattoos during RSAC. Ragrets? None.“This is the highlight of the conference for me,” was just one of the comments we picked up at the bus.

We also heard: “Hey, you’re the urinal cake guys from last year!” Not the legacy we planned — but we’ll own it.

RSAC 2026

And Then There Was… AI 4 Pets

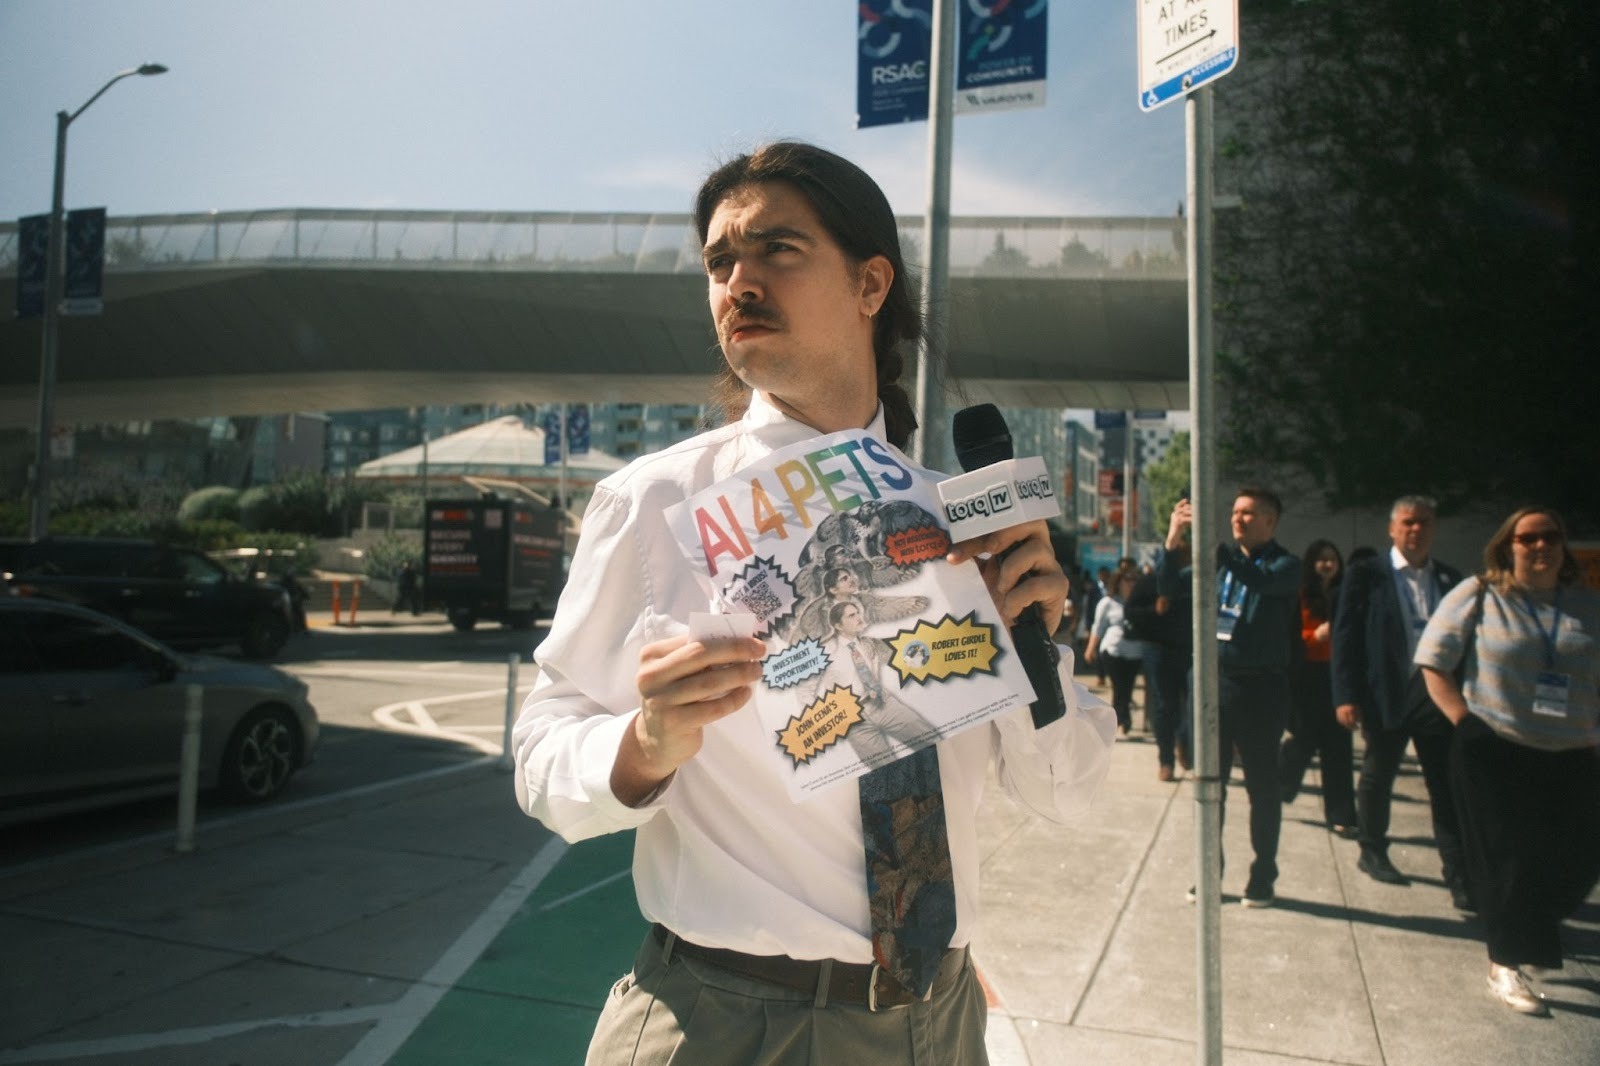
Trevor came to RSAC with a plan. Not Torq’s plan. His plan.

While the rest of the team was running demos and giving out tattoos, Torq’s Junior Media Intern had been quietly working on something of his own: AI 4 Pets — a “bajillion dollar idea” to bring agentic autonomy to pets. He made a website. He filmed a pitch video. He took it to the streets to ask people to invest. 

Nobody invested. 

RSAC 2026

New Research, Hot Off the Press

The 2026 AI SOC Leadership Report dropped during the show — 450 CISOs and security leaders across four countries on what AI is actually doing inside the SOC. The findings landed hard because they matched what we were hearing at the booth all week: 

  • AI is everywhere, but it’s fragmented. 
  • 94% of teams use it. 80% say it’s adding complexity, not reducing it.
  • And 97% trust AI to handle triage — but only 35% actually let it.

Beyond the Booth 

Presidents Forum

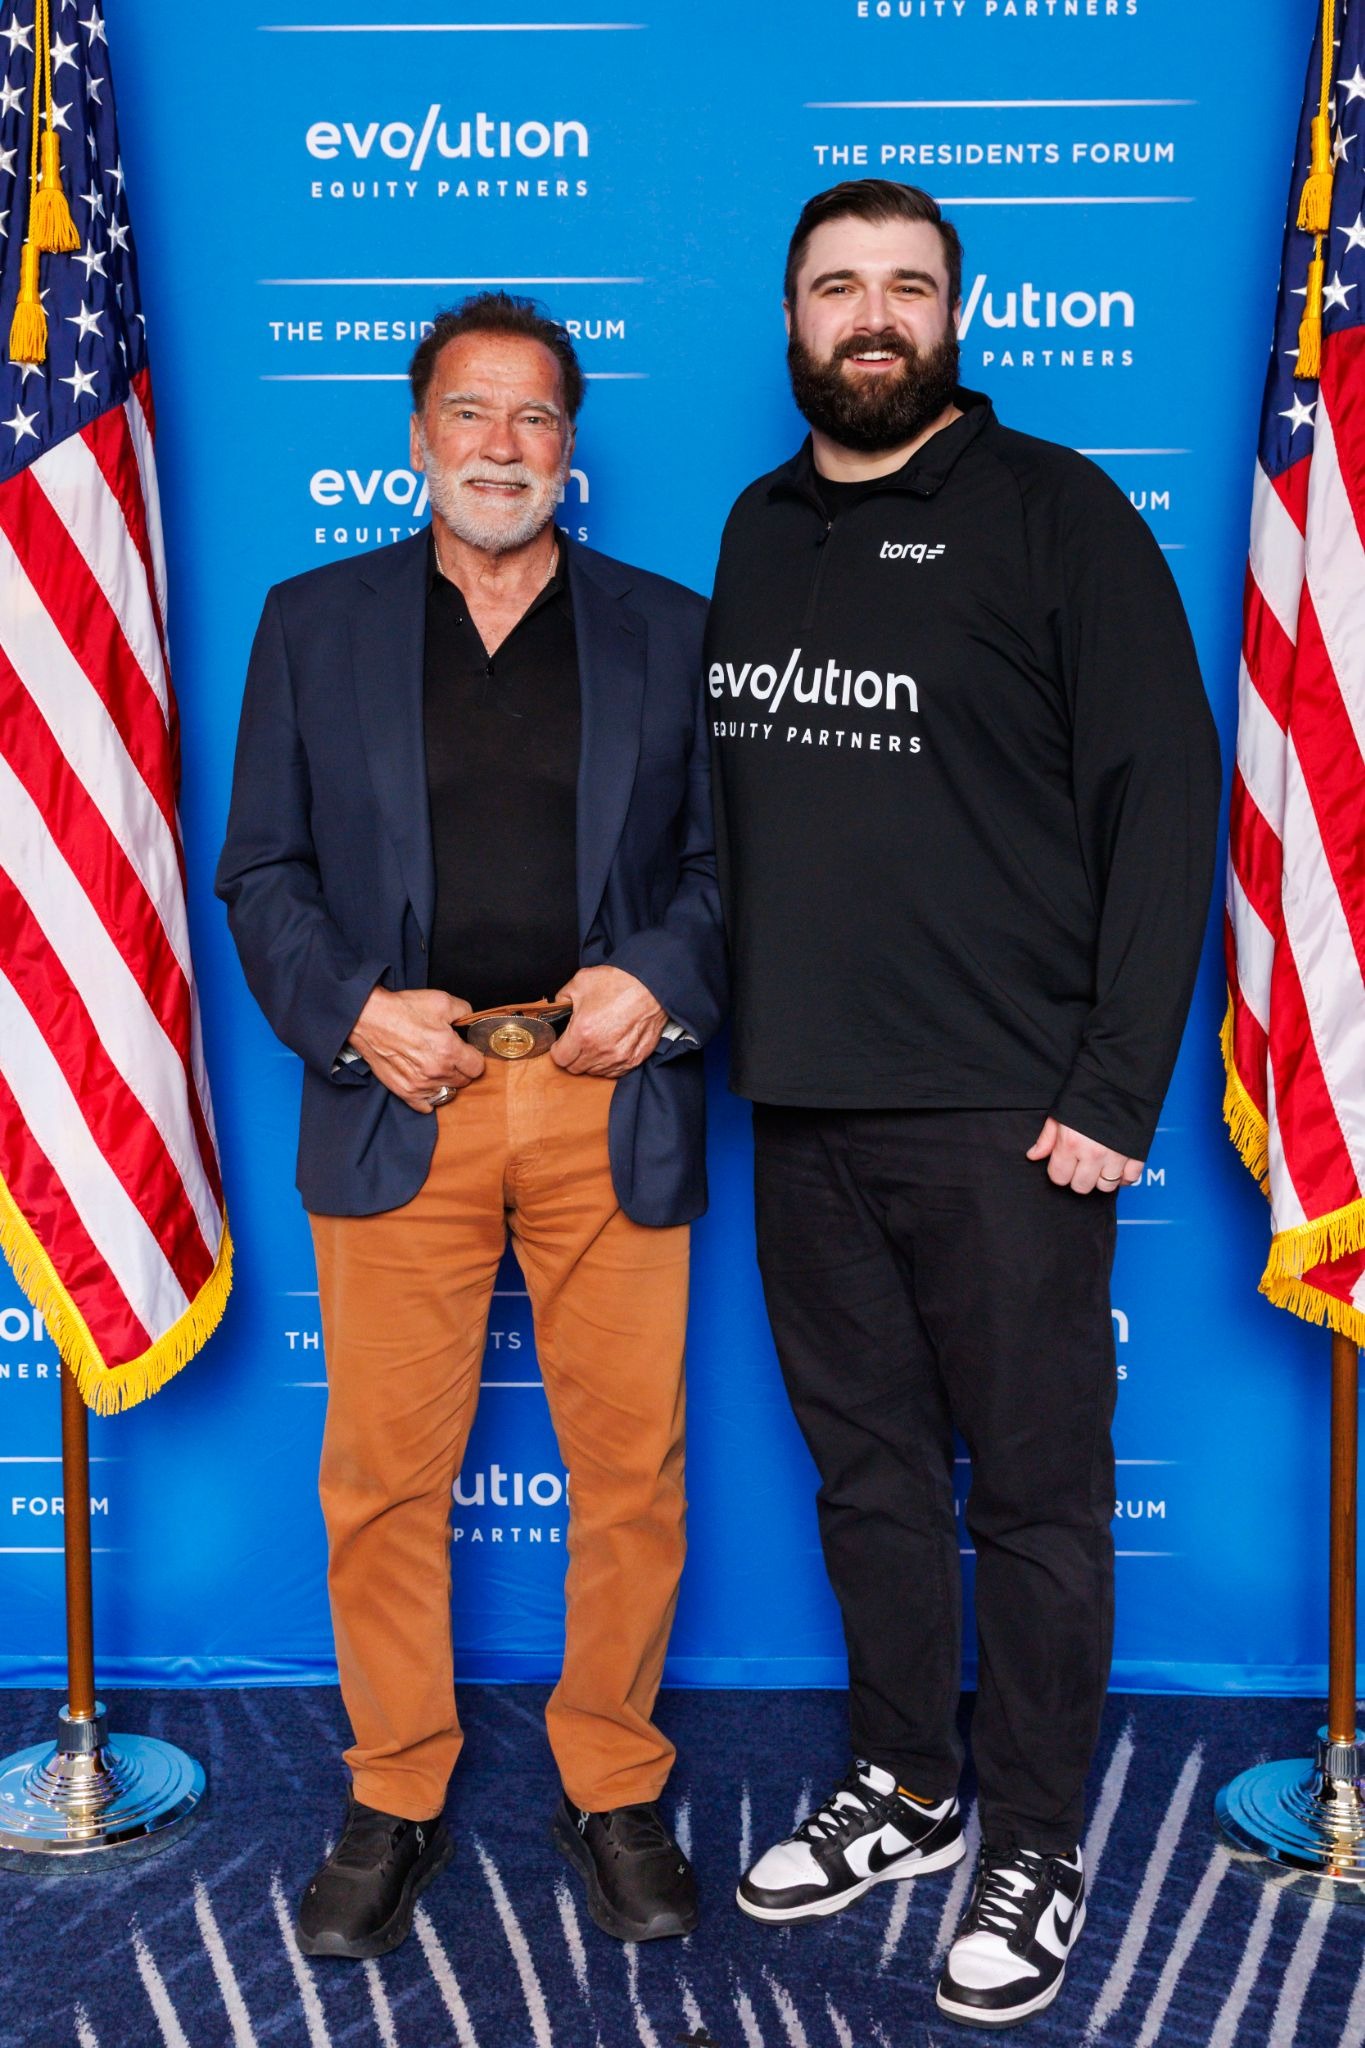
Torq’s Bob Boyle emceed the Presidents Forum, an invitation-only event hosted by Evolution Equity Partners during RSAC week. The headliner: Arnold Schwarzenegger, moderated by SINET Chairman Robert Rodriguez. The conversation centered on leadership under pressure — building teams, making calls with imperfect information, and communicating through crisis. 

Tell NY Marketing Happy Hour

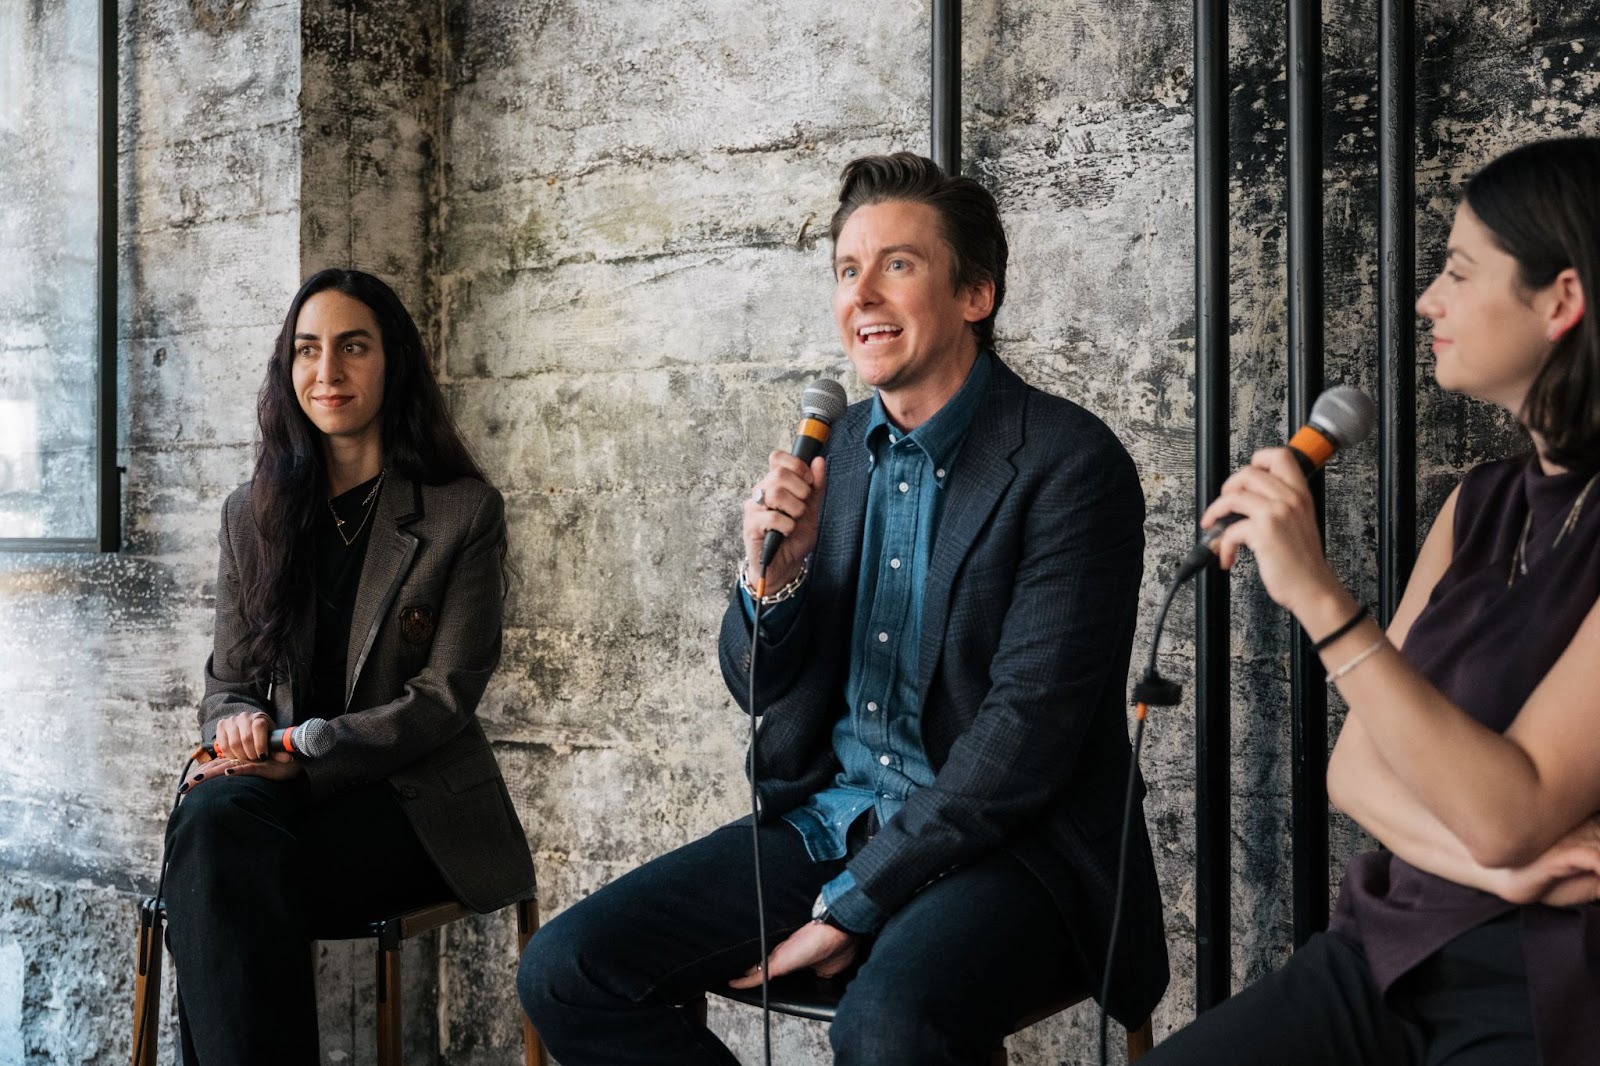
Don Jeter joined Wiz CMO Raaz Herzberg at Tell NY’s marketing mixer — unconventional brand moves, the evolving role of PR, and how to stand out in a space that doesn’t always reward creativity.

RSAC 2026

See You Next Year

RSAC 2026 is in the books. Skelly has been deflated. The tattoo bus has left San Francisco. AI 4 Pets remains unfunded.

But Torq? That’s forever.

How do we go EVEN BIGGER next year? You’ll have to wait until RSAC 2027 to find out.

The conversations at Booth #527 all pointed to the same thing: AI adoption isn’t the problem — unification is. We put the data behind it. 450 security leaders. Five findings. One report.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

CISO to CISO: Redesigning SecOps for AI

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

SOC Automation for MSSPs: The 2026 Guide

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • Alert volumes have surged by more than 300% over the past 5 years. But MSSP pricing hasn’t kept pace. SOC automation is the only path to profitable scale.
  • Legacy SOAR and playbook-based automation can’t keep up. The shift is from scripted execution to agentic AI that reasons, adapts, and acts autonomously.
  • The biggest barrier to AI adoption in the SOC isn’t capability; it’s trust. Full auditability and explainability are non-negotiable, especially for MSSPs serving compliance-sensitive clients.
  • MSSPs evaluating SOC automation platforms should prioritize: Autonomous action, native multi-tenancy, deep integrations, and built-in ROI tracking.

Alert volumes are higher than ever. Client budgets are not. For managed security service providers, that math doesn’t work and no amount of hiring will fix it.

The MSSPs that are scaling profitably right now aren’t doing it with more analysts. They’re doing it with smarter automation. But SOC automation for MSSPs means something very different in 2026 than it did two years ago. This guide breaks down what it actually means, why legacy approaches are failing, and how to evaluate whether a platform can deliver real operational leverage for your business.

What Is SOC Automation?

SOC automation is the use of technology to execute security operations tasks — alert triage, enrichment, investigation, containment, and remediation — with minimal or no human intervention.

In practice, that means replacing the manual, repetitive work that consumes most of a Tier 1 analyst’s day: copy-pasting indicators between tools, running the same enrichment lookups on every alert, filling out tickets, and making low-stakes disposition decisions that follow the same pattern every time.

The goal is to stop wasting analysts’ time on work that doesn’t require human judgment.

For MSSPs specifically, SOC automation addresses the most painful structural realities of running a managed security practice:

  • Multi-tenant scale. You’re managing security for dozens or hundreds of clients simultaneously, each with different environments, tools, and risk tolerances.
  • 24/7 coverage requirements. Threats don’t stop at 5pm, but staffing around the clock is expensive.
  • Margin pressure. Alert volume has grown dramatically; client pricing has not.
  • Talent shortage. Analyst burnout is endemic — 70% of SOC analysts with fewer than five years of experience leave within three years.

Without SOC automation, none of these pain points gets better.

Why Most SOC Automation Falls Short

Not all SOC automation is created equal, and a lot of what’s marketed as “automation” is really just slightly faster manual work.

First-generation SOC automation was built on SOAR platforms that let teams write playbooks. A phishing alert arrives, the playbook runs a series of steps, and if everything goes as expected, a ticket gets created. It was better than nothing. But it came with limitations.

Playbooks are brittle. They break when APIs change, when a new threat variant doesn’t fit the expected pattern, or when a client modifies their stack. Maintaining them at scale is a part-time job in itself. 

The other problem: playbooks execute steps. They don’t think. They can’t adapt to a novel attack chain, correlate signals across multiple clients, or make a judgment call when something doesn’t fit the template. For a single-tenant enterprise SOC, that’s manageable. For an MSSP running hundreds of tenants, it becomes a ceiling on how much you can scale.

What the market is moving toward — and what leading MSSPs are already adopting — is SOC autonomy: AI-driven systems that don’t just follow scripts but reason through investigations, adapt to new threat patterns, and take goal-driven action. For a deeper look at how MSSP cybersecurity is evolving in 2026, this breakdown covers the key trends shaping the market right now.

The Real Benefits of SOC Automation for MSSPs

When AI-driven SOC automation for MSSPs is working the way it should, the operational impact is significant. Here’s where managed security providers see the most measurable gains.

Scale without adding headcount. The most direct benefit. With the right automation in place, a single analyst can effectively oversee what used to require a full Tier 1 team. Leading AI SOC platforms achieve 90%+ autonomous Tier 1 alert handling, meaning the vast majority of incoming alerts are triaged, investigated, and resolved without a human ever touching them.

That’s not a marginal improvement. That’s a fundamentally different operating model.

Faster MTTR across every client. Automated triage and enrichment happen in seconds, not minutes. When a phishing email hits a client’s inbox, an AI-driven workflow can analyze the message, pull threat intelligence, verify the user’s account status, quarantine the message, and close the ticket — all before an analyst would have even opened the alert. Mean time to response (MTTR) drops from 45 minutes or more to under five.

Margin protection. Every alert your platform handles autonomously is an alert your analysts don’t have to touch. That reduces cost-per-alert, cost-per-client, and the pressure to hire ahead of growth. It also frees senior analysts to focus on high-value services — threat hunting, client advisory, proactive risk assessments — that command better margins and differentiate your offering.

Analyst retention. Burnout is the talent crisis hiding inside the talent shortage. When analysts spend their days grinding through repetitive triage work, they leave. When automation absorbs that grind, they stay and do more interesting work. That’s good for your team and it’s good for your clients.

Multi-tenant operational consistency. Standardized, automated workflows mean every client gets the same quality of response, every time, regardless of which analyst is on shift. Centralized visibility with client-specific customization is how MSSPs turn consistency into a selling point. For a closer look at what this kind of AI-powered MSSP model looks like in practice, the Hyperautomation for MSSPs guide walks through the operational details.

Automation vs. Autonomy: Why the Difference Matters in 2026

The 2026 AI SOC Leadership Report surveyed 450 CISOs and security leaders and found that 94% of organizations are already using AI in the SOC in some capacity — but the average team is running seven different AI tools, most of them disconnected. 85% said they’d prefer a unified AI SOC platform to managing multiple point solutions. That fragmentation is both a symptom of the problem and a reason why basic automation continues to fall short.

The distinction that matters right now is between automation and autonomy.

Automation executes predefined steps. A playbook fires, checks a box, sends a notification. It’s deterministic. It does exactly what it was told to do, no more.

Autonomy means an AI system can reason with context, adapt when something unexpected happens, and take goal-directed action — not because it was scripted to do so, but because it understands the goal. When an alert fires, an autonomous system enriches across your SIEM, EDR, identity provider, and cloud environment, correlates related signals, makes a verdict, and either remediates or escalates with full context documented. No human touched it unless escalation was warranted.

The 2026 AI SOC Leadership Report also found that 97% of security leaders are confident AI can handle triage — but only 35% are actually using it there. 

That gap isn’t a capability problem. It’s a trust problem. The number-one barrier cited was visibility: teams can’t see what the AI did, why it made the decision it made, or how to audit it after the fact. For MSSPs who have to demonstrate security outcomes to clients, that’s a critical gap. Establishing where human authority sits within AI governance is increasingly part of how mature SOC teams build that trust internally and with clients.

The platforms worth evaluating in 2026 close both gaps: autonomous action and full explainability.

5 Questions to Evaluate SOC Automation Platforms

Not every platform that calls itself “SOC Automation” delivers autonomous operations. Here’s a practical checklist for cutting through the noise.

1. Does it act or just advise? Can the platform autonomously execute containment and remediation, or does it surface recommendations for human approval? There’s a place for human-in-the-loop workflows, but if every action requires analyst sign-off, you haven’t actually automated anything.

2. Is it built for multi-tenancy? Can you manage hundreds of client environments from a single platform with client-specific customization at scale? This is non-negotiable for MSSPs. Generic enterprise platforms often bolt multi-tenancy on as an afterthought.

3. How does it handle integration complexity? Your clients don’t all run the same stack. Does the platform support your full range of SIEMs, XDR tools, EDR vendors, identity providers, cloud environments, and ticketing systems — with pre-built integrations that actually work? AI agents built for the SOC should be able to pull context from across the environment, not just one or two connected tools.

4. Is it explainable and auditable? Can you show clients exactly what the AI did, why it did it, and when it did it? This is where the trust barrier lives, according to the 2026 AI SOC Leadership Report. Both compliance requirements and client trust depend on transparency. If you can’t explain an AI decision, you can’t defend it.

5. Can you measure ROI? Does the platform track MTTR, automation rates, alert clearance volume, and analyst hours saved? Your clients want outcomes, not activity. You need the data to prove value and to price your services accordingly.

What This Looks Like in Practice

Use Case: Alert volume at Scale

An MSSP managing 50+ clients is drowning in alerts and missing SLAs. Tier 1 analysts spend their entire shift triaging, and escalations are backing up. With autonomous SOC automation, Tier 1 triage runs continuously across all tenants simultaneously — no shift changes, no queue backlogs. Analysts handle escalations only. Alert coverage goes from reactive and inconsistent to 90%+ autonomous.

Use Case: Phishing Response

A phishing campaign hits a client’s inbox. Each report historically required manual enrichment, user verification, and remediation steps. With an AI-driven workflow, the platform analyzes the email header and payload, cross-references threat intelligence, notifies the affected user via Slack, quarantines malicious messages, and closes the ticket. Phishing response time drops from 45 minutes to under five — across every affected client, simultaneously.

The AI SOC Platform Built for MSSPs

The Torq AI SOC Platform is purpose-built for the way modern SOCs actually operate and for the specific demands of multi-tenant managed security. Specialized AI agents handle triage, investigation, remediation, and case management autonomously, coordinated by Torq Socrates, an AI SOC analyst that reasons across the full alert context rather than executing a fixed script.

For MSSPs, that means:

The SOC org chart is already changing at the organizations leading this shift. The MSSPs that win in 2026 won’t have the most analysts. They’ll have the smartest automation.

Ready to see what 450 security leaders said they want from an AI SOC?

FAQs

What is SOC automation for MSSPs?

Modern SOC automation for MSSPs is the use of AI-driven technology to handle security operations tasks — including alert triage, threat enrichment, investigation, containment, and remediation — across multiple client environments with minimal human intervention. Unlike single-tenant enterprise deployments, MSSP SOC automation must operate at scale across dozens or hundreds of clients simultaneously, making native multi-tenancy and consistent workflow standardization essential requirements.

How does SOC automation differ from SOAR?

SOAR (security orchestration, automation, and response) platforms use predefined playbooks to execute scripted steps when specific conditions are met. SOC automation in 2026 goes further, leveraging agentic AI that can reason through alert context, adapt to novel threats, and take autonomous action without a pre-written script for every scenario. SOAR executes. Agentic AI thinks.

What is the ROI of SOC automation for MSSPs?

The clearest ROI metrics include reduced cost-per-alert, lower analyst headcount requirements per client, faster mean time to response (MTTR), and improved SLA performance. MSSPs using advanced SOC automation platforms typically achieve 90%+ autonomous Tier-1 alert handling, which directly reduces service delivery labor costs and creates capacity to take on more clients without proportional headcount growth.

What should MSSPs look for when evaluating SOC automation platforms?

The most critical criteria are autonomous action (not just recommendations), native multi-tenant architecture, broad pre-built integrations across common security stacks, full auditability of AI decisions, and built-in ROI reporting. MSSPs should be skeptical of platforms that require significant playbook maintenance, lack multi-tenant support, or can’t demonstrate transparent decision-making — all of which undermine the scalability and client trust that automation is supposed to deliver.

How does AI change the MSSP analyst role?

AI doesn’t eliminate the analyst role; it elevates it. By automating Tier-1 triage and routine enrichment tasks, AI allows analysts to focus on higher-value work: complex incident investigation, threat hunting, client advisory, and strategic security improvements. According to the 2026 AI SOC Leadership Report, 9 in 10 security leaders view AI oversight as meaningful work, not overhead — a signal that the analyst role is evolving, not disappearing.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

SOAR is Dead. Here’s What Replaces It in 2026.

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • Legacy SOAR was built for a slower threat landscape. Static playbooks, custom scripting, and 12–18 month implementations can’t keep pace with threats that move at machine speed.
  • The right SOAR replacement isn’t a better playbook engine. It’s an AI-native platform built on agentic AI and Hyperautomation that investigates every alert, adapts to novel threats, and delivers ROI in days, not months.
  • Migration doesn’t mean starting over. Your tried-and-true workflows run faster on  Hyperautomation, and the agentic AI layer adds everything legacy SOAR never could: autonomous investigation, adaptive triage, full case management, and remediation at scale.

When SOAR emerged around 2015, it was trying to solve a real problem: SOC analysts were drowning in manual, repetitive tasks across disconnected tools. SOAR promised to connect those tools, automate the workflows between them, and give analysts their time back. For a while, it mostly delivered. 

That era is long dead.

Attackers now move at machine speed, leverage AI to scale their campaigns, and use techniques that evolve faster than any playbook library can track. Meanwhile, legacy SOAR platforms are still running on the same architectural premise they launched with a decade ago: build a playbook for every scenario, script every integration by hand, and hope your engineers never leave.

The evidence of the breakdown is everywhere. IDC found that 83% of SOC analysts struggle with alert volume. The SANS 2024 SOC Survey found that automation had become the top barrier to effective SOC operations, ranking higher than staffing shortages. That’s not a tooling gap. That’s a category failure.

In 2025, GigaOm renamed its SOAR Radar to the SecOps Automation Radar, acknowledging that the category had moved on. The question for security leaders in 2026 isn’t whether to replace legacy SOAR. It’s what the replacement actually needs to look like.

Why Legacy SOAR Can’t Be Fixed With More Playbooks

Before evaluating what comes next, it’s worth being clear-eyed about why legacy SOAR failed. The problems aren’t cosmetic. They’re architectural.

The playbook ceiling is real. Legacy SOAR can only automate what someone has already anticipated and coded. Every scenario requires a custom playbook built and maintained by a security engineer. New threat types, updated tool integrations, and evolving attacker techniques mean playbooks are perpetually incomplete or outdated. 

Most organizations automate 30–40% of their alert volume at best, leaving the rest to queue up or go uninvestigated entirely. According to the SACR 2025 AI SOC Market Landscape, 40% of alerts are never investigated. Of those that are, 90% turn out to be false positives. That’s the real return on a legacy SOAR investment.

Integration sprawl compounds the problem. Legacy SOAR relies on custom scripting to connect your tools. Every new integration is a new maintenance commitment. At enterprise scale, this creates a fragile web of interdependencies that consumes engineering time without a corresponding increase in coverage. When one vendor updates their API, a cascade of playbooks can break simultaneously.

The talent dependency is unsustainable. The engineers who built your SOAR playbooks are the same engineers every company in your industry is trying to hire. When one leaves, they take the tribal knowledge encoded in your automation with them. Legacy SOAR’s reliance on custom scripting creates a dependency on scarce, expensive talent that compounds in cost every year. The economics of an agentic SOC make an increasingly compelling case for making the switch.

Alert fatigue isn’t a people problem. It’s a platform problem. When automation only covers a fraction of alert volume, the gap falls on human analysts. That sustained overload drives burnout, attrition, and the kind of alert fatigue that causes real threats to get missed. Adding more analysts to a broken process doesn’t fix the process.

More playbooks don’t solve these problems. Better playbook management doesn’t solve them either. The architecture itself is the constraint. If you want to understand just how broken the model has become, the SOAR is Dead Manifesto lays it out plainly.

What the Best SOAR Replacement Actually Looks Like

The strongest AI-driven SecOps automation platforms in 2026 don’t look like SOAR. They were built from scratch around a different set of assumptions: that not every threat can be anticipated in advance, that AI should reason through problems rather than match them to templates, and that automation should be accessible to every analyst, not just the engineers who can write Python.

Here’s what separates a genuine next-generation platform from a rebranded version of the same architecture:

It’s built on AI-native design, not AI as an afterthought. The platforms worth evaluating were built around agentic AI from the ground up. Agentic AI reasons through security scenarios dynamically, planning, investigating, and executing actions based on context rather than matching alerts against static rules. This distinction is critical: AI layered on top of playbook logic remains bounded by it. Agentic AI investigates threats for which no playbook exists. Understanding how AI should actually work in your SOC is the right starting point for any evaluation.

Hyperautomation is the foundation, not the feature. True security Hyperautomation means elastic, cloud-native workflow execution that scales with alert volume without degradation. Not a serial queue that backs up during volume spikes, exactly when you need your automation most. Look for platforms that can execute millions of automations daily and that let any analyst easily build and modify workflows, not just your most senior engineers.

Autonomous case management instead of a separate ticketing system. In most legacy SOC environments, case accountability is scattered across ticketing tools, chat threads, and analyst memory. Nobody has the full picture of an incident without manually assembling it from five different tools. The best SOAR replacements unify detection, investigation, and case lifecycle management in a single place, automatically creating cases from correlated alerts, enriching them with context from across the stack, and tracking every action from detection through resolution. When leadership asks what happened and how the team responded, the answer should live in the case record, not in someone’s head.

Any analyst can build automations, not just your engineers. If only two people on your team understand how your automation works, your platform is a single point of failure. Modern Hyperautomation platforms enable analysts to create, modify, and deploy workflows using natural language or a no-code visual builder. The best platforms reduce engineering dependency rather than requiring it as a baseline.

300+ native integrations with no custom scripting. Assess the native integration library depth, the quality of those integrations, and whether the platform can generate new connectors programmatically when needed. Custom scripting required per tool is a red flag. It’s the same maintenance trap that makes legacy SOAR expensive to scale.

Governance is built into the architecture. Automation and AI without governance accelerates risk. The best platforms build governance into the operating model: configurable approval gates for high-impact actions, scope limits on what AI agents can touch, and immutable audit trails for every AI decision and automated action. This isn’t a compliance checkbox. It’s the architecture that makes autonomous operations safe enough to trust at scale and defensible to auditors, insurers, and the board.

Time-to-value measured in days, not months. Ask every vendor for actual customer proof, not projected timelines. The best platforms get priority use cases live in days to weeks. If a vendor can’t point to customers who were live and generating measurable ROI within the first month, that tells you something.

Six Things the Right SOAR Replacement Delivers for Your SOC

Together, those capabilities define what an AI SOC platform actually is — not a rebrand, but a fundamentally different way of operating. The right SOAR replacement doesn’t just close the gaps left by legacy tools. It changes what your SOC can do entirely.

Here’s what that looks like for your team.

1. You go from automating tasks to automating outcomes. Legacy SOAR automates workflow steps. AI-native Hyperautomation automates entire outcomes — investigation, enrichment, triage decision, and response action — without a human orchestrating each stage. Instead of automating only the cases that have playbooks, you’re covering every case that hits your queue. The benefits of an AI SOC compound fast once the coverage gap closes.

2. Alert coverage goes from 30–40% to 100%. When agentic AI investigates every alert, including scenarios for which no playbook exists, nothing falls through the cracks. The best AI SOC platforms close over 90% of Tier 1 cases autonomously. The coverage gap that defined legacy SOAR simply stops existing.

3. Your engineers stop maintaining automation and start building strategy. When the platform handles playbook logic dynamically, your security engineers stop burning cycles on maintenance and start solving harder problems. That shift from automation janitor to strategic contributor is one of the most consistent things security leaders report after moving off legacy SOAR.

4. Response times compress from hours to minutes. Time-to-contain is the metric that matters most in a real incident. AI-native platforms don’t queue work serially; they execute at machine speed across every alert in parallel. The compounding effect of faster triage, faster enrichment, and faster response changes your MTTD and MTTR in ways that playbook tuning never could. This is especially critical in high-stakes scenarios, such as ransomware protection, where minutes matter.

5. The tribal knowledge problem disappears. When institutional automation knowledge lives in the platform rather than in a senior engineer’s head or a Python script nobody else understands, your team stops being one resignation away from a coverage collapse. Any analyst can build, understand, and modify workflows, so the system gets smarter over time instead of more fragile.

6. Every action is captured, every case tells the full story. Modern AI-native platforms build governance into the architecture: immutable audit trails for every AI decision, configurable approval gates for sensitive actions, and case records that hold up in a post-incident review. Real-time SOC dashboards give leadership full visibility into case status, SLA performance, and operational trends in one place. When your CISO, your compliance team, or your cyber insurer asks what happened and how you responded, the answer is already documented.

This is What Torq Was Built For

If the capabilities described above sound like they were written with a specific platform in mind, they were.

The Torq AI SOC Platform is purpose-built to replace legacy SOAR. It’s the only platform that combines Torq Hyperautomation™ — executing orchestration workflows at 10x the speed of legacy SOAR with 300+ native integrations and 4,000+ actions — with a Multi-Agent System that plans, investigates, and responds to threats autonomously.

At the center of the Torq AI SOC Platform is Socrates, Torq’s AI SOC Analyst. It coordinates Torq’s AI Agents to autonomously handle Tier 1 case triage, investigation, and remediation, escalating only what genuinely requires human judgment. This isn’t a chatbot layer over legacy automation. It’s an agentic system that reasons through security scenarios at machine speed, documents every decision, and learns from analyst feedback over time. Learn more about what an AI SOC platform should actually do before making your decision.

Autonomous case management means every alert is automatically correlated into a case, enriched with context from across your stack, prioritized by business impact, and tracked from detection through resolution. Kenvue — protecting household brands including Johnson’s, BAND-AID, and Neutrogena — launched end-to-end autonomous case management in six weeks on Torq.

The results from teams that have already made the switch are hard to argue with:

  • Carvana uses Torq agentic AI to handle 100% of Tier 1 security alerts and automated 41 runbooks within one month of deployment.
  • Valvoline replaced their legacy SOAR, went live in 48 hours, and saves six to seven analyst hours every single day.
  • RSM migrated 200+ managed MSSP customers to the Torq platform in three weeks and now automates 82% of global customer cases.
  • Lennar Corporation replaced their legacy SOAR deployment and cut phishing remediation from hours to minutes.
  • Deepwatch standardized its entire global security infrastructure on Torq. Their Sr. Director of Solutions Engineering noted the analyst environment they’ve built would never have been achievable with legacy SOAR.
  • Check Point uses the Torq platform to react automatically to problems before they become security incidents, eliminating alert fatigue despite a 30% manpower gap.

GigaOm named Torq a Leader and Outperformer in the SecOps Automation Radar for three consecutive years, specifically recognizing Hyperautomation capabilities that legacy SOAR platforms can’t replicate. And with a recent $140M Series D, Torq is accelerating the next phase of the agentic SOC era.

Your SOAR Had Its Run. See What Comes Next.

Legacy SOAR is dead. The teams still on it aren’t just dealing with a dated tool. They’re managing a coverage gap that widens every quarter, a maintenance burden that consumes engineering capacity, and an architecture that fundamentally cannot keep pace with how threats move in 2026.

The right replacement doesn’t automate more tasks. It automates outcomes: every alert investigated, every response executed at machine speed, every action auditable, and your analysts focused on work that actually requires human judgment.

Ready to make the move?

FAQs

What should replace legacy SOAR in 2026?

The right SOAR replacement is an AI-native platform built on agentic AI and Hyperautomation, not a better version of the same playbook-driven architecture. The key capabilities to look for are full alert coverage, autonomous case management, low-code/no-code and AI workflow building accessibility for all analysts, 300+ native integrations without custom scripting, built-in governance, and time-to-value measured in days. The Torq AI SOC Platform was built specifically to deliver all of these and is named a GigaOm Leader and Outperformer for three consecutive years.

What's the difference between SOAR and AI-native Hyperautomation?

SOAR automates predefined workflows through static playbooks that engineers build and maintain. AI-native Hyperautomation uses agentic AI to reason through, investigate, and respond to alerts dynamically, including threat scenarios for which no playbook exists. SOAR covers a subset of known, repeatable processes (typically 30–40% of alert volume). The Torq AI SOC Platform investigates 100% of alerts at machine speed, with the Hyperautomation layer handling known workflows and the agentic layer handling everything else.

How long does it take to migrate from legacy SOAR to a modern platform?

With the right platform, migration happens in days to weeks, not months. Valvoline replaced their legacy SOAR and achieved ROI within 48 hours. RSM migrated 200+ managed customers in three weeks. The key is a platform with a structured migration path, native integrations that don’t require custom scripting, and an implementation program designed for fast time-to-value. See how to migrate →

What is the Torq AI SOC Platform?

The Torq AI SOC Platform combines Torq’s Hyperautomation engine with agentic system to triage, investigate, and autonomously remediate security cases at machine speed. At its core is Socrates, Torq’s AI SOC Analyst, which coordinates specialized AI Agents to handle the full Tier 1 case lifecycle from alert enrichment through remediation, escalating to human analysts only when genuinely required. The platform closes more than 90% of security cases autonomously and is trusted by enterprise security teams and MSSPs globally.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

From Intent to Outcome: How Agentic Coding is Transforming the SOC

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

Security teams are being asked to move faster and handle more complexity, while the threats they defend against are increasingly AI-assisted. When I wrote about VoidLink in January, my point was simple: you cannot fight machine-speed threats with human-speed defense. Attackers are using AI to code, adapt, and scale attacks while humans are still grinding away doing the heavy lifting in the SOC.

Earlier this year, Torq raised our $140M Series D to build the agentic SOC, where machines fight machines. This requires AI that goes far beyond just triaging alerts or summarizing threats. The agentic SOC must cover the complete SecOps lifecycle — from triage to fix, from Tier 1 to Tier 3, from builder to responder. 

Simply better automation isn’t enough. Agentic automation is. 

Today, we’re announcing Agentic Builder — a critical extension of the Torq AI SOC Platform, and the most significant step we’ve taken toward making the agentic SOC a practical reality for every security team.

The Problem Hasn’t Changed

The SOC’s struggle isn’t a people problem. The security teams I speak to every day are sharp, dedicated, and deeply skilled. The problem is legacy security models that expect human beings to act like machines, doing repetitive work at a pace and scale that human beings will never be able to sustain.

We’ve spent the last few years solving the first half of that problem, deploying agentic AI to handle the triage, investigation, and response that was drowning analysts. That’s working. Our customers are closing over 90% of security cases autonomously. Carvana is handling 100% of their Tier 1 alerts with Torq AI Agents. The average tenure of a security analyst using Torq is increasing, and teams are handling more work without adding headcount. 

After successfully delivering AI capabilities that have freed SOC analysts from overwhelming alerts, false positives, and fatigue, Torq now liberates SecOps engineers and architects from the manual tedium that delays value realization. Torq is ensuring defenders move faster than attackers — autonomously, intelligently, and without limits.” 

– Ofer Smadari, CEO and Co-Founder, Torq

But there’s a second major constraint to address: the engineering bottleneck. Building and maintaining the agents that do this work still requires human effort. It requires skilled engineers to create and maintain workflows as new threat categories emerge, format security cases, and write the logic for custom AI agents. 

Hyperautomation’s no-code automation and drag-and-drop building solved a lot of the pain surrounding security engineering caused by legacy SOAR, but there is still a baseline of work hours that need to be dedicated to the maintenance overtime. 

And if VoidLink taught us anything it is that “agentic coding” is accelerating threat engineering. Malware that once took months to create can now be produced in less than a 2-week agile sprint. It is not fair to expect humans to fight back against that level of machine-speed engineering. The agentic SOC must address every source of SecOps fatigue across the full threat lifecycle, not just a single piece of the larger puzzle.

That’s the problem Torq’s Agentic Builder solves.

What is Agentic Coding, and Why Does It Matter?

If you work in software development, you’ve watched what Cursor has done to engineering productivity. It didn’t just autocomplete code or create a chatbot that would discuss what code might look like. It moved to autonomous, multi-file execution — reading the full codebase, understanding dependencies, writing orchestration logic, and producing working output.

The shift wasn’t incremental. It was categorical.

Agentic coding is when an AI autonomously plans, writes, executes, and iterates on code to complete multi-step development tasks. The same categorical shift is now possible in security operations, which is exactly what we built here at Torq.

Within SecOps, agentic coding means ingesting a high-level security objective, planning, building across available security tools, running validation tests, and iterating until operationally correct in a production SOC environment. The AI operates with full system context, breaks down complex intent-based goals, executes independently, iterates against real feedback, and produces production-ready outputs. 

This shift the cognitive load of engineering security automation from humans to machines, taking SecOps from “here’s a workflow template for you to start with” to “here’s a fully working security agent that is already integrated across your stack”

From Intent to Working Agent

Torq Agentic Builder builds production-grade AI agents from natural language prompts through contextual analysis, planning, and testing — effectively turning human intent into agentic outcomes in minutes. 

Here’s what Agentic Builder actually does:

  1. A SOC engineer or security architect describes what they need. Something like: “Correlate EDR alerts with suspicious login attempts and known malicious IPs, map to MITRE ATT&CK, and escalate based on severity.”
  2. From that intent, Agentic Builder — part of Torq Socrates, the core orchestrator of the Torq AI SOC Platform — takes over to:
    • Read your integrations, available APIs, existing workflows, runbooks, and case schemas
    • Plan the assignment, selects the right tools, and defines guardrails
    • Write the orchestration logic
    • Build a deployable Torq HyperAgents™ 
    • Test it against real scenarios before anything goes live — showing you every step, tool call, and output so you can refine behavior until it matches how your SOC actually runs

Nothing deploys without your explicit approval so humans remain the on-the-loop reviewers while the machine handles the execution, and heavy lifting, at machine speed. The output isn’t a template or a suggestion — it’s a working security agent, already integrated across your stack, ready to manage alerts 24/7.

What Agentic Coding Means for Security Teams

The historic tradeoff in security automation has been speed versus control. You could move fast and accept the risk or move carefully and fall behind the threat, but neither option was good enough. Agentic Builder eliminates that tradeoff.

With agentic coding, security engineers and architects can now design and operationalize sophisticated, agentic security workflows in minutes — without sacrificing governance, transparency, or control. Each agent is tested against real data before deployment, surfacing every decision for review, and continuously monitoring and auto-calibrating the SecOps workflow in production to eliminate the risk of drift.

That frees your best people to do what they do best: threat hunting, strategic risk decisions, and high-stakes incident response.

Where We’re Headed: Security Engineering at Machine Speed

Torq raised our Series D because we believe that the future of security operations is agentic, and we are uniquely positioned to deliver that reality. Not AI as a feature bolted on or another point solution, but full threat lifecycle management — from alert through remediation — with humans in control and machines doing the work.

Agentic Builder is the next chapter in that story. It means the Torq AI SOC Platform doesn’t just run your SOC, it helps you build it, scale it, and continuously improve it while keeping pace with an adversary that never slows down.

Torq is providing exclusive demos of Agentic Builder for qualified RSAC attendees, March 23-26, at Booth #527, South Expo Hall, Moscone Center in San Francisco.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

AI or Die: Where Human Authority Must Ultimately Sit

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to that, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.

There’s a growing acceptance that AI is no longer optional in security. That battle is largely won. The more interesting question — and the one I keep getting asked — is what we actually believe AI should be responsible for, and where human authority must ultimately sit.

It’s a governance question. And right now, most organizations are getting it wrong.

Not because they’re being reckless. But because they’re thinking about AI governance the same way they thought about governing ChatGPT usage: as a risk to be managed rather than a capability to be designed. 

That’s the wrong frame entirely. 

Especially as technologies like Model Context Protocol (MCP) — the mechanism by which AI models communicate with each other — start to reshape the landscape in ways most governance frameworks aren’t remotely equipped to handle.

So let me share how I think about this. Where AI can and should own the work. Where humans must stay in the loop. And what a governance model that’s actually fit for purpose looks like in 2026.

The Accountability Gap: Extreme Ownership Starts With the CISO 

Let me start with the question I get asked more than any other: If AI makes the wrong call and a breach happens, who’s accountable?

The answer is straightforward, even if it’s uncomfortable: the CISO.

It’s no different from recruiting a senior analyst you believed in, and they make a catastrophic mistake. The analyst may be at fault — but your head is on the block. 

AI is the same. The CISO’s responsibility is to validate the technology, validate the approach, test the effectiveness, test the outcomes, and play in that judgment space in a safe environment before letting it anywhere near the enterprise. Then go through every step to de-risk it as much as possible. That accountability doesn’t transfer to the vendor. It doesn’t transfer to the board. It sits with you.

It’s a mindset Navy SEALs Jocko Willink and Leif Babin captured perfectly with the concept of Extreme Ownership — the idea that leaders must take full responsibility for everything in their world, including failure, with no excuses and no ego. 

It’s one of the core values at Torq, and honestly, it’s a big part of why the culture resonated with me when I joined. Because this is exactly how I’ve always approached security leadership. You don’t get to point at the AI. You don’t get to point at the vendor. You own it.

And once you accept that, the whole question of where to draw the governance line becomes a lot clearer.

What AI Should Own, What It Should Inform, and What Stays Human 

I think about this in terms of the three-layer model I outlined in the first piece in this series: Outcome, Judgment, and Execution. 

In that model, the execution layer is where AI and automation operate — continuously, consistently, at machine speed, within predefined guardrails. This is where AI earns its keep in the AI SOC: Repeatable, rules-based, high-volume work. Tier 1 triage. Alert enrichment. Containment actions that are reversible, well-understood, and within clearly defined boundaries.

The judgment layer is where humans must stay in the loop. This is where I draw the line — and it’s not an arbitrary one. The decisions that require human authority are the ones that demand business context. Risk appetite. The political environment you’re operating in. The company’s financial situation. The strategic direction the board is pursuing this quarter.

No matter how well-trained an AI agent is, no matter how much historical incident data it can pull from, it will never have its finger on the pulse of all of that. You could add it to the knowledge base — but full contextual judgment isn’t something you can upload. That’s where humans must sit.

The outcome layer is where the strategic intent lives. This is entirely human. What are we trying to protect? What does success look like? How do we measure it? AI can inform this layer — surface patterns, highlight gaps, accelerate analysis — but it cannot define it.

The more capable AI becomes, the more important it is to be precise about where human authority is non-negotiable.

AI Trust Isn’t Given. It’s Earned. 

One of the most common mistakes I see is organizations trying to go too fast, too soon. They see the potential, they’re under pressure to deliver results, and they push AI into complex, high-stakes decisions before they’ve built the foundation of trust that those decisions require.

Here’s how I think about the right sequence for building trust with AI: least critical to most critical, least complex to most complex.

Start with lower-level, repeatable tasks. Build workflows. Run them. Review the outcomes. Ask the honest question: did the workflow you just built actually achieve the outcome you wanted? If yes, take the learning and move further along the stack. If not, go back through the process, improve it, and run it again.

It’s a continuous improvement loop — the objective is to build trust incrementally as you go. And it’s the only approach that’s actually sustainable.

Think about how trust works — with a new colleague, a new friend, a new direct report. It’s never given. It’s earned through consistent actions that match intent. You start small, observe, and expand as the track record develops. And when something doesn’t go as planned, you use it to recalibrate, not give up.

Building trust with AI is no different. The actions the system takes are a direct reflection of the foundations and boundaries you built: the workflows you designed, the guardrails you set, the outcomes you defined. If it’s producing the right results, that’s your foundation holding. If it isn’t, that’s the feedback loop telling you to go back and rebuild before you go further.

You Can See Automation. You Have to Trust AI.

The apprehension around AI in SecOps is significantly higher than the apprehension around traditional security automation, and for good reason. With automation, the input-output relationship is transparent. With AI — particularly agentic AI — the system is making a learned judgment about what should happen next. That’s a fundamentally different kind of relationship to build.

To get comfortable with AI, CISOs need to go back to the basic building blocks. Understand how decisions are being made. Understand what guardrails are in place. Understand what the boundaries are. And then expand them deliberately, as the evidence builds. Just like you would with anyone new you’re learning to trust.

What Governance Actually Needs to Cover

Most governance models being applied to AI right now were designed to manage GenAI usage — the “who’s using ChatGPT” era of governance. They’re not built for governing AI within security tooling itself. And they’re certainly not built for what’s coming next with MCP, where AI models are communicating with each other in ways that create entirely new chains of decision-making and action.

When I think about a governance model that’s actually fit for purpose, I see three dimensions:

  1. The people dimension treats AI as you would a new employee. What decisions is it authorized to make? What requires escalation? What is it never permitted to do? These aren’t technical questions. They’re policy questions, and they need to be answered at the organizational level — not by the security team in isolation.
  2. The legal dimension covers data processing, how AI interacts with sensitive information throughout the company, and how its usage is documented for regulatory purposes. This isn’t just a security problem. Legal needs a seat at this table.
  3. The technology dimension covers what technology you’re using, how you’re using it, and the integrity of the system. This is where the security and technical teams lead — validating the platform, the architecture, the integrations, and the guardrails.

None of these dimensions operate in isolation. The day-to-day governance can sit with the security and GRC teams. But the policy has to be organizational. It has to be holistic. Enforcing it comes down to the technical teams, but owning it requires the whole organization to be aligned.

And this isn’t a new role. It’s an existing role that is adapting. The people responsible for policy today need to develop new skills, understand the new technology, and update their frameworks accordingly. The answer isn’t to hire a Chief AI Governance Officer and call it done. The answer is to build the capability into the teams you already have.

When Security Gets It Right, the Whole Org Catches Up

Here’s something I’ve noticed consistently: once adjacent teams see the outcomes security is delivering with AI and automation, they want in.

GRC is the most natural next step. Identity and access management. IT operations. Any function that involves repeatable processes, assurance activity, or continuous monitoring stands to gain significantly. The model translates directly.

And that’s actually one of the most compelling arguments for security teams to lead the initiative on AI advancements. 

When security builds a working model — an outcome layer, a judgment layer, an execution layer that actually delivers — it becomes a common language the wider organization can adopt. 

Security becomes the team that figured it out first. Everyone else becomes a customer of that thinking.

And maybe the most exciting possibility? A real-time CISO-level SOC dashboard that reflects actual organizational risk posture as it stands right now, not as it stood at last quarter’s reporting cycle. CISOs being able to finally see everything has been the holy grail for years. 

With AI doing the continuous monitoring, the continuous enrichment, the continuous assessment, we might finally be close to it.

The One Place Humans Will Always Sit

I want to be direct about this, because I think it gets obscured in the excitement around AI’s capabilities.
The most complex investigations will always require a human in the loop. 

Not because AI can’t process the data. It can process more data, faster, than any human team. But the decision that comes out of that investigation isn’t solely a data decision — it’s a judgment call that requires knowing the business, the risk appetite, the stakeholders, and what’s politically viable right now. That judgment doesn’t sit in a knowledge base. It lives in the people who’ve built relationships across the organization, who’ve sat in the board meetings, who understand the strategy, the pressures, and the history. 

AI can inform that judgment. It can surface the evidence, structure the analysis, and highlight the options. But the call? That’s human. That stays human.

The organizations that design their AI governance around this principle — AI at machine speed in the execution layer, human authority at the points where it genuinely matters — will be the ones that build something sustainable.

The organizations that sacrifice that line for a quick fix of speed or efficiency will find out exactly why it mattered in the first place — and not at a moment of their choosing.

And that moment will come.

Machine speed where it counts. Human authority where it matters. Get the AI or Die Manifesto and start building.

Keep reading John’s CISO to CISO Blog Series on Redesigning SecOps for AI.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO

Agentic AI & Hyperautomation: Your SOC Guide for 2026

Contents

Get a Personalized Demo

See how Torq harnesses AI in your SOC to investigate, prioritize, and respond to threats faster.

Request a Demo

TL;DR

  • 40% of security alerts go uninvestigated — legacy tools and SOAR simply can’t keep up.
  • Hyperautomation is what SOC teams need. It replaces static, engineer-heavy playbooks with AI-generated, no-code workflows that scale.
  • Agentic AI goes even further — it doesn’t just automate tasks, it reasons, plans, and acts autonomously.
  • The winning model is “human-on-the-loop”: AI handles alert volume, humans handle strategic judgment calls.
  • Start small — phishing triage is the ideal first use case to build trust before expanding AI autonomy.
  • The SOCs that thrive in 2026 will treat AI as the foundation — not just another feature in the stack.

What is Agentic AI in Security Operations?

Agentic AI in security operations refers to autonomous AI systems that reason through security threats, plan multi-step investigation workflows, and execute response actions — without requiring constant human direction for each step. Unlike AI tools that summarize or recommend, agentic AI acts. It ingests an alert, pulls context from across your security stack, correlates signals, reaches a verdict, and initiates containment — all within defined guardrails your team controls.

The distinction that matters most is between AI-assisted and AI-autonomous operations. AI-assisted tools advise analysts. AI-autonomous systems act on their behalf. A tool that surfaces a summary of a phishing alert and a system that triages, scores, remediates, and documents that alert are fundamentally different things — and only one of them closes the gap between attacker speed and defender capacity.

In the SOC context, agentic AI operates as a digital analyst that works 24/7 — processing alert volume that no human team can match, applying consistent judgment across every case, and escalating to human analysts only when the situation genuinely requires strategic authority. According to IDC, organizations using the Torq AI SOC Platform achieve 95% of Tier-1 cases auto-investigated, with MTTR dropping from hours to minutes.

What Skills Do SOC Analysts Need for Agentic AI?

SOC analysts working alongside agentic AI need a different skill set than analysts working in traditional environments. Technical triage skills matter less — the AI handles that. Strategic judgment, threat hunting, AI oversight, and the ability to direct AI agents using natural language matter more.

Specifically, analysts benefit from familiarity with MITRE ATT&CK and how attacker TTPs map to observable behaviors, experience interpreting AI-generated investigation summaries and audit logs, and the ability to configure escalation thresholds and governance guardrails. Workflow literacy — understanding how to build, modify, and quality-check automated response workflows — is increasingly essential. Platforms like the Torq are designed so analysts work in natural language rather than code, which lowers the bar significantly for teams without deep scripting expertise.

How Much Can Agentic AI Reduce Alert Fatigue?

Alert fatigue is one of the most measurable problems agentic AI solves. According to the SACR 2025 AI SOC Market Landscape report, 40% of security alerts go uninvestigated with legacy tooling. Agentic AI addresses this directly by handling the full Tier-1 investigation lifecycle autonomously — enriching alerts, suppressing false positives, and closing low-risk cases without analyst involvement.

The practical result: analysts stop spending their shifts on repetitive triage and start spending them on the threats that actually require human judgment. Valvoline’s SOC team saved 7 analyst hours per day after deploying Torq — time previously consumed by manual phishing review and alert queue management. RSM automated 82% of global MSSP customer cases. The ROI from reducing alert fatigue compounds quickly: lower burnout, better retention, and a team that can take on more without adding headcount.

Your AI SOC Guide Starts Here

According to the SACR 2025 AI SOC Market Landscape report, 40% of security alerts go uninvestigated. The average alert investigation takes 70 minutes. Meanwhile, attackers achieve breakout in under 48 hours. That math doesn’t work in anyone’s favor — except the adversary’s.

Today’s SOCs are fighting a losing battle with legacy tools. Alert volumes are exploding, skilled analysts are nearly impossible to hire and retain, and traditional automation can’t keep pace with AI-powered threats that evolve faster than any playbook can be written. 

The answer isn’t more analysts or more tools. It’s a smarter approach to how security operations work altogether. Agentic AI powered by Hyperautomation represents a fundamental shift from automated (static playbooks that execute predefined steps) to autonomous (AI that reasons, plans, and acts). Organizations that embrace this shift will outpace threats. Those that don’t will fall further behind.

This guide covers the evolution of SOCs, how to implement agentic AI powered by Hyperautomation, the challenges you’ll face, and a practical checklist to overcome them.

The SOC Glow-Up: Manual to Autonomous 

To understand where SOCs are headed, it helps to understand how they got here.

The traditional SOC was built on human expertise and manual investigation. Analysts triaged alerts by hand, pivoted between siloed tools, and followed static runbooks. It worked — until alert volumes outpaced human capacity. Alert fatigue set in. Analyst burnout followed. And threat actors got faster.

The first wave of automation (SOAR) promised relief. And to its credit, it helped teams automate repetitive, well-defined tasks. But SOAR had a fundamental flaw: it required heavy scripting, constant maintenance, and a dedicated engineering team just to keep workflows running. Worse, it couldn’t adapt to novel threats. Every new attack vector meant another playbook to write, test, and maintain. SOAR became a second job.

The shift to Hyperautomation changed the equation. Instead of static, hand-coded workflows, security Hyperautomation delivers seamless integration across the entire security stack, with AI-generated workflows, no-code orchestration, and automation that scales without engineering dependency. Security teams stopped spending cycles maintaining automation and started spending them on what actually matters.

The emergence of agentic AI took it a step further. Agentic AI doesn’t just execute playbooks — it reasons through problems, plans multi-step investigations, and takes autonomous action within defined guardrails. It can investigate an alert, gather context from across the stack, and respond autonomously, with humans on the loop only for critical judgment calls.

The distinction that matters most here is between AI-assisted and AI-autonomous operations. AI-assisted tools advise. AI-autonomous systems act. A chatbot that summarizes an alert and a system that triages, investigates, and remediates it are fundamentally different things — and only one of them closes the gap between attacker speed and defender capacity.

The results speak for themselves. According to IDC, organizations using Torq can automate more than 95% of Tier 1 analyst tasks, reducing MTTR from hours to minutes. The autonomous SOC isn’t a future-state aspiration. It’s happening now.

How Does Hyperautomation Differ from Legacy Security Automation?

Hyperautomation and legacy security automation both aim to reduce manual work in the SOC — but they take fundamentally different approaches, and the gap between them shows up immediately in production.

Legacy security automation executes predefined, static playbooks. An analyst or engineer writes a script: if X happens, do Y. That works well for known, repeatable scenarios. The moment attack patterns deviate from what the playbook expected, the automation breaks and an analyst has to step in. Maintaining those playbooks at scale requires a dedicated engineering team, and every new threat vector means a new playbook to build, test, and maintain.

Hyperautomation takes a different approach. Rather than static scripts, it delivers AI-generated workflows that adapt to new inputs, no-code orchestration that security engineers — not developers — can build and modify, and seamless integration across the entire security stack through API-first architecture. Hyperautomation connects your EDR, SIEM, identity, cloud, and ticketing tools into a single orchestration layer — so when an alert fires, the response draws on context from everywhere, not just the tool that triggered it.

Here’s how the two approaches compare across the dimensions that matter most in production.

Flexibility. Legacy automation requires manual playbook updates for each new threat type. Hyperautomation generates and adapts workflows using AI, handling novel scenarios without engineering intervention.

Maintenance. Legacy automation demands constant playbook upkeep and dedicated engineering resources. Hyperautomation is built to be managed by security professionals directly, with no proprietary scripting required.

Scale. Legacy automation scales by adding more playbooks and more engineers. Hyperautomation scales by expanding AI autonomy — the same team handles significantly more alert volume.

Integration. Legacy automation relies on proprietary connectors that lock teams into a rigid vendor stack. Hyperautomation uses API-first architecture with 300+ native integrations (https://torq.io/integrations/) and unlimited extensibility.

Speed. Legacy automation executes predefined steps at human-defined intervals. Hyperautomation operates at machine speed — detecting, correlating, and responding in seconds.

What are the Key Benefits of Agentic AI for SOC Teams?

SOC teams that deploy agentic AI powered by Hyperautomation see improvements across four dimensions: speed, scale, consistency, and analyst experience.

Speed. Automated incident response executes containment actions — isolating endpoints, disabling compromised accounts, blocking malicious IPs — in seconds. The average adversary breakout time from initial access to lateral movement is 62 minutes, according to CrowdStrike. Agentic AI closes that window. Human-speed response keeps it open.

Scale. AI agents process thousands of security events simultaneously, around the clock, without fatigue or shift limitations. A SOC running agentic AI handles alert volume that would require a significantly larger human team to match.

Consistency. Every alert receives the same quality of investigation, every time. Agentic AI applies the same enrichment logic, the same escalation criteria, and the same documentation standards regardless of which analyst is on shift, what time it is, or how high the alert queue is.

Analyst experience. When AI absorbs Tier-1 triage, analysts stop doing the work that drives burnout and start doing the work that drives career growth — complex investigations, threat hunting, strategic security improvements. According to the Torq 2026 AI SOC Leadership Report, when security leaders were asked about the number-one expected benefit of agentic AI, their top answer was quality of life — not faster detection, not better MTTR.

A Roadmap for Implementing Agentic AI Powered by Hyperautomation

Knowing the technology is one thing. Getting it into production is another. Here’s how to do it right.

1. Assess organizational readiness

Before deploying anything, audit your current environment. Map your existing tools, workflows, and integration points. Identify where the biggest bottlenecks are — the high-volume, repetitive use cases that consume the most analyst time without requiring deep human judgment. Common candidates: phishing triage, impossible travel alerts, cloud misconfiguration remediation, and user verification workflows.

2. Define objectives and success metrics

What does success actually look like for your team? Get specific. Define target metrics before you start: percentage of Tier 1 alerts auto-resolved, MTTR reduction, analyst hours saved per week, false positive rate. Tie those metrics to business outcomes, because security leadership needs to be able to explain the value to the board.

3. Select the right platform

Not all automation platforms are created equal. Avoid legacy SOAR solutions with AI bolted on as an afterthought — the architectural limitations will follow you. Look for platforms built AI-native from the ground up, with multi-agent systems, advanced case management, no-code and AI-generated workflow building, MCP support, and deep integrations across your stack.

The Torq AI SOC Platform was built for exactly this. With 300+ integrations, no-code workflow generation, and Torq Socrates — the AI SOC Analyst that operates as an agentic OmniAgent, coordinating a system of specialized  AI gents — organizations can go from deployment to value in days, not months. Socrates handles deep research, planning, autonomous remediation, and natural language collaboration with analysts. It’s not a copilot. It acts.

4. Start with high-impact, low-risk use cases

Don’t try to automate everything at once. Pick one or two well-defined use cases where the stakes of an error are manageable. Phishing triage is a great starting point — high volume, well-understood, and easy to measure. Build trust with your team and your stakeholders before expanding AI autonomy.

5. Train personnel and establish governance

This step is non-negotiable. Define clear guardrails: what can AI act on autonomously, and what requires human approval? This is the “human-on-the-loop” model — where AI handles volume and humans supervise strategy, stepping in only when predefined thresholds require it. Upskill analysts to work alongside AI agents, collaborate in natural language, and escalate appropriately.

Read now: Where should AI operate autonomously in security — and where must human authority always sit? >

6. Iterate and expand

Use feedback loops to continuously refine workflows. As confidence grows, expand AI autonomy incrementally. The teams getting the most out of these platforms aren’t the ones who deployed everything at once — they’re the ones who iterated their way to full autonomy.

How Do You Implement Agentic AI in Your SOC?

Successful agentic AI implementation follows a six-step pattern. Teams that skip steps, especially governance and iteration, consistently run into the trust and adoption problems that slow deployment.

  1. Assess organizational readiness. Audit your current environment before deploying anything. Map existing tools, workflows, and integration points. Identify the highest-volume, most repetitive use cases that consume analyst time without requiring deep human judgment. Strong starting candidates: phishing triage, impossible travel alerts, cloud misconfiguration remediation, and user verification workflows.
  2. Define objectives and success metrics. Specificity matters here. Define target metrics before deployment: percentage of Tier-1 alerts auto-resolved, MTTR reduction, analyst hours saved per week, false positive rate. Tie those metrics to business outcomes so security leadership can communicate value to the board clearly.
  3. Select the right platform. Prioritize platforms built AI-native from the ground up. Look for multi-agent architecture, advanced case management, workflow building, and deep integrations across your stack. The Torq AI SOC Platform includes Socrates, Torq’s agentic SOC orchestrator, which coordinates specialized AI agents across the full Tier-1 case lifecycle — from enrichment through containment — escalating to human analysts only when genuine judgment is required.
  4. Start with high-impact, low-risk use cases. Deploy one or two well-defined use cases where the cost of an error is manageable. Phishing triage is the most common and highest-ROI starting point. Build team confidence and stakeholder trust before expanding AI autonomy.
  5. Train personnel and establish governance. Define clear guardrails: what AI acts on autonomously, and what requires human approval. This is the human-on-the-loop model — AI handles volume, humans supervise strategy. Upskill analysts to direct AI agents, interpret AI-generated findings, and escalate appropriately.
  6. Iterate and expand. Use feedback loops to continuously refine workflows. Expand AI autonomy incrementally as confidence grows. The teams achieving the highest automation rates are the ones that iterated their way there, not the ones that tried to deploy everything at once.

What Challenges Should You Expect When Deploying Agentic AI?

Four challenges show up consistently across agentic AI deployments. Each one is solvable.

Analyst skepticism: Analysts who have dealt with unreliable automation before bring healthy skepticism to agentic AI deployments. Address it directly by framing AI as the solution to the work analysts dislike most — the repetitive, high-volume triage that causes burnout — and showing early wins on a contained use case before expanding. Transparency matters enormously here. Analysts trust AI systems that show their work. Platforms with clear audit logs and explainable decision-making earn adoption faster than black-box systems.

Data privacy and governance: Security teams rightly scrutinize AI systems that access sensitive data and make autonomous decisions. Solve this by selecting platforms with strong compliance postures — SOC 2 Type II, HIPAA, GDPR — combined with configurable guardrails that keep AI actions within approved boundaries and full audit trails on every action taken.

Integration complexity: Legacy tools, fragmented data, and siloed systems are the biggest technical barriers to agentic AI adoption. Prioritize platforms with broad native integrations and API-first architecture. Every connector that requires a professional services engagement adds cost and delay that compounds across your stack.

Measuring ROI: Quantifying what did not happen is genuinely hard. Solve this by defining baseline metrics before deployment — alert volume, investigation time, MTTR, analyst hours on Tier-1 work — so post-deployment comparisons are meaningful. The 2026 AI SOC Leadership Report found that the number-one barrier to AI adoption is visibility into what the AI did and why. Teams that build explainability and reporting into their deployment from day one sustain executive support through the full rollout.

The Part Where Things Get Difficult (And What to Do About It)

Even the best-planned implementations hit friction. Here’s what to expect and how to push through it.

Resistance to change. Analysts who’ve been burned by unreliable automation before are right to be skeptical. Address it directly. Frame AI as augmentation, not replacement — something that eliminates the tedious, soul-crushing work and elevates analysts to the strategic, high-judgment roles they actually want to be doing. Socrates is designed for exactly this: it absorbs Tier 1 case load so analysts can focus on critical threats that genuinely require human expertise.

Data privacy and governance concerns. Security teams are rightfully cautious about AI accessing sensitive data or making unauthorized decisions. The answer is choosing platforms with a strong compliance posture — SOC 2 Type II, HIPAA, GDPR — combined with explainable AI that produces full audit trails and configurable guardrails that keep AI actions within approved boundaries. Every Socrates decision comes with a clear record of what it observed, what it concluded, and why it acted.

Integration complexity. Legacy tools, fragmented data, and siloed systems are the biggest technical barriers to adoption. Prioritize platforms with broad native integrations and API-first architecture. If every new connector requires a professional services engagement, that’s not scale — that’s just a new maintenance burden. The economics of a fragmented SOC compound quickly: tool sprawl, integration debt, and overlapping functionality drain budgets and engineering hours before a single alert is resolved.

Measuring ROI. It’s hard to quantify what didn’t happen. Define your baseline metrics before implementation so you have something to measure against. According to IDC, Torq customers achieve 95% of Tier-1 cases auto-investigated, and MSSPs using Torq onboard customers 18x faster. Valvoline reclaimed 6–7 analyst hours per day through automated phishing triage alone — time that’s now spent on higher-priority work.

Real-World Agentic AI Use Cases in Security Operations

The following use cases come directly from Torq customers who have deployed agentic AI and Hyperautomation in production environments. Each one is real — the problems, the workflows, and the outcomes.

Automated Phishing Response and Containment: Valvoline

When Corey Kaemming stepped into the Senior Director of InfoSec role at Valvoline, his team had been cut in half — down from 24 to 12 analysts — while alert volume stayed the same. Their legacy automation was brittle, heavily customized, and required specialist engineers just to keep running. Phishing triage alone consumed up to 12 analyst hours per day.

After deploying the Torq AI SOC Platform, Valvoline saw operational value within 48 hours. Torq automated phishing triage by continuously monitoring inboxes, correlating activity across Microsoft 365, Defender, and CrowdStrike, and escalating only when necessary. When a user clicks a malicious link, Torq automatically initiates password resets, terminates active sessions, and executes containment actions across integrated platforms — with everything tracked in case management. A Rapid7 integration their previous platform had failed to build after hundreds of hours was running in under a week.

Results: 6-7 analyst hours saved per day. Phishing triage went from a 12-hour daily burden to a largely automated workflow. The team expanded Torq’s use beyond security into adjacent operational teams.

“My team is in love with the product. Sometimes, I have to tell them to stop having so much fun and go do something else.”

— Corey Kaemming, Senior Director of InfoSec, Valvoline

Read the full case study: https://torq.io/resources/valvoline-soc-automation/

Autonomous SOC Operations and Incident Response for an MSSP: HWG Sababa

HWG Sababa, a global managed security provider serving enterprise clients across energy, utilities, finance, and healthcare, hit a growth ceiling with their in-house automation tool. Custom coding every workflow was too slow and resource-intensive to scale as they onboarded more clients and expanded their tool stack. With hundreds of customers and a wide range of playbooks to manage, they needed automation their team could build and iterate without heavy engineering overhead.

After deploying Torq, HWG Sababa shifted from months of custom coding to building years’ worth of automations in weeks. They built automated workflows across their multi-tenant client environments, connecting tools across their full stack and enabling investigation and response to happen nearly simultaneously for most case types.

Results: MTTI and MTTR improved by 95% for medium- and low-priority cases and by 85% for high-priority cases. Investigation and response now happen in under eight minutes for most incidents. The efficiency gains translated directly into a competitive advantage — HWG Sababa delivers faster, more consistent outcomes to clients without proportionally growing their analyst headcount.

Read the full case study: https://torq.io/resources/hwg-sababa-mssp-case-study/

Tier-1 and Tier-2 Automation at MDR Scale: Deepwatch

Deepwatch, a leading MDR provider protecting enterprise clients globally, needed to scale their managed detection and response operations without simply adding more analysts. They wanted to automate more deeply across both Tier-1 and Tier-2 tasks — not just the easiest, most repetitive work — while continuing to deliver fast, consistent outcomes to clients with demanding SLAs.

Deepwatch deployed Torq Hyperautomation to automate analysis, triage, and response workflows across their client environments. Torq’s low-code and no-code capabilities allowed the Deepwatch team to build and ship new automations and features at speeds previously impossible with their prior tooling. Torq also streamlined their customer onboarding process, enabling them to iteratively improve it over time.

Results: Deepwatch automates over 90% of Tier-1 and Tier-2 tasks, leading to faster case validation and shorter response times. Customer onboarding is faster than it has ever been.

“New customers are seeing faster onboardings than we’ve seen ever.”

Micah Donald, Former Sr. Director, Deepwatch

Read the full case study: https://torq.io/resources/deepwatch-case-study/

10 Steps to Integrate Agentic AI and Hyperautomation AI into Your SOC

  1. Conduct a readiness assessment of current tools, workflows, and integration gaps.
  2. Identify your top 3–5 high-volume, repetitive use cases to automate first.
  3. Define clear objectives and success metrics aligned to business outcomes.
  4. Evaluate vendors based on AI-native architecture, integrations, and explainability.
  5. Establish governance guardrails — what AI can do autonomously vs. with human approval.
  6. Start with a pilot use case (phishing triage is a great first step) to build trust and demonstrate value.
  7. Train analysts on AI supervision, natural language collaboration, and escalation workflows.
  8. Deploy with full audit logging to ensure compliance and transparency.
  9. Measure outcomes against baseline metrics and iterate based on feedback.
  10. Expand AI autonomy incrementally as confidence and trust grow.

Will Your SOC Be One That Wins?

Agentic AI and Hyperautomation are already transforming how the best security teams operate. Organizations that adopt them now will scale their operations without scaling headcount, reduce MTTR from hours to minutes, and make the shift from reactive firefighting to proactive defense.

The SOCs that thrive in 2026 will be the ones that figured out how to let AI handle volume while humans handle strategy — shifting from human-in-the-loop to human-on-the-loop, and from AI as a feature to AI as the foundation.

Ready to see how to transform your SOC in 90 days? 

FAQs

What's the difference between Hyperautomation and traditional SOAR?

SOAR automates predefined, hand-coded workflows but requires constant engineering maintenance and can’t adapt to new threats. Hyperautomation uses AI-generated, no-code workflows that scale without engineering dependency and adapt dynamically.

How does agentic AI work in a SOC?

It operates as a collaborative system of specialized agents, each handling a distinct part of the threat response lifecycle. Torq’s Socrates acts as an agentic OmniAgent, coordinating a network of specialized agents torq that cover investigation, planning, remediation, and case management — working together to handle threats from detection through resolution.

Does agentic AI replace human analysts?

No. It handles high-volume, repetitive Tier 1 work autonomously while escalating critical cases that require human judgment. Analysts can also collaborate with the system directly using natural language, staying in control of decisions that matter most.

SEE TORQ IN ACTION

Ready to automate everything?

“Torq takes the vision that’s in your head and actually puts it on paper and into practice.”

Corey Kaemming, Senior Director of InfoSec

“Torq offers unprecedented protection and drives extraordinary efficiency for RSM and our customers.”

Todd Willoughby, Director

Compuquip logo in white

“Torq saves hundreds of hours a month on analysis. Alert fatigue is a thing of the past.”

Phillip Tarrant, SOC Technical Manager

Fiverr logo in black

“The only limit Torq has is people’s imaginations.”

Gai Hanochi, VP Business Technologies

Carvana logo in black

“Torq Agentic AI now handles 100% of Carvana’s Tier-1 security alerts.”

Dina Mathers, CISO

Riskified logo in white

“Torq has transformed efficiency for all five of my security teams and enabled them to focus on much more high-value strategic work.”

Yossi Yeshua, CISO